
Oracle Critical Patch Update October 2017
Released October 2017 · Oracle's advisory ↗ · ← Critical Patch Update, July 2017 · Critical Patch Update, January 2018 →
225 CVEs in this release, one square each
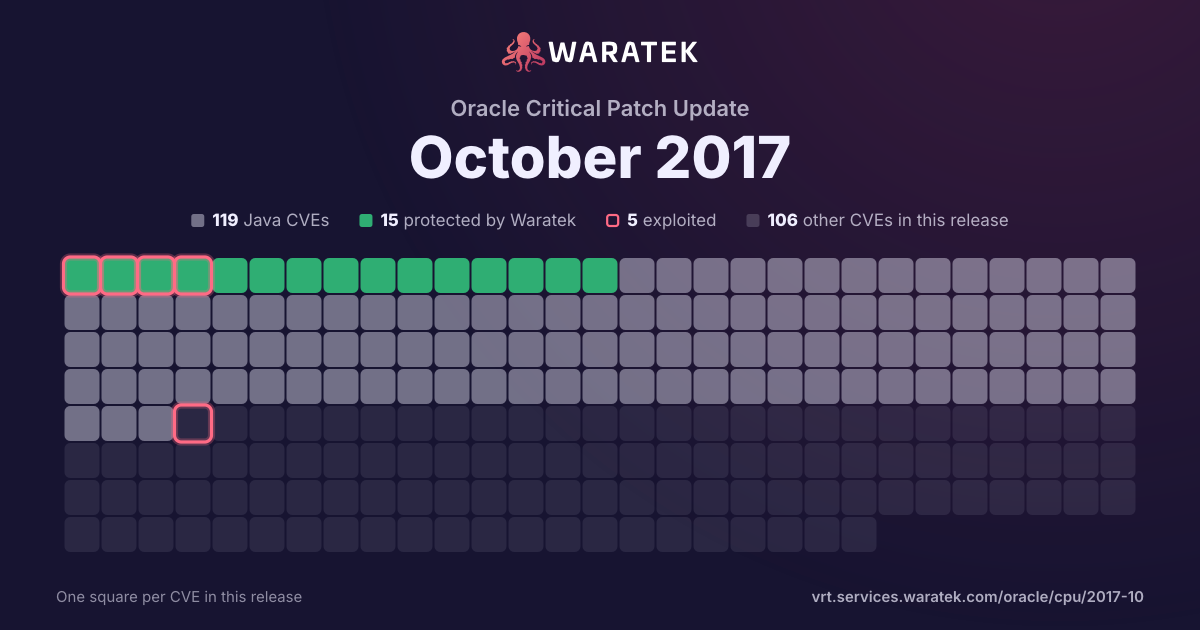
By status
15Protected by Waratek3Mitigation candidate101No exploit published34Outside Waratek scope72Not applicable
5Exploited, marked by the ring
No exploit published. For 100 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 225 matches · 119 in Waratek scope · 15 protected · 5 exploited · 2 CISA KEV · 13 public PoC · 11 EPSS ≥ 0.5
225matches
119in Waratek scope52.9%
15protected6.7%
5exploited2.2%
2CISA KEV0.9%
13public PoC5.8%
11EPSS ≥ 0.54.9%
Protected by Waratek
15
6.7%
Rule in development
0
0.0%
Mitigation candidate
3
1.3%
No exploit published
101
44.9%
Outside Waratek scope
34
15.1%
Not applicable
72
32.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
15
6.7%
partly blocked
0
0.0%
not blocked
210
93.3%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 197 / year
20031
Not applicable1
Medium1
not blocked1
No public exploit1
20040
20050
20060
20070
20080
20090
20100
20110
20120
20131
Not applicable1
High1
not blocked1
No public exploit1
20148
Protected by Waratek2
Outside Waratek scope1
Not applicable5
High4
Medium4
blocked by ARMR today2
not blocked6
Exploited2
No public exploit6
20154
Outside Waratek scope4
Critical1
High1
Medium1
Low1
not blocked4
Working exploit published1
Forecast only1
No public exploit2
201613
Protected by Waratek3
No exploit published1
Outside Waratek scope3
Not applicable6
Critical2
High10
Medium1
blocked by ARMR today3
not blocked10
Working exploit published1
Proof of concept only2
Forecast only1
No public exploit9
2017197
Protected by Waratek10
Mitigation candidate3
No exploit published100
Outside Waratek scope25
Not applicable59
Critical15
High64
Medium108
Low10
blocked by ARMR today10
not blocked187
Exploited3
Working exploit published4
Proof of concept only1
Forecast only1
No public exploit188
20181
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
20042006200820102012201420162018
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-6304 | High | 2016-09-26 | Not applicable | Forecast only | Multiple memory leaks in t1_lib.c in OpenSSL before 1.0.1u, 1.0.2 before 1.0.2i, and 1.1.0 before 1.1.0a allow remote attackers to cause a denial of service (memory consumption) via large OCSP Status Request extensions. |
| CVE-2016-2183 | High | 2016-09-01 | Outside Waratek scope | Proof of concept only | The DES and Triple DES ciphers, as used in the TLS, SSH, and IPSec protocols and other protocols and products, have a birthday bound of approximately four billion blocks, which makes it easier for remote attackers to obtain cleartext data via a birthday attack against a long-duration encrypted session, as demonstrated by an HTTPS session using Triple DES in CBC mode, aka a "Sweet32" attack. |
| CVE-2016-3506 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the JDBC component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2; the Oracle Retail Xstore Point of Service 5.5, 6.0, 6.5, 7.0, 7.1, 15.0, and 16.0; the Oracle Retail Warehouse Management System 14.04, 14.1.3, and 15.0.1; the Oracle Retail Workforce Management 1.60.7, and 1.64.0; the Oracle Retail Clearance Optimization Engine 13.4; the Oracle Retail Markdown Optimization 13.4 and 14.0; and Oracle Retail Merchandising System 16.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-0635 | High | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Enterprise Manager Ops Center component in Oracle Enterprise Manager Grid Control 12.1.4, 12.2.2, and 12.3.2; the Oracle Health Sciences Information Manager component in Oracle Health Sciences Applications 1.2.8.3, 2.0.2.3, and 3.0.1.0; the Oracle Healthcare Master Person Index component in Oracle Health Sciences Applications 2.0.12, 3.0.0, and 4.0.1; the Oracle Documaker component in Oracle Insurance Applications before 12.5; the Oracle Insurance Calculation Engine component in Oracle Insurance Applications 9.7.1, 10.1.2, and 10.2.2; the Oracle Insurance Policy Administration J2EE and Oracle Insurance Rules Palette components in Oracle Insurance Applications 9.6.1, 9.7.1, 10.0.1, 10.1.2, 10.2.0, and 10.2.2; the Oracle Retail Integration Bus component in Oracle Retail Applications 15.0; the Oracle Retail Order Broker component in Oracle Retail Applications 5.1, 5.2, and 15.0; the Primavera Contract Management component in Oracle Primavera Products Suite 14.2; the Primavera P6 Enterprise Project Portfolio Management component in Oracle Primavera Products Suite 8.2, 8.3, 8.4, 15.1, 15.2, and 16.1; the Oracle Financial Services Analytical Applications Infrastructure component in Oracle Financial Services Applications 8.0.0, 8.0.1, 8.0.2, and 8.0.3; the Oracle Commerce Guided Search / Oracle Commerce Experience Manager component in Oracle Commerce 3.1.1, 3.1.2, 11.0, 11.1, and 11.2; the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5; the Oracle Communications BRM - Elastic Charging Engine 11.2.0.0.0 and 11.3.0.0.0; the Oracle Enterprise Repository Enterprise Repository 12.1.3.0.0; the Oracle Financial Services Behavior Detection Platform 8.0.1 and 8.0.2; the Oracle Hyperion Essbase 12.2.1.1; the Oracle Tuxedo System and Applications Monitor (TSAM) 11.1.1.2.0, 11.1.1.2.1, 11.1.1.2.1, 12.1.1.1.0, 12.1.3.0.0, and 12.2.2.0.0; the Oracle Communications WebRTC Session Controller component of Oracle Communications Applications (subcomponent: Security (Spring)) 7.0, 7.1 and 7.2; the Oracle Endeca Information Discovery Integrator 3.2; the Converged Commerce component of Oracle Retail Applications 16.0.1; the Oracle Identity Manager 11.1.2.3.0; Oracle Enterprise Manager for MySQL Database 12.1.0.4; Oracle Retail Invoice Matching 12.0, 13.0, 13.1, 13.2, 14.0, and 14.1; Oracle Communications Performance Intelligence Center (PIC) Software Prior to 10.2.1 and the Oracle Knowledge component of Oracle Siebel CRM (subcomponent: AnswerFlow (Spring Framework)) version 8.5.1.0 - 8.5.1.7 and 8.6.0 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-3092 | High | 2016-07-04 | No exploit published | No public exploit | The MultipartStream class in Apache Commons Fileupload before 1.3.2, as used in Apache Tomcat 7.x before 7.0.70, 8.x before 8.0.36, 8.5.x before 8.5.3, and 9.x before 9.0.0.M7 and other products, allows remote attackers to cause a denial of service (CPU consumption) via a long boundary string. |
| CVE-2016-1181 | High | 2016-07-04 | Protected by Waratek | No public exploit | ActionServlet.java in Apache Struts 1 1.x through 1.3.10 mishandles multithreaded access to an ActionForm instance, which allows remote attackers to execute arbitrary code or cause a denial of service (unexpected memory access) via a multipart request, a related issue to CVE-2015-0899. |
| CVE-2016-2834 | High | 2016-06-13 | Not applicable | No public exploit | Mozilla Network Security Services (NSS) before 3.23, as used in Mozilla Firefox before 47.0, allows remote attackers to cause a denial of service (memory corruption and application crash) or possibly have unspecified other impact via unknown vectors. |
| CVE-2016-2107 | Medium | 2016-05-05 | Not applicable | Working exploit published | The AES-NI implementation in OpenSSL before 1.0.1t and 1.0.2 before 1.0.2h does not consider memory allocation during a certain padding check, which allows remote attackers to obtain sensitive cleartext information via a padding-oracle attack against an AES CBC session. NOTE: this vulnerability exists because of an incorrect fix for CVE-2013-0169. |
| CVE-2016-2381 | High | 2016-04-08 | Not applicable | No public exploit | Perl might allow context-dependent attackers to bypass the taint protection mechanism in a child process via duplicate environment variables in envp. |
| CVE-2016-0714 | High | 2016-02-25 | Outside Waratek scope | No public exploit | The session-persistence implementation in Apache Tomcat 6.x before 6.0.45, 7.x before 7.0.68, 8.x before 8.0.31, and 9.x before 9.0.0.M2 mishandles session attributes, which allows remote authenticated users to bypass intended SecurityManager restrictions and execute arbitrary code in a privileged context via a web application that places a crafted object in a session. |
| CVE-2015-5254 | Critical | 2016-01-08 | Protected by Waratek | Proof of concept only | Apache ActiveMQ 5.x before 5.13.0 does not restrict the classes that can be serialized in the broker, which allows remote attackers to execute arbitrary code via a crafted serialized Java Message Service (JMS) ObjectMessage object. |
| CVE-2015-7940 | Medium | 2015-11-09 | Outside Waratek scope | No public exploit | The Bouncy Castle Java library before 1.51 does not validate a point is withing the elliptic curve, which makes it easier for remote attackers to obtain private keys via a series of crafted elliptic curve Diffie Hellman (ECDH) key exchanges, aka an "invalid curve attack." |
| CVE-2015-3253 | Critical | 2015-08-13 | Outside Waratek scope | No public exploit | The MethodClosure class in runtime/MethodClosure.java in Apache Groovy 1.7.0 through 2.4.3 allows remote attackers to execute arbitrary code or cause a denial of service via a crafted serialized object. |
| CVE-2015-2808 | Low | 2015-04-01 | Outside Waratek scope | Forecast only | The RC4 algorithm, as used in the TLS protocol and SSL protocol, does not properly combine state data with key data during the initialization phase, which makes it easier for remote attackers to conduct plaintext-recovery attacks against the initial bytes of a stream by sniffing network traffic that occasionally relies on keys affected by the Invariance Weakness, and then using a brute-force approach involving LSB values, aka the "Bar Mitzvah" issue. |
| CVE-2015-0235 | High | 2015-01-28 | Outside Waratek scope | Working exploit published | Heap-based buffer overflow in the __nss_hostname_digits_dots function in glibc 2.2, and other 2.x versions before 2.18, allows context-dependent attackers to execute arbitrary code via vectors related to the (1) gethostbyname or (2) gethostbyname2 function, aka "GHOST." |
| CVE-2014-8714 | Medium | 2014-11-23 | Not applicable | No public exploit | The dissect_write_structured_field function in epan/dissectors/packet-tn5250.c in the TN5250 dissector in Wireshark 1.10.x before 1.10.11 and 1.12.x before 1.12.2 allows remote attackers to cause a denial of service (infinite loop) via a crafted packet. |
| CVE-2014-3707 | Medium | 2014-11-15 | Not applicable | No public exploit | The curl_easy_duphandle function in libcurl 7.17.1 through 7.38.0, when running with the CURLOPT_COPYPOSTFIELDS option, does not properly copy HTTP POST data for an easy handle, which triggers an out-of-bounds read that allows remote web servers to read sensitive memory information. |
| CVE-2014-4345 | High | 2014-08-14 | Not applicable | No public exploit | Off-by-one error in the krb5_encode_krbsecretkey function in plugins/kdb/ldap/libkdb_ldap/ldap_principal2.c in the LDAP KDB module in kadmind in MIT Kerberos 5 (aka krb5) 1.6.x through 1.11.x before 1.11.6 and 1.12.x before 1.12.2 allows remote authenticated users to cause a denial of service (buffer overflow) or possibly execute arbitrary code via a series of "cpw -keepold" commands. |
| CVE-2014-3538 | Medium | 2014-07-03 | Not applicable | No public exploit | file before 5.19 does not properly restrict the amount of data read during a regex search, which allows remote attackers to cause a denial of service (CPU consumption) via a crafted file that triggers backtracking during processing of an awk rule. NOTE: this vulnerability exists because of an incomplete fix for CVE-2013-7345. |
| CVE-2014-0224 | High | 2014-06-05 | Outside Waratek scope | Exploited | OpenSSL before 0.9.8za, 1.0.0 before 1.0.0m, and 1.0.1 before 1.0.1h does not properly restrict processing of ChangeCipherSpec messages, which allows man-in-the-middle attackers to trigger use of a zero-length master key in certain OpenSSL-to-OpenSSL communications, and consequently hijack sessions or obtain sensitive information, via a crafted TLS handshake, aka the "CCS Injection" vulnerability. |
| CVE-2014-0114 | High | 2014-04-30 | Protected by Waratek | Exploited | Apache Commons BeanUtils, as distributed in lib/commons-beanutils-1.8.0.jar in Apache Struts 1.x through 1.3.10 and in other products requiring commons-beanutils through 1.9.2, does not suppress the class property, which allows remote attackers to "manipulate" the ClassLoader and execute arbitrary code via the class parameter, as demonstrated by the passing of this parameter to the getClass method of the ActionForm object in Struts 1. |
| CVE-2014-0107 | High | 2014-04-15 | Protected by Waratek | No public exploit | The TransformerFactory in Apache Xalan-Java before 2.7.2 does not properly restrict access to certain properties when FEATURE_SECURE_PROCESSING is enabled, which allows remote attackers to bypass expected restrictions and load arbitrary classes or access external resources via a crafted (1) xalan:content-header, (2) xalan:entities, (3) xslt:content-header, or (4) xslt:entities property, or a Java property that is bound to the XSLT 1.0 system-property function. |
| CVE-2014-0062 | Medium | 2014-03-31 | Not applicable | No public exploit | Race condition in the (1) CREATE INDEX and (2) unspecified ALTER TABLE commands in PostgreSQL before 8.4.20, 9.0.x before 9.0.16, 9.1.x before 9.1.12, 9.2.x before 9.2.7, and 9.3.x before 9.3.3 allows remote authenticated users to create an unauthorized index or read portions of unauthorized tables by creating or deleting a table with the same name during the timing window. |
| CVE-2013-1903 | High | 2013-04-04 | Not applicable | No public exploit | PostgreSQL, possibly 9.2.x before 9.2.4, 9.1.x before 9.1.9, 9.0.x before 9.0.13, 8.4.x before 8.4.17, and 8.3.x before 8.3.23 incorrectly provides the superuser password to scripts related to "graphical installers for Linux and Mac OS X," which has unspecified impact and attack vectors. |
| CVE-2003-1418 | Medium | 2003-12-31 | Not applicable | No public exploit | Apache HTTP Server 1.3.22 through 1.3.27 on OpenBSD allows remote attackers to obtain sensitive information via (1) the ETag header, which reveals the inode number, or (2) multipart MIME boundary, which reveals child process IDs (PID). |