
Oracle Critical Patch Update July 2017
Released July 2017 · Oracle's advisory ↗ · ← Critical Patch Update, April 2017 · Critical Patch Update, October 2017 →
272 CVEs in this release, one square each
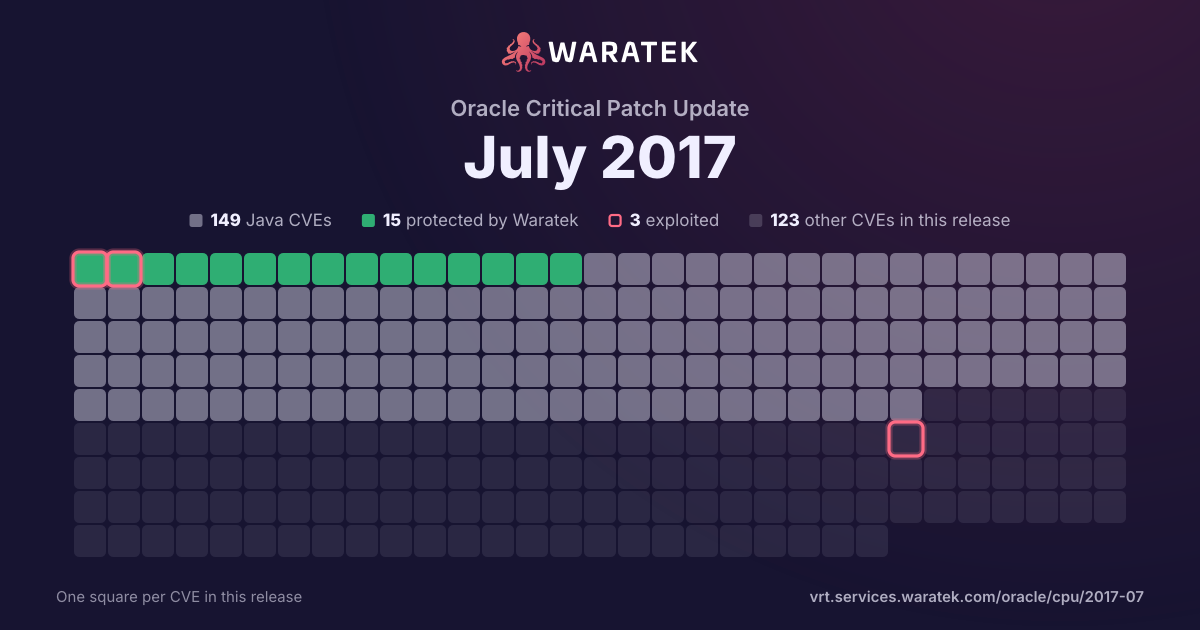
By status
15Protected by Waratek3Mitigation candidate131No exploit published30Outside Waratek scope93Not applicable
3Exploited, marked by the ring
No exploit published. For 126 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 149 matches · 15 protected · 2 exploited · 1 CISA KEV · 6 public PoC · 2 EPSS ≥ 0.5
Protected by Waratek
15
10.1%
Rule in development
0
0.0%
Mitigation candidate
3
2.0%
No exploit published
131
87.9%
blocked by ARMR today
15
10.1%
partly blocked
0
0.0%
not blocked
134
89.9%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 139 / quarter
Q1 151
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Q2 150
Q3 150
Q4 150
Q1 161
Protected by Waratek1
Critical1
blocked by ARMR today1
Proof of concept only1
Q2 160
Q3 162
Protected by Waratek1
No exploit published1
High2
blocked by ARMR today1
not blocked1
No public exploit2
Q4 162
Protected by Waratek1
No exploit published1
Critical2
blocked by ARMR today1
not blocked1
No public exploit2
Q1 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q2 172
No exploit published2
Critical1
High1
not blocked2
No public exploit2
Q3 17139
Protected by Waratek9
Mitigation candidate3
No exploit published127
Critical2
High45
Medium90
Low2
blocked by ARMR today9
not blocked130
Working exploit published3
No public exploit136
Q4 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q1 15Q2 15Q3 15Q4 15Q1 16Q2 16Q3 16Q4 16Q1 17Q2 17Q3 17Q4 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-7501 | Critical | 2017-11-09 | Protected by Waratek | Exploited | Red Hat JBoss A-MQ 6.x; BPM Suite (BPMS) 6.x; BRMS 6.x and 5.x; Data Grid (JDG) 6.x; Data Virtualization (JDV) 6.x and 5.x; Enterprise Application Platform 6.x, 5.x, and 4.3.x; Fuse 6.x; Fuse Service Works (FSW) 6.x; Operations Network (JBoss ON) 3.x; Portal 6.x; SOA Platform (SOA-P) 5.x; Web Server (JWS) 3.x; Red Hat OpenShift/xPAAS 3.x; and Red Hat Subscription Asset Manager 1.3 allow remote attackers to execute arbitrary commands via a crafted serialized Java object, related to the Apache Commons Collections (ACC) library. |
| CVE-2017-3562 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Applications DBA component of Oracle E-Business Suite (subcomponent: AD Utilities). Supported versions that are affected are 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Applications DBA. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Applications DBA accessible data as well as unauthorized access to critical data or complete access to all Oracle Applications DBA accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-10258 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PRTL Interaction Hub component of Oracle PeopleSoft Products (subcomponent: Add New Image). The supported version that is affected is 9.1.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PRTL Interaction Hub. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PRTL Interaction Hub, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PRTL Interaction Hub accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PRTL Interaction Hub accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10257 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PRTL Interaction Hub component of Oracle PeopleSoft Products (subcomponent: Browse Folder Hierarchy). The supported version that is affected is 9.1.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PRTL Interaction Hub. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PRTL Interaction Hub, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PRTL Interaction Hub accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PRTL Interaction Hub accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10256 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PRTL Interaction Hub component of Oracle PeopleSoft Products (subcomponent: EPPCM_HIER_TOP). The supported version that is affected is 9.1.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PRTL Interaction Hub. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PRTL Interaction Hub, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PRTL Interaction Hub accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PRTL Interaction Hub accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10255 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PRTL Interaction Hub component of Oracle PeopleSoft Products (subcomponent: EPPCM_HIER_TOP). The supported version that is affected is 9.1.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PRTL Interaction Hub. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PRTL Interaction Hub, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PRTL Interaction Hub accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PRTL Interaction Hub accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10254 | Low | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FSCM component of Oracle PeopleSoft Products (subcomponent: Staffing Front Office). The supported version that is affected is 9.2. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise FSCM. Successful attacks of this vulnerability can result in unauthorized read access to a subset of PeopleSoft Enterprise FSCM accessible data. CVSS 3.0 Base Score 2.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-10253 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Pivot Grid). Supported versions that are affected are 8.54 and 8.55. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PeopleTools, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PeopleTools accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10252 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Updates Change Assistant). Supported versions that are affected are 8.54 and 8.55. Difficult to exploit vulnerability allows low privileged attacker with logon to the infrastructure where PeopleSoft Enterprise PeopleTools executes to compromise PeopleSoft Enterprise PeopleTools. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 4.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10251 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Test Framework). Supported versions that are affected are 8.54 and 8.55. Difficult to exploit vulnerability allows low privileged attacker with logon to the infrastructure where PeopleSoft Enterprise PeopleTools executes to compromise PeopleSoft Enterprise PeopleTools. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 4.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10250 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Tuxedo). Supported versions that are affected are 8.54 and 8.55. Difficult to exploit vulnerability allows low privileged attacker with logon to the infrastructure where PeopleSoft Enterprise PeopleTools executes to compromise PeopleSoft Enterprise PeopleTools. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 4.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10249 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Integration Broker). Supported versions that are affected are 8.54 and 8.55. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PeopleTools, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PeopleTools accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10248 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PRTL Interaction Hub component of Oracle PeopleSoft Products (subcomponent: EPPCM_HIER_TOP). The supported version that is affected is 9.1.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PRTL Interaction Hub. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PRTL Interaction Hub, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PRTL Interaction Hub accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PRTL Interaction Hub accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10247 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PRTL Interaction Hub component of Oracle PeopleSoft Products (subcomponent: HTML Area). The supported version that is affected is 9.1.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PRTL Interaction Hub. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PRTL Interaction Hub, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PRTL Interaction Hub accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PRTL Interaction Hub accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10246 | High | 2017-08-08 | Mitigation candidate | Working exploit published | Vulnerability in the Oracle Application Object Library component of Oracle E-Business Suite (subcomponent: iHelp). Supported versions that are affected are 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Application Object Library. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Application Object Library accessible data as well as unauthorized update, insert or delete access to some of Oracle Application Object Library accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:L/A:N). |
| CVE-2017-10245 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle General Ledger component of Oracle E-Business Suite (subcomponent: Account Hierarchy Manager). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle General Ledger. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle General Ledger accessible data. CVSS 3.0 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10244 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Application Object Library component of Oracle E-Business Suite (subcomponent: Attachments). Supported versions that are affected are 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Application Object Library. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Application Object Library accessible data. CVSS 3.0 Base Score 5.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-10243 | Medium | 2017-08-08 | Protected by Waratek | No public exploit | Vulnerability in the Java SE, Java SE Embedded, JRockit component of Oracle Java SE (subcomponent: JAX-WS). Supported versions that are affected are Java SE: 6u151, 7u141 and 8u131; Java SE Embedded: 8u131; JRockit: R28.3.14. Easily exploitable vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE, Java SE Embedded, JRockit. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Java SE, Java SE Embedded, JRockit accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Java SE, Java SE Embedded, JRockit. Note: This vulnerability can be exploited through sandboxed Java Web Start applications and sandboxed Java applets. It can also be exploited by supplying data to APIs in the specified Component without using sandboxed Java Web Start applications or sandboxed Java applets, such as through a web service. CVSS 3.0 Base Score 6.5 (Confidentiality and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:L). |
| CVE-2017-10228 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality Cruise Shipboard Property Management System component of Oracle Hospitality Applications (subcomponent: Module). The supported version that is affected is 8.0.0.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Hospitality Cruise Shipboard Property Management System. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Hospitality Cruise Shipboard Property Management System accessible data as well as unauthorized read access to a subset of Oracle Hospitality Cruise Shipboard Property Management System accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-10219 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality Guest Access component of Oracle Hospitality Applications (subcomponent: Base). Supported versions that are affected are 4.2.0.0 and 4.2.1.0. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Hospitality Guest Access executes to compromise Oracle Hospitality Guest Access. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Hospitality Guest Access accessible data. CVSS 3.0 Base Score 5.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10218 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality Guest Access component of Oracle Hospitality Applications (subcomponent: Base). Supported versions that are affected are 4.2.0.0 and 4.2.1.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Hospitality Guest Access. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Hospitality Guest Access accessible data. CVSS 3.0 Base Score 4.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-10217 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality Guest Access component of Oracle Hospitality Applications (subcomponent: Base). Supported versions that are affected are 4.2.0.0 and 4.2.1.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Hospitality Guest Access. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Hospitality Guest Access accessible data. CVSS 3.0 Base Score 4.3 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2017-10215 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PRTL Interaction Hub component of Oracle PeopleSoft Products (subcomponent: EPPCM_DEFN_CATG). The supported version that is affected is 9.1.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PRTL Interaction Hub. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PRTL Interaction Hub, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PRTL Interaction Hub accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PRTL Interaction Hub accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10214 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Retail Xstore Point of Service component of Oracle Retail Applications (subcomponent: Xstore Office). Supported versions that are affected are 6.0.x, 6.5.x, 7.0.x, 7.1.x, 15.0.x and 16.0.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Retail Xstore Point of Service. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Retail Xstore Point of Service accessible data as well as unauthorized update, insert or delete access to some of Oracle Retail Xstore Point of Service accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:L/A:N). |
| CVE-2017-10199 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle iLearning component of Oracle iLearning (subcomponent: Learner Pages). The supported version that is affected is 6.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle iLearning. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle iLearning, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle iLearning accessible data as well as unauthorized update, insert or delete access to some of Oracle iLearning accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10198 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Java SE, Java SE Embedded, JRockit component of Oracle Java SE (subcomponent: Security). Supported versions that are affected are Java SE: 6u151, 7u141 and 8u131; Java SE Embedded: 8u131; JRockit: R28.3.14. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE, Java SE Embedded, JRockit. While the vulnerability is in Java SE, Java SE Embedded, JRockit, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Java SE, Java SE Embedded, JRockit accessible data. Note: This vulnerability can be exploited through sandboxed Java Web Start applications and sandboxed Java applets. It can also be exploited by supplying data to APIs in the specified Component without using sandboxed Java Web Start applications or sandboxed Java applets, such as through a web service. CVSS 3.0 Base Score 6.8 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:C/C:H/I:N/A:N). |
| CVE-2017-10192 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle iStore component of Oracle E-Business Suite (subcomponent: Shopping Cart). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle iStore. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle iStore accessible data. CVSS 3.0 Base Score 5.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-10191 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Web Analytics component of Oracle E-Business Suite (subcomponent: Common Libraries). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Web Analytics. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Web Analytics, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Web Analytics accessible data as well as unauthorized update, insert or delete access to some of Oracle Web Analytics accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10186 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle iStore component of Oracle E-Business Suite (subcomponent: User and Company Profile). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle iStore. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle iStore accessible data. CVSS 3.0 Base Score 5.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-10185 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle CRM Technical Foundation component of Oracle E-Business Suite (subcomponent: User Management). Supported versions that are affected are 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle CRM Technical Foundation. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle CRM Technical Foundation, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle CRM Technical Foundation accessible data as well as unauthorized update, insert or delete access to some of Oracle CRM Technical Foundation accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10184 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Field Service component of Oracle E-Business Suite (subcomponent: Wireless/WAP). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Field Service. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Field Service accessible data. CVSS 3.0 Base Score 5.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-10183 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Retail Xstore Point of Service component of Oracle Retail Applications (subcomponent: Point of Sale). Supported versions that are affected are 6.0.x, 6.5.x, 7.0.x, 7.1.x, 15.0.x and 16.0.0. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Retail Xstore Point of Service. While the vulnerability is in Oracle Retail Xstore Point of Service, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Retail Xstore Point of Service accessible data as well as unauthorized read access to a subset of Oracle Retail Xstore Point of Service accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Retail Xstore Point of Service. CVSS 3.0 Base Score 6.5 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:C/C:L/I:L/A:L). |
| CVE-2017-10182 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality OPERA 5 Property Services component of Oracle Hospitality Applications (subcomponent: OPERA Export Functionality). Supported versions that are affected are 5.4.0.x, 5.4.1.x and 5.4.3.x. Difficult to exploit vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Hospitality OPERA 5 Property Services. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Hospitality OPERA 5 Property Services accessible data. CVSS 3.0 Base Score 4.4 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:H/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10181 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Direct Banking component of Oracle Financial Services Applications (subcomponent: Forgot Password). Supported versions that are affected are 12.0.2 and 12.0.3. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Direct Banking. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle FLEXCUBE Direct Banking as well as unauthorized update, insert or delete access to some of Oracle FLEXCUBE Direct Banking accessible data and unauthorized read access to a subset of Oracle FLEXCUBE Direct Banking accessible data. CVSS 3.0 Base Score 6.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:U/C:L/I:L/A:H). |
| CVE-2017-10180 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle CRM Technical Foundation component of Oracle E-Business Suite (subcomponent: CMRO). Supported versions that are affected are 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle CRM Technical Foundation. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle CRM Technical Foundation, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle CRM Technical Foundation accessible data as well as unauthorized update, insert or delete access to some of Oracle CRM Technical Foundation accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10179 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Application Management Pack for Oracle E-Business Suite component of Oracle E-Business Suite (subcomponent: User Monitoring). Supported versions that are affected are AMP 12.1.0.4.0 and AMP 13.1.1.1.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Application Management Pack for Oracle E-Business Suite. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Application Management Pack for Oracle E-Business Suite accessible data as well as unauthorized read access to a subset of Application Management Pack for Oracle E-Business Suite accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-10178 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: Web Container). Supported versions that are affected are 10.3.6.0, 12.1.3.0, 12.2.1.1 and 12.2.1.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebLogic Server. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle WebLogic Server, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle WebLogic Server accessible data as well as unauthorized read access to a subset of Oracle WebLogic Server accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10177 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Application Object Library component of Oracle E-Business Suite (subcomponent: Flexfields). The supported version that is affected is 12.2.6. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Application Object Library. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Application Object Library accessible data as well as unauthorized access to critical data or complete access to all Oracle Application Object Library accessible data. CVSS 3.0 Base Score 8.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-10176 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Java SE, Java SE Embedded, JRockit component of Oracle Java SE (subcomponent: Security). Supported versions that are affected are Java SE: 7u141 and 8u131; Java SE Embedded: 8u131; JRockit: R28.3.14. Easily exploitable vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE, Java SE Embedded, JRockit. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Java SE, Java SE Embedded, JRockit accessible data. Note: This vulnerability can be exploited through sandboxed Java Web Start applications and sandboxed Java applets. It can also be exploited by supplying data to APIs in the specified Component without using sandboxed Java Web Start applications or sandboxed Java applets, such as through a web service. CVSS 3.0 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10175 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle iSupport component of Oracle E-Business Suite (subcomponent: Profiles). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle iSupport. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle iSupport accessible data. CVSS 3.0 Base Score 4.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-10174 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle iSupport component of Oracle E-Business Suite (subcomponent: Service Request). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle iSupport. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle iSupport, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle iSupport accessible data as well as unauthorized update, insert or delete access to some of Oracle iSupport accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10173 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Retail Open Commerce Platform component of Oracle Retail Applications (subcomponent: Website). Supported versions that are affected are 5.0, 5.1, 5.2, 5.3, 6.0, 6.1, 15.0 and 15.1. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Retail Open Commerce Platform. While the vulnerability is in Oracle Retail Open Commerce Platform, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Retail Open Commerce Platform accessible data. CVSS 3.0 Base Score 5.8 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:C/C:N/I:L/A:N). |
| CVE-2017-10172 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Retail Open Commerce Platform component of Oracle Retail Applications (subcomponent: Framework). Supported versions that are affected are 5.0, 5.1, 5.2, 5.3, 6.0, 6.1, 15.0 and 15.1. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Retail Open Commerce Platform. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Retail Open Commerce Platform, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Retail Open Commerce Platform accessible data as well as unauthorized read access to a subset of Oracle Retail Open Commerce Platform accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10171 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Marketing component of Oracle E-Business Suite (subcomponent: Home Page). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Marketing. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Marketing, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Marketing accessible data as well as unauthorized update, insert or delete access to some of Oracle Marketing accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10170 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Field Service component of Oracle E-Business Suite (subcomponent: Wireless/WAP). Supported versions that are affected are 12.1.1, 12.1.2 and 12.1.3. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Field Service. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Field Service, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Field Service accessible data as well as unauthorized update, insert or delete access to some of Oracle Field Service accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10160 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Primavera P6 Enterprise Project Portfolio Management component of Oracle Primavera Products Suite (subcomponent: Web Access). Supported versions that are affected are 8.3, 8.4, 15.1, 15.2, 16.1 and 16.2. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Primavera P6 Enterprise Project Portfolio Management. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Primavera P6 Enterprise Project Portfolio Management accessible data. CVSS 3.0 Base Score 4.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-10157 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the BI Publisher component of Oracle Fusion Middleware (subcomponent: BI Publisher Security). Supported versions that are affected are 11.1.1.7.0, 11.1.1.9.0, 12.2.1.1.0 and 12.2.1.2.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise BI Publisher. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of BI Publisher accessible data as well as unauthorized read access to a subset of BI Publisher accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-10156 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the BI Publisher component of Oracle Fusion Middleware (subcomponent: BI Publisher Security). Supported versions that are affected are 11.1.1.7.0, 11.1.1.9.0, 12.2.1.1.0 and 12.2.1.2.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise BI Publisher. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in BI Publisher, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all BI Publisher accessible data as well as unauthorized update, insert or delete access to some of BI Publisher accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10150 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Primavera Unifier component of Oracle Primavera Products Suite (subcomponent: Platform). Supported versions that are affected are 9.13, 9.14, 10.1, 10.2, 15.1, 15.2, 16.1 and 16.2. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Primavera Unifier. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Primavera Unifier accessible data. CVSS 3.0 Base Score 4.3 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2017-10149 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Primavera Unifier component of Oracle Primavera Products Suite (subcomponent: Platform). Supported versions that are affected are 9.13, 9.14, 10.1, 10.2, 15.1, 15.2, 16.1 and 16.2. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Primavera Unifier. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Primavera Unifier, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Primavera Unifier accessible data as well as unauthorized read access to a subset of Primavera Unifier accessible data. CVSS 3.0 Base Score 4.8 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10148 | Medium | 2017-08-08 | Protected by Waratek | No public exploit | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: Core Components). Supported versions that are affected are 10.3.6.0, 12.1.3.0, 12.2.1.1 and 12.2.1.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via T3 to compromise Oracle WebLogic Server. While the vulnerability is in Oracle WebLogic Server, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle WebLogic Server accessible data. CVSS 3.0 Base Score 5.8 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:C/C:N/I:L/A:N). NOTE: the previous information is from the July 2017 CPU. Oracle has not commented on third-party claims that this issue allows remote attackers to inject special data into log files via a crafted T3 request. |
| CVE-2017-10147 | High | 2017-08-08 | Protected by Waratek | No public exploit | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: Core Components). Supported versions that are affected are 10.3.6.0, 12.1.3.0, 12.2.1.1 and 12.2.1.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via T3 to compromise Oracle WebLogic Server. While the vulnerability is in Oracle WebLogic Server, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle WebLogic Server. CVSS 3.0 Base Score 8.6 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:C/C:N/I:N/A:H). NOTE: the previous information is from the July 2017 CPU. Oracle has not commented on third-party claims that this issue exists in the migrate functionality in the WebLogic/cluster/singleton/ServerMigrationCoordinator class and allows remote attackers to shutdown the server via a crafted T3 request. |
| CVE-2017-10146 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Portal). Supported versions that are affected are 8.54 and 8.55. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. While the vulnerability is in PeopleSoft Enterprise PeopleTools, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PeopleTools accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of PeopleSoft Enterprise PeopleTools. CVSS 3.0 Base Score 8.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:C/C:L/I:L/A:L). |
| CVE-2017-10145 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Java Advanced Management Console component of Oracle Java SE (subcomponent: Server). The supported version that is affected is Java Advanced Management Console: 2.6. Easily exploitable vulnerability allows low privileged attacker with network access via multiple protocols to compromise Java Advanced Management Console. While the vulnerability is in Java Advanced Management Console, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Java Advanced Management Console accessible data as well as unauthorized read access to a subset of Java Advanced Management Console accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Java Advanced Management Console. CVSS 3.0 Base Score 7.4 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:L/I:L/A:L). |
| CVE-2017-10144 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Applications Manager component of Oracle E-Business Suite (subcomponent: Oracle Diagnostics Interfaces). The supported version that is affected is 12.1.3. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Applications Manager. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Applications Manager. CVSS 3.0 Base Score 7.5 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-10143 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle CRM Technical Foundation component of Oracle E-Business Suite (subcomponent: Preferences). Supported versions that are affected are 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle CRM Technical Foundation. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle CRM Technical Foundation, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle CRM Technical Foundation accessible data as well as unauthorized update, insert or delete access to some of Oracle CRM Technical Foundation accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10142 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality Reporting and Analytics component of Oracle Hospitality Applications (subcomponent: Mobile Apps). Supported versions that are affected are 8.5.1 and 9.0.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Hospitality Reporting and Analytics. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Hospitality Reporting and Analytics accessible data as well as unauthorized read access to a subset of Oracle Hospitality Reporting and Analytics accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-10137 | Critical | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: JNDI). Supported versions that are affected are 10.3.6.0 and 12.1.3.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebLogic Server. While the vulnerability is in Oracle WebLogic Server, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Oracle WebLogic Server. CVSS 3.0 Base Score 10.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2017-10135 | Medium | 2017-08-08 | Protected by Waratek | No public exploit | Vulnerability in the Java SE, Java SE Embedded, JRockit component of Oracle Java SE (subcomponent: JCE). Supported versions that are affected are Java SE: 6u151, 7u141 and 8u131; Java SE Embedded: 8u131; JRockit: R28.3.14. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE, Java SE Embedded, JRockit. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Java SE, Java SE Embedded, JRockit accessible data. Note: This vulnerability can be exploited through sandboxed Java Web Start applications and sandboxed Java applets. It can also be exploited by supplying data to APIs in the specified Component without using sandboxed Java Web Start applications or sandboxed Java applets, such as through a web service. CVSS 3.0 Base Score 5.9 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10134 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FSCM component of Oracle PeopleSoft Products (subcomponent: eProcurement). The supported version that is affected is 9.2. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise FSCM. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise FSCM, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise FSCM accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise FSCM accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10131 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Primavera P6 Enterprise Project Portfolio Management component of Oracle Primavera Products Suite (subcomponent: Web Access). Supported versions that are affected are 8.3, 8.4, 15.1, 15.2, 16.1 and 16.2. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Primavera P6 Enterprise Project Portfolio Management. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Primavera P6 Enterprise Project Portfolio Management, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Primavera P6 Enterprise Project Portfolio Management accessible data as well as unauthorized read access to a subset of Primavera P6 Enterprise Project Portfolio Management accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Primavera P6 Enterprise Project Portfolio Management. CVSS 3.0 Base Score 6.5 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:L). |
| CVE-2017-10130 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle iStore component of Oracle E-Business Suite (subcomponent: User Management). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle iStore. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle iStore, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle iStore accessible data as well as unauthorized update, insert or delete access to some of Oracle iStore accessible data. CVSS 3.0 Base Score 7.6 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10126 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PRTL Interaction Hub component of Oracle PeopleSoft Products (subcomponent: HTML Area). The supported version that is affected is 9.1.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PRTL Interaction Hub. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PRTL Interaction Hub, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PRTL Interaction Hub accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PRTL Interaction Hub accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10123 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: Web Container). The supported version that is affected is 12.1.3.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle WebLogic Server. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle WebLogic Server accessible data. CVSS 3.0 Base Score 4.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-10121 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Java Advanced Management Console component of Oracle Java SE (subcomponent: Server). The supported version that is affected is Java Advanced Management Console: 2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Java Advanced Management Console. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Java Advanced Management Console, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Java Advanced Management Console accessible data as well as unauthorized read access to a subset of Java Advanced Management Console accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10119 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Service Bus component of Oracle Fusion Middleware (subcomponent: OSB Web Console Design, Admin). The supported version that is affected is 11.1.1.9.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Service Bus. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Service Bus, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Service Bus accessible data as well as unauthorized update, insert or delete access to some of Oracle Service Bus accessible data. CVSS 3.0 Base Score 7.6 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10118 | High | 2017-08-08 | Protected by Waratek | No public exploit | Vulnerability in the Java SE, Java SE Embedded, JRockit component of Oracle Java SE (subcomponent: JCE). Supported versions that are affected are Java SE: 7u141 and 8u131; Java SE Embedded: 8u131; JRockit: R28.3.14. Easily exploitable vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE, Java SE Embedded, JRockit. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Java SE, Java SE Embedded, JRockit accessible data. Note: This vulnerability can be exploited through sandboxed Java Web Start applications and sandboxed Java applets. It can also be exploited by supplying data to APIs in the specified Component without using sandboxed Java Web Start applications or sandboxed Java applets, such as through a web service. CVSS 3.0 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10117 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Java Advanced Management Console component of Oracle Java SE (subcomponent: Server). The supported version that is affected is Java Advanced Management Console: 2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Java Advanced Management Console. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Java Advanced Management Console accessible data. CVSS 3.0 Base Score 5.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-10116 | High | 2017-08-08 | Protected by Waratek | No public exploit | Vulnerability in the Java SE, Java SE Embedded, JRockit component of Oracle Java SE (subcomponent: Security). Supported versions that are affected are Java SE: 6u151, 7u141 and 8u131; Java SE Embedded: 8u131; JRockit: R28.3.14. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE, Java SE Embedded, JRockit. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Java SE, Java SE Embedded, JRockit, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Java SE, Java SE Embedded, JRockit. Note: This vulnerability can be exploited through sandboxed Java Web Start applications and sandboxed Java applets. It can also be exploited by supplying data to APIs in the specified Component without using sandboxed Java Web Start applications or sandboxed Java applets, such as through a web service. CVSS 3.0 Base Score 8.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:R/S:C/C:H/I:H/A:H). |
| CVE-2017-10115 | High | 2017-08-08 | Protected by Waratek | No public exploit | Vulnerability in the Java SE, Java SE Embedded, JRockit component of Oracle Java SE (subcomponent: JCE). Supported versions that are affected are Java SE: 6u151, 7u141 and 8u131; Java SE Embedded: 8u131; JRockit: R28.3.14. Easily exploitable vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE, Java SE Embedded, JRockit. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Java SE, Java SE Embedded, JRockit accessible data. Note: This vulnerability can be exploited through sandboxed Java Web Start applications and sandboxed Java applets. It can also be exploited by supplying data to APIs in the specified Component without using sandboxed Java Web Start applications or sandboxed Java applets, such as through a web service. CVSS 3.0 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10113 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Common Applications component of Oracle E-Business Suite (subcomponent: CRM User Management Framework). Supported versions that are affected are 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Common Applications. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Common Applications, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Common Applications accessible data as well as unauthorized update, insert or delete access to some of Oracle Common Applications accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10112 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle iStore component of Oracle E-Business Suite (subcomponent: User Registration). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle iStore. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle iStore, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle iStore accessible data as well as unauthorized update, insert or delete access to some of Oracle iStore accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10108 | Medium | 2017-08-08 | Protected by Waratek | No public exploit | Vulnerability in the Java SE, Java SE Embedded, JRockit component of Oracle Java SE (subcomponent: Serialization). Supported versions that are affected are Java SE: 6u151, 7u141 and 8u131; Java SE Embedded: 8u131; JRockit: R28.3.14. Easily exploitable vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE, Java SE Embedded, JRockit. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Java SE, Java SE Embedded, JRockit. Note: This vulnerability can be exploited through sandboxed Java Web Start applications and sandboxed Java applets. It can also be exploited by supplying data to APIs in the specified Component without using sandboxed Java Web Start applications or sandboxed Java applets, such as through a web service. CVSS 3.0 Base Score 5.3 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2017-10106 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Portal). Supported versions that are affected are 8.54 and 8.55. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PeopleTools, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PeopleTools accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10104 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Java Advanced Management Console component of Oracle Java SE (subcomponent: Server). The supported version that is affected is Java Advanced Management Console: 2.6. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Java Advanced Management Console. While the vulnerability is in Java Advanced Management Console, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Java Advanced Management Console accessible data as well as unauthorized read access to a subset of Java Advanced Management Console accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Java Advanced Management Console. CVSS 3.0 Base Score 7.4 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:L/I:L/A:L). |
| CVE-2017-10103 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Miscellaneous). Supported versions that are affected are 2.0.0, 2.0.1, 2.2.0 and 12.0.1. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle FLEXCUBE Private Banking accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10102 | Critical | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Java SE, Java SE Embedded component of Oracle Java SE (subcomponent: RMI). Supported versions that are affected are Java SE: 6u151, 7u141 and 8u131; Java SE Embedded: 8u131. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE, Java SE Embedded. While the vulnerability is in Java SE, Java SE Embedded, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Java SE, Java SE Embedded. Note: This vulnerability can only be exploited by supplying data to APIs in the specified Component without using Untrusted Java Web Start applications or Untrusted Java applets, such as through a web service. CVSS 3.0 Base Score 9.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2017-10100 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PRTL Interaction Hub component of Oracle PeopleSoft Products (subcomponent: HTML Area). The supported version that is affected is 9.1.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PRTL Interaction Hub. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PRTL Interaction Hub, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PRTL Interaction Hub accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PRTL Interaction Hub accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10098 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Universal Banking component of Oracle Financial Services Applications (subcomponent: Infrastructure). Supported versions that are affected are 11.3.0, 11.4.0, 12.0.1, 12.0.2, 12.0.3, 12.1.0, 12.2.0 and 12.3.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Universal Banking. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Universal Banking accessible data as well as unauthorized read access to a subset of Oracle FLEXCUBE Universal Banking accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-10097 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality Reporting and Analytics component of Oracle Hospitality Applications (subcomponent: Reporting). Supported versions that are affected are 8.5.1 and 9.0.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Hospitality Reporting and Analytics. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Hospitality Reporting and Analytics, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Hospitality Reporting and Analytics accessible data as well as unauthorized read access to a subset of Oracle Hospitality Reporting and Analytics accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10094 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Agile PLM component of Oracle Supply Chain Products Suite (subcomponent: Security). Supported versions that are affected are 9.3.5 and 9.3.6. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Agile PLM. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Agile PLM, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Agile PLM accessible data as well as unauthorized read access to a subset of Oracle Agile PLM accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10093 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Agile PLM component of Oracle Supply Chain Products Suite (subcomponent: Security). Supported versions that are affected are 9.3.5 and 9.3.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Agile PLM. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Agile PLM accessible data. CVSS 3.0 Base Score 5.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-10092 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Agile PLM component of Oracle Supply Chain Products Suite (subcomponent: Security). Supported versions that are affected are 9.3.5 and 9.3.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Agile PLM. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Agile PLM, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Agile PLM accessible data as well as unauthorized read access to a subset of Oracle Agile PLM accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10091 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Enterprise Manager Base Platform component of Oracle Enterprise Manager Grid Control (subcomponent: UI Framework). Supported versions that are affected are 12.1.0, 13.1.0 and 13.2.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Enterprise Manager Base Platform. While the vulnerability is in Enterprise Manager Base Platform, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Enterprise Manager Base Platform accessible data. CVSS 3.0 Base Score 7.7 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:N/I:H/A:N). |
| CVE-2017-10088 | Low | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Agile PLM component of Oracle Supply Chain Products Suite (subcomponent: Security). Supported versions that are affected are 9.3.5 and 9.3.6. Easily exploitable vulnerability allows high privileged attacker with logon to the infrastructure where Oracle Agile PLM executes to compromise Oracle Agile PLM. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Agile PLM accessible data as well as unauthorized read access to a subset of Oracle Agile PLM accessible data. CVSS 3.0 Base Score 3.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:H/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-10085 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Universal Banking component of Oracle Financial Services Applications (subcomponent: Infrastructure). Supported versions that are affected are 11.3.0, 11.4.0, 12.0.1, 12.0.2, 12.0.3, 12.1.0, 12.2.0 and 12.3.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Universal Banking. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle FLEXCUBE Universal Banking accessible data as well as unauthorized update, insert or delete access to some of Oracle FLEXCUBE Universal Banking accessible data. CVSS 3.0 Base Score 7.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:L/A:N). |
| CVE-2017-10084 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Universal Banking component of Oracle Financial Services Applications (subcomponent: Report Generator). Supported versions that are affected are 11.3.0, 11.4.0, 12.0.1, 12.0.2, 12.0.3, 12.1.0, 12.2.0 and 12.3.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Universal Banking. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle FLEXCUBE Universal Banking accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10083 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Universal Banking component of Oracle Financial Services Applications (subcomponent: Infrastructure). Supported versions that are affected are 11.3.0, 11.4.0, 12.0.1, 12.0.2, 12.0.3, 12.1.0, 12.2.0 and 12.3.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle FLEXCUBE Universal Banking. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle FLEXCUBE Universal Banking, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Universal Banking accessible data as well as unauthorized read access to a subset of Oracle FLEXCUBE Universal Banking accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10082 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Agile PLM component of Oracle Supply Chain Products Suite (subcomponent: Security). Supported versions that are affected are 9.3.5 and 9.3.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Agile PLM. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Agile PLM, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Agile PLM accessible data as well as unauthorized read access to a subset of Oracle Agile PLM accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10080 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Agile PLM component of Oracle Supply Chain Products Suite (subcomponent: Security). Supported versions that are affected are 9.3.5 and 9.3.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Agile PLM. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Agile PLM, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Agile PLM accessible data as well as unauthorized read access to a subset of Oracle Agile PLM accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10078 | High | 2017-08-08 | Protected by Waratek | No public exploit | Vulnerability in the Java SE component of Oracle Java SE (subcomponent: Scripting). The supported version that is affected is Java SE: 8u131. Easily exploitable vulnerability allows low privileged attacker with network access via multiple protocols to compromise Java SE. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Java SE accessible data as well as unauthorized access to critical data or complete access to all Java SE accessible data. Note: This vulnerability can be exploited through sandboxed Java Web Start applications and sandboxed Java applets. It can also be exploited by supplying data to APIs in the specified Component without using sandboxed Java Web Start applications or sandboxed Java applets, such as through a web service. CVSS 3.0 Base Score 8.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-10075 | High | 2017-08-08 | Mitigation candidate | Working exploit published | Vulnerability in the Oracle WebCenter Content component of Oracle Fusion Middleware (subcomponent: Content Server). Supported versions that are affected are 11.1.1.9.0, 12.2.1.1.0 and 12.2.1.2.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebCenter Content. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle WebCenter Content, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle WebCenter Content accessible data as well as unauthorized update, insert or delete access to some of Oracle WebCenter Content accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10073 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Universal Banking component of Oracle Financial Services Applications (subcomponent: Infrastructure). Supported versions that are affected are 11.3.0, 11.4.0, 12.0.1, 12.0.2, 12.0.3, 12.1.0, 12.2.0 and 12.3.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Universal Banking. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle FLEXCUBE Universal Banking, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Universal Banking accessible data as well as unauthorized read access to a subset of Oracle FLEXCUBE Universal Banking accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10072 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Universal Banking component of Oracle Financial Services Applications (subcomponent: All Modules). Supported versions that are affected are 11.3.0, 11.4.0, 12.0.1, 12.0.2, 12.0.3, 12.1.0, 12.2.0 and 12.3.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Universal Banking. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Universal Banking accessible data as well as unauthorized read access to a subset of Oracle FLEXCUBE Universal Banking accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-10071 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Universal Banking component of Oracle Financial Services Applications (subcomponent: All Modules). Supported versions that are affected are 11.3.0, 11.4.0, 12.0.1, 12.0.2, 12.0.3, 12.1.0, 12.2.0 and 12.3.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle FLEXCUBE Universal Banking. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Universal Banking accessible data. CVSS 3.0 Base Score 4.3 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:U/C:N/I:L/A:N). |
| CVE-2017-10070 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PRTL Interaction Hub component of Oracle PeopleSoft Products (subcomponent: Maintenance Folders). The supported version that is affected is 9.1.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PRTL Interaction Hub. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PRTL Interaction Hub, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PRTL Interaction Hub accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PRTL Interaction Hub accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10069 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Payment Interface component of Oracle Hospitality Applications (subcomponent: Core). The supported version that is affected is 6.1.1. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Payment Interface. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Payment Interface accessible data. CVSS 3.0 Base Score 5.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10063 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: Web Services). Supported versions that are affected are 10.3.6.0, 12.1.3.0, 12.2.1.1 and 12.2.1.2. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebLogic Server. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle WebLogic Server accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle WebLogic Server. CVSS 3.0 Base Score 4.8 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:N/I:L/A:L). |
| CVE-2017-10061 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Integration Broker). Supported versions that are affected are 8.54 and 8.55. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. While the vulnerability is in PeopleSoft Enterprise PeopleTools, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PeopleTools accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of PeopleSoft Enterprise PeopleTools. CVSS 3.0 Base Score 8.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:C/C:L/I:L/A:L). |
| CVE-2017-10059 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the BI Publisher component of Oracle Fusion Middleware (subcomponent: Mobile Service). The supported version that is affected is 11.1.1.7.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise BI Publisher. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in BI Publisher, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all BI Publisher accessible data as well as unauthorized update, insert or delete access to some of BI Publisher accessible data. CVSS 3.0 Base Score 7.6 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:H/I:L/A:N). |