
Oracle Critical Patch Update April 2017
Released April 2017 · Oracle's advisory ↗ · ← Critical Patch Update, January 2017 · Critical Patch Update, July 2017 →
227 CVEs in this release, one square each
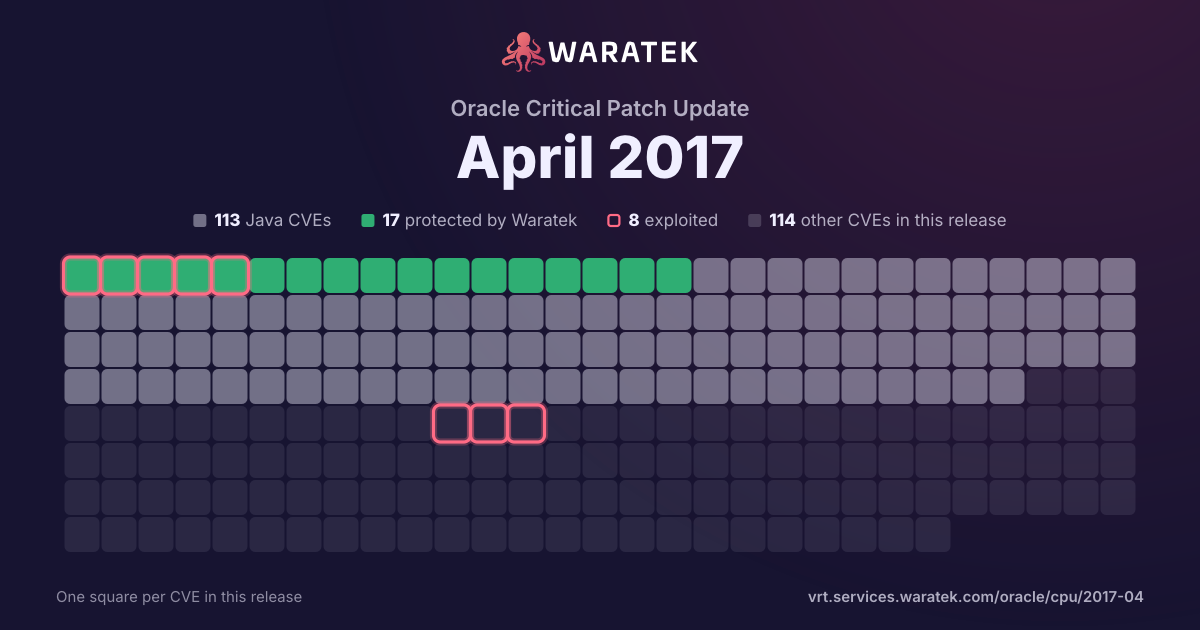
By status
17Protected by Waratek1Mitigation candidate95No exploit published13Outside Waratek scope101Not applicable
8Exploited, marked by the ring
No exploit published. For 93 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 113 matches · 17 protected · 5 exploited · 3 CISA KEV · 9 public PoC · 7 EPSS ≥ 0.5
Protected by Waratek
17
15.0%
Rule in development
0
0.0%
Mitigation candidate
1
0.9%
No exploit published
95
84.1%
blocked by ARMR today
17
15.0%
partly blocked
0
0.0%
not blocked
96
85.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
5
4.4%
Working exploit published
4
3.5%
Proof of concept only
0
0.0%
Forecast only
1
0.9%
No public exploit
103
91.2%
split by
peak 102 / quarter
Q2 141
Protected by Waratek1
High1
blocked by ARMR today1
Exploited1
Q3 141
No exploit published1
Medium1
not blocked1
No public exploit1
Q4 140
Q1 150
Q2 150
Q3 150
Q4 151
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q1 160
Q2 162
Protected by Waratek2
High2
blocked by ARMR today2
Forecast only1
No public exploit1
Q3 163
Protected by Waratek1
No exploit published2
Critical1
High2
blocked by ARMR today1
not blocked2
No public exploit3
Q4 161
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Q1 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q2 17102
Protected by Waratek9
Mitigation candidate1
No exploit published92
Critical4
High36
Medium55
Low7
blocked by ARMR today9
not blocked93
Exploited1
Working exploit published4
No public exploit97
Q3 170
Q4 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q2 14Q4 14Q2 15Q4 15Q2 16Q4 16Q2 17Q4 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2017-3288 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Investor Servicing component of Oracle Financial Services Applications (subcomponent: Unit Trust). Supported versions that are affected are 12.0.1, 12.0.2, 12.0.3, 12.0.4, 12.1.0, 12.2.0 and 12.3.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Investor Servicing. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Investor Servicing accessible data as well as unauthorized read access to a subset of Oracle FLEXCUBE Investor Servicing accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-3254 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Retail Invoice Matching component of Oracle Retail Applications (subcomponent: Security). Supported versions that are affected are 12.0 and 13.0. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Retail Invoice Matching. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Retail Invoice Matching accessible data as well as unauthorized update, insert or delete access to some of Oracle Retail Invoice Matching accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Retail Invoice Matching. CVSS 3.0 Base Score 7.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:L/A:L). |
| CVE-2017-3230 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Fusion Middleware MapViewer component of Oracle Fusion Middleware (subcomponent: Map Builder). Supported versions that are affected are 11.1.1.9, 12.2.1.1 and 12.2.1.2. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Fusion Middleware MapViewer. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Fusion Middleware MapViewer accessible data as well as unauthorized read access to a subset of Oracle Fusion Middleware MapViewer accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Fusion Middleware MapViewer. CVSS 3.0 Base Score 8.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:H/A:L). |
| CVE-2017-5638 | Critical | 2017-03-11 | Protected by Waratek | Exploited | The Jakarta Multipart parser in Apache Struts 2 2.3.x before 2.3.32 and 2.5.x before 2.5.10.1 has incorrect exception handling and error-message generation during file-upload attempts, which allows remote attackers to execute arbitrary commands via a crafted Content-Type, Content-Disposition, or Content-Length HTTP header, as exploited in the wild in March 2017 with a Content-Type header containing a #cmd= string. |
| CVE-2016-5019 | Critical | 2016-10-03 | Protected by Waratek | No public exploit | CoreResponseStateManager in Apache MyFaces Trinidad 1.0.0 through 1.0.13, 1.2.x before 1.2.15, 2.0.x before 2.0.2, and 2.1.x before 2.1.2 might allow attackers to conduct deserialization attacks via a crafted serialized view state string. |
| CVE-2016-3607 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle GlassFish Server component in Oracle Fusion Middleware 3.0.1 and 3.1.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Web Container. |
| CVE-2016-3092 | High | 2016-07-04 | No exploit published | No public exploit | The MultipartStream class in Apache Commons Fileupload before 1.3.2, as used in Apache Tomcat 7.x before 7.0.70, 8.x before 8.0.36, 8.5.x before 8.5.3, and 9.x before 9.0.0.M7 and other products, allows remote attackers to cause a denial of service (CPU consumption) via a long boundary string. |
| CVE-2016-1181 | High | 2016-07-04 | Protected by Waratek | No public exploit | ActionServlet.java in Apache Struts 1 1.x through 1.3.10 mishandles multithreaded access to an ActionForm instance, which allows remote attackers to execute arbitrary code or cause a denial of service (unexpected memory access) via a multipart request, a related issue to CVE-2015-0899. |
| CVE-2016-3674 | High | 2016-05-17 | Protected by Waratek | No public exploit | Multiple XML external entity (XXE) vulnerabilities in the (1) Dom4JDriver, (2) DomDriver, (3) JDomDriver, (4) JDom2Driver, (5) SjsxpDriver, (6) StandardStaxDriver, and (7) WstxDriver drivers in XStream before 1.4.9 allow remote attackers to read arbitrary files via a crafted XML document. |
| CVE-2016-2510 | High | 2016-04-07 | Protected by Waratek | Forecast only | BeanShell (bsh) before 2.0b6, when included on the classpath by an application that uses Java serialization or XStream, allows remote attackers to execute arbitrary code via crafted serialized data, related to XThis.Handler. |
| CVE-2015-4852 | Critical | 2015-11-18 | Protected by Waratek | Exploited | The WLS Security component in Oracle WebLogic Server 10.3.6.0, 12.1.2.0, 12.1.3.0, and 12.2.1.0 allows remote attackers to execute arbitrary commands via a crafted serialized Java object in T3 protocol traffic to TCP port 7001, related to oracle_common/modules/com.bea.core.apache.commons.collections.jar. NOTE: the scope of this CVE is limited to the WebLogic Server product. |
| CVE-2014-3596 | Medium | 2014-08-27 | No exploit published | No public exploit | The getCN function in Apache Axis 1.4 and earlier does not properly verify that the server hostname matches a domain name in the subject's Common Name (CN) or subjectAltName field of the X.509 certificate, which allows man-in-the-middle attackers to spoof SSL servers via a certificate with a subject that specifies a common name in a field that is not the CN field. NOTE: this issue exists because of an incomplete fix for CVE-2012-5784. |
| CVE-2014-0114 | High | 2014-04-30 | Protected by Waratek | Exploited | Apache Commons BeanUtils, as distributed in lib/commons-beanutils-1.8.0.jar in Apache Struts 1.x through 1.3.10 and in other products requiring commons-beanutils through 1.9.2, does not suppress the class property, which allows remote attackers to "manipulate" the ClassLoader and execute arbitrary code via the class parameter, as demonstrated by the passing of this parameter to the getClass method of the ActionForm object in Struts 1. |