
Oracle Critical Patch Update January 2023
Released January 2023 · Oracle's advisory ↗ · ← Critical Patch Update, October 2022 · Critical Patch Update, April 2023 →
183 CVEs in this release, one square each
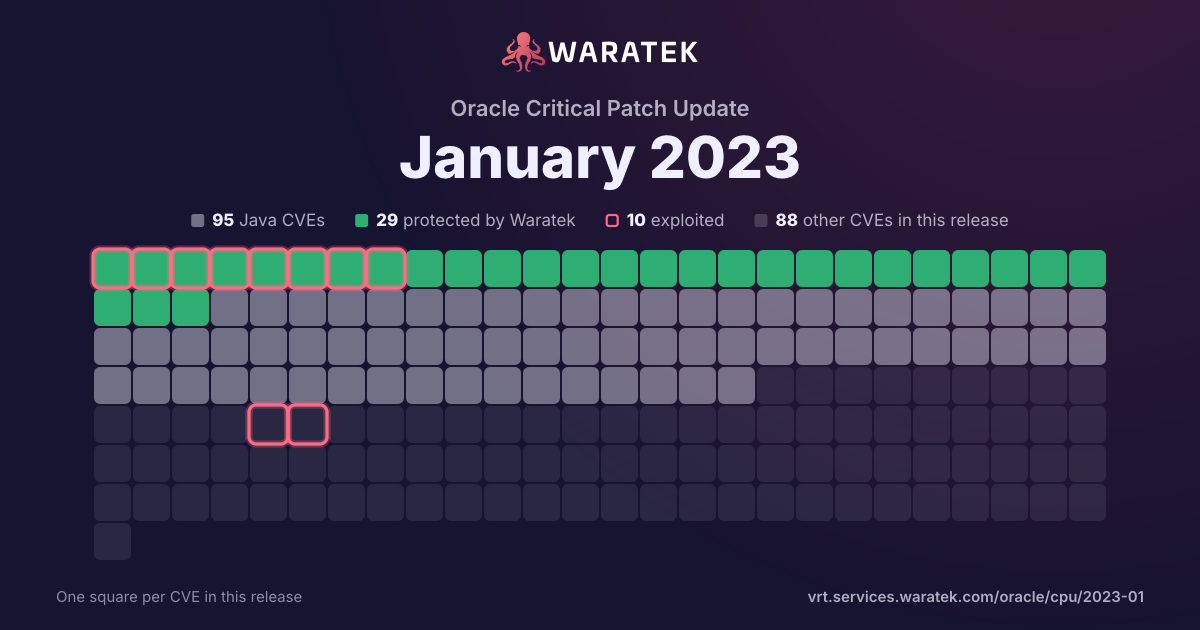
By status
29Protected by Waratek4Mitigation candidate62No exploit published13Outside Waratek scope74Not applicable1Withdrawn CVE
10Exploited, marked by the ring
No exploit published. For 39 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 183 matches · 95 in Waratek scope · 29 protected · 10 exploited · 4 CISA KEV · 18 public PoC · 12 EPSS ≥ 0.5
183matches
95in Waratek scope51.9%
29protected15.8%
10exploited5.5%
4CISA KEV2.2%
18public PoC9.8%
12EPSS ≥ 0.56.6%
Protected by Waratek
29
15.8%
Rule in development
0
0.0%
Mitigation candidate
4
2.2%
No exploit published
62
33.9%
Outside Waratek scope
13
7.1%
Not applicable
74
40.4%
Withdrawn CVE
1
0.5%
blocked by ARMR today
29
15.8%
partly blocked
0
0.0%
not blocked
154
84.2%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
10
5.5%
Working exploit published
0
0.0%
Proof of concept only
26
14.2%
Forecast only
0
0.0%
No public exploit
147
80.3%
split by
peak 74 / quarter
Q1 181
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Q2 181
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q3 180
Q4 180
Q1 191
Not applicable1
Medium1
not blocked1
No public exploit1
Q2 190
Q3 190
Q4 192
Protected by Waratek2
Critical1
Medium1
blocked by ARMR today2
Proof of concept only1
No public exploit1
Q1 200
Q2 202
Protected by Waratek1
No exploit published1
Critical1
Medium1
blocked by ARMR today1
not blocked1
No public exploit2
Q3 200
Q4 202
No exploit published1
Outside Waratek scope1
High1
Medium1
not blocked2
No public exploit2
Q1 214
No exploit published1
Outside Waratek scope1
Not applicable2
Critical1
High3
not blocked4
Proof of concept only1
No public exploit3
Q2 212
Protected by Waratek1
No exploit published1
Medium2
blocked by ARMR today1
not blocked1
No public exploit2
Q3 215
No exploit published2
Not applicable3
High4
Medium1
not blocked5
No public exploit5
Q4 217
Protected by Waratek2
Outside Waratek scope2
Not applicable3
Critical1
High2
Medium4
blocked by ARMR today2
not blocked5
Exploited2
Proof of concept only1
No public exploit4
Q1 2215
Protected by Waratek3
No exploit published3
Outside Waratek scope3
Not applicable6
Critical5
High6
Medium4
blocked by ARMR today3
not blocked12
Exploited1
Proof of concept only5
No public exploit9
Q2 2219
Protected by Waratek7
Mitigation candidate1
No exploit published4
Outside Waratek scope1
Not applicable6
Critical7
High6
Medium6
blocked by ARMR today7
not blocked12
Exploited3
Proof of concept only4
No public exploit12
Q3 2227
Protected by Waratek4
Mitigation candidate2
No exploit published7
Outside Waratek scope3
Not applicable10
Withdrawn CVE1
Critical4
High18
Medium4
Unknown1
blocked by ARMR today4
not blocked23
Proof of concept only9
No public exploit18
Q4 2221
Protected by Waratek3
Mitigation candidate1
No exploit published9
Not applicable8
Critical8
High12
Medium1
blocked by ARMR today3
not blocked18
Exploited2
Proof of concept only5
No public exploit14
Q1 2374
Protected by Waratek4
No exploit published33
Outside Waratek scope2
Not applicable35
Critical1
High24
Medium44
Low5
blocked by ARMR today4
not blocked70
Exploited1
No public exploit73
Q1 18Q3 18Q1 19Q3 19Q1 20Q3 20Q1 21Q3 21Q1 22Q3 22Q1 23
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2022-40150 | High | 2022-09-16 | No exploit published | No public exploit | Those using Jettison to parse untrusted XML or JSON data may be vulnerable to Denial of Service attacks (DOS). If the parser is running on user supplied input, an attacker may supply content that causes the parser to crash by Out of memory. This effect may support a denial of service attack. |
| CVE-2022-40149 | High | 2022-09-16 | No exploit published | No public exploit | Those using Jettison to parse untrusted XML or JSON data may be vulnerable to Denial of Service attacks (DOS). If the parser is running on user supplied input, an attacker may supply content that causes the parser to crash by stackoverflow. This effect may support a denial of service attack. |
| CVE-2022-2526 | Critical | 2022-09-09 | Outside Waratek scope | No public exploit | A use-after-free vulnerability was found in systemd. This issue occurs due to the on_stream_io() function and dns_stream_complete() function in 'resolved-dns-stream.c' not incrementing the reference counting for the DnsStream object. Therefore, other functions and callbacks called can dereference the DNSStream object, causing the use-after-free when the reference is still used later. |
| CVE-2020-10735 | High | 2022-09-09 | Not applicable | No public exploit | A flaw was found in python. In algorithms with quadratic time complexity using non-binary bases, when using int("text"), a system could take 50ms to parse an int string with 100,000 digits and 5s for 1,000,000 digits (float, decimal, int.from_bytes(), and int() for binary bases 2, 4, 8, 16, and 32 are not affected). The highest threat from this vulnerability is to system availability. |
| CVE-2022-38752 | Medium | 2022-09-05 | Protected by Waratek | Proof of concept only | Using snakeYAML to parse untrusted YAML files may be vulnerable to Denial of Service attacks (DOS). If the parser is running on user supplied input, an attacker may supply content that causes the parser to crash by stack-overflow. |
| CVE-2022-36055 | Medium | 2022-09-01 | Not applicable | No public exploit | Helm is a tool for managing Charts. Charts are packages of pre-configured Kubernetes resources. Fuzz testing, provided by the CNCF, identified input to functions in the _strvals_ package that can cause an out of memory panic. The _strvals_ package contains a parser that turns strings in to Go structures. The _strvals_ package converts these strings into structures Go can work with. Some string inputs can cause array data structures to be created causing an out of memory panic. Applications that use the _strvals_ package in the Helm SDK to parse user supplied input can suffer a Denial of Service when that input causes a panic that cannot be recovered from. The Helm Client will panic with input to `--set`, `--set-string`, and other value setting flags that causes an out of memory panic. Helm is not a long running service so the panic will not affect future uses of the Helm client. This issue has been resolved in 3.9.4. SDK users can validate strings supplied by users won't create large arrays causing significant memory usage before passing them to the _strvals_ functions. |
| CVE-2022-3028 | High | 2022-08-31 | Not applicable | No public exploit | A race condition was found in the Linux kernel's IP framework for transforming packets (XFRM subsystem) when multiple calls to xfrm_probe_algs occurred simultaneously. This flaw could allow a local attacker to potentially trigger an out-of-bounds write or leak kernel heap memory by performing an out-of-bounds read and copying it into a socket. |
| CVE-2022-1319 | High | 2022-08-31 | No exploit published | No public exploit | A flaw was found in Undertow. For an AJP 400 response, EAP 7 is improperly sending two response packets, and those packets have the reuse flag set even though JBoss EAP closes the connection. A failure occurs when the connection is reused after a 400 by CPING since it reads in the second SEND_HEADERS response packet instead of a CPONG. |
| CVE-2022-25857 | High | 2022-08-30 | Protected by Waratek | No public exploit | The package org.yaml:snakeyaml from 0 and before 1.31 are vulnerable to Denial of Service (DoS) due missing to nested depth limitation for collections. |
| CVE-2022-36033 | Medium | 2022-08-29 | Protected by Waratek | Proof of concept only | jsoup is a Java HTML parser, built for HTML editing, cleaning, scraping, and cross-site scripting (XSS) safety. jsoup may incorrectly sanitize HTML including `javascript:` URL expressions, which could allow XSS attacks when a reader subsequently clicks that link. If the non-default `SafeList.preserveRelativeLinks` option is enabled, HTML including `javascript:` URLs that have been crafted with control characters will not be sanitized. If the site that this HTML is published on does not set a Content Security Policy, an XSS attack is then possible. This issue is patched in jsoup 1.15.3. Users should upgrade to this version. Additionally, as the unsanitized input may have been persisted, old content should be cleaned again using the updated version. To remediate this issue without immediately upgrading: - disable `SafeList.preserveRelativeLinks`, which will rewrite input URLs as absolute URLs - ensure an appropriate [Content Security Policy](https://developer.mozilla.org/en-US/docs/Web/HTTP/CSP) is defined. (This should be used regardless of upgrading, as a defence-in-depth best practice.) |
| CVE-2022-0934 | High | 2022-08-29 | Not applicable | No public exploit | A single-byte, non-arbitrary write/use-after-free flaw was found in dnsmasq. This flaw allows an attacker who sends a crafted packet processed by dnsmasq, potentially causing a denial of service. |
| CVE-2022-0084 | High | 2022-08-26 | No exploit published | No public exploit | A flaw was found in XNIO, specifically in the notifyReadClosed method. The issue revealed this method was logging a message to another expected end. This flaw allows an attacker to send flawed requests to a server, possibly causing log contention-related performance concerns or an unwanted disk fill-up. |
| CVE-2022-37434 | Critical | 2022-08-05 | Outside Waratek scope | Proof of concept only | zlib through 1.2.12 has a heap-based buffer over-read or buffer overflow in inflate in inflate.c via a large gzip header extra field. NOTE: only applications that call inflateGetHeader are affected. Some common applications bundle the affected zlib source code but may be unable to call inflateGetHeader (e.g., see the nodejs/node reference). |
| CVE-2022-2053 | High | 2022-08-05 | No exploit published | No public exploit | When a POST request comes through AJP and the request exceeds the max-post-size limit (maxEntitySize), Undertow's AjpServerRequestConduit implementation closes a connection without sending any response to the client/proxy. This behavior results in that a front-end proxy marking the backend worker (application server) as an error state and not forward requests to the worker for a while. In mod_cluster, this continues until the next STATUS request (10 seconds intervals) from the application server updates the server state. So, in the worst case, it can result in "All workers are in error state" and mod_cluster responds "503 Service Unavailable" for a while (up to 10 seconds). In mod_proxy_balancer, it does not forward requests to the worker until the "retry" timeout passes. However, luckily, mod_proxy_balancer has "forcerecovery" setting (On by default; this parameter can force the immediate recovery of all workers without considering the retry parameter of the workers if all workers of a balancer are in error state.). So, unlike mod_cluster, mod_proxy_balancer does not result in responding "503 Service Unavailable". An attacker could use this behavior to send a malicious request and trigger server errors, resulting in DoS (denial of service). This flaw was fixed in Undertow 2.2.19.Final, Undertow 2.3.0.Alpha2. |
| CVE-2022-35737 | High | 2022-08-03 | Not applicable | Proof of concept only | SQLite 1.0.12 through 3.39.x before 3.39.2 sometimes allows an array-bounds overflow if billions of bytes are used in a string argument to a C API. |
| CVE-2022-2509 | High | 2022-08-01 | Not applicable | No public exploit | A vulnerability found in gnutls. This security flaw happens because of a double free error occurs during verification of pkcs7 signatures in gnutls_pkcs7_verify function. |
| CVE-2022-34169 | High | 2022-07-19 | Protected by Waratek | Proof of concept only | The Apache Xalan Java XSLT library is vulnerable to an integer truncation issue when processing malicious XSLT stylesheets. This can be used to corrupt Java class files generated by the internal XSLTC compiler and execute arbitrary Java bytecode. Users are recommended to update to version 2.7.3 or later. Note: Java runtimes (such as OpenJDK) include repackaged copies of Xalan. |
| CVE-2022-32212 | High | 2022-07-14 | Not applicable | No public exploit | A OS Command Injection vulnerability exists in Node.js versions <14.20.0, <16.20.0, <18.5.0 due to an insufficient IsAllowedHost check that can easily be bypassed because IsIPAddress does not properly check if an IP address is invalid before making DBS requests allowing rebinding attacks. |
| CVE-2022-2048 | High | 2022-07-07 | No exploit published | No public exploit | In Eclipse Jetty HTTP/2 server implementation, when encountering an invalid HTTP/2 request, the error handling has a bug that can wind up not properly cleaning up the active connections and associated resources. This can lead to a Denial of Service scenario where there are no enough resources left to process good requests. |
| CVE-2022-33980 | Critical | 2022-07-06 | Mitigation candidate | Proof of concept only | Apache Commons Configuration performs variable interpolation, allowing properties to be dynamically evaluated and expanded. The standard format for interpolation is "${prefix:name}", where "prefix" is used to locate an instance of org.apache.commons.configuration2.interpol.Lookup that performs the interpolation. Starting with version 2.4 and continuing through 2.7, the set of default Lookup instances included interpolators that could result in arbitrary code execution or contact with remote servers. These lookups are: - "script" - execute expressions using the JVM script execution engine (javax.script) - "dns" - resolve dns records - "url" - load values from urls, including from remote servers Applications using the interpolation defaults in the affected versions may be vulnerable to remote code execution or unintentional contact with remote servers if untrusted configuration values are used. Users are recommended to upgrade to Apache Commons Configuration 2.8.0, which disables the problematic interpolators by default. |
| CVE-2022-31129 | High | 2022-07-06 | Not applicable | Proof of concept only | moment is a JavaScript date library for parsing, validating, manipulating, and formatting dates. Affected versions of moment were found to use an inefficient parsing algorithm. Specifically using string-to-date parsing in moment (more specifically rfc2822 parsing, which is tried by default) has quadratic (N^2) complexity on specific inputs. Users may notice a noticeable slowdown is observed with inputs above 10k characters. Users who pass user-provided strings without sanity length checks to moment constructor are vulnerable to (Re)DoS attacks. The problem is patched in 2.29.4, the patch can be applied to all affected versions with minimal tweaking. Users are advised to upgrade. Users unable to upgrade should consider limiting date lengths accepted from user input. |
| CVE-2022-2274 | Critical | 2022-07-01 | Outside Waratek scope | Proof of concept only | The OpenSSL 3.0.4 release introduced a serious bug in the RSA implementation for X86_64 CPUs supporting the AVX512IFMA instructions. This issue makes the RSA implementation with 2048 bit private keys incorrect on such machines and memory corruption will happen during the computation. As a consequence of the memory corruption an attacker may be able to trigger a remote code execution on the machine performing the computation. SSL/TLS servers or other servers using 2048 bit RSA private keys running on machines supporting AVX512IFMA instructions of the X86_64 architecture are affected by this issue. |
| CVE-2022-34305 | Medium | 2022-06-23 | Protected by Waratek | Exploited | In Apache Tomcat 10.1.0-M1 to 10.1.0-M16, 10.0.0-M1 to 10.0.22, 9.0.30 to 9.0.64 and 8.5.50 to 8.5.81 the Form authentication example in the examples web application displayed user provided data without filtering, exposing a XSS vulnerability. |
| CVE-2021-41411 | Critical | 2022-06-16 | Protected by Waratek | No public exploit | drools <=7.59.x is affected by an XML External Entity (XXE) vulnerability in KieModuleMarshaller.java. The Validator class is not used correctly, resulting in the XXE injection vulnerability. |
| CVE-2022-31813 | Critical | 2022-06-09 | Not applicable | No public exploit | Apache HTTP Server 2.4.53 and earlier may not send the X-Forwarded-* headers to the origin server based on client side Connection header hop-by-hop mechanism. This may be used to bypass IP based authentication on the origin server/application. |
| CVE-2022-27782 | High | 2022-06-02 | Not applicable | Proof of concept only | libcurl would reuse a previously created connection even when a TLS or SSHrelated option had been changed that should have prohibited reuse.libcurl keeps previously used connections in a connection pool for subsequenttransfers to reuse if one of them matches the setup. However, several TLS andSSH settings were left out from the configuration match checks, making themmatch too easily. |
| CVE-2022-22978 | Critical | 2022-05-19 | Mitigation candidate | Proof of concept only | In spring security versions prior to 5.4.11+, 5.5.7+ , 5.6.4+ and older unsupported versions, RegexRequestMatcher can easily be misconfigured to be bypassed on some servlet containers. Applications using RegexRequestMatcher with `.` in the regular expression are possibly vulnerable to an authorization bypass. |
| CVE-2022-30126 | Medium | 2022-05-16 | No exploit published | No public exploit | In Apache Tika, a regular expression in our StandardsText class, used by the StandardsExtractingContentHandler could lead to a denial of service caused by backtracking on a specially crafted file. This only affects users who are running the StandardsExtractingContentHandler, which is a non-standard handler. This is fixed in 1.28.2 and 2.4.0 |
| CVE-2022-22971 | Medium | 2022-05-12 | Protected by Waratek | No public exploit | In spring framework versions prior to 5.3.20+ , 5.2.22+ and old unsupported versions, application with a STOMP over WebSocket endpoint is vulnerable to a denial of service attack by an authenticated user. |
| CVE-2022-22970 | Medium | 2022-05-12 | No exploit published | No public exploit | In spring framework versions prior to 5.3.20+ , 5.2.22+ and old unsupported versions, applications that handle file uploads are vulnerable to DoS attack if they rely on data binding to set a MultipartFile or javax.servlet.Part to a field in a model object. |
| CVE-2022-30293 | High | 2022-05-06 | Not applicable | No public exploit | In WebKitGTK through 2.36.0 (and WPE WebKit), there is a heap-based buffer overflow in WebCore::TextureMapperLayer::setContentsLayer in WebCore/platform/graphics/texmap/TextureMapperLayer.cpp. |
| CVE-2022-24903 | High | 2022-05-06 | Outside Waratek scope | No public exploit | Rsyslog is a rocket-fast system for log processing. Modules for TCP syslog reception have a potential heap buffer overflow when octet-counted framing is used. This can result in a segfault or some other malfunction. As of our understanding, this vulnerability can not be used for remote code execution. But there may still be a slight chance for experts to do that. The bug occurs when the octet count is read. While there is a check for the maximum number of octets, digits are written to a heap buffer even when the octet count is over the maximum, This can be used to overrun the memory buffer. However, once the sequence of digits stop, no additional characters can be added to the buffer. In our opinion, this makes remote exploits impossible or at least highly complex. Octet-counted framing is one of two potential framing modes. It is relatively uncommon, but enabled by default on receivers. Modules `imtcp`, `imptcp`, `imgssapi`, and `imhttp` are used for regular syslog message reception. It is best practice not to directly expose them to the public. When this practice is followed, the risk is considerably lower. Module `imdiag` is a diagnostics module primarily intended for testbench runs. We do not expect it to be present on any production installation. Octet-counted framing is not very common. Usually, it needs to be specifically enabled at senders. If users do not need it, they can turn it off for the most important modules. This will mitigate the vulnerability. |
| CVE-2022-24823 | Medium | 2022-05-06 | No exploit published | Proof of concept only | Netty is an open-source, asynchronous event-driven network application framework. The package `io.netty:netty-codec-http` prior to version 4.1.77.Final contains an insufficient fix for CVE-2021-21290. When Netty's multipart decoders are used local information disclosure can occur via the local system temporary directory if temporary storing uploads on the disk is enabled. This only impacts applications running on Java version 6 and lower. Additionally, this vulnerability impacts code running on Unix-like systems, and very old versions of Mac OSX and Windows as they all share the system temporary directory between all users. Version 4.1.77.Final contains a patch for this vulnerability. As a workaround, specify one's own `java.io.tmpdir` when starting the JVM or use DefaultHttpDataFactory.setBaseDir(...) to set the directory to something that is only readable by the current user. |
| CVE-2022-29824 | Medium | 2022-05-03 | Not applicable | No public exploit | In libxml2 before 2.9.14, several buffer handling functions in buf.c (xmlBuf*) and tree.c (xmlBuffer*) don't check for integer overflows. This can result in out-of-bounds memory writes. Exploitation requires a victim to open a crafted, multi-gigabyte XML file. Other software using libxml2's buffer functions, for example libxslt through 1.1.35, is affected as well. |
| CVE-2022-25647 | High | 2022-05-01 | Protected by Waratek | No public exploit | The package com.google.code.gson:gson before 2.8.9 are vulnerable to Deserialization of Untrusted Data via the writeReplace() method in internal classes, which may lead to DoS attacks. |
| CVE-2022-23457 | Critical | 2022-04-25 | Protected by Waratek | Proof of concept only | ESAPI (The OWASP Enterprise Security API) is a free, open source, web application security control library. Prior to version 2.3.0.0, the default implementation of `Validator.getValidDirectoryPath(String, String, File, boolean)` may incorrectly treat the tested input string as a child of the specified parent directory. This potentially could allow control-flow bypass checks to be defeated if an attack can specify the entire string representing the 'input' path. This vulnerability is patched in release 2.3.0.0 of ESAPI. As a workaround, it is possible to write one's own implementation of the Validator interface. However, maintainers do not recommend this. |
| CVE-2022-27404 | Critical | 2022-04-22 | Not applicable | No public exploit | FreeType commit 1e2eb65048f75c64b68708efed6ce904c31f3b2f was discovered to contain a heap buffer overflow via the function sfnt_init_face. |
| CVE-2022-1304 | High | 2022-04-14 | Not applicable | No public exploit | An out-of-bounds read/write vulnerability was found in e2fsprogs 1.46.5. This issue leads to a segmentation fault and possibly arbitrary code execution via a specially crafted filesystem. |
| CVE-2021-31805 | Critical | 2022-04-12 | Protected by Waratek | Exploited | The fix issued for CVE-2020-17530 was incomplete. So from Apache Struts 2.0.0 to 2.5.29, still some of the tag’s attributes could perform a double evaluation if a developer applied forced OGNL evaluation by using the %{...} syntax. Using forced OGNL evaluation on untrusted user input can lead to a Remote Code Execution and security degradation. |
| CVE-2022-24839 | High | 2022-04-11 | No exploit published | No public exploit | org.cyberneko.html is an html parser written in Java. The fork of `org.cyberneko.html` used by Nokogiri (Rubygem) raises a `java.lang.OutOfMemoryError` exception when parsing ill-formed HTML markup. Users are advised to upgrade to `>= 1.9.22.noko2`. Note: The upstream library `org.cyberneko.html` is no longer maintained. Nokogiri uses its own fork of this library located at https://github.com/sparklemotion/nekohtml and this CVE applies only to that fork. Other forks of nekohtml may have a similar vulnerability. |
| CVE-2022-22965 | Critical | 2022-04-01 | Protected by Waratek | Exploited | A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to remote code execution (RCE) via data binding. The specific exploit requires the application to run on Tomcat as a WAR deployment. If the application is deployed as a Spring Boot executable jar, i.e. the default, it is not vulnerable to the exploit. However, the nature of the vulnerability is more general, and there may be other ways to exploit it. |
| CVE-2022-1122 | Medium | 2022-03-29 | Not applicable | No public exploit | A flaw was found in the opj2_decompress program in openjpeg2 2.4.0 in the way it handles an input directory with a large number of files. When it fails to allocate a buffer to store the filenames of the input directory, it calls free() on an uninitialized pointer, leading to a segmentation fault and a denial of service. |
| CVE-2018-25032 | High | 2022-03-25 | Outside Waratek scope | Proof of concept only | zlib before 1.2.12 allows memory corruption when deflating (i.e., when compressing) if the input has many distant matches. |
| CVE-2020-36518 | High | 2022-03-11 | No exploit published | No public exploit | jackson-databind before 2.13.0 allows a Java StackOverflow exception and denial of service via a large depth of nested objects. |
| CVE-2022-26336 | Medium | 2022-03-04 | Protected by Waratek | No public exploit | A shortcoming in the HMEF package of poi-scratchpad (Apache POI) allows an attacker to cause an Out of Memory exception. This package is used to read TNEF files (Microsoft Outlook and Microsoft Exchange Server). If an application uses poi-scratchpad to parse TNEF files and the application allows untrusted users to supply them, then a carefully crafted file can cause an Out of Memory exception. This issue affects poi-scratchpad version 5.2.0 and prior versions. Users are recommended to upgrade to poi-scratchpad 5.2.1. |
| CVE-2021-3737 | High | 2022-03-04 | Not applicable | No public exploit | A flaw was found in python. An improperly handled HTTP response in the HTTP client code of python may allow a remote attacker, who controls the HTTP server, to make the client script enter an infinite loop, consuming CPU time. The highest threat from this vulnerability is to system availability. |
| CVE-2022-0492 | High | 2022-03-03 | Not applicable | Exploited | A vulnerability was found in the Linux kernel’s cgroup_release_agent_write in the kernel/cgroup/cgroup-v1.c function. This flaw, under certain circumstances, allows the use of the cgroups v1 release_agent feature to escalate privileges and bypass the namespace isolation unexpectedly. |
| CVE-2022-24329 | Medium | 2022-02-25 | No exploit published | No public exploit | In JetBrains Kotlin before 1.6.0, it was not possible to lock dependencies for Multiplatform Gradle Projects. |
| CVE-2022-24407 | High | 2022-02-24 | Outside Waratek scope | No public exploit | In Cyrus SASL 2.1.17 through 2.1.27 before 2.1.28, plugins/sql.c does not escape the password for a SQL INSERT or UPDATE statement. |
| CVE-2022-21824 | High | 2022-02-24 | Not applicable | No public exploit | Due to the formatting logic of the "console.table()" function it was not safe to allow user controlled input to be passed to the "properties" parameter while simultaneously passing a plain object with at least one property as the first parameter, which could be "__proto__". The prototype pollution has very limited control, in that it only allows an empty string to be assigned to numerical keys of the object prototype.Node.js >= 12.22.9, >= 14.18.3, >= 16.13.2, and >= 17.3.1 use a null protoype for the object these properties are being assigned to. |
| CVE-2022-25315 | Critical | 2022-02-18 | Not applicable | Proof of concept only | In Expat (aka libexpat) before 2.4.5, there is an integer overflow in storeRawNames. |
| CVE-2022-25236 | Critical | 2022-02-16 | Not applicable | No public exploit | xmlparse.c in Expat (aka libexpat) before 2.4.5 allows attackers to insert namespace-separator characters into namespace URIs. |
| CVE-2022-23437 | Medium | 2022-01-24 | No exploit published | No public exploit | There's a vulnerability within the Apache Xerces Java (XercesJ) XML parser when handling specially crafted XML document payloads. This causes, the XercesJ XML parser to wait in an infinite loop, which may sometimes consume system resources for prolonged duration. This vulnerability is present within XercesJ version 2.12.1 and the previous versions. |
| CVE-2022-23221 | Critical | 2022-01-19 | Protected by Waratek | Proof of concept only | H2 Console before 2.1.210 allows remote attackers to execute arbitrary code via a jdbc:h2:mem JDBC URL containing the IGNORE_UNKNOWN_SETTINGS=TRUE;FORBID_CREATION=FALSE;INIT=RUNSCRIPT substring, a different vulnerability than CVE-2021-42392. |
| CVE-2022-23305 | Critical | 2022-01-18 | Protected by Waratek | Proof of concept only | By design, the JDBCAppender in Log4j 1.2.x accepts an SQL statement as a configuration parameter where the values to be inserted are converters from PatternLayout. The message converter, %m, is likely to always be included. This allows attackers to manipulate the SQL by entering crafted strings into input fields or headers of an application that are logged allowing unintended SQL queries to be executed. Note this issue only affects Log4j 1.x when specifically configured to use the JDBCAppender, which is not the default. Beginning in version 2.0-beta8, the JDBCAppender was re-introduced with proper support for parameterized SQL queries and further customization over the columns written to in logs. Apache Log4j 1.2 reached end of life in August 2015. Users should upgrade to Log4j 2 as it addresses numerous other issues from the previous versions. |
| CVE-2022-23219 | Critical | 2022-01-14 | Outside Waratek scope | Proof of concept only | The deprecated compatibility function clnt_create in the sunrpc module of the GNU C Library (aka glibc) through 2.34 copies its hostname argument on the stack without validating its length, which may result in a buffer overflow, potentially resulting in a denial of service or (if an application is not built with a stack protector enabled) arbitrary code execution. |
| CVE-2021-44832 | Medium | 2021-12-28 | Protected by Waratek | Exploited | Apache Log4j2 versions 2.0-beta7 through 2.17.0 (excluding security fix releases 2.3.2 and 2.12.4) are vulnerable to a remote code execution (RCE) attack when a configuration uses a JDBC Appender with a JNDI LDAP data source URI when an attacker has control of the target LDAP server. This issue is fixed by limiting JNDI data source names to the java protocol in Log4j2 versions 2.17.1, 2.12.4, and 2.3.2. |
| CVE-2021-45105 | Medium | 2021-12-18 | Protected by Waratek | Exploited | Apache Log4j2 versions 2.0-alpha1 through 2.16.0 (excluding 2.12.3 and 2.3.1) did not protect from uncontrolled recursion from self-referential lookups. This allows an attacker with control over Thread Context Map data to cause a denial of service when a crafted string is interpreted. This issue was fixed in Log4j 2.17.0, 2.12.3, and 2.3.1. |
| CVE-2020-16156 | High | 2021-12-13 | Not applicable | No public exploit | CPAN 2.28 allows Signature Verification Bypass. |
| CVE-2021-43797 | Medium | 2021-12-09 | Outside Waratek scope | No public exploit | Netty is an asynchronous event-driven network application framework for rapid development of maintainable high performance protocol servers & clients. Netty prior to version 4.1.71.Final skips control chars when they are present at the beginning / end of the header name. It should instead fail fast as these are not allowed by the spec and could lead to HTTP request smuggling. Failing to do the validation might cause netty to "sanitize" header names before it forward these to another remote system when used as proxy. This remote system can't see the invalid usage anymore, and therefore does not do the validation itself. Users should upgrade to version 4.1.71.Final. |
| CVE-2021-42717 | High | 2021-12-07 | Not applicable | No public exploit | ModSecurity 3.x through 3.0.5 mishandles excessively nested JSON objects. Crafted JSON objects with nesting tens-of-thousands deep could result in the web server being unable to service legitimate requests. Even a moderately large (e.g., 300KB) HTTP request can occupy one of the limited NGINX worker processes for minutes and consume almost all of the available CPU on the machine. Modsecurity 2 is similarly vulnerable: the affected versions include 2.8.0 through 2.9.4. |
| CVE-2021-3918 | Critical | 2021-11-13 | Not applicable | No public exploit | json-schema is vulnerable to Improperly Controlled Modification of Object Prototype Attributes ('Prototype Pollution') |
| CVE-2021-41184 | Medium | 2021-10-26 | Outside Waratek scope | Proof of concept only | jQuery-UI is the official jQuery user interface library. Prior to version 1.13.0, accepting the value of the `of` option of the `.position()` util from untrusted sources may execute untrusted code. The issue is fixed in jQuery UI 1.13.0. Any string value passed to the `of` option is now treated as a CSS selector. A workaround is to not accept the value of the `of` option from untrusted sources. |
| CVE-2021-40528 | Medium | 2021-09-06 | Not applicable | No public exploit | The ElGamal implementation in Libgcrypt before 1.9.4 allows plaintext recovery because, during interaction between two cryptographic libraries, a certain dangerous combination of the prime defined by the receiver's public key, the generator defined by the receiver's public key, and the sender's ephemeral exponents can lead to a cross-configuration attack against OpenPGP. |
| CVE-2021-36770 | High | 2021-08-11 | Not applicable | No public exploit | Encode.pm, as distributed in Perl through 5.34.0, allows local users to gain privileges via a Trojan horse Encode::ConfigLocal library (in the current working directory) that preempts dynamic module loading. Exploitation requires an unusual configuration, and certain 2021 versions of Encode.pm (3.05 through 3.11). This issue occurs because the || operator evaluates @INC in a scalar context, and thus @INC has only an integer value. |
| CVE-2021-36483 | High | 2021-08-04 | Not applicable | No public exploit | DevExpress.XtraReports.UI through v21.1 allows attackers to execute arbitrary code via insecure deserialization. |
| CVE-2021-2351 | High | 2021-07-21 | No exploit published | No public exploit | Vulnerability in the Advanced Networking Option component of Oracle Database Server. Supported versions that are affected are 12.1.0.2, 12.2.0.1 and 19c. Difficult to exploit vulnerability allows unauthenticated attacker with network access via Oracle Net to compromise Advanced Networking Option. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Advanced Networking Option, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Advanced Networking Option. Note: The July 2021 Critical Patch Update introduces a number of Native Network Encryption changes to deal with vulnerability CVE-2021-2351 and prevent the use of weaker ciphers. Customers should review: "Changes in Native Network Encryption with the July 2021 Critical Patch Update" (Doc ID 2791571.1). CVSS 3.1 Base Score 8.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:C/C:H/I:H/A:H). |
| CVE-2021-36090 | High | 2021-07-13 | No exploit published | No public exploit | When reading a specially crafted ZIP archive, Compress can be made to allocate large amounts of memory that finally leads to an out of memory error even for very small inputs. This could be used to mount a denial of service attack against services that use Compress' zip package. |
| CVE-2021-31812 | Medium | 2021-06-12 | No exploit published | No public exploit | In Apache PDFBox, a carefully crafted PDF file can trigger an infinite loop while loading the file. This issue affects Apache PDFBox version 2.0.23 and prior 2.0.x versions. |
| CVE-2021-29425 | Medium | 2021-04-13 | Protected by Waratek | No public exploit | In Apache Commons IO before 2.7, When invoking the method FileNameUtils.normalize with an improper input string, like "//../foo", or "\\..\foo", the result would be the same value, thus possibly providing access to files in the parent directory, but not further above (thus "limited" path traversal), if the calling code would use the result to construct a path value. |
| CVE-2021-23358 | High | 2021-03-29 | Not applicable | Proof of concept only | The package underscore from 1.13.0-0 and before 1.13.0-2, from 1.3.2 and before 1.12.1 are vulnerable to Arbitrary Code Injection via the template function, particularly when a variable property is passed as an argument as it is not sanitized. |
| CVE-2020-11987 | High | 2021-02-24 | No exploit published | No public exploit | Apache Batik 1.13 is vulnerable to server-side request forgery, caused by improper input validation by the NodePickerPanel. By using a specially-crafted argument, an attacker could exploit this vulnerability to cause the underlying server to make arbitrary GET requests. |
| CVE-2020-36242 | Critical | 2021-02-07 | Outside Waratek scope | No public exploit | In the cryptography package before 3.3.2 for Python, certain sequences of update calls to symmetrically encrypt multi-GB values could result in an integer overflow and buffer overflow, as demonstrated by the Fernet class. |
| CVE-2020-27844 | High | 2021-01-05 | Not applicable | No public exploit | A flaw was found in openjpeg's src/lib/openjp2/t2.c in versions prior to 2.4.0. This flaw allows an attacker to provide crafted input to openjpeg during conversion and encoding, causing an out-of-bounds write. The highest threat from this vulnerability is to confidentiality, integrity, as well as system availability. |
| CVE-2020-13956 | Medium | 2020-12-02 | Outside Waratek scope | No public exploit | Apache HttpClient versions prior to version 4.5.13 and 5.0.3 can misinterpret malformed authority component in request URIs passed to the library as java.net.URI object and pick the wrong target host for request execution. |
| CVE-2020-11979 | High | 2020-10-01 | No exploit published | No public exploit | As mitigation for CVE-2020-1945 Apache Ant 1.10.8 changed the permissions of temporary files it created so that only the current user was allowed to access them. Unfortunately the fixcrlf task deleted the temporary file and created a new one without said protection, effectively nullifying the effort. This would still allow an attacker to inject modified source files into the build process. |
| CVE-2020-10693 | Medium | 2020-05-06 | No exploit published | No public exploit | A flaw was found in Hibernate Validator version 6.1.2.Final. A bug in the message interpolation processor enables invalid EL expressions to be evaluated as if they were valid. This flaw allows attackers to bypass input sanitation (escaping, stripping) controls that developers may have put in place when handling user-controlled data in error messages. |
| CVE-2020-10683 | Critical | 2020-05-01 | Protected by Waratek | No public exploit | dom4j before 2.0.3 and 2.1.x before 2.1.3 allows external DTDs and External Entities by default, which might enable XXE attacks. However, there is popular external documentation from OWASP showing how to enable the safe, non-default behavior in any application that uses dom4j. |
| CVE-2019-17571 | Critical | 2019-12-20 | Protected by Waratek | Proof of concept only | Included in Log4j 1.2 is a SocketServer class that is vulnerable to deserialization of untrusted data which can be exploited to remotely execute arbitrary code when combined with a deserialization gadget when listening to untrusted network traffic for log data. This affects Log4j versions up to 1.2 up to 1.2.17. |
| CVE-2019-12415 | Medium | 2019-10-23 | Protected by Waratek | No public exploit | In Apache POI up to 4.1.0, when using the tool XSSFExportToXml to convert user-provided Microsoft Excel documents, a specially crafted document can allow an attacker to read files from the local filesystem or from internal network resources via XML External Entity (XXE) Processing. |
| CVE-2019-7317 | Medium | 2019-02-04 | Not applicable | No public exploit | png_image_free in png.c in libpng 1.6.x before 1.6.37 has a use-after-free because png_image_free_function is called under png_safe_execute. |
| CVE-2018-1273 | Critical | 2018-04-11 | Protected by Waratek | Exploited | Spring Data Commons, versions prior to 1.13 to 1.13.10, 2.0 to 2.0.5, and older unsupported versions, contain a property binder vulnerability caused by improper neutralization of special elements. An unauthenticated remote malicious user (or attacker) can supply specially crafted request parameters against Spring Data REST backed HTTP resources or using Spring Data's projection-based request payload binding hat can lead to a remote code execution attack. |
| CVE-2018-7489 | Critical | 2018-02-26 | Protected by Waratek | No public exploit | FasterXML jackson-databind before 2.7.9.3, 2.8.x before 2.8.11.1 and 2.9.x before 2.9.5 allows unauthenticated remote code execution because of an incomplete fix for the CVE-2017-7525 deserialization flaw. This is exploitable by sending maliciously crafted JSON input to the readValue method of the ObjectMapper, bypassing a blacklist that is ineffective if the c3p0 libraries are available in the classpath. |