
Oracle Critical Patch Update January 2022
Released January 2022 · Oracle's advisory ↗ · ← Critical Patch Update, October 2021 · Critical Patch Update, April 2022 →
266 CVEs in this release, one square each
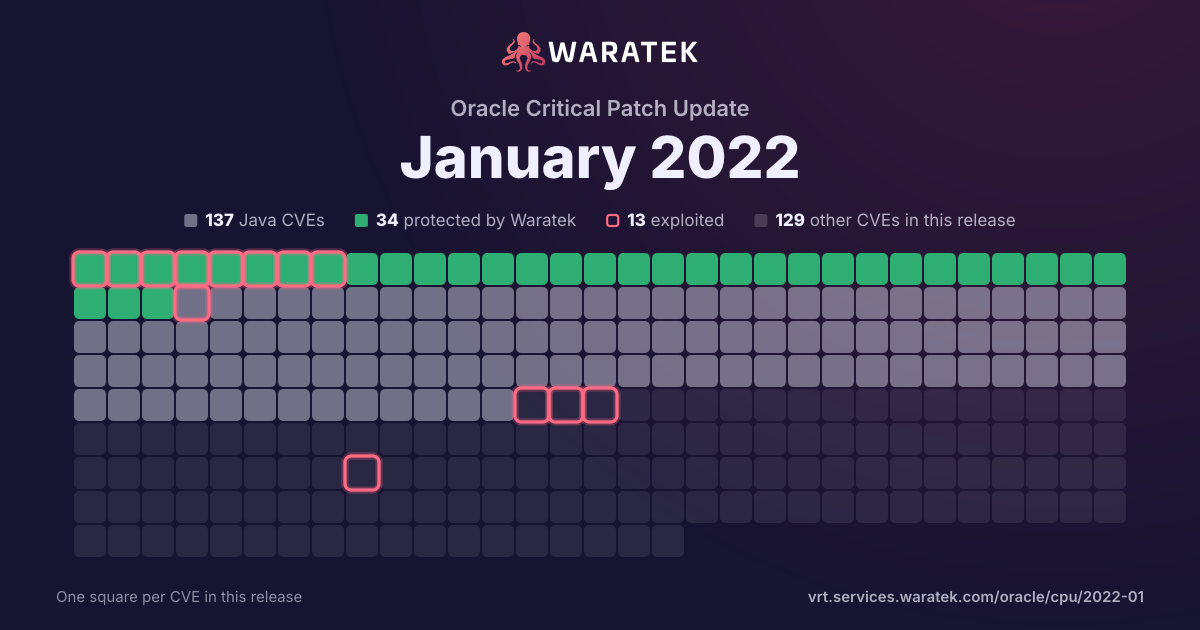
By status
34Protected by Waratek3Mitigation candidate100No exploit published57Outside Waratek scope72Not applicable
13Exploited, marked by the ring
No exploit published. For 71 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 266 matches · 137 in Waratek scope · 34 protected · 13 exploited · 4 CISA KEV · 18 public PoC · 24 EPSS ≥ 0.5
266matches
137in Waratek scope51.5%
34protected12.8%
13exploited4.9%
4CISA KEV1.5%
18public PoC6.8%
24EPSS ≥ 0.59.0%
Protected by Waratek
34
12.8%
Rule in development
0
0.0%
Mitigation candidate
3
1.1%
No exploit published
100
37.6%
Outside Waratek scope
57
21.4%
Not applicable
72
27.1%
Withdrawn CVE
0
0.0%
blocked by ARMR today
34
12.8%
partly blocked
0
0.0%
not blocked
232
87.2%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 163 / quarter
Q1 171
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Q2 170
Q3 170
Q4 170
Q1 181
No exploit published1
Medium1
not blocked1
No public exploit1
Q2 180
Q3 180
Q4 180
Q1 190
Q2 190
Q3 191
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Q4 194
Protected by Waratek1
No exploit published1
Outside Waratek scope1
Not applicable1
Critical1
High2
Medium1
blocked by ARMR today1
not blocked3
No public exploit4
Q1 202
Outside Waratek scope2
High1
Medium1
not blocked2
No public exploit2
Q2 206
Protected by Waratek1
Outside Waratek scope5
Critical1
High2
Medium3
blocked by ARMR today1
not blocked5
Exploited2
No public exploit4
Q3 205
Protected by Waratek2
Mitigation candidate1
No exploit published2
High4
Medium1
blocked by ARMR today2
not blocked3
Working exploit published1
No public exploit4
Q4 2010
Protected by Waratek4
No exploit published4
Outside Waratek scope1
Not applicable1
Critical1
High6
Medium2
Low1
blocked by ARMR today4
not blocked6
Exploited1
Proof of concept only1
No public exploit8
Q1 2116
Protected by Waratek3
No exploit published7
Outside Waratek scope5
Not applicable1
Critical3
High8
Medium5
blocked by ARMR today3
not blocked13
Exploited2
Proof of concept only1
Forecast only1
No public exploit12
Q2 2121
Protected by Waratek4
Mitigation candidate1
No exploit published5
Outside Waratek scope3
Not applicable8
Critical2
High11
Medium8
blocked by ARMR today4
not blocked17
Working exploit published4
Forecast only3
No public exploit14
Q3 2124
Protected by Waratek1
Mitigation candidate1
No exploit published11
Outside Waratek scope6
Not applicable5
Critical5
High12
Medium7
blocked by ARMR today1
not blocked23
Exploited3
Proof of concept only2
Forecast only2
No public exploit17
Q4 2111
Protected by Waratek5
Outside Waratek scope2
Not applicable4
Critical2
High5
Medium4
blocked by ARMR today5
not blocked6
Exploited3
Working exploit published1
No public exploit7
Q1 22163
Protected by Waratek12
No exploit published69
Outside Waratek scope31
Not applicable51
Critical8
High15
Medium117
Low23
blocked by ARMR today12
not blocked151
Exploited2
Proof of concept only1
Forecast only2
No public exploit158
Q2 220
Q3 220
Q4 221
Not applicable1
Medium1
not blocked1
Proof of concept only1
Q2 17Q4 17Q2 18Q4 18Q2 19Q4 19Q2 20Q4 20Q2 21Q4 21Q2 22Q4 22
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2021-32723 | High | 2021-06-28 | Not applicable | No public exploit | Prism is a syntax highlighting library. Some languages before 1.24.0 are vulnerable to Regular Expression Denial of Service (ReDoS). When Prism is used to highlight untrusted (user-given) text, an attacker can craft a string that will take a very very long time to highlight. This problem has been fixed in Prism v1.24. As a workaround, do not use ASCIIDoc or ERB to highlight untrusted text. Other languages are not affected and can be used to highlight untrusted text. |
| CVE-2021-31812 | Medium | 2021-06-12 | No exploit published | No public exploit | In Apache PDFBox, a carefully crafted PDF file can trigger an infinite loop while loading the file. This issue affects Apache PDFBox version 2.0.23 and prior 2.0.x versions. |
| CVE-2021-22901 | High | 2021-06-11 | Outside Waratek scope | Forecast only | curl 7.75.0 through 7.76.1 suffers from a use-after-free vulnerability resulting in already freed memory being used when a TLS 1.3 session ticket arrives over a connection. A malicious server can use this in rare unfortunate circumstances to potentially reach remote code execution in the client. When libcurl at run-time sets up support for TLS 1.3 session tickets on a connection using OpenSSL, it stores pointers to the transfer in-memory object for later retrieval when a session ticket arrives. If the connection is used by multiple transfers (like with a reused HTTP/1.1 connection or multiplexed HTTP/2 connection) that first transfer object might be freed before the new session is established on that connection and then the function will access a memory buffer that might be freed. When using that memory, libcurl might even call a function pointer in the object, making it possible for a remote code execution if the server could somehow manage to get crafted memory content into the correct place in memory. |
| CVE-2021-26691 | Critical | 2021-06-10 | Outside Waratek scope | Forecast only | In Apache HTTP Server versions 2.4.0 to 2.4.46 a specially crafted SessionHeader sent by an origin server could cause a heap overflow |
| CVE-2021-33560 | High | 2021-06-08 | No exploit published | No public exploit | Libgcrypt before 1.8.8 and 1.9.x before 1.9.3 mishandles ElGamal encryption because it lacks exponent blinding to address a side-channel attack against mpi_powm, and the window size is not chosen appropriately. This, for example, affects use of ElGamal in OpenPGP. |
| CVE-2021-33880 | Medium | 2021-06-06 | Not applicable | No public exploit | The aaugustin websockets library before 9.1 for Python has an Observable Timing Discrepancy on servers when HTTP Basic Authentication is enabled with basic_auth_protocol_factory(credentials=...). An attacker may be able to guess a password via a timing attack. |
| CVE-2020-28469 | High | 2021-06-03 | Not applicable | No public exploit | This affects the package glob-parent before 5.1.2. The enclosure regex used to check for strings ending in enclosure containing path separator. |
| CVE-2020-6950 | Medium | 2021-06-02 | Protected by Waratek | Working exploit published | Directory traversal in Eclipse Mojarra before 2.3.14 allows attackers to read arbitrary files via the loc parameter or con parameter. |
| CVE-2020-14340 | Medium | 2021-06-02 | No exploit published | No public exploit | A vulnerability was discovered in XNIO where file descriptor leak caused by growing amounts of NIO Selector file handles between garbage collection cycles. It may allow the attacker to cause a denial of service. It affects XNIO versions 3.6.0.Beta1 through 3.8.1.Final. |
| CVE-2021-23017 | High | 2021-06-01 | Not applicable | Working exploit published | A security issue in nginx resolver was identified, which might allow an attacker who is able to forge UDP packets from the DNS server to cause 1-byte memory overwrite, resulting in worker process crash or potential other impact. |
| CVE-2021-29505 | High | 2021-05-28 | Mitigation candidate | Working exploit published | XStream is software for serializing Java objects to XML and back again. A vulnerability in XStream versions prior to 1.4.17 may allow a remote attacker has sufficient rights to execute commands of the host only by manipulating the processed input stream. No user who followed the recommendation to setup XStream's security framework with a whitelist limited to the minimal required types is affected. The vulnerability is patched in version 1.4.17. |
| CVE-2021-22118 | High | 2021-05-27 | Protected by Waratek | No public exploit | In Spring Framework, versions 5.2.x prior to 5.2.15 and versions 5.3.x prior to 5.3.7, a WebFlux application is vulnerable to a privilege escalation: by (re)creating the temporary storage directory, a locally authenticated malicious user can read or modify files that have been uploaded to the WebFlux application, or overwrite arbitrary files with multipart request data. |
| CVE-2021-3426 | Medium | 2021-05-20 | Not applicable | No public exploit | There's a flaw in Python 3's pydoc. A local or adjacent attacker who discovers or is able to convince another local or adjacent user to start a pydoc server could access the server and use it to disclose sensitive information belonging to the other user that they would not normally be able to access. The highest risk of this flaw is to data confidentiality. This flaw affects Python versions before 3.8.9, Python versions before 3.9.3 and Python versions before 3.10.0a7. |
| CVE-2021-20718 | High | 2021-05-20 | Not applicable | No public exploit | mod_auth_openidc 2.4.0 to 2.4.7 allows a remote attacker to cause a denial-of-service (DoS) condition via unspecified vectors. |
| CVE-2021-3517 | High | 2021-05-19 | Not applicable | No public exploit | There is a flaw in the xml entity encoding functionality of libxml2 in versions before 2.9.11. An attacker who is able to supply a crafted file to be processed by an application linked with the affected functionality of libxml2 could trigger an out-of-bounds read. The most likely impact of this flaw is to application availability, with some potential impact to confidentiality and integrity if an attacker is able to use memory information to further exploit the application. |
| CVE-2021-29921 | Critical | 2021-05-06 | Outside Waratek scope | No public exploit | In Python before 3,9,5, the ipaddress library mishandles leading zero characters in the octets of an IP address string. This (in some situations) allows attackers to bypass access control that is based on IP addresses. |
| CVE-2021-29425 | Medium | 2021-04-13 | Protected by Waratek | No public exploit | In Apache Commons IO before 2.7, When invoking the method FileNameUtils.normalize with an improper input string, like "//../foo", or "\\..\foo", the result would be the same value, thus possibly providing access to files in the parent directory, but not further above (thus "limited" path traversal), if the calling code would use the result to construct a path value. |
| CVE-2021-3448 | Medium | 2021-04-08 | Not applicable | No public exploit | A flaw was found in dnsmasq in versions before 2.85. When configured to use a specific server for a given network interface, dnsmasq uses a fixed port while forwarding queries. An attacker on the network, able to find the outgoing port used by dnsmasq, only needs to guess the random transmission ID to forge a reply and get it accepted by dnsmasq. This flaw makes a DNS Cache Poisoning attack much easier. The highest threat from this vulnerability is to data integrity. |
| CVE-2021-28165 | High | 2021-04-01 | No exploit published | Forecast only | In Eclipse Jetty 7.2.2 to 9.4.38, 10.0.0.alpha0 to 10.0.1, and 11.0.0.alpha0 to 11.0.1, CPU usage can reach 100% upon receiving a large invalid TLS frame. |
| CVE-2021-28164 | Medium | 2021-04-01 | Protected by Waratek | Working exploit published | In Eclipse Jetty 9.4.37.v20210219 to 9.4.38.v20210224, the default compliance mode allows requests with URIs that contain %2e or %2e%2e segments to access protected resources within the WEB-INF directory. For example a request to /context/%2e/WEB-INF/web.xml can retrieve the web.xml file. This can reveal sensitive information regarding the implementation of a web application. |
| CVE-2021-21409 | Medium | 2021-03-30 | No exploit published | No public exploit | Netty is an open-source, asynchronous event-driven network application framework for rapid development of maintainable high performance protocol servers & clients. In Netty (io.netty:netty-codec-http2) before version 4.1.61.Final there is a vulnerability that enables request smuggling. The content-length header is not correctly validated if the request only uses a single Http2HeaderFrame with the endStream set to to true. This could lead to request smuggling if the request is proxied to a remote peer and translated to HTTP/1.1. This is a followup of GHSA-wm47-8v5p-wjpj/CVE-2021-21295 which did miss to fix this one case. This was fixed as part of 4.1.61.Final. |
| CVE-2021-21783 | Critical | 2021-03-25 | No exploit published | No public exploit | A code execution vulnerability exists in the WS-Addressing plugin functionality of Genivia gSOAP 2.8.107. A specially crafted SOAP request can lead to remote code execution. An attacker can send an HTTP request to trigger this vulnerability. |
| CVE-2020-13936 | High | 2021-03-10 | No exploit published | No public exploit | An attacker that is able to modify Velocity templates may execute arbitrary Java code or run arbitrary system commands with the same privileges as the account running the Servlet container. This applies to applications that allow untrusted users to upload/modify velocity templates running Apache Velocity Engine versions up to 2.2. |
| CVE-2021-25122 | High | 2021-03-01 | Protected by Waratek | No public exploit | When responding to new h2c connection requests, Apache Tomcat versions 10.0.0-M1 to 10.0.0, 9.0.0.M1 to 9.0.41 and 8.5.0 to 8.5.61 could duplicate request headers and a limited amount of request body from one request to another meaning user A and user B could both see the results of user A's request. |
| CVE-2020-27618 | Medium | 2021-02-26 | Outside Waratek scope | No public exploit | The iconv function in the GNU C Library (aka glibc or libc6) 2.32 and earlier, when processing invalid multi-byte input sequences in IBM1364, IBM1371, IBM1388, IBM1390, and IBM1399 encodings, fails to advance the input state, which could lead to an infinite loop in applications, resulting in a denial of service, a different vulnerability from CVE-2016-10228. |
| CVE-2020-11987 | High | 2021-02-24 | No exploit published | No public exploit | Apache Batik 1.13 is vulnerable to server-side request forgery, caused by improper input validation by the NodePickerPanel. By using a specially-crafted argument, an attacker could exploit this vulnerability to cause the underlying server to make arbitrary GET requests. |
| CVE-2021-27568 | Medium | 2021-02-23 | Protected by Waratek | No public exploit | An issue was discovered in netplex json-smart-v1 through 2015-10-23 and json-smart-v2 through 2.4. An exception is thrown from a function, but it is not caught, as demonstrated by NumberFormatException. When it is not caught, it may cause programs using the library to crash or expose sensitive information. |
| CVE-2021-23840 | High | 2021-02-16 | Outside Waratek scope | Forecast only | Calls to EVP_CipherUpdate, EVP_EncryptUpdate and EVP_DecryptUpdate may overflow the output length argument in some cases where the input length is close to the maximum permissable length for an integer on the platform. In such cases the return value from the function call will be 1 (indicating success), but the output length value will be negative. This could cause applications to behave incorrectly or crash. OpenSSL versions 1.1.1i and below are affected by this issue. Users of these versions should upgrade to OpenSSL 1.1.1j. OpenSSL versions 1.0.2x and below are affected by this issue. However OpenSSL 1.0.2 is out of support and no longer receiving public updates. Premium support customers of OpenSSL 1.0.2 should upgrade to 1.0.2y. Other users should upgrade to 1.1.1j. Fixed in OpenSSL 1.1.1j (Affected 1.1.1-1.1.1i). Fixed in OpenSSL 1.0.2y (Affected 1.0.2-1.0.2x). |
| CVE-2021-23337 | High | 2021-02-15 | Not applicable | Exploited | Lodash versions prior to 4.17.21 are vulnerable to Command Injection via the template function. |
| CVE-2020-13949 | High | 2021-02-12 | No exploit published | No public exploit | In Apache Thrift 0.9.3 to 0.13.0, malicious RPC clients could send short messages which would result in a large memory allocation, potentially leading to denial of service. |
| CVE-2020-29582 | Medium | 2021-02-03 | No exploit published | No public exploit | In JetBrains Kotlin before 1.4.21, a vulnerable Java API was used for temporary file and folder creation. An attacker was able to read data from such files and list directories due to insecure permissions. |
| CVE-2021-3326 | High | 2021-01-27 | Outside Waratek scope | No public exploit | The iconv function in the GNU C Library (aka glibc or libc6) 2.32 and earlier, when processing invalid input sequences in the ISO-2022-JP-3 encoding, fails an assertion in the code path and aborts the program, potentially resulting in a denial of service. |
| CVE-2020-8554 | Medium | 2021-01-21 | Outside Waratek scope | No public exploit | Kubernetes API server in all versions allow an attacker who is able to create a ClusterIP service and set the spec.externalIPs field, to intercept traffic to that IP address. Additionally, an attacker who is able to patch the status (which is considered a privileged operation and should not typically be granted to users) of a LoadBalancer service can set the status.loadBalancer.ingress.ip to similar effect. |
| CVE-2020-14756 | Critical | 2021-01-20 | Protected by Waratek | Exploited | Vulnerability in the Oracle Coherence product of Oracle Fusion Middleware (component: Core Components). Supported versions that are affected are 3.7.1.0, 12.1.3.0.0, 12.2.1.3.0, 12.2.1.4.0 and 14.1.1.0.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via IIOP, T3 to compromise Oracle Coherence. Successful attacks of this vulnerability can result in takeover of Oracle Coherence. CVSS 3.1 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2021-3177 | Critical | 2021-01-19 | Outside Waratek scope | Proof of concept only | Python 3.x through 3.9.1 has a buffer overflow in PyCArg_repr in _ctypes/callproc.c, which may lead to remote code execution in certain Python applications that accept floating-point numbers as untrusted input, as demonstrated by a 1e300 argument to c_double.from_param. This occurs because sprintf is used unsafely. |
| CVE-2020-36189 | High | 2021-01-06 | No exploit published | No public exploit | FasterXML jackson-databind 2.x before 2.9.10.8 mishandles the interaction between serialization gadgets and typing, related to com.newrelic.agent.deps.ch.qos.logback.core.db.DriverManagerConnectionSource. |
| CVE-2020-28052 | High | 2020-12-18 | No exploit published | No public exploit | An issue was discovered in Legion of the Bouncy Castle BC Java 1.65 and 1.66. The OpenBSDBCrypt.checkPassword utility method compared incorrect data when checking the password, allowing incorrect passwords to indicate they were matching with previously hashed ones that were different. |
| CVE-2020-8285 | High | 2020-12-14 | Not applicable | Proof of concept only | curl 7.21.0 to and including 7.73.0 is vulnerable to uncontrolled recursion due to a stack overflow issue in FTP wildcard match parsing. |
| CVE-2020-17530 | Critical | 2020-12-11 | Protected by Waratek | Exploited | Forced OGNL evaluation, when evaluated on raw user input in tag attributes, may lead to remote code execution. Affected software : Apache Struts 2.0.0 - Struts 2.5.25. |
| CVE-2020-8908 | Low | 2020-12-10 | No exploit published | No public exploit | A temp directory creation vulnerability exists in all versions of Guava, allowing an attacker with access to the machine to potentially access data in a temporary directory created by the Guava API com.google.common.io.Files.createTempDir(). By default, on unix-like systems, the created directory is world-readable (readable by an attacker with access to the system). The method in question has been marked @Deprecated in versions 30.0 and later and should not be used. For Android developers, we recommend choosing a temporary directory API provided by Android, such as context.getCacheDir(). For other Java developers, we recommend migrating to the Java 7 API java.nio.file.Files.createTempDirectory() which explicitly configures permissions of 700, or configuring the Java runtime's java.io.tmpdir system property to point to a location whose permissions are appropriately configured. |
| CVE-2020-17521 | Medium | 2020-12-07 | Protected by Waratek | No public exploit | Apache Groovy provides extension methods to aid with creating temporary directories. Prior to this fix, Groovy's implementation of those extension methods was using a now superseded Java JDK method call that is potentially not secure on some operating systems in some contexts. Users not using the extension methods mentioned in the advisory are not affected, but may wish to read the advisory for further details. Versions Affected: 2.0 to 2.4.20, 2.5.0 to 2.5.13, 3.0.0 to 3.0.6, and 4.0.0-alpha-1. Fixed in versions 2.4.21, 2.5.14, 3.0.7, 4.0.0-alpha-2. |
| CVE-2020-25649 | High | 2020-12-03 | Protected by Waratek | No public exploit | A flaw was found in FasterXML Jackson Databind, where it did not have entity expansion secured properly. This flaw allows vulnerability to XML external entity (XXE) attacks. The highest threat from this vulnerability is data integrity. |
| CVE-2020-17527 | High | 2020-12-03 | No exploit published | No public exploit | While investigating bug 64830 it was discovered that Apache Tomcat 10.0.0-M1 to 10.0.0-M9, 9.0.0-M1 to 9.0.39 and 8.5.0 to 8.5.59 could re-use an HTTP request header value from the previous stream received on an HTTP/2 connection for the request associated with the subsequent stream. While this would most likely lead to an error and the closure of the HTTP/2 connection, it is possible that information could leak between requests. |
| CVE-2020-13956 | Medium | 2020-12-02 | Outside Waratek scope | No public exploit | Apache HttpClient versions prior to version 4.5.13 and 5.0.3 can misinterpret malformed authority component in request URIs passed to the library as java.net.URI object and pick the wrong target host for request execution. |
| CVE-2019-17566 | High | 2020-11-12 | Protected by Waratek | No public exploit | Apache Batik is vulnerable to server-side request forgery, caused by improper input validation by the "xlink:href" attributes. By using a specially-crafted argument, an attacker could exploit this vulnerability to cause the underlying server to make arbitrary GET requests. |
| CVE-2020-11979 | High | 2020-10-01 | No exploit published | No public exploit | As mitigation for CVE-2020-1945 Apache Ant 1.10.8 changed the permissions of temporary files it created so that only the current user was allowed to access them. Unfortunately the fixcrlf task deleted the temporary file and created a new one without said protection, effectively nullifying the effort. This would still allow an attacker to inject modified source files into the build process. |
| CVE-2020-5421 | Medium | 2020-09-19 | No exploit published | No public exploit | In Spring Framework versions 5.2.0 - 5.2.8, 5.1.0 - 5.1.17, 5.0.0 - 5.0.18, 4.3.0 - 4.3.28, and older unsupported versions, the protections against RFD attacks from CVE-2015-5211 may be bypassed depending on the browser used through the use of a jsessionid path parameter. |
| CVE-2020-24750 | High | 2020-09-17 | Protected by Waratek | No public exploit | FasterXML jackson-databind 2.x before 2.9.10.6 mishandles the interaction between serialization gadgets and typing, related to com.pastdev.httpcomponents.configuration.JndiConfiguration. |
| CVE-2020-7712 | High | 2020-08-30 | Protected by Waratek | No public exploit | This affects the package json before 10.0.0. It is possible to inject arbritary commands using the parseLookup function. |
| CVE-2020-15824 | High | 2020-08-08 | No exploit published | No public exploit | In JetBrains Kotlin from 1.4-M1 to 1.4-RC (as Kotlin 1.3.7x is not affected by the issue. Fixed version is 1.4.0) there is a script-cache privilege escalation vulnerability due to kotlin-main-kts cached scripts in the system temp directory, which is shared by all users by default. |
| CVE-2020-13935 | High | 2020-07-14 | Mitigation candidate | Working exploit published | The payload length in a WebSocket frame was not correctly validated in Apache Tomcat 10.0.0-M1 to 10.0.0-M6, 9.0.0.M1 to 9.0.36, 8.5.0 to 8.5.56 and 7.0.27 to 7.0.104. Invalid payload lengths could trigger an infinite loop. Multiple requests with invalid payload lengths could lead to a denial of service. |
| CVE-2020-10878 | High | 2020-06-05 | Outside Waratek scope | No public exploit | Perl before 5.30.3 has an integer overflow related to mishandling of a "PL_regkind[OP(n)] == NOTHING" situation. A crafted regular expression could lead to malformed bytecode with a possibility of instruction injection. |
| CVE-2020-13817 | High | 2020-06-04 | Outside Waratek scope | No public exploit | ntpd in ntp before 4.2.8p14 and 4.3.x before 4.3.100 allows remote attackers to cause a denial of service (daemon exit or system time change) by predicting transmit timestamps for use in spoofed packets. The victim must be relying on unauthenticated IPv4 time sources. There must be an off-path attacker who can query time from the victim's ntpd instance. |
| CVE-2020-10683 | Critical | 2020-05-01 | Protected by Waratek | No public exploit | dom4j before 2.0.3 and 2.1.x before 2.1.3 allows external DTDs and External Entities by default, which might enable XXE attacks. However, there is popular external documentation from OWASP showing how to enable the safe, non-default behavior in any application that uses dom4j. |
| CVE-2020-11023 | Medium | 2020-04-29 | Outside Waratek scope | Exploited | In jQuery versions greater than or equal to 1.0.3 and before 3.5.0, passing HTML containing <option> elements from untrusted sources - even after sanitizing it - to one of jQuery's DOM manipulation methods (i.e. .html(), .append(), and others) may execute untrusted code. This problem is patched in jQuery 3.5.0. |
| CVE-2020-11022 | Medium | 2020-04-29 | Outside Waratek scope | Exploited | In jQuery starting with 1.12.0 and before 3.5.0, passing HTML from untrusted sources - even after sanitizing it - to one of jQuery's DOM manipulation methods (i.e. .html(), .append(), and others) may execute untrusted code. This problem is patched in jQuery 3.5.0. |
| CVE-2020-2934 | Medium | 2020-04-15 | Outside Waratek scope | No public exploit | Vulnerability in the MySQL Connectors product of Oracle MySQL (component: Connector/J). Supported versions that are affected are 8.0.19 and prior and 5.1.48 and prior. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise MySQL Connectors. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of MySQL Connectors accessible data as well as unauthorized read access to a subset of MySQL Connectors accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of MySQL Connectors. CVSS 3.0 Base Score 5.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:R/S:U/C:L/I:L/A:L). |
| CVE-2020-5258 | High | 2020-03-10 | Outside Waratek scope | No public exploit | In affected versions of dojo (NPM package), the deepCopy method is vulnerable to Prototype Pollution. Prototype Pollution refers to the ability to inject properties into existing JavaScript language construct prototypes, such as objects. An attacker manipulates these attributes to overwrite, or pollute, a JavaScript application object prototype of the base object by injecting other values. This has been patched in versions 1.12.8, 1.13.7, 1.14.6, 1.15.3 and 1.16.2 |
| CVE-2020-9281 | Medium | 2020-03-07 | Outside Waratek scope | No public exploit | A cross-site scripting (XSS) vulnerability in the HTML Data Processor for CKEditor 4.0 before 4.14 allows remote attackers to inject arbitrary web script through a crafted "protected" comment (with the cke_protected syntax). |
| CVE-2018-1311 | High | 2019-12-18 | Not applicable | No public exploit | The Apache Xerces-C 3.0.0 to 3.2.3 XML parser contains a use-after-free error triggered during the scanning of external DTDs. This flaw has not been addressed in the maintained version of the library and has no current mitigation other than to disable DTD processing. This can be accomplished via the DOM using a standard parser feature, or via SAX using the XERCES_DISABLE_DTD environment variable. |
| CVE-2019-13734 | High | 2019-12-10 | Outside Waratek scope | No public exploit | Out of bounds write in SQLite in Google Chrome prior to 79.0.3945.79 allowed a remote attacker to potentially exploit heap corruption via a crafted HTML page. |
| CVE-2019-10219 | Medium | 2019-11-08 | Protected by Waratek | No public exploit | A vulnerability was found in Hibernate-Validator. The SafeHtml validator annotation fails to properly sanitize payloads consisting of potentially malicious code in HTML comments and instructions. This vulnerability can result in an XSS attack. |
| CVE-2019-17495 | Critical | 2019-10-10 | No exploit published | No public exploit | A Cascading Style Sheets (CSS) injection vulnerability in Swagger UI before 3.23.11 allows attackers to use the Relative Path Overwrite (RPO) technique to perform CSS-based input field value exfiltration, such as exfiltration of a CSRF token value. In other words, this product intentionally allows the embedding of untrusted JSON data from remote servers, but it was not previously known that <style>@import within the JSON data was a functional attack method. |
| CVE-2019-10086 | High | 2019-08-20 | Protected by Waratek | No public exploit | In Apache Commons Beanutils 1.9.2, a special BeanIntrospector class was added which allows suppressing the ability for an attacker to access the classloader via the class property available on all Java objects. We, however were not using this by default characteristic of the PropertyUtilsBean. |
| CVE-2018-1324 | Medium | 2018-03-16 | No exploit published | No public exploit | A specially crafted ZIP archive can be used to cause an infinite loop inside of Apache Commons Compress' extra field parser used by the ZipFile and ZipArchiveInputStream classes in versions 1.11 to 1.15. This can be used to mount a denial of service attack against services that use Compress' zip package. |
| CVE-2016-7103 | Medium | 2017-03-15 | Outside Waratek scope | No public exploit | Cross-site scripting (XSS) vulnerability in jQuery UI before 1.12.0 might allow remote attackers to inject arbitrary web script or HTML via the closeText parameter of the dialog function. |