
Oracle Critical Patch Update April 2018
Released April 2018 · Oracle's advisory ↗ · ← Critical Patch Update, January 2018 · Critical Patch Update, July 2018 →
165 CVEs in this release, one square each
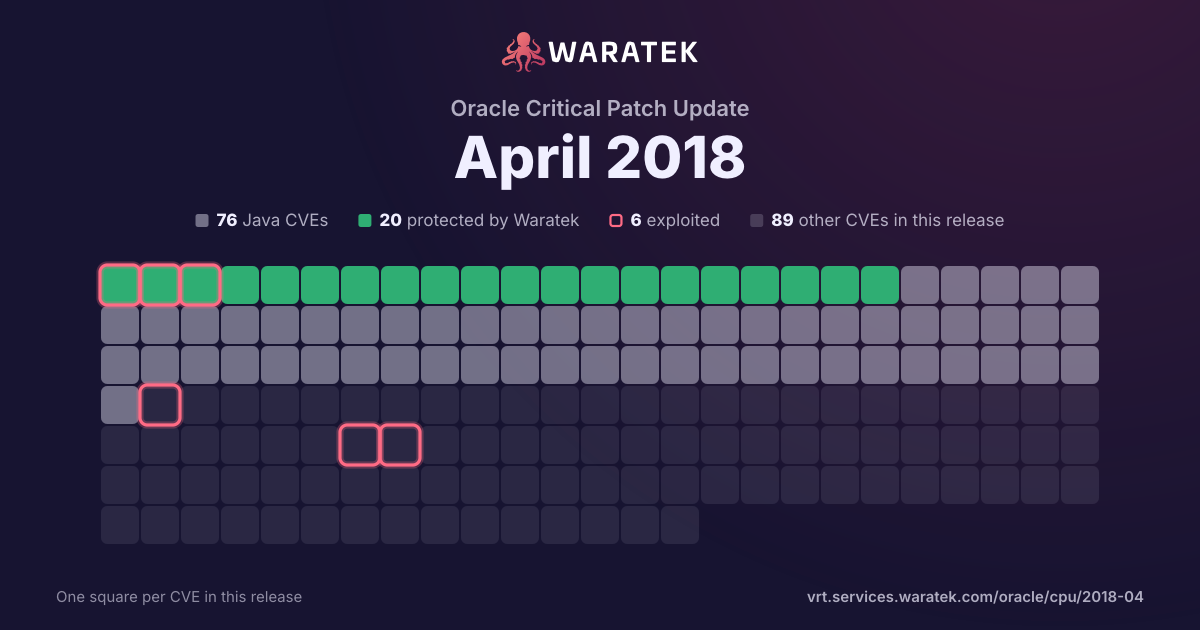
By status
22Protected by Waratek2Mitigation candidate59No exploit published6Outside Waratek scope76Not applicable
6Exploited, marked by the ring
No exploit published. For 54 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 16 matches · 7 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
Protected by Waratek
7
43.8%
Rule in development
0
0.0%
Mitigation candidate
1
6.2%
No exploit published
8
50.0%
blocked by ARMR today
7
43.8%
partly blocked
0
0.0%
not blocked
9
56.2%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
16
100.0%
split by
peak 7 / quarter
Q3 131
Mitigation candidate1
High1
not blocked1
No public exploit1
Q4 130
Q1 140
Q2 140
Q3 140
Q4 140
Q1 150
Q2 150
Q3 150
Q4 151
No exploit published1
Medium1
not blocked1
No public exploit1
Q1 160
Q2 160
Q3 162
No exploit published2
High2
not blocked2
No public exploit2
Q4 161
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Q1 170
Q2 171
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Q3 170
Q4 170
Q1 183
Protected by Waratek3
Critical3
blocked by ARMR today3
No public exploit3
Q2 187
Protected by Waratek2
No exploit published5
Critical1
High4
Medium2
blocked by ARMR today2
not blocked5
No public exploit7
Q4 13Q2 14Q4 14Q2 15Q4 15Q2 16Q4 16Q2 17Q4 17Q2 18
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2018-2834 | High | 2018-04-19 | No exploit published | No public exploit | Vulnerability in the Oracle Data Visualization Desktop component of Oracle Fusion Middleware (subcomponent: Security). The supported version that is affected is 12.2.4.1.1. Easily exploitable vulnerability allows unauthenticated attacker with logon to the infrastructure where Oracle Data Visualization Desktop executes to compromise Oracle Data Visualization Desktop. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Data Visualization Desktop, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Data Visualization Desktop accessible data as well as unauthorized read access to a subset of Oracle Data Visualization Desktop accessible data and unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Data Visualization Desktop. Note: Please refer to Doc ID <a href="http://support.oracle.com/CSP/main/article?cmd=show&type=NOT&id=2384640.1">My Oracle Support Note 2384640.1 for instructions on how to address this issue. CVSS 3.0 Base Score 8.5 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:N/UI:R/S:C/C:L/I:H/A:H). |
| CVE-2018-2828 | High | 2018-04-19 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Content component of Oracle Fusion Middleware (subcomponent: Content Server). Supported versions that are affected are 11.1.1.9.0, 12.2.1.2.0 and 12.2.1.3.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle WebCenter Content. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle WebCenter Content, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle WebCenter Content accessible data as well as unauthorized update, insert or delete access to some of Oracle WebCenter Content accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle WebCenter Content. CVSS 3.0 Base Score 8.2 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:H/I:L/A:L). |
| CVE-2018-2770 | High | 2018-04-19 | No exploit published | No public exploit | Vulnerability in the Oracle Adaptive Access Manager component of Oracle Fusion Middleware (subcomponent: OAAM Admin). The supported version that is affected is 11.1.2.3.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Adaptive Access Manager. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Adaptive Access Manager, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Adaptive Access Manager accessible data as well as unauthorized update, insert or delete access to some of Oracle Adaptive Access Manager accessible data. CVSS 3.0 Base Score 7.6 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2018-2765 | High | 2018-04-19 | No exploit published | No public exploit | Vulnerability in the Oracle Security Service component of Oracle Fusion Middleware (subcomponent: Oracle SSL API). Supported versions that are affected are 11.1.1.9.0, 12.1.3.0.0, 12.2.1.2.0 and 12.2.1.3.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTPS to compromise Oracle Security Service. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Security Service accessible data. CVSS 3.0 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2018-2760 | Medium | 2018-04-19 | No exploit published | No public exploit | Vulnerability in the Oracle HTTP Server component of Oracle Fusion Middleware (subcomponent: OSSL Module). Supported versions that are affected are 12.1.3 and 12.2.1.2. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTPS to compromise Oracle HTTP Server. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle HTTP Server accessible data. CVSS 3.0 Base Score 5.9 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2018-2739 | Critical | 2018-04-19 | Protected by Waratek | No public exploit | Vulnerability in the Oracle Access Manager component of Oracle Fusion Middleware (subcomponent: Web Server Plugin). Supported versions that are affected are 10.1.4.3.0, 11.1.2.3.0 and 12.2.1.3.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Access Manager. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Access Manager, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Access Manager accessible data as well as unauthorized access to critical data or complete access to all Oracle Access Manager accessible data. CVSS 3.0 Base Score 9.3 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:H/A:N). |
| CVE-2018-2587 | Medium | 2018-04-19 | Protected by Waratek | No public exploit | Vulnerability in the Oracle Access Manager component of Oracle Fusion Middleware (subcomponent: Web Server Plugin). Supported versions that are affected are 10.1.4.3.0, 11.1.2.3.0 and 12.2.1.3.0. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Access Manager. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Access Manager accessible data as well as unauthorized read access to a subset of Oracle Access Manager accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:L/I:H/A:N). |
| CVE-2018-7489 | Critical | 2018-02-26 | Protected by Waratek | No public exploit | FasterXML jackson-databind before 2.7.9.3, 2.8.x before 2.8.11.1 and 2.9.x before 2.9.5 allows unauthenticated remote code execution because of an incomplete fix for the CVE-2017-7525 deserialization flaw. This is exploitable by sending maliciously crafted JSON input to the readValue method of the ObjectMapper, bypassing a blacklist that is ineffective if the c3p0 libraries are available in the classpath. |
| CVE-2017-15095 | Critical | 2018-02-06 | Protected by Waratek | No public exploit | A deserialization flaw was discovered in the jackson-databind in versions before 2.8.10 and 2.9.1, which could allow an unauthenticated user to perform code execution by sending the maliciously crafted input to the readValue method of the ObjectMapper. This issue extends the previous flaw CVE-2017-7525 by blacklisting more classes that could be used maliciously. |
| CVE-2016-6814 | Critical | 2018-01-18 | Protected by Waratek | No public exploit | When an application with unsupported Codehaus versions of Groovy from 1.7.0 to 2.4.3, Apache Groovy 2.4.4 to 2.4.7 on classpath uses standard Java serialization mechanisms, e.g. to communicate between servers or to store local data, it was possible for an attacker to bake a special serialized object that will execute code directly when deserialized. All applications which rely on serialization and do not isolate the code which deserializes objects were subject to this vulnerability. |
| CVE-2017-5662 | High | 2017-04-18 | Protected by Waratek | No public exploit | In Apache Batik before 1.9, files lying on the filesystem of the server which uses batik can be revealed to arbitrary users who send maliciously formed SVG files. The file types that can be shown depend on the user context in which the exploitable application is running. If the user is root a full compromise of the server - including confidential or sensitive files - would be possible. XXE can also be used to attack the availability of the server via denial of service as the references within a xml document can trivially trigger an amplification attack. |
| CVE-2016-5019 | Critical | 2016-10-03 | Protected by Waratek | No public exploit | CoreResponseStateManager in Apache MyFaces Trinidad 1.0.0 through 1.0.13, 1.2.x before 1.2.15, 2.0.x before 2.0.2, and 2.1.x before 2.1.2 might allow attackers to conduct deserialization attacks via a crafted serialized view state string. |
| CVE-2016-0635 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Ops Center component in Oracle Enterprise Manager Grid Control 12.1.4, 12.2.2, and 12.3.2; the Oracle Health Sciences Information Manager component in Oracle Health Sciences Applications 1.2.8.3, 2.0.2.3, and 3.0.1.0; the Oracle Healthcare Master Person Index component in Oracle Health Sciences Applications 2.0.12, 3.0.0, and 4.0.1; the Oracle Documaker component in Oracle Insurance Applications before 12.5; the Oracle Insurance Calculation Engine component in Oracle Insurance Applications 9.7.1, 10.1.2, and 10.2.2; the Oracle Insurance Policy Administration J2EE and Oracle Insurance Rules Palette components in Oracle Insurance Applications 9.6.1, 9.7.1, 10.0.1, 10.1.2, 10.2.0, and 10.2.2; the Oracle Retail Integration Bus component in Oracle Retail Applications 15.0; the Oracle Retail Order Broker component in Oracle Retail Applications 5.1, 5.2, and 15.0; the Primavera Contract Management component in Oracle Primavera Products Suite 14.2; the Primavera P6 Enterprise Project Portfolio Management component in Oracle Primavera Products Suite 8.2, 8.3, 8.4, 15.1, 15.2, and 16.1; the Oracle Financial Services Analytical Applications Infrastructure component in Oracle Financial Services Applications 8.0.0, 8.0.1, 8.0.2, and 8.0.3; the Oracle Commerce Guided Search / Oracle Commerce Experience Manager component in Oracle Commerce 3.1.1, 3.1.2, 11.0, 11.1, and 11.2; the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5; the Oracle Communications BRM - Elastic Charging Engine 11.2.0.0.0 and 11.3.0.0.0; the Oracle Enterprise Repository Enterprise Repository 12.1.3.0.0; the Oracle Financial Services Behavior Detection Platform 8.0.1 and 8.0.2; the Oracle Hyperion Essbase 12.2.1.1; the Oracle Tuxedo System and Applications Monitor (TSAM) 11.1.1.2.0, 11.1.1.2.1, 11.1.1.2.1, 12.1.1.1.0, 12.1.3.0.0, and 12.2.2.0.0; the Oracle Communications WebRTC Session Controller component of Oracle Communications Applications (subcomponent: Security (Spring)) 7.0, 7.1 and 7.2; the Oracle Endeca Information Discovery Integrator 3.2; the Converged Commerce component of Oracle Retail Applications 16.0.1; the Oracle Identity Manager 11.1.2.3.0; Oracle Enterprise Manager for MySQL Database 12.1.0.4; Oracle Retail Invoice Matching 12.0, 13.0, 13.1, 13.2, 14.0, and 14.1; Oracle Communications Performance Intelligence Center (PIC) Software Prior to 10.2.1 and the Oracle Knowledge component of Oracle Siebel CRM (subcomponent: AnswerFlow (Spring Framework)) version 8.5.1.0 - 8.5.1.7 and 8.6.0 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-3092 | High | 2016-07-04 | No exploit published | No public exploit | The MultipartStream class in Apache Commons Fileupload before 1.3.2, as used in Apache Tomcat 7.x before 7.0.70, 8.x before 8.0.36, 8.5.x before 8.5.3, and 9.x before 9.0.0.M7 and other products, allows remote attackers to cause a denial of service (CPU consumption) via a long boundary string. |
| CVE-2015-7940 | Medium | 2015-11-09 | No exploit published | No public exploit | The Bouncy Castle Java library before 1.51 does not validate a point is withing the elliptic curve, which makes it easier for remote attackers to obtain private keys via a series of crafted elliptic curve Diffie Hellman (ECDH) key exchanges, aka an "invalid curve attack." |
| CVE-2013-1768 | High | 2013-07-11 | Mitigation candidate | No public exploit | The BrokerFactory functionality in Apache OpenJPA 1.x before 1.2.3 and 2.x before 2.2.2 creates local executable JSP files containing logging trace data produced during deserialization of certain crafted OpenJPA objects, which makes it easier for remote attackers to execute arbitrary code by creating a serialized object and leveraging improperly secured server programs. |