
Oracle Critical Patch Update April 2017
Released April 2017 · Oracle's advisory ↗ · ← Critical Patch Update, January 2017 · Critical Patch Update, July 2017 →
227 CVEs in this release, one square each
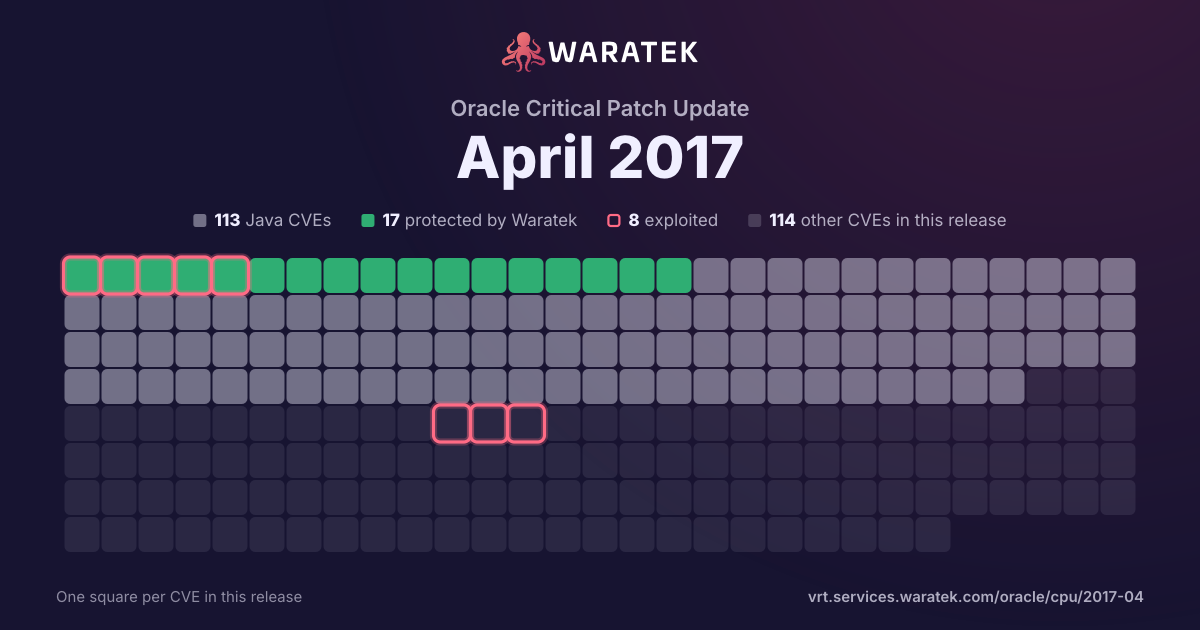
By status
17Protected by Waratek1Mitigation candidate95No exploit published13Outside Waratek scope101Not applicable
8Exploited, marked by the ring
No exploit published. For 93 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 227 matches · 113 in Waratek scope · 17 protected · 8 exploited · 3 CISA KEV · 21 public PoC · 13 EPSS ≥ 0.5
227matches
113in Waratek scope49.8%
17protected7.5%
8exploited3.5%
3CISA KEV1.3%
21public PoC9.3%
13EPSS ≥ 0.55.7%
Protected by Waratek
17
7.5%
Rule in development
0
0.0%
Mitigation candidate
1
0.4%
No exploit published
95
41.9%
Outside Waratek scope
13
5.7%
Not applicable
101
44.5%
Withdrawn CVE
0
0.0%
blocked by ARMR today
17
7.5%
partly blocked
0
0.0%
not blocked
210
92.5%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
8
3.5%
Working exploit published
13
5.7%
Proof of concept only
0
0.0%
Forecast only
4
1.8%
No public exploit
202
89.0%
split by
peak 197 / year
20091
Not applicable1
Critical1
not blocked1
Working exploit published1
20100
20110
20122
Not applicable2
High1
Medium1
not blocked2
No public exploit2
20133
Outside Waratek scope1
Not applicable2
High1
Medium2
not blocked3
Forecast only1
No public exploit2
20142
Protected by Waratek1
No exploit published1
High1
Medium1
blocked by ARMR today1
not blocked1
Exploited1
No public exploit1
20155
Protected by Waratek1
Outside Waratek scope1
Not applicable3
Critical1
High1
Medium3
blocked by ARMR today1
not blocked4
Exploited2
No public exploit3
201617
Protected by Waratek4
No exploit published2
Outside Waratek scope2
Not applicable9
Critical6
High9
Medium2
blocked by ARMR today4
not blocked13
Working exploit published1
Forecast only2
No public exploit14
2017197
Protected by Waratek11
Mitigation candidate1
No exploit published92
Outside Waratek scope9
Not applicable84
Critical9
High86
Medium84
Low18
blocked by ARMR today11
not blocked186
Exploited5
Working exploit published11
Forecast only1
No public exploit180
200920102011201220132014201520162017
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2017-3526 | Medium | 2017-04-24 | Protected by Waratek | No public exploit | Vulnerability in the Java SE, Java SE Embedded, JRockit component of Oracle Java SE (subcomponent: JAXP). Supported versions that are affected are Java SE: 6u141, 7u131 and 8u121; Java SE Embedded: 8u121; JRockit: R28.3.13. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE, Java SE Embedded, JRockit. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Java SE, Java SE Embedded, JRockit. Note: Applies to client and server deployment of Java. This vulnerability can be exploited through sandboxed Java Web Start applications and sandboxed Java applets. It can also be exploited by supplying data to APIs in the specified Component without using sandboxed Java Web Start applications or sandboxed Java applets, such as through a web service. CVSS 3.0 Base Score 5.9 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3525 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise SCM Service Procurement component of Oracle PeopleSoft Products (subcomponent: Usability). The supported version that is affected is 9.2. Easily "exploitable" vulnerability allows high privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise SCM Service Procurement. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all PeopleSoft Enterprise SCM Service Procurement accessible data as well as unauthorized access to critical data or complete access to all PeopleSoft Enterprise SCM Service Procurement accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-3524 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise SCM Strategic Sourcing component of Oracle PeopleSoft Products (subcomponent: Bidder Registration). The supported version that is affected is 9.2. Easily "exploitable" vulnerability allows high privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise SCM Strategic Sourcing. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all PeopleSoft Enterprise SCM Strategic Sourcing accessible data as well as unauthorized access to critical data or complete access to all PeopleSoft Enterprise SCM Strategic Sourcing accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-3523 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Connectors component of Oracle MySQL (subcomponent: Connector/J). Supported versions that are affected are 5.1.40 and earlier. Difficult to exploit vulnerability allows low privileged attacker with network access via multiple protocols to compromise MySQL Connectors. While the vulnerability is in MySQL Connectors, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of MySQL Connectors. CVSS 3.0 Base Score 8.5 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:L/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2017-3522 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise SCM eSupplier Connection component of Oracle PeopleSoft Products (subcomponent: Vendor). The supported version that is affected is 9.2. Easily "exploitable" vulnerability allows high privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise SCM eSupplier Connection. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all PeopleSoft Enterprise SCM eSupplier Connection accessible data as well as unauthorized access to critical data or complete access to all PeopleSoft Enterprise SCM eSupplier Connection accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-3521 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise SCM Purchasing component of Oracle PeopleSoft Products (subcomponent: Supplier Registration). The supported version that is affected is 9.2. Easily "exploitable" vulnerability allows high privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise SCM Purchasing. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all PeopleSoft Enterprise SCM Purchasing accessible data as well as unauthorized access to critical data or complete access to all PeopleSoft Enterprise SCM Purchasing accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-3520 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Fluid Core). Supported versions that are affected are 8.54 and 8.55. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 6.5 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:U/C:N/I:H/A:N). |
| CVE-2017-3519 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Security). Supported versions that are affected are 8.54 and 8.55. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-3518 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Enterprise Manager Base Platform component of Oracle Enterprise Manager Grid Control (subcomponent: Discovery Framework). Supported versions that are affected are 12.1.0, 13.1.0 and 13.2.0. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTPS to compromise Enterprise Manager Base Platform. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Enterprise Manager Base Platform. CVSS 3.0 Base Score 7.5 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3517 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the JD Edwards EnterpriseOne Tools component of Oracle JD Edwards Products (subcomponent: Web Runtime SEC). The supported version that is affected is 9.2. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise JD Edwards EnterpriseOne Tools. Successful attacks of this vulnerability can result in unauthorized read access to a subset of JD Edwards EnterpriseOne Tools accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of JD Edwards EnterpriseOne Tools. CVSS 3.0 Base Score 6.5 (Confidentiality and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:L). |
| CVE-2017-3516 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Solaris component of Oracle Sun Systems Products Suite (subcomponent: Kernel Zones virtualized NIC driver). The supported version that is affected is 11.3. Easily "exploitable" vulnerability allows low privileged attacker with network access via multiple protocols to compromise Solaris. While the vulnerability is in Solaris, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Solaris. CVSS 3.0 Base Score 7.7 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:N/I:N/A:H). |
| CVE-2017-3515 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle User Management component of Oracle E-Business Suite (subcomponent: User Name/Password Management). Supported versions that are affected are 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle User Management. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle User Management, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle User Management accessible data. CVSS 3.0 Base Score 4.7 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:N/I:L/A:N). |
| CVE-2017-3514 | High | 2017-04-24 | Outside Waratek scope | No public exploit | Vulnerability in the Java SE component of Oracle Java SE (subcomponent: AWT). Supported versions that are affected are Java SE: 6u141, 7u131 and 8u121. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Java SE, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Java SE. Note: This vulnerability applies to Java deployments, typically in clients running sandboxed Java Web Start applications or sandboxed Java applets, that load and run untrusted code (e.g., code that comes from the internet) and rely on the Java sandbox for security. This vulnerability does not apply to Java deployments, typically in servers, that load and run only trusted code (e.g., code installed by an administrator). CVSS 3.0 Base Score 8.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:R/S:C/C:H/I:H/A:H). |
| CVE-2017-3513 | Low | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Oracle VM VirtualBox component of Oracle Virtualization (subcomponent: Core). Supported versions that are affected are Prior to 5.0.38 and Prior to 5.1.20. Difficult to exploit vulnerability allows high privileged attacker with logon to the infrastructure where Oracle VM VirtualBox executes to compromise Oracle VM VirtualBox. While the vulnerability is in Oracle VM VirtualBox, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle VM VirtualBox accessible data. CVSS 3.0 Base Score 2.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:H/UI:N/S:C/C:L/I:N/A:N). |
| CVE-2017-3512 | High | 2017-04-24 | Outside Waratek scope | No public exploit | Vulnerability in the Java SE component of Oracle Java SE (subcomponent: AWT). Supported versions that are affected are Java SE: 7u131 and 8u121. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Java SE, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Java SE. Note: This vulnerability applies to Java deployments, typically in clients running sandboxed Java Web Start applications or sandboxed Java applets, that load and run untrusted code (e.g., code that comes from the internet) and rely on the Java sandbox for security. This vulnerability does not apply to Java deployments, typically in servers, that load and run only trusted code (e.g., code installed by an administrator). CVSS 3.0 Base Score 8.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:R/S:C/C:H/I:H/A:H). |
| CVE-2017-3511 | High | 2017-04-24 | Protected by Waratek | No public exploit | Vulnerability in the Java SE, Java SE Embedded, JRockit component of Oracle Java SE (subcomponent: JCE). Supported versions that are affected are Java SE: 7u131 and 8u121; Java SE Embedded: 8u121; JRockit: R28.3.13. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Java SE, Java SE Embedded, JRockit executes to compromise Java SE, Java SE Embedded, JRockit. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Java SE, Java SE Embedded, JRockit, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Java SE, Java SE Embedded, JRockit. Note: Applies to client and server deployment of Java. This vulnerability can be exploited through sandboxed Java Web Start applications and sandboxed Java applets. It can also be exploited by supplying data to APIs in the specified Component without using sandboxed Java Web Start applications or sandboxed Java applets, such as through a web service. CVSS 3.0 Base Score 7.7 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:N/UI:R/S:C/C:H/I:H/A:H). |
| CVE-2017-3510 | Critical | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Solaris component of Oracle Sun Systems Products Suite (subcomponent: Kernel Zones virtualized NIC driver). The supported version that is affected is 11.3. Easily "exploitable" vulnerability allows low privileged attacker with network access via multiple protocols to compromise Solaris. While the vulnerability is in Solaris, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Solaris accessible data. CVSS 3.0 Base Score 7.7 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:N/I:H/A:N). |
| CVE-2017-3509 | Medium | 2017-04-24 | Outside Waratek scope | No public exploit | Vulnerability in the Java SE, Java SE Embedded component of Oracle Java SE (subcomponent: Networking). Supported versions that are affected are Java SE: 6u141, 7u131 and 8u121; Java SE Embedded: 8u121. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE, Java SE Embedded. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Java SE, Java SE Embedded accessible data as well as unauthorized read access to a subset of Java SE, Java SE Embedded accessible data. Note: This vulnerability applies to Java deployments, typically in clients running sandboxed Java Web Start applications or sandboxed Java applets, that load and run untrusted code (e.g., code that comes from the internet) and rely on the Java sandbox for security. This vulnerability does not apply to Java deployments, typically in servers, that load and run only trusted code (e.g., code installed by an administrator). CVSS 3.0 Base Score 4.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:R/S:U/C:L/I:L/A:N). |
| CVE-2017-3508 | Critical | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Primavera Gateway component of Oracle Primavera Products Suite (subcomponent: Primavera Desktop Integration). Supported versions that are affected are 1.0, 1.1, 14.2, 15.1, 15.2, 16.1 and 16.2. Easily "exploitable" vulnerability allows high privileged attacker with network access via HTTP to compromise Primavera Gateway. While the vulnerability is in Primavera Gateway, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Primavera Gateway. CVSS 3.0 Base Score 9.1 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2017-3507 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Service Bus component of Oracle Fusion Middleware (subcomponent: Web Console Design). Supported versions that are affected are 12.1.3.0.0, 12.2.1.0.0, 12.2.1.1.0 and 12.2.1.2.0. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Service Bus. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Service Bus accessible data as well as unauthorized read access to a subset of Oracle Service Bus accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Service Bus. CVSS 3.0 Base Score 7.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:L). |
| CVE-2017-3506 | High | 2017-04-24 | Protected by Waratek | Exploited | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: Web Services). Supported versions that are affected are 10.3.6.0, 12.1.3.0, 12.2.1.0, 12.2.1.1 and 12.2.1.2. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebLogic Server. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle WebLogic Server accessible data as well as unauthorized access to critical data or complete access to all Oracle WebLogic Server accessible data. CVSS 3.0 Base Score 7.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-3505 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Automatic Service Request (ASR) component of Oracle Support Tools (subcomponent: ASR Manager). The supported version that is affected is Prior to 5.7. Easily "exploitable" vulnerability allows unauthenticated attacker with logon to the infrastructure where Automatic Service Request (ASR) executes to compromise Automatic Service Request (ASR). Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Automatic Service Request (ASR) accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Automatic Service Request (ASR). CVSS 3.0 Base Score 5.1 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:N/UI:N/S:U/C:N/I:L/A:L). |
| CVE-2017-3504 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Automatic Service Request (ASR) component of Oracle Support Tools (subcomponent: ASR Manager). The supported version that is affected is Prior to 5.7. Easily "exploitable" vulnerability allows unauthenticated attacker with logon to the infrastructure where Automatic Service Request (ASR) executes to compromise Automatic Service Request (ASR). Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Automatic Service Request (ASR) accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Automatic Service Request (ASR). CVSS 3.0 Base Score 5.1 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:N/UI:N/S:U/C:N/I:L/A:L). |
| CVE-2017-3503 | Critical | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Primavera P6 Enterprise Project Portfolio Management component of Oracle Primavera Products Suite (subcomponent: Web Access (Apache Commons BeanUtils)). Supported versions that are affected are 8.3, 8.4, 15.1, 15.2, 16.1 and 16.2. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Primavera P6 Enterprise Project Portfolio Management. While the vulnerability is in Primavera P6 Enterprise Project Portfolio Management, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Primavera P6 Enterprise Project Portfolio Management. CVSS 3.0 Base Score 9.9 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2017-3502 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FIN Receivables component of Oracle PeopleSoft Products (subcomponent: Receivables). The supported version that is affected is 9.2. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise FIN Receivables. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise FIN Receivables accessible data. CVSS 3.0 Base Score 5.3 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2017-3501 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Primavera Unifier component of Oracle Primavera Products Suite (subcomponent: Platform). Supported versions that are affected are 9.13, 9.14, 10.0, 10.1, 15.1 and 15.2. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Primavera Unifier. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Primavera Unifier, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Primavera Unifier accessible data as well as unauthorized read access to a subset of Primavera Unifier accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-3500 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Primavera Gateway component of Oracle Primavera Products Suite (subcomponent: Primavera Desktop Integration). Supported versions that are affected are 1.0, 1.1, 14.2, 15.1, 15.2, 16.1 and 16.2. Easily "exploitable" vulnerability allows high privileged attacker with network access via HTTP to compromise Primavera Gateway. While the vulnerability is in Primavera Gateway, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Primavera Gateway accessible data and unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Primavera Gateway. CVSS 3.0 Base Score 8.7 (Confidentiality and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:C/C:H/I:N/A:H). |
| CVE-2017-3499 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Social Network component of Oracle Fusion Middleware (subcomponent: Android Client). The supported version that is affected is prior to 11.1.12.0.0 (17019101). Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTPS to compromise Oracle Social Network. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Social Network accessible data. CVSS 3.0 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-3498 | Low | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Solaris component of Oracle Sun Systems Products Suite (subcomponent: Kernel). The supported version that is affected is 11.3. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Solaris executes to compromise Solaris. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Solaris accessible data. CVSS 3.0 Base Score 3.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-3497 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Solaris component of Oracle Sun Systems Products Suite (subcomponent: Remote Administration Daemon). The supported version that is affected is 11.3. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Solaris. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Solaris accessible data as well as unauthorized read access to a subset of Solaris accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Solaris. CVSS 3.0 Base Score 7.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:L). |
| CVE-2017-3496 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Enterprise Limits and Collateral Management component of Oracle Financial Services Applications (subcomponent: Infrastructure). Supported versions that are affected are 12.0.0 and 12.1.0. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle FLEXCUBE Enterprise Limits and Collateral Management. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle FLEXCUBE Enterprise Limits and Collateral Management, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Enterprise Limits and Collateral Management accessible data as well as unauthorized read access to a subset of Oracle FLEXCUBE Enterprise Limits and Collateral Management accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-3495 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Direct Banking component of Oracle Financial Services Applications (subcomponent: Pre-Login). Supported versions that are affected are 12.0.2 and 12.0.3. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle FLEXCUBE Direct Banking. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle FLEXCUBE Direct Banking, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle FLEXCUBE Direct Banking accessible data. CVSS 3.0 Base Score 4.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:N/A:N). |
| CVE-2017-3494 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Universal Banking component of Oracle Financial Services Applications (subcomponent: Retail Teller). Supported versions that are affected are 11.3.0, 11.4.0, 12.0.1, 12.0.2 and 12.0.3. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle FLEXCUBE Universal Banking. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle FLEXCUBE Universal Banking, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle FLEXCUBE Universal Banking accessible data. CVSS 3.0 Base Score 4.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:N/A:N). |
| CVE-2017-3493 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Enterprise Limits and Collateral Management component of Oracle Financial Services Applications (subcomponent: Infrastructure). Supported versions that are affected are 12.0.0 and 12.1.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Enterprise Limits and Collateral Management. While the vulnerability is in Oracle FLEXCUBE Enterprise Limits and Collateral Management, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle FLEXCUBE Enterprise Limits and Collateral Management accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle FLEXCUBE Enterprise Limits and Collateral Management. CVSS 3.0 Base Score 8.5 (Confidentiality and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:N/A:L). |
| CVE-2017-3492 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Enterprise Limits and Collateral Management component of Oracle Financial Services Applications (subcomponent: Infrastructure). Supported versions that are affected are 12.0.0 and 12.1.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Enterprise Limits and Collateral Management. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Enterprise Limits and Collateral Management accessible data as well as unauthorized read access to a subset of Oracle FLEXCUBE Enterprise Limits and Collateral Management accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-3491 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Enterprise Limits and Collateral Management component of Oracle Financial Services Applications (subcomponent: Limits and Collateral). Supported versions that are affected are 12.0.1 and 12.1.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Enterprise Limits and Collateral Management. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle FLEXCUBE Enterprise Limits and Collateral Management accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-3490 | Low | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Enterprise Limits and Collateral Management component of Oracle Financial Services Applications (subcomponent: Limits and Collateral). Supported versions that are affected are 12.0.0 and 12.1.0. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Enterprise Limits and Collateral Management. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle FLEXCUBE Enterprise Limits and Collateral Management accessible data. CVSS 3.0 Base Score 3.1 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-3489 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Investor Servicing component of Oracle Financial Services Applications (subcomponent: Security Management System). Supported versions that are affected are 12.0.1, 12.0.2, 12.0.3, 12.0.4, 12.1.0, 12.2.0 and 12.3.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Investor Servicing. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Investor Servicing accessible data as well as unauthorized read access to a subset of Oracle FLEXCUBE Investor Servicing accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-3488 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Investor Servicing component of Oracle Financial Services Applications (subcomponent: Unit Trust). Supported versions that are affected are 12.0.1, 12.0.2, 12.0.3, 12.0.4, 12.1.0, 12.2.0 and 12.3.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Investor Servicing. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle FLEXCUBE Investor Servicing accessible data. CVSS 3.0 Base Score 6.5 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:H/A:N). |
| CVE-2017-3487 | Low | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Investor Servicing component of Oracle Financial Services Applications (subcomponent: Unit Trust). Supported versions that are affected are 12.0.1, 12.0.2, 12.0.3, 12.0.4, 12.1.0, 12.2.0 and 12.3.0. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Investor Servicing. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Investor Servicing accessible data. CVSS 3.0 Base Score 3.1 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:L/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2017-3486 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the SQL*Plus component of Oracle Database Server. Supported versions that are affected are 11.2.0.4 and 12.1.0.2. Difficult to exploit vulnerability allows high privileged attacker having Local Logon privilege with logon to the infrastructure where SQL*Plus executes to compromise SQL*Plus. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in SQL*Plus, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of SQL*Plus. Note: This score is for Windows platform version 11.2.0.4 of Database. For Windows platform version 12.1.0.2 and Linux, the score is 6.3 with scope Unchanged. CVSS 3.0 Base Score 7.2 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:H/UI:R/S:C/C:H/I:H/A:H). |
| CVE-2017-3485 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Universal Banking component of Oracle Financial Services Applications (subcomponent: Infrastructure). Supported versions that are affected are 11.3.0, 11.4.0, 12.0.0, 12.0.1, 12.0.2, 12.0.3, 12.1.0 and 12.2.0. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Universal Banking. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle FLEXCUBE Universal Banking accessible data and unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle FLEXCUBE Universal Banking. CVSS 3.0 Base Score 6.8 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:L/UI:N/S:U/C:N/I:H/A:H). |
| CVE-2017-3484 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Enterprise Limits and Collateral Management component of Oracle Financial Services Applications (subcomponent: Limits and Collateral). Supported versions that are affected are 12.0.0 and 12.1.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Enterprise Limits and Collateral Management. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Enterprise Limits and Collateral Management accessible data as well as unauthorized read access to a subset of Oracle FLEXCUBE Enterprise Limits and Collateral Management accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-3483 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Enterprise Limits and Collateral Management component of Oracle Financial Services Applications (subcomponent: Limits and Collateral). Supported versions that are affected are 12.0.0 and 12.1.0. Easily "exploitable" vulnerability allows high privileged attacker with logon to the infrastructure where Oracle FLEXCUBE Enterprise Limits and Collateral Management executes to compromise Oracle FLEXCUBE Enterprise Limits and Collateral Management. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle FLEXCUBE Enterprise Limits and Collateral Management accessible data. CVSS 3.0 Base Score 4.4 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:H/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-3482 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Universal Banking component of Oracle Financial Services Applications (subcomponent: Infrastructure). Supported versions that are affected are 12.0.0, 12.0.1, 12.0.2, 12.0.3, 12.1.0, 12.2.0 and 12.3.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Universal Banking. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle FLEXCUBE Universal Banking, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Universal Banking accessible data as well as unauthorized read access to a subset of Oracle FLEXCUBE Universal Banking accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-3481 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Universal Banking component of Oracle Financial Services Applications (subcomponent: Infrastructure). Supported versions that are affected are 11.3.0, 11.4.0 and 12.0.1. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Universal Banking. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Oracle FLEXCUBE Universal Banking. CVSS 3.0 Base Score 4.3 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2017-3480 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Universal Banking component of Oracle Financial Services Applications (subcomponent: Infrastructure). Supported versions that are affected are 11.3.0, 11.4.0 and 12.0.1. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle FLEXCUBE Universal Banking. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle FLEXCUBE Universal Banking, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle FLEXCUBE Universal Banking accessible data. CVSS 3.0 Base Score 4.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:N/A:N). |
| CVE-2017-3479 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Miscellaneous). Supported versions that are affected are 2.0.0, 2.0.1, 2.2.0.1 and 12.0.1. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Private Banking accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle FLEXCUBE Private Banking. CVSS 3.0 Base Score 5.4 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:L). |
| CVE-2017-3478 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Miscellaneous). Supported versions that are affected are 12.0.0 and 12.1.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Private Banking accessible data as well as unauthorized read access to a subset of Oracle FLEXCUBE Private Banking accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-3477 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Miscellaneous). Supported versions that are affected are 12.0.0 and 12.1.0. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Private Banking accessible data as well as unauthorized read access to a subset of Oracle FLEXCUBE Private Banking accessible data. CVSS 3.0 Base Score 4.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-3476 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Miscellaneous). Supported versions that are affected are 2.0.0, 2.0.1, 2.2.0.1 and 12.0.1. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle FLEXCUBE Private Banking accessible data as well as unauthorized update, insert or delete access to some of Oracle FLEXCUBE Private Banking accessible data. CVSS 3.0 Base Score 7.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:L/A:N). |
| CVE-2017-3475 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Miscellaneous). Supported versions that are affected are 2.0.0, 2.0.1, 2.2.0.1 and 12.0.1. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. While the vulnerability is in Oracle FLEXCUBE Private Banking, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Oracle FLEXCUBE Private Banking. CVSS 3.0 Base Score 5.0 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:N/I:N/A:L). |
| CVE-2017-3474 | Low | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Solaris component of Oracle Sun Systems Products Suite (subcomponent: Zone). The supported version that is affected is 11.3. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Solaris executes to compromise Solaris. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Solaris accessible data. CVSS 3.0 Base Score 3.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-3473 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Miscellaneous). Supported versions that are affected are 2.0.0, 2.0.1, 2.2.0.1 and 12.0.1. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle FLEXCUBE Private Banking accessible data. CVSS 3.0 Base Score 4.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-3472 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Portfolio Management). Supported versions that are affected are 2.0.0, 2.0.1, 2.2.0.1 and 12.0.1. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle FLEXCUBE Private Banking accessible data as well as unauthorized access to critical data or complete access to all Oracle FLEXCUBE Private Banking accessible data. CVSS 3.0 Base Score 8.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-3471 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Miscellaneous). Supported versions that are affected are 12.0.0 and 12.1.0. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle FLEXCUBE Private Banking, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Private Banking accessible data. CVSS 3.0 Base Score 4.7 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:N/I:L/A:N). |
| CVE-2017-3470 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Security Gateway component of Oracle Communications Applications (subcomponent: Network). The supported version that is affected is 3.0.0. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via ICMP Ping to compromise Oracle Communications Security Gateway. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Communications Security Gateway. CVSS 3.0 Base Score 5.3 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2017-3469 | Low | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Workbench component of Oracle MySQL (subcomponent: Workbench: Security : Encryption). Supported versions that are affected are 6.3.8 and earlier. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise MySQL Workbench. Successful attacks of this vulnerability can result in unauthorized read access to a subset of MySQL Workbench accessible data. CVSS 3.0 Base Score 3.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-3468 | Low | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: Security: Encryption). Supported versions that are affected are 5.7.17 and earlier. Difficult to exploit vulnerability allows low privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of MySQL Server accessible data. CVSS 3.0 Base Score 3.1 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:L/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2017-3467 | Low | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: C API). Supported versions that are affected are 5.7.17 and earlier. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized read access to a subset of MySQL Server accessible data. CVSS 3.0 Base Score 3.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-3465 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: Security: Privileges). Supported versions that are affected are 5.7.17 and earlier. Easily "exploitable" vulnerability allows low privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of MySQL Server accessible data. CVSS 3.0 Base Score 4.3 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2017-3464 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: DDL). Supported versions that are affected are 5.5.54 and earlier, 5.6.35 and earlier and 5.7.17 and earlier. Easily "exploitable" vulnerability allows low privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of MySQL Server accessible data. CVSS 3.0 Base Score 4.3 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2017-3463 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: Security: Privileges). Supported versions that are affected are 5.5.54 and earlier, 5.6.35 and earlier and 5.7.17 and earlier. Easily "exploitable" vulnerability allows high privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.0 Base Score 4.9 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3462 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: Security: Privileges). Supported versions that are affected are 5.5.54 and earlier, 5.6.35 and earlier and 5.7.17 and earlier. Easily "exploitable" vulnerability allows high privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.0 Base Score 4.9 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3461 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: Security: Privileges). Supported versions that are affected are 5.5.54 and earlier, 5.6.35 and earlier and 5.7.17 and earlier. Easily "exploitable" vulnerability allows high privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.0 Base Score 4.9 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3460 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: Audit Plug-in). Supported versions that are affected are 5.7.17 and earlier. Easily "exploitable" vulnerability allows high privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.0 Base Score 4.9 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3459 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: Optimizer). Supported versions that are affected are 5.7.17 and earlier. Easily "exploitable" vulnerability allows high privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.0 Base Score 4.9 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3458 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: DML). Supported versions that are affected are 5.7.17 and earlier. Easily "exploitable" vulnerability allows high privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.0 Base Score 4.9 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3457 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: DML). Supported versions that are affected are 5.7.17 and earlier. Easily "exploitable" vulnerability allows high privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.0 Base Score 4.9 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3456 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: DML). Supported versions that are affected are 5.5.54 and earlier, 5.6.35 and earlier and 5.7.17 and earlier. Easily "exploitable" vulnerability allows high privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.0 Base Score 4.9 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3455 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: Security: Privileges). Supported versions that are affected are 5.7.17 and earlier. Easily "exploitable" vulnerability allows low privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of MySQL Server accessible data as well as unauthorized read access to a subset of MySQL Server accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-3454 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: InnoDB). Supported versions that are affected are 5.7.17 and earlier. Easily "exploitable" vulnerability allows high privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server as well as unauthorized update, insert or delete access to some of MySQL Server accessible data. CVSS 3.0 Base Score 5.5 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:L/A:H). |
| CVE-2017-3453 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: Optimizer). Supported versions that are affected are 5.5.54 and earlier, 5.6.35 and earlier and 5.7.17 and earlier. Easily "exploitable" vulnerability allows low privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.0 Base Score 6.5 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3452 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: Optimizer). Supported versions that are affected are 5.6.35 and earlier. Easily "exploitable" vulnerability allows low privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.0 Base Score 6.5 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3451 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Retail Open Commerce Platform component of Oracle Retail Applications (subcomponent: Web). Supported versions that are affected are 4.0, 5.0, 5.1, 5.3, 6.0,6.1, 15.0 and 16.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Retail Open Commerce Platform. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Retail Open Commerce Platform, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Retail Open Commerce Platform accessible data as well as unauthorized read access to a subset of Oracle Retail Open Commerce Platform accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-3450 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: Memcached). Supported versions that are affected are 5.6.35 and earlier and 5.7.17 and earlier. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.0 Base Score 7.5 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3432 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle One-to-One Fulfillment component of Oracle E-Business Suite (subcomponent: Audience workbench). Supported versions that are affected are 12.1.1, 12.1.2 and 12.1.3. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle One-to-One Fulfillment. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle One-to-One Fulfillment, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle One-to-One Fulfillment accessible data as well as unauthorized update, insert or delete access to some of Oracle One-to-One Fulfillment accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-3393 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Advanced Outbound Telephony component of Oracle E-Business Suite (subcomponent: Interaction History). Supported versions that are affected are 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Advanced Outbound Telephony. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Advanced Outbound Telephony, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Advanced Outbound Telephony accessible data as well as unauthorized update, insert or delete access to some of Oracle Advanced Outbound Telephony accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-3337 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Marketing component of Oracle E-Business Suite (subcomponent: User Interface). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Marketing. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Marketing, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Marketing accessible data as well as unauthorized update, insert or delete access to some of Oracle Marketing accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-3331 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: DML). The supported version that is affected is 5.7.11 to 5.7.17. Easily "exploitable" vulnerability allows low privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.0 Base Score 6.5 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3329 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: Thread Pooling). Supported versions that are affected are 5.5.54 and earlier, 5.6.35 and earlier and 5.7.17 and earlier. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.0 Base Score 7.5 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3309 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: Optimizer). Supported versions that are affected are 5.5.54 and earlier, 5.6.35 and earlier and 5.7.17 and earlier. Easily "exploitable" vulnerability allows low privileged attacker with network access via multiple protocols to compromise MySQL Server. While the vulnerability is in MySQL Server, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.0 Base Score 7.7 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:N/I:N/A:H). |
| CVE-2017-3308 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: DML). Supported versions that are affected are 5.5.54 and earlier, 5.6.35 and earlier and 5.7.17 and earlier. Easily "exploitable" vulnerability allows low privileged attacker with network access via multiple protocols to compromise MySQL Server. While the vulnerability is in MySQL Server, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.0 Base Score 7.7 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:N/I:N/A:H). |
| CVE-2017-3307 | Low | 2017-04-24 | Outside Waratek scope | No public exploit | Vulnerability in the MySQL Enterprise Monitor component of Oracle MySQL (subcomponent: Monitoring: Server). Supported versions that are affected are 3.1.6.8003 and earlier, 3.2.1182 and earlier and 3.3.2.1162 and earlier. Difficult to exploit vulnerability allows high privileged attacker with network access via multiple protocols to compromise MySQL Enterprise Monitor. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of MySQL Enterprise Monitor accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of MySQL Enterprise Monitor. CVSS 3.0 Base Score 3.1 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:H/UI:R/S:U/C:N/I:L/A:L). |
| CVE-2017-3306 | High | 2017-04-24 | Outside Waratek scope | No public exploit | Vulnerability in the MySQL Enterprise Monitor component of Oracle MySQL (subcomponent: Monitoring: Server). Supported versions that are affected are 3.1.6.8003 and earlier, 3.2.1182 and earlier and 3.3.2.1162 and earlier. Easily "exploitable" vulnerability allows high privileged attacker with network access via multiple protocols to compromise MySQL Enterprise Monitor. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in MySQL Enterprise Monitor, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all MySQL Enterprise Monitor accessible data as well as unauthorized access to critical data or complete access to all MySQL Enterprise Monitor accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of MySQL Enterprise Monitor. CVSS 3.0 Base Score 8.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:C/C:H/I:H/A:L). |
| CVE-2017-3305 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: C API). Supported versions that are affected are 5.5.55 and earlier and 5.6.35 and earlier. Difficult to exploit vulnerability allows low privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all MySQL Server accessible data. CVSS 3.0 Base Score 5.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:L/UI:N/S:U/C:H/I:N/A:N). NOTE: the previous information is from the April 2017 CPU. Oracle has not commented on third-party claims that this issue allows man-in-the-middle attackers to hijack the authentication of users by leveraging incorrect ordering of security parameter verification in a client, aka, "The Riddle". |
| CVE-2017-3304 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Cluster component of Oracle MySQL (subcomponent: Cluster: DD). Supported versions that are affected are 7.2.27 and earlier, 7.3.16 and earlier, 7.4.14 and earlier and 7.5.5 and earlier. Easily "exploitable" vulnerability allows low privileged attacker with network access via multiple protocols to compromise MySQL Cluster. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of MySQL Cluster accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of MySQL Cluster. CVSS 3.0 Base Score 5.4 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:L). |
| CVE-2017-3288 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Investor Servicing component of Oracle Financial Services Applications (subcomponent: Unit Trust). Supported versions that are affected are 12.0.1, 12.0.2, 12.0.3, 12.0.4, 12.1.0, 12.2.0 and 12.3.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Investor Servicing. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Investor Servicing accessible data as well as unauthorized read access to a subset of Oracle FLEXCUBE Investor Servicing accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-3254 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Retail Invoice Matching component of Oracle Retail Applications (subcomponent: Security). Supported versions that are affected are 12.0 and 13.0. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Retail Invoice Matching. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Retail Invoice Matching accessible data as well as unauthorized update, insert or delete access to some of Oracle Retail Invoice Matching accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Retail Invoice Matching. CVSS 3.0 Base Score 7.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:L/A:L). |
| CVE-2017-3237 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Automatic Service Request (ASR) component of Oracle Support Tools (subcomponent: ASR Manager). The supported version that is affected is Prior to 5.7. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Automatic Service Request (ASR) executes to compromise Automatic Service Request (ASR). Successful attacks of this vulnerability can result in takeover of Automatic Service Request (ASR). CVSS 3.0 Base Score 7.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2017-3234 | Critical | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Automatic Service Request (ASR) component of Oracle Support Tools (subcomponent: ASR Manager). The supported version that is affected is Prior to 5.7. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via SFT to compromise Automatic Service Request (ASR). Successful attacks of this vulnerability can result in takeover of Automatic Service Request (ASR). CVSS 3.0 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2017-3233 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Automatic Service Request (ASR) component of Oracle Support Tools (subcomponent: ASR Manager). The supported version that is affected is Prior to 5.7. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Automatic Service Request (ASR). Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Automatic Service Request (ASR) accessible data. CVSS 3.0 Base Score 7.5 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:H/A:N). |
| CVE-2017-3232 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Automatic Service Request (ASR) component of Oracle Support Tools (subcomponent: ASR Manager). The supported version that is affected is Prior to 5.7. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Automatic Service Request (ASR) executes to compromise Automatic Service Request (ASR). Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Automatic Service Request (ASR) accessible data. CVSS 3.0 Base Score 5.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-3230 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Fusion Middleware MapViewer component of Oracle Fusion Middleware (subcomponent: Map Builder). Supported versions that are affected are 11.1.1.9, 12.2.1.1 and 12.2.1.2. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Fusion Middleware MapViewer. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Fusion Middleware MapViewer accessible data as well as unauthorized read access to a subset of Oracle Fusion Middleware MapViewer accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Fusion Middleware MapViewer. CVSS 3.0 Base Score 8.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:H/A:L). |
| CVE-2016-5551 | Low | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Solaris Cluster component of Oracle Sun Systems Products Suite (subcomponent: NAS device addition). The supported version that is affected is 4.3. Easily "exploitable" vulnerability allows unauthenticated attacker with logon to the infrastructure where Solaris Cluster executes to compromise Solaris Cluster. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Solaris Cluster accessible data. CVSS 3.0 Base Score 3.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:N/UI:R/S:U/C:L/I:N/A:N). |
| CVE-2017-5638 | Critical | 2017-03-11 | Protected by Waratek | Exploited | The Jakarta Multipart parser in Apache Struts 2 2.3.x before 2.3.32 and 2.5.x before 2.5.10.1 has incorrect exception handling and error-message generation during file-upload attempts, which allows remote attackers to execute arbitrary commands via a crafted Content-Type, Content-Disposition, or Content-Length HTTP header, as exploited in the wild in March 2017 with a Content-Type header containing a #cmd= string. |
| CVE-2017-3302 | High | 2017-02-12 | Not applicable | No public exploit | Crash in libmysqlclient.so in Oracle MySQL before 5.6.21 and 5.7.x before 5.7.5 and MariaDB through 5.5.54, 10.0.x through 10.0.29, 10.1.x through 10.1.21, and 10.2.x through 10.2.3. |
| CVE-2016-5407 | Critical | 2016-12-13 | Not applicable | No public exploit | The (1) XvQueryAdaptors and (2) XvQueryEncodings functions in X.org libXv before 1.0.11 allow remote X servers to trigger out-of-bounds memory access operations via vectors involving length specifications in received data. |
| CVE-2016-5019 | Critical | 2016-10-03 | Protected by Waratek | No public exploit | CoreResponseStateManager in Apache MyFaces Trinidad 1.0.0 through 1.0.13, 1.2.x before 1.2.15, 2.0.x before 2.0.2, and 2.1.x before 2.1.2 might allow attackers to conduct deserialization attacks via a crafted serialized view state string. |
| CVE-2016-6304 | High | 2016-09-26 | Not applicable | Forecast only | Multiple memory leaks in t1_lib.c in OpenSSL before 1.0.1u, 1.0.2 before 1.0.2i, and 1.1.0 before 1.1.0a allow remote attackers to cause a denial of service (memory consumption) via large OCSP Status Request extensions. |