
Oracle Critical Patch Update July 2016
Released July 2016 · Oracle's advisory ↗ · ← Critical Patch Update, April 2016 · Critical Patch Update, October 2016 →
222 CVEs in this release, one square each
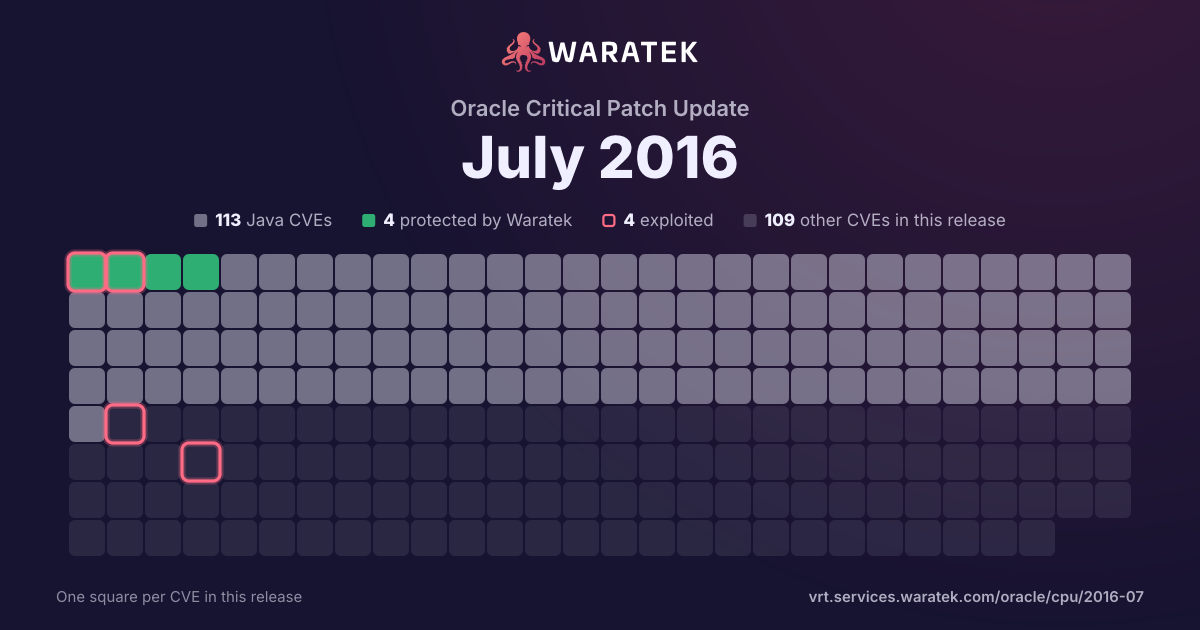
By status
4Protected by Waratek1Mitigation candidate108No exploit published30Outside Waratek scope79Not applicable
4Exploited, marked by the ring
No exploit published. For 108 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 222 matches · 113 in Waratek scope · 4 protected · 4 exploited · 1 CISA KEV · 12 public PoC · 14 EPSS ≥ 0.5
222matches
113in Waratek scope50.9%
4protected1.8%
4exploited1.8%
1CISA KEV0.5%
12public PoC5.4%
14EPSS ≥ 0.56.3%
Protected by Waratek
4
1.8%
Rule in development
0
0.0%
Mitigation candidate
1
0.5%
No exploit published
108
48.6%
Outside Waratek scope
30
13.5%
Not applicable
79
35.6%
Withdrawn CVE
0
0.0%
blocked by ARMR today
4
1.8%
partly blocked
0
0.0%
not blocked
218
98.2%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 193 / quarter
Q3 122
Outside Waratek scope1
Not applicable1
Medium2
not blocked2
Working exploit published1
No public exploit1
Q4 120
Q1 131
Outside Waratek scope1
Medium1
not blocked1
Forecast only1
Q2 131
Not applicable1
Medium1
not blocked1
No public exploit1
Q3 130
Q4 130
Q1 140
Q2 141
Outside Waratek scope1
High1
not blocked1
Exploited1
Q3 140
Q4 141
Outside Waratek scope1
Low1
not blocked1
Proof of concept only1
Q1 155
Outside Waratek scope2
Not applicable3
High1
Medium4
not blocked5
Exploited1
Working exploit published1
Forecast only1
No public exploit2
Q2 153
Outside Waratek scope1
Not applicable2
Medium2
Low1
not blocked3
Forecast only1
No public exploit2
Q3 154
Outside Waratek scope2
Not applicable2
Critical1
High1
Medium2
not blocked4
Working exploit published1
Forecast only1
No public exploit2
Q4 152
Outside Waratek scope1
Not applicable1
Critical2
not blocked2
No public exploit2
Q1 163
Outside Waratek scope1
Not applicable2
Medium3
not blocked3
Proof of concept only1
No public exploit2
Q2 163
Protected by Waratek1
Not applicable2
High2
Medium1
blocked by ARMR today1
not blocked2
Exploited1
Working exploit published1
No public exploit1
Q3 16193
Protected by Waratek2
Mitigation candidate1
No exploit published108
Outside Waratek scope19
Not applicable63
Critical20
High62
Medium96
Low15
blocked by ARMR today2
not blocked191
Working exploit published2
No public exploit191
Q4 160
Q1 171
Not applicable1
High1
not blocked1
No public exploit1
Q2 170
Q3 171
Not applicable1
High1
not blocked1
No public exploit1
Q4 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q4 12Q2 13Q4 13Q2 14Q4 14Q2 15Q4 15Q2 16Q4 16Q2 17Q4 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-3550 | Medium | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u115, 7u101, and 8u92 and Java SE Embedded 8u91 allows remote attackers to affect confidentiality via vectors related to Hotspot. |
| CVE-2016-3549 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle E-Business Suite Secure Enterprise Search component in Oracle E-Business Suite 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect confidentiality via vectors related to Search Integration Engine. |
| CVE-2016-3548 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Marketing component in Oracle E-Business Suite 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect confidentiality via vectors related to Marketing activity collateral. |
| CVE-2016-3547 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle One-to-One Fulfillment component in Oracle E-Business Suite 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect confidentiality via vectors related to Content Manager. |
| CVE-2016-3546 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Advanced Collections component in Oracle E-Business Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Report JSPs. |
| CVE-2016-3545 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect confidentiality via vectors related to Web based help screens. |
| CVE-2016-3544 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Business Intelligence Enterprise Edition component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, and 11.2.1.0.0 allows remote authenticated users to affect confidentiality and integrity via vectors related to Analytics Web General. |
| CVE-2016-3543 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Common Applications Calendar component in Oracle E-Business Suite 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect confidentiality and integrity via vectors related to Tasks. |
| CVE-2016-3542 | Medium | 2016-07-21 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle Knowledge Management component in Oracle E-Business Suite 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote administrators to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-3541 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Common Applications Calendar component in Oracle E-Business Suite 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect confidentiality and integrity via vectors related to Notes. |
| CVE-2016-3540 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Base Platform component in Oracle Enterprise Manager Grid Control 12.1.0.5 and 13.1.0.0 allows remote attackers to affect confidentiality via vectors related to UI Framework. |
| CVE-2016-3539 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect integrity and availability via vectors related to File Folders / Attachment, a different vulnerability than CVE-2016-3538. |
| CVE-2016-3538 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect integrity and availability via vectors related to File Folders / Attachment, a different vulnerability than CVE-2016-3539. |
| CVE-2016-3537 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect confidentiality via vectors related to File Folders / Attachment, a different vulnerability than CVE-2016-5473. |
| CVE-2016-3536 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Marketing component in Oracle E-Business Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Deliverables. NOTE: the previous information is from the July 2016 CPU. Oracle has not commented on third-party claims that this issue involves multiple cross-site scripting (XSS) vulnerabilities, which allow remote attackers to inject arbitrary web script or HTML via unspecified vectors. |
| CVE-2016-3535 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle CRM Technical Foundation component in Oracle E-Business Suite 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Remote Launch. NOTE: the previous information is from the July 2016 CPU. Oracle has not commented on third-party claims that this issue is a cross-site scripting (XSS) vulnerability, which allows remote attackers to inject arbitrary web script or HTML via unspecified vectors. |
| CVE-2016-3534 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Installed Base component in Oracle E-Business Suite 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect integrity via vectors related to Engineering Change Order. NOTE: the previous information is from the July 2016 CPU. Oracle has not commented on third-party claims that this issue involves an open redirect vulnerability, which allows remote attackers to redirect users to arbitrary web sites and conduct phishing attacks via unspecified vectors. |
| CVE-2016-3533 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Knowledge Management component in Oracle E-Business Suite 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect integrity via vectors related to Search. NOTE: the previous information is from the July 2016 CPU. Oracle has not commented on third-party claims that this issue involves multiple open redirect vulnerabilities, which allow remote attackers to redirect users to arbitrary web sites and conduct phishing attacks via unspecified vectors. |
| CVE-2016-3532 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Advanced Inbound Telephony component in Oracle E-Business Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to SDK client integration. NOTE: the previous information is from the July 2016 CPU. Oracle has not commented on third-party claims that this issue involves multiple cross-site scripting (XSS) vulnerabilities, which allow remote attackers to inject arbitrary web script or HTML via unspecified vectors. |
| CVE-2016-3531 | Low | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect confidentiality via vectors related to PC / Notification. |
| CVE-2016-3530 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect integrity and availability via vectors related to PGC / Import. |
| CVE-2016-3529 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality via vectors related to SDK, a different vulnerability than CVE-2016-3526 and CVE-2016-3560. |
| CVE-2016-3528 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Internet Expenses component in Oracle E-Business Suite 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect availability via vectors related to Expenses Admin Utilities. |
| CVE-2016-3527 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Demand Planning component in Oracle Supply Chain Products Suite 12.1 and 12.2 allows remote attackers to affect confidentiality and integrity via vectors related to ODPDA Servlet. |
| CVE-2016-3526 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality via vectors related to SDK, a different vulnerability than CVE-2016-3529 and CVE-2016-3560. |
| CVE-2016-3525 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Manager component in Oracle E-Business Suite 12.1.3 allows remote attackers to affect confidentiality via vectors related to Cookie Management. |
| CVE-2016-3524 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Technology Stack component in Oracle E-Business Suite 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect confidentiality and integrity via vectors related to Configuration. |
| CVE-2016-3523 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Web Applications Desktop Integrator component in Oracle E-Business Suite 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect integrity via vectors related to Application Service. |
| CVE-2016-3522 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Web Applications Desktop Integrator component in Oracle E-Business Suite 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect confidentiality and integrity via vectors related to Application Service. |
| CVE-2016-3521 | Medium | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.49 and earlier, 5.6.30 and earlier, and 5.7.12 and earlier and MariaDB before 5.5.50, 10.0.x before 10.0.26, and 10.1.x before 10.1.15 allows remote authenticated users to affect availability via vectors related to Server: Types. |
| CVE-2016-3520 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote administrators to affect confidentiality via vectors related to AOL Diagnostic tests. |
| CVE-2016-3519 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality and integrity via vectors related to PC / Get Shortcut. |
| CVE-2016-3518 | Medium | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.12 and earlier allows remote authenticated users to affect availability via vectors related to Server: Optimizer. |
| CVE-2016-3517 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect integrity via vectors related to PC / Get Shortcut. |
| CVE-2016-3516 | Low | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Enterprise Communications Broker component in Oracle Communications Applications before PCz 2.0.0m4p1 allows remote authenticated users to affect confidentiality via vectors related to GUI, a different vulnerability than CVE-2016-3514. |
| CVE-2016-3515 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Enterprise Communications Broker component in Oracle Communications Applications before PCz 2.0.0m4p1 allows remote attackers to affect confidentiality via unknown vectors. |
| CVE-2016-3514 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Enterprise Communications Broker component in Oracle Communications Applications before PCz 2.0.0m4p1 allows remote authenticated users to affect confidentiality via vectors related to GUI, a different vulnerability than CVE-2016-3516. |
| CVE-2016-3513 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Communications Operations Monitor component in Oracle Communications Applications before 3.3.92.0.0 allows remote authenticated users to affect confidentiality via vectors related to Infrastructure. |
| CVE-2016-3512 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Customer Interaction History component in Oracle E-Business Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Function Security. |
| CVE-2016-3511 | High | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u101 and 8u92 allows local users to affect confidentiality, integrity, and availability via vectors related to Deployment. |
| CVE-2016-3510 | Critical | 2016-07-21 | Protected by Waratek | Working exploit published | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.3.0, and 12.2.1.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to WLS Core Components, a different vulnerability than CVE-2016-3586. |
| CVE-2016-3509 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect confidentiality and integrity via vectors related to File Folders / URL Attachment. |
| CVE-2016-3508 | Medium | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u115, 7u101, and 8u92; Java SE Embedded 8u91; and JRockit R28.3.10 allows remote attackers to affect availability via vectors related to JAXP, a different vulnerability than CVE-2016-3500. |
| CVE-2016-3507 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect integrity via vectors related to WebClient / Admin. |
| CVE-2016-3506 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the JDBC component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2; the Oracle Retail Xstore Point of Service 5.5, 6.0, 6.5, 7.0, 7.1, 15.0, and 16.0; the Oracle Retail Warehouse Management System 14.04, 14.1.3, and 15.0.1; the Oracle Retail Workforce Management 1.60.7, and 1.64.0; the Oracle Retail Clearance Optimization Engine 13.4; the Oracle Retail Markdown Optimization 13.4 and 14.0; and Oracle Retail Merchandising System 16.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-3504 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle JDeveloper component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, 11.1.2.4.0, 12.1.3.0.0, and 12.2.1.0.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to ADF Faces. |
| CVE-2016-3503 | High | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u115, 7u101, and 8u92 allows local users to affect confidentiality, integrity, and availability via vectors related to Install. |
| CVE-2016-3502 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Sites component in Oracle Fusion Middleware 11.1.1.8 and 12.2.1.0 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-3501 | Medium | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.30 and earlier and 5.7.12 and earlier allows remote authenticated users to affect availability via vectors related to Server: Optimizer. |
| CVE-2016-3500 | Medium | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u115, 7u101, and 8u92; Java SE Embedded 8u91; and JRockit R28.3.10 allows remote attackers to affect availability via vectors related to JAXP, a different vulnerability than CVE-2016-3508. |
| CVE-2016-3499 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 12.1.3.0 and 12.2.1.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Web Container. |
| CVE-2016-3498 | Medium | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u101 and 8u92 allows remote attackers to affect availability via vectors related to JavaFX. |
| CVE-2016-3497 | Medium | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows local users to affect availability via vectors related to Kernel, a different vulnerability than CVE-2016-5469 and CVE-2016-5471. |
| CVE-2016-3496 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager for Fusion Middleware component in Oracle Enterprise Manager Grid Control 11.1.1.7, and 11.1.1.9 allows remote attackers to affect confidentiality via vectors related to SOA Topology Viewer. |
| CVE-2016-3494 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Ops Center component in Oracle Enterprise Manager Grid Control 12.1.4, 12.2.2, and 12.3.2 allows remote attackers to affect availability via vectors related to OS Provisioning. |
| CVE-2016-3493 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Financial Reporting component in Oracle Hyperion 11.1.2.4 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Security Models. |
| CVE-2016-3491 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle CRM Technical Foundation component in Oracle E-Business Suite 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Wireless Framework. NOTE: the previous information is from the July 2016 CPU. Oracle has not commented on third-party claims that this issue is a cross-site scripting (XSS) vulnerability, which allows remote attackers to inject arbitrary web script or HTML via unspecified vectors. |
| CVE-2016-3490 | Low | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Transportation Management component in Oracle Supply Chain Products Suite 6.3.0, 6.3.1, 6.3.2, 6.3.3, 6.3.4, 6.3.5, 6.3.6, 6.3.7, 6.4.0, and 6.4.1 allows remote authenticated users to affect confidentiality via vectors related to Database. |
| CVE-2016-3489 | Medium | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Data Pump Import component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows local users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-3488 | Medium | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the DB Sharding component in Oracle Database Server 12.1.0.2 allows local users to affect integrity via unknown vectors. |
| CVE-2016-3487 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Sites component in Oracle Fusion Middleware 11.1.1.8, and 12.2.1.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-3486 | Medium | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.30 and earlier and 5.7.12 and earlier allows remote authenticated users to affect availability via vectors related to Server: FTS. |
| CVE-2016-3485 | Low | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u115, 7u101, and 8u92; Java SE Embedded 8u91; and JRockit R28.3.10 allows local users to affect integrity via vectors related to Networking. |
| CVE-2016-3484 | Low | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Database Vault component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows local users to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-3483 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53, 8.54, and 8.55 allows remote attackers to affect confidentiality and availability via vectors related to File Processing. |
| CVE-2016-3482 | Low | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle HTTP Server component in Oracle Fusion Middleware 11.1.1.9 and 12.1.3.0 allows remote attackers to affect confidentiality via vectors related to SSL/TLS Module. |
| CVE-2016-3481 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the ILOM component in Oracle Sun Systems Products Suite 3.0, 3.1, and 3.2 allows remote authenticated users to affect availability via vectors related to Web. |
| CVE-2016-3480 | Medium | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris Cluster component in Oracle Sun Systems Products Suite 3.3 and 4.3 allows local users to affect confidentiality via vectors related to HA for Postgresql. |
| CVE-2016-3479 | High | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Portable Clusterware component in Oracle Database Server 11.2.0.4 and 12.1.0.2 allows remote attackers to affect availability via unknown vectors. |
| CVE-2016-3478 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53, 8.54, and 8.55 allows remote attackers to affect confidentiality and integrity via vectors related to File Processing. |
| CVE-2016-3477 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.49 and earlier, 5.6.30 and earlier, and 5.7.12 and earlier and MariaDB before 5.5.50, 10.0.x before 10.0.26, and 10.1.x before 10.1.15 allows local users to affect confidentiality, integrity, and availability via vectors related to Server: Parser. |
| CVE-2016-3476 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Knowledge component in Oracle Siebel CRM 8.5.x allows remote attackers to affect confidentiality and integrity via vectors related to Information Manager Console. |
| CVE-2016-3475 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Knowledge component in Oracle Siebel CRM 8.5.x allows remote authenticated users to affect confidentiality via vectors related to Information Manager Console. |
| CVE-2016-3474 | Low | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the BI Publisher (formerly XML Publisher) component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, and 12.2.1.0.0 allows remote attackers to affect confidentiality via vectors related to Security. |
| CVE-2016-3472 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Engineering - Installer and Deployment component in Oracle Siebel CRM 8.1.1, 8.2.2, IP2014, IP2015, and IP2016 allows remote authenticated users to affect confidentiality via vectors related to Web Server. |
| CVE-2016-3471 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.45 and earlier and 5.6.26 and earlier allows local users to affect confidentiality, integrity, and availability via vectors related to Server: Option. |
| CVE-2016-3470 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Transportation Management component in Oracle Supply Chain Products Suite 6.4.1 allows remote authenticated users to affect confidentiality and integrity via vectors related to Install. |
| CVE-2016-3469 | Low | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Core - Server Framework component in Oracle Siebel CRM 8.1.1, 8.2.2, IP2014, IP2015, and IP2016 allows local users to affect confidentiality via vectors related to Services. |
| CVE-2016-3468 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile Engineering Data Management component in Oracle Supply Chain Products Suite 6.1.3.0 and 6.2.0.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Install. |
| CVE-2016-3467 | Medium | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Application Express component in Oracle Database Server before 5.0.4 allows remote attackers to affect availability via unknown vectors. |
| CVE-2016-3459 | Medium | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.30 and earlier and 5.7.12 and earlier and MariaDB 10.0.x before 10.0.25 and 10.1.x before 10.1.14 allows remote administrators to affect availability via vectors related to Server: InnoDB. |
| CVE-2016-3458 | Medium | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u115, 7u101, and 8u92; and Java SE Embedded 8u91 allows remote attackers to affect integrity via vectors related to CORBA. |
| CVE-2016-3453 | Medium | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 allows local users to affect availability via vectors related to Kernel. |
| CVE-2016-3452 | Low | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.48 and earlier, 5.6.29 and earlier, and 5.7.10 and earlier and MariaDB before 5.5.49, 10.0.x before 10.0.25, and 10.1.x before 10.1.14 allows remote attackers to affect confidentiality via vectors related to Server: Security: Encryption. |
| CVE-2016-3451 | Medium | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the ILOM component in Oracle Sun Systems Products Suite 3.0, 3.1, and 3.2 allows remote attackers to affect integrity via vectors related to Web. |
| CVE-2016-3450 | Low | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Core - Server Framework component in Oracle Siebel CRM 8.1.1, 8.2.2, IP2014, IP2015, and IP2016 allows remote attackers to affect confidentiality via vectors related to Services, a different vulnerability than CVE-2016-5460 and CVE-2016-5466. |
| CVE-2016-3448 | Medium | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Application Express component in Oracle Database Server before 5.0.4 allows remote attackers to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-3446 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Business Intelligence Enterprise Edition component in Oracle Fusion Middleware 11.1.1.7.0 and 11.1.1.9.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Analytics Web Administration. |
| CVE-2016-3445 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0 and 12.1.3.0 allows remote attackers to affect availability via vectors related to Web Container, a different vulnerability than CVE-2016-5488. |
| CVE-2016-3444 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Integration Bus component in Oracle Retail Applications 13.0, 13.1, 13.2, 14.0, 14.1, and 15.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Install. |
| CVE-2016-3440 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.11 and earlier allows remote authenticated users to affect availability via vectors related to Server: Optimizer. |
| CVE-2016-3433 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Business Intelligence Enterprise Edition component in Oracle Fusion Middleware 11.1.1.7.0 and 11.1.1.9.0 allows remote authenticated users to affect confidentiality and integrity via vectors related to Analytics Web Administration. |
| CVE-2016-3432 | Medium | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the BI Publisher (formerly XML Publisher) component in Oracle Fusion Middleware 11.1.1.7.0 and 11.1.1.9.0 allows remote authenticated users to affect confidentiality and integrity via vectors related to Web Server. |
| CVE-2016-3424 | Medium | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.12 and earlier allows remote administrators to affect availability via vectors related to Server: Optimizer. |
| CVE-2016-0635 | High | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Enterprise Manager Ops Center component in Oracle Enterprise Manager Grid Control 12.1.4, 12.2.2, and 12.3.2; the Oracle Health Sciences Information Manager component in Oracle Health Sciences Applications 1.2.8.3, 2.0.2.3, and 3.0.1.0; the Oracle Healthcare Master Person Index component in Oracle Health Sciences Applications 2.0.12, 3.0.0, and 4.0.1; the Oracle Documaker component in Oracle Insurance Applications before 12.5; the Oracle Insurance Calculation Engine component in Oracle Insurance Applications 9.7.1, 10.1.2, and 10.2.2; the Oracle Insurance Policy Administration J2EE and Oracle Insurance Rules Palette components in Oracle Insurance Applications 9.6.1, 9.7.1, 10.0.1, 10.1.2, 10.2.0, and 10.2.2; the Oracle Retail Integration Bus component in Oracle Retail Applications 15.0; the Oracle Retail Order Broker component in Oracle Retail Applications 5.1, 5.2, and 15.0; the Primavera Contract Management component in Oracle Primavera Products Suite 14.2; the Primavera P6 Enterprise Project Portfolio Management component in Oracle Primavera Products Suite 8.2, 8.3, 8.4, 15.1, 15.2, and 16.1; the Oracle Financial Services Analytical Applications Infrastructure component in Oracle Financial Services Applications 8.0.0, 8.0.1, 8.0.2, and 8.0.3; the Oracle Commerce Guided Search / Oracle Commerce Experience Manager component in Oracle Commerce 3.1.1, 3.1.2, 11.0, 11.1, and 11.2; the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5; the Oracle Communications BRM - Elastic Charging Engine 11.2.0.0.0 and 11.3.0.0.0; the Oracle Enterprise Repository Enterprise Repository 12.1.3.0.0; the Oracle Financial Services Behavior Detection Platform 8.0.1 and 8.0.2; the Oracle Hyperion Essbase 12.2.1.1; the Oracle Tuxedo System and Applications Monitor (TSAM) 11.1.1.2.0, 11.1.1.2.1, 11.1.1.2.1, 12.1.1.1.0, 12.1.3.0.0, and 12.2.2.0.0; the Oracle Communications WebRTC Session Controller component of Oracle Communications Applications (subcomponent: Security (Spring)) 7.0, 7.1 and 7.2; the Oracle Endeca Information Discovery Integrator 3.2; the Converged Commerce component of Oracle Retail Applications 16.0.1; the Oracle Identity Manager 11.1.2.3.0; Oracle Enterprise Manager for MySQL Database 12.1.0.4; Oracle Retail Invoice Matching 12.0, 13.0, 13.1, 13.2, 14.0, and 14.1; Oracle Communications Performance Intelligence Center (PIC) Software Prior to 10.2.1 and the Oracle Knowledge component of Oracle Siebel CRM (subcomponent: AnswerFlow (Spring Framework)) version 8.5.1.0 - 8.5.1.7 and 8.6.0 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-1181 | High | 2016-07-04 | Protected by Waratek | No public exploit | ActionServlet.java in Apache Struts 1 1.x through 1.3.10 mishandles multithreaded access to an ActionForm instance, which allows remote attackers to execute arbitrary code or cause a denial of service (unexpected memory access) via a multipart request, a related issue to CVE-2015-0899. |
| CVE-2016-2107 | Medium | 2016-05-05 | Not applicable | Working exploit published | The AES-NI implementation in OpenSSL before 1.0.1t and 1.0.2 before 1.0.2h does not consider memory allocation during a certain padding check, which allows remote attackers to obtain sensitive cleartext information via a padding-oracle attack against an AES CBC session. NOTE: this vulnerability exists because of an incorrect fix for CVE-2013-0169. |
| CVE-2016-2105 | High | 2016-05-05 | Not applicable | No public exploit | Integer overflow in the EVP_EncodeUpdate function in crypto/evp/encode.c in OpenSSL before 1.0.1t and 1.0.2 before 1.0.2h allows remote attackers to cause a denial of service (heap memory corruption) via a large amount of binary data. |
| CVE-2016-3081 | High | 2016-04-26 | Protected by Waratek | Exploited | Apache Struts 2.3.19 to 2.3.20.2, 2.3.21 to 2.3.24.1, and 2.3.25 to 2.3.28, when Dynamic Method Invocation is enabled, allow remote attackers to execute arbitrary code via method: prefix, related to chained expressions. |
| CVE-2016-0702 | Medium | 2016-03-03 | Not applicable | No public exploit | The MOD_EXP_CTIME_COPY_FROM_PREBUF function in crypto/bn/bn_exp.c in OpenSSL 1.0.1 before 1.0.1s and 1.0.2 before 1.0.2g does not properly consider cache-bank access times during modular exponentiation, which makes it easier for local users to discover RSA keys by running a crafted application on the same Intel Sandy Bridge CPU core as a victim and leveraging cache-bank conflicts, aka a "CacheBleed" attack. |