
Oracle Critical Patch Update July 2025
Released July 2025 · Oracle's advisory ↗ · ← Critical Patch Update, April 2025 · Critical Patch Update, October 2025 →
196 CVEs in this release, one square each
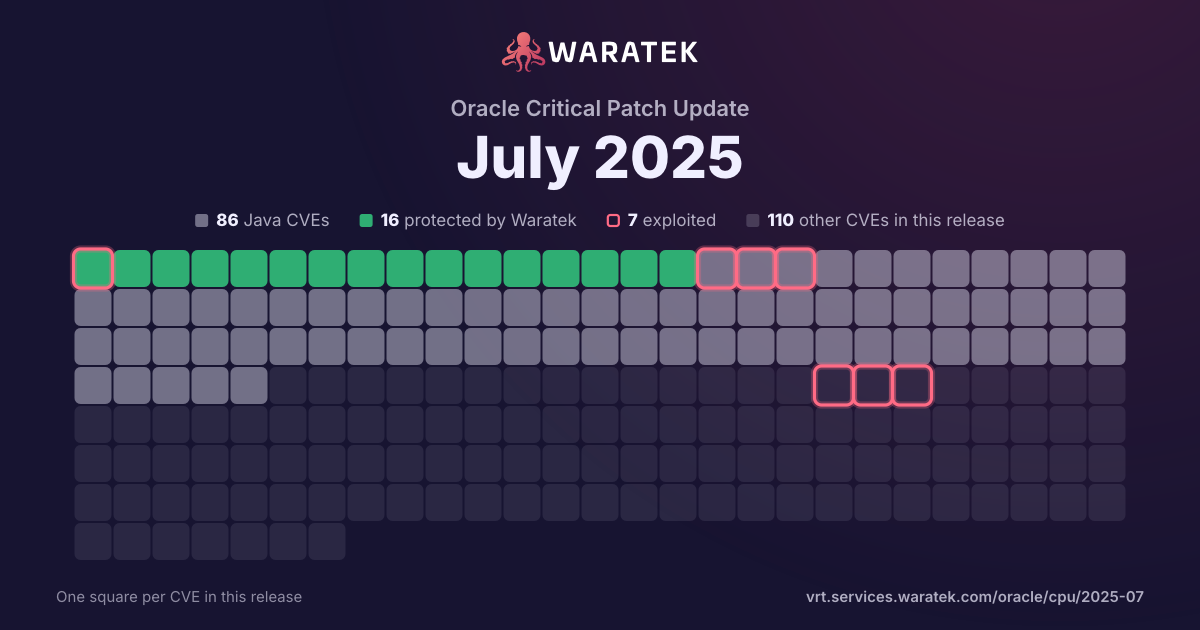
By status
16Protected by Waratek4Mitigation candidate66No exploit published14Outside Waratek scope96Not applicable
7Exploited, marked by the ring
No exploit published. For 31 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 6 matches · 0 in Waratek scope · 0 protected · 1 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
6matches
0in Waratek scope0.0%
0protected0.0%
1exploited16.7%
0CISA KEV0.0%
1public PoC16.7%
1EPSS ≥ 0.516.7%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
3
50.0%
Not applicable
3
50.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
6
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
16.7%
Working exploit published
0
0.0%
Proof of concept only
1
16.7%
Forecast only
0
0.0%
No public exploit
4
66.7%
split by
peak 1 / month
Dec 241
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
Jan 251
Not applicable1
Critical1
not blocked1
Proof of concept only1
Feb 251
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
Mar 251
Not applicable1
Critical1
not blocked1
Exploited1
Apr 251
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
May 250
Jun 250
Jul 251
Not applicable1
Critical1
not blocked1
No public exploit1
Dec 24Jan 25Feb 25Mar 25Apr 25May 25Jun 25Jul 25
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2025-50067 | Critical | 2025-07-15 | Not applicable | No public exploit | Vulnerability in Oracle Application Express (component: Strategic Planner Starter App). Supported versions that are affected are 24.2.4 and 24.2.5. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Application Express. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Application Express, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in takeover of Oracle Application Express. CVSS 3.1 Base Score 9.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:H/I:H/A:H). |
| CVE-2025-31651 | Critical | 2025-04-28 | Outside Waratek scope | No public exploit | Improper Neutralization of Escape, Meta, or Control Sequences vulnerability in Apache Tomcat. For a subset of unlikely rewrite rule configurations, it was possible for a specially crafted request to bypass some rewrite rules. If those rewrite rules effectively enforced security constraints, those constraints could be bypassed. This issue affects Apache Tomcat: from 11.0.0-M1 through 11.0.5, from 10.1.0-M1 through 10.1.39, from 9.0.0.M1 through 9.0.102. The following versions were EOL at the time the CVE was created but are known to be affected: 8.5.0 though 8.5.100. Other, older, EOL versions may also be affected. Users are recommended to upgrade to version [FIXED_VERSION], which fixes the issue. |
| CVE-2025-1974 | Critical | 2025-03-25 | Not applicable | Exploited | A security issue was discovered in Kubernetes where under certain conditions, an unauthenticated attacker with access to the pod network can achieve arbitrary code execution in the context of the ingress-nginx controller. This can lead to disclosure of Secrets accessible to the controller. (Note that in the default installation, the controller can access all Secrets cluster-wide.) |
| CVE-2024-56171 | Critical | 2025-02-18 | Outside Waratek scope | No public exploit | libxml2 before 2.12.10 and 2.13.x before 2.13.6 has a use-after-free in xmlSchemaIDCFillNodeTables and xmlSchemaBubbleIDCNodeTables in xmlschemas.c. To exploit this, a crafted XML document must be validated against an XML schema with certain identity constraints, or a crafted XML schema must be used. |
| CVE-2025-23016 | Critical | 2025-01-10 | Not applicable | Proof of concept only | FastCGI fcgi2 (aka fcgi) 2.x through 2.4.4 has an integer overflow (and resultant heap-based buffer overflow) via crafted nameLen or valueLen values in data to the IPC socket. This occurs in ReadParams in fcgiapp.c. |
| CVE-2024-40896 | Critical | 2024-12-23 | Outside Waratek scope | No public exploit | In libxml2 2.11 before 2.11.9, 2.12 before 2.12.9, and 2.13 before 2.13.3, the SAX parser can produce events for external entities even if custom SAX handlers try to override entity content (by setting "checked"). This makes classic XXE attacks possible. |