
Oracle Critical Patch Update April 2021
Released April 2021 · Oracle's advisory ↗ · ← Critical Patch Update, January 2021 · Critical Patch Update, July 2021 →
258 CVEs in this release, one square each
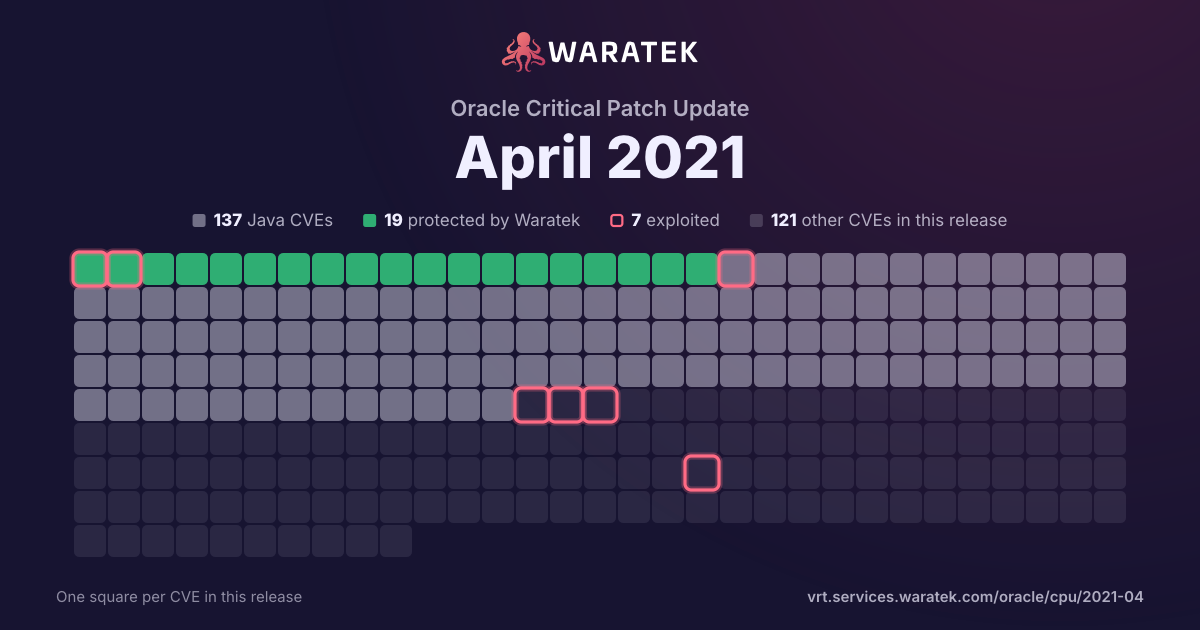
By status
19Protected by Waratek3Mitigation candidate115No exploit published67Outside Waratek scope54Not applicable
7Exploited, marked by the ring
No exploit published. For 97 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 8 matches · 3 in Waratek scope · 1 protected · 0 exploited · 0 CISA KEV · 5 public PoC
Protected by Waratek
1
12.5%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
2
25.0%
Outside Waratek scope
3
37.5%
Not applicable
2
25.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
12.5%
partly blocked
0
0.0%
not blocked
7
87.5%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
2
25.0%
Proof of concept only
3
37.5%
Forecast only
3
37.5%
No public exploit
0
0.0%
split by
peak 2 / quarter
Q2 191
Outside Waratek scope1
High1
not blocked1
Working exploit published1
Q3 190
Q4 190
Q1 201
Outside Waratek scope1
High1
not blocked1
Proof of concept only1
Q2 201
Outside Waratek scope1
High1
not blocked1
Proof of concept only1
Q3 200
Q4 202
Protected by Waratek1
Not applicable1
High2
blocked by ARMR today1
not blocked1
Working exploit published1
Proof of concept only1
Q1 211
Not applicable1
High1
not blocked1
Forecast only1
Q2 212
No exploit published2
High2
not blocked2
Forecast only2
Q2 19Q3 19Q4 19Q1 20Q2 20Q3 20Q4 20Q1 21Q2 21
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2021-2198 | High | 2021-04-22 | No exploit published | Forecast only | Vulnerability in the Oracle Knowledge Management product of Oracle E-Business Suite (component: Setup, Admin). Supported versions that are affected are 12.1.1-12.1.3 and 12.2.3-12.2.10. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Knowledge Management. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Knowledge Management, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Knowledge Management accessible data as well as unauthorized update, insert or delete access to some of Oracle Knowledge Management accessible data. CVSS 3.1 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2021-2190 | High | 2021-04-22 | No exploit published | Forecast only | Vulnerability in the Oracle Sales Offline product of Oracle E-Business Suite (component: Template). Supported versions that are affected are 12.1.1-12.1.3 and 12.2.3-12.2.10. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Sales Offline. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Sales Offline. CVSS 3.1 Base Score 7.5 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2021-22883 | High | 2021-03-03 | Not applicable | Forecast only | Node.js before 10.24.0, 12.21.0, 14.16.0, and 15.10.0 is vulnerable to a denial of service attack when too many connection attempts with an 'unknownProtocol' are established. This leads to a leak of file descriptors. If a file descriptor limit is configured on the system, then the server is unable to accept new connections and prevent the process also from opening, e.g. a file. If no file descriptor limit is configured, then this lead to an excessive memory usage and cause the system to run out of memory. |
| CVE-2020-8277 | High | 2020-11-19 | Not applicable | Proof of concept only | A Node.js application that allows an attacker to trigger a DNS request for a host of their choice could trigger a Denial of Service in versions < 15.2.1, < 14.15.1, and < 12.19.1 by getting the application to resolve a DNS record with a larger number of responses. This is fixed in 15.2.1, 14.15.1, and 12.19.1. |
| CVE-2020-26217 | High | 2020-11-16 | Protected by Waratek | Working exploit published | XStream before version 1.4.14 is vulnerable to Remote Code Execution.The vulnerability may allow a remote attacker to run arbitrary shell commands only by manipulating the processed input stream. Only users who rely on blocklists are affected. Anyone using XStream's Security Framework allowlist is not affected. The linked advisory provides code workarounds for users who cannot upgrade. The issue is fixed in version 1.4.14. |
| CVE-2020-1967 | High | 2020-04-21 | Outside Waratek scope | Proof of concept only | Server or client applications that call the SSL_check_chain() function during or after a TLS 1.3 handshake may crash due to a NULL pointer dereference as a result of incorrect handling of the "signature_algorithms_cert" TLS extension. The crash occurs if an invalid or unrecognised signature algorithm is received from the peer. This could be exploited by a malicious peer in a Denial of Service attack. OpenSSL version 1.1.1d, 1.1.1e, and 1.1.1f are affected by this issue. This issue did not affect OpenSSL versions prior to 1.1.1d. Fixed in OpenSSL 1.1.1g (Affected 1.1.1d-1.1.1f). |
| CVE-2020-5398 | High | 2020-01-17 | Outside Waratek scope | Proof of concept only | In Spring Framework, versions 5.2.x prior to 5.2.3, versions 5.1.x prior to 5.1.13, and versions 5.0.x prior to 5.0.16, an application is vulnerable to a reflected file download (RFD) attack when it sets a "Content-Disposition" header in the response where the filename attribute is derived from user supplied input. |
| CVE-2019-0227 | High | 2019-05-01 | Outside Waratek scope | Working exploit published | A Server Side Request Forgery (SSRF) vulnerability affected the Apache Axis 1.4 distribution that was last released in 2006. Security and bug commits commits continue in the projects Axis 1.x Subversion repository, legacy users are encouraged to build from source. The successor to Axis 1.x is Axis2, the latest version is 1.7.9 and is not vulnerable to this issue. |