
Oracle Critical Patch Update July 2020
Released July 2020 · Oracle's advisory ↗ · ← Critical Patch Update, April 2020 · Critical Patch Update, October 2020 →
285 CVEs in this release, one square each
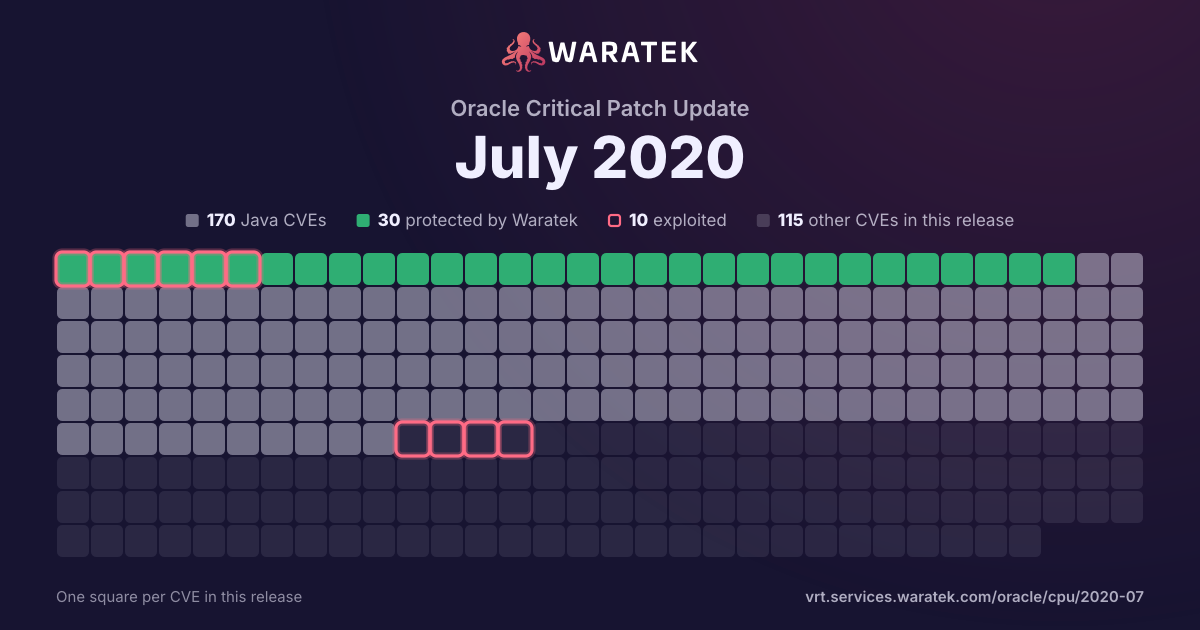
By status
30Protected by Waratek1Mitigation candidate139No exploit published68Outside Waratek scope47Not applicable
10Exploited, marked by the ring
No exploit published. For 126 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 8 matches · 0 in Waratek scope · 0 protected · 4 exploited · 0 CISA KEV · 6 EPSS ≥ 0.5
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
7
87.5%
Not applicable
1
12.5%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
8
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
4
50.0%
Working exploit published
1
12.5%
Proof of concept only
3
37.5%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 2 / quarter
Q1 181
Outside Waratek scope1
Medium1
not blocked1
Exploited1
Q2 181
Outside Waratek scope1
Medium1
not blocked1
Exploited1
Q3 180
Q4 180
Q1 191
Not applicable1
Medium1
not blocked1
Proof of concept only1
Q2 192
Outside Waratek scope2
High1
Medium1
not blocked2
Exploited1
Working exploit published1
Q3 190
Q4 190
Q1 201
Outside Waratek scope1
High1
not blocked1
Proof of concept only1
Q2 202
Outside Waratek scope2
High1
Medium1
not blocked2
Exploited1
Proof of concept only1
Q1 18Q2 18Q3 18Q4 18Q1 19Q2 19Q3 19Q4 19Q1 20Q2 20
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2020-11022 | Medium | 2020-04-29 | Outside Waratek scope | Exploited | In jQuery starting with 1.12.0 and before 3.5.0, passing HTML from untrusted sources - even after sanitizing it - to one of jQuery's DOM manipulation methods (i.e. .html(), .append(), and others) may execute untrusted code. This problem is patched in jQuery 3.5.0. |
| CVE-2020-1967 | High | 2020-04-21 | Outside Waratek scope | Proof of concept only | Server or client applications that call the SSL_check_chain() function during or after a TLS 1.3 handshake may crash due to a NULL pointer dereference as a result of incorrect handling of the "signature_algorithms_cert" TLS extension. The crash occurs if an invalid or unrecognised signature algorithm is received from the peer. This could be exploited by a malicious peer in a Denial of Service attack. OpenSSL version 1.1.1d, 1.1.1e, and 1.1.1f are affected by this issue. This issue did not affect OpenSSL versions prior to 1.1.1d. Fixed in OpenSSL 1.1.1g (Affected 1.1.1d-1.1.1f). |
| CVE-2020-5398 | High | 2020-01-17 | Outside Waratek scope | Proof of concept only | In Spring Framework, versions 5.2.x prior to 5.2.3, versions 5.1.x prior to 5.1.13, and versions 5.0.x prior to 5.0.16, an application is vulnerable to a reflected file download (RFD) attack when it sets a "Content-Disposition" header in the response where the filename attribute is derived from user supplied input. |
| CVE-2019-0227 | High | 2019-05-01 | Outside Waratek scope | Working exploit published | A Server Side Request Forgery (SSRF) vulnerability affected the Apache Axis 1.4 distribution that was last released in 2006. Security and bug commits commits continue in the projects Axis 1.x Subversion repository, legacy users are encouraged to build from source. The successor to Axis 1.x is Axis2, the latest version is 1.7.9 and is not vulnerable to this issue. |
| CVE-2019-11358 | Medium | 2019-04-20 | Outside Waratek scope | Exploited | jQuery before 3.4.0, as used in Drupal, Backdrop CMS, and other products, mishandles jQuery.extend(true, {}, ...) because of Object.prototype pollution. If an unsanitized source object contained an enumerable __proto__ property, it could extend the native Object.prototype. |
| CVE-2019-5489 | Medium | 2019-01-07 | Not applicable | Proof of concept only | The mincore() implementation in mm/mincore.c in the Linux kernel through 4.19.13 allowed local attackers to observe page cache access patterns of other processes on the same system, potentially allowing sniffing of secret information. (Fixing this affects the output of the fincore program.) Limited remote exploitation may be possible, as demonstrated by latency differences in accessing public files from an Apache HTTP Server. |
| CVE-2018-3639 | Medium | 2018-05-22 | Outside Waratek scope | Exploited | Systems with microprocessors utilizing speculative execution and speculative execution of memory reads before the addresses of all prior memory writes are known may allow unauthorized disclosure of information to an attacker with local user access via a side-channel analysis, aka Speculative Store Bypass (SSB), Variant 4. |
| CVE-2015-9251 | Medium | 2018-01-18 | Outside Waratek scope | Exploited | jQuery before 3.0.0 is vulnerable to Cross-site Scripting (XSS) attacks when a cross-domain Ajax request is performed without the dataType option, causing text/javascript responses to be executed. |