
Oracle Critical Patch Update April 2020
Released April 2020 · Oracle's advisory ↗ · ← Critical Patch Update, January 2020 · Critical Patch Update, July 2020 →
300 CVEs in this release, one square each
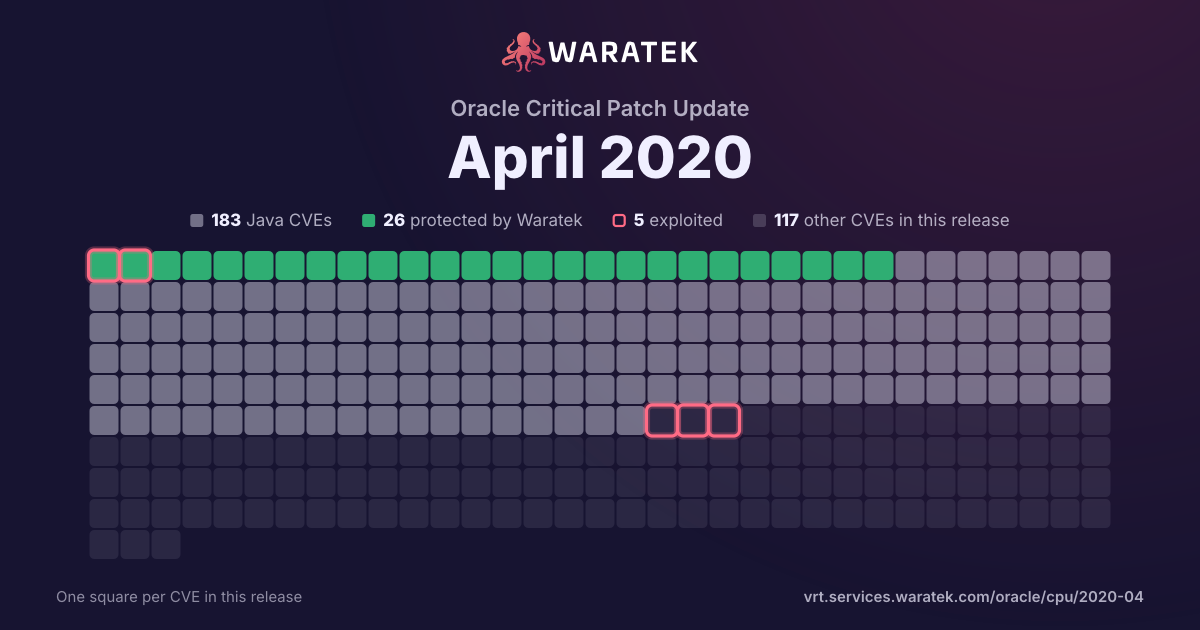
By status
26Protected by Waratek1Mitigation candidate156No exploit published60Outside Waratek scope56Not applicable1Withdrawn CVE
5Exploited, marked by the ring
No exploit published. For 141 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 10 matches · 5 protected · 2 exploited · 1 CISA KEV · 4 public PoC
Protected by Waratek
5
50.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
5
50.0%
blocked by ARMR today
5
50.0%
partly blocked
0
0.0%
not blocked
5
50.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
2
20.0%
Working exploit published
1
10.0%
Proof of concept only
1
10.0%
Forecast only
6
60.0%
No public exploit
0
0.0%
split by
peak 5 / quarter
Q2 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Working exploit published1
Q3 170
Q4 170
Q1 180
Q2 180
Q3 180
Q4 180
Q1 190
Q2 192
Protected by Waratek1
No exploit published1
Critical1
High1
blocked by ARMR today1
not blocked1
Exploited1
Forecast only1
Q3 191
Protected by Waratek1
Critical1
blocked by ARMR today1
Forecast only1
Q4 191
Protected by Waratek1
Critical1
blocked by ARMR today1
Proof of concept only1
Q1 200
Q2 205
Protected by Waratek1
No exploit published4
Critical2
High3
blocked by ARMR today1
not blocked4
Exploited1
Forecast only4
Q2 17Q4 17Q2 18Q4 18Q2 19Q4 19Q2 20
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2020-2950 | Critical | 2020-04-15 | No exploit published | Forecast only | Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Fusion Middleware (component: Analytics Web General). Supported versions that are affected are 5.5.0.0.0, 11.1.1.9.0, 12.2.1.3.0 and 12.2.1.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Business Intelligence Enterprise Edition. Successful attacks of this vulnerability can result in takeover of Oracle Business Intelligence Enterprise Edition. CVSS 3.0 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2020-2883 | Critical | 2020-04-15 | Protected by Waratek | Exploited | Vulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core). Supported versions that are affected are 10.3.6.0.0, 12.1.3.0.0, 12.2.1.3.0 and 12.2.1.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via IIOP, T3 to compromise Oracle WebLogic Server. Successful attacks of this vulnerability can result in takeover of Oracle WebLogic Server. CVSS 3.0 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2020-2871 | High | 2020-04-15 | No exploit published | Forecast only | Vulnerability in the Oracle Advanced Outbound Telephony product of Oracle E-Business Suite (component: User Interface). Supported versions that are affected are 12.1.1-12.1.3 and 12.2.3-12.2.9. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Advanced Outbound Telephony. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Advanced Outbound Telephony, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Advanced Outbound Telephony accessible data as well as unauthorized update, insert or delete access to some of Oracle Advanced Outbound Telephony accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2020-2854 | High | 2020-04-15 | No exploit published | Forecast only | Vulnerability in the Oracle Advanced Outbound Telephony product of Oracle E-Business Suite (component: User Interface). Supported versions that are affected are 12.1.1-12.1.3. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Advanced Outbound Telephony. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Advanced Outbound Telephony, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Advanced Outbound Telephony accessible data as well as unauthorized update, insert or delete access to some of Oracle Advanced Outbound Telephony accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2020-2852 | High | 2020-04-15 | No exploit published | Forecast only | Vulnerability in the Oracle Advanced Outbound Telephony product of Oracle E-Business Suite (component: Calendar). Supported versions that are affected are 12.1.1-12.1.3. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Advanced Outbound Telephony. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Advanced Outbound Telephony, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Advanced Outbound Telephony accessible data as well as unauthorized update, insert or delete access to some of Oracle Advanced Outbound Telephony accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2019-17571 | Critical | 2019-12-20 | Protected by Waratek | Proof of concept only | Included in Log4j 1.2 is a SocketServer class that is vulnerable to deserialization of untrusted data which can be exploited to remotely execute arbitrary code when combined with a deserialization gadget when listening to untrusted network traffic for log data. This affects Log4j versions up to 1.2 up to 1.2.17. |
| CVE-2019-10173 | Critical | 2019-07-23 | Protected by Waratek | Forecast only | It was found that xstream API version 1.4.10 before 1.4.11 introduced a regression for a previous deserialization flaw. If the security framework has not been initialized, it may allow a remote attacker to run arbitrary shell commands when unmarshalling XML or any supported format. e.g. JSON. (regression of CVE-2013-7285) |
| CVE-2019-10072 | High | 2019-06-21 | No exploit published | Forecast only | The fix for CVE-2019-0199 was incomplete and did not address HTTP/2 connection window exhaustion on write in Apache Tomcat versions 9.0.0.M1 to 9.0.19 and 8.5.0 to 8.5.40 . By not sending WINDOW_UPDATE messages for the connection window (stream 0) clients were able to cause server-side threads to block eventually leading to thread exhaustion and a DoS. |
| CVE-2019-2729 | Critical | 2019-06-19 | Protected by Waratek | Exploited | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: Web Services). Supported versions that are affected are 10.3.6.0.0, 12.1.3.0.0 and 12.2.1.3.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebLogic Server. Successful attacks of this vulnerability can result in takeover of Oracle WebLogic Server. CVSS 3.0 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2017-5645 | Critical | 2017-04-17 | Protected by Waratek | Working exploit published | In Apache Log4j 2.x before 2.8.2, when using the TCP socket server or UDP socket server to receive serialized log events from another application, a specially crafted binary payload can be sent that, when deserialized, can execute arbitrary code. |