
Oracle Critical Patch Update April 2019
Released April 2019 · Oracle's advisory ↗ · ← Critical Patch Update, January 2019 · Critical Patch Update, July 2019 →
207 CVEs in this release, one square each
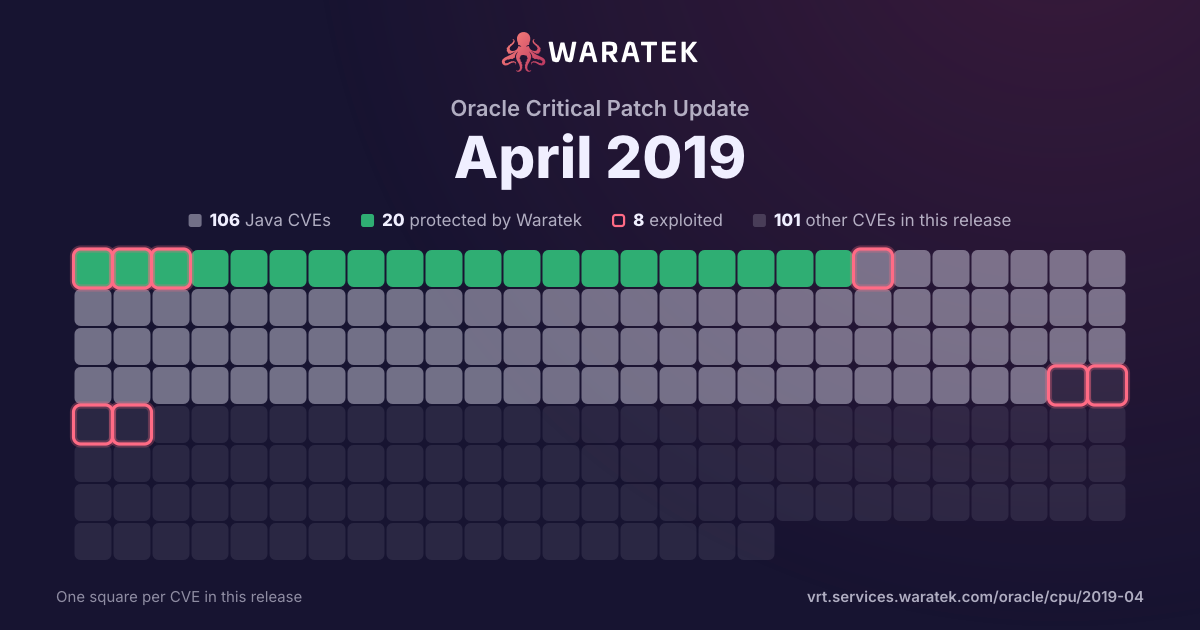
By status
20Protected by Waratek3Mitigation candidate83No exploit published58Outside Waratek scope43Not applicable
8Exploited, marked by the ring
No exploit published. For 80 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 106 matches · 19 protected · 4 exploited · 1 CISA KEV · 8 public PoC · 4 EPSS ≥ 0.5
Protected by Waratek
20
18.9%
Rule in development
0
0.0%
Mitigation candidate
3
2.8%
No exploit published
83
78.3%
blocked by ARMR today
19
17.9%
partly blocked
1
0.9%
not blocked
86
81.1%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 87 / quarter
Q2 142
Protected by Waratek2
High2
blocked by ARMR today2
Exploited1
No public exploit1
Q3 140
Q4 140
Q1 150
Q2 150
Q3 150
Q4 150
Q1 160
Q2 161
No exploit published1
Critical1
not blocked1
No public exploit1
Q3 161
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Q4 161
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Q1 170
Q2 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Working exploit published1
Q3 171
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Q4 170
Q1 182
Protected by Waratek2
Critical2
blocked by ARMR today2
No public exploit2
Q2 183
Protected by Waratek1
No exploit published2
Critical1
High2
blocked by ARMR today1
not blocked2
No public exploit3
Q3 183
Protected by Waratek2
No exploit published1
High3
blocked by ARMR today2
not blocked1
Proof of concept only1
No public exploit2
Q4 180
Q1 194
Protected by Waratek4
Critical3
High1
blocked by ARMR today4
No public exploit4
Q2 1987
Protected by Waratek5
Mitigation candidate3
No exploit published79
Critical6
High44
Medium35
Low2
blocked by ARMR today4
partly blocked1
not blocked82
Exploited3
Working exploit published2
No public exploit82
Q2 14Q4 14Q2 15Q4 15Q2 16Q4 16Q2 17Q4 17Q2 18Q4 18Q2 19
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2017-5645 | Critical | 2017-04-17 | Protected by Waratek | Working exploit published | In Apache Log4j 2.x before 2.8.2, when using the TCP socket server or UDP socket server to receive serialized log events from another application, a specially crafted binary payload can be sent that, when deserialized, can execute arbitrary code. |
| CVE-2016-1000031 | Critical | 2016-10-25 | Protected by Waratek | No public exploit | Apache Commons FileUpload before 1.3.3 DiskFileItem File Manipulation Remote Code Execution |
| CVE-2016-1181 | High | 2016-07-04 | Protected by Waratek | No public exploit | ActionServlet.java in Apache Struts 1 1.x through 1.3.10 mishandles multithreaded access to an ActionForm instance, which allows remote attackers to execute arbitrary code or cause a denial of service (unexpected memory access) via a multipart request, a related issue to CVE-2015-0899. |
| CVE-2016-2141 | Critical | 2016-06-30 | No exploit published | No public exploit | It was found that JGroups did not require necessary headers for encrypt and auth protocols from new nodes joining the cluster. An attacker could use this flaw to bypass security restrictions, and use this vulnerability to send and receive messages within the cluster, leading to information disclosure, message spoofing, or further possible attacks. |
| CVE-2014-0114 | High | 2014-04-30 | Protected by Waratek | Exploited | Apache Commons BeanUtils, as distributed in lib/commons-beanutils-1.8.0.jar in Apache Struts 1.x through 1.3.10 and in other products requiring commons-beanutils through 1.9.2, does not suppress the class property, which allows remote attackers to "manipulate" the ClassLoader and execute arbitrary code via the class parameter, as demonstrated by the passing of this parameter to the getClass method of the ActionForm object in Struts 1. |
| CVE-2014-0107 | High | 2014-04-15 | Protected by Waratek | No public exploit | The TransformerFactory in Apache Xalan-Java before 2.7.2 does not properly restrict access to certain properties when FEATURE_SECURE_PROCESSING is enabled, which allows remote attackers to bypass expected restrictions and load arbitrary classes or access external resources via a crafted (1) xalan:content-header, (2) xalan:entities, (3) xslt:content-header, or (4) xslt:entities property, or a Java property that is bound to the XSLT 1.0 system-property function. |