
Oracle Critical Patch Update January 2019
Released January 2019 · Oracle's advisory ↗ · ← Critical Patch Update, October 2018 · Critical Patch Update, April 2019 →
198 CVEs in this release, one square each
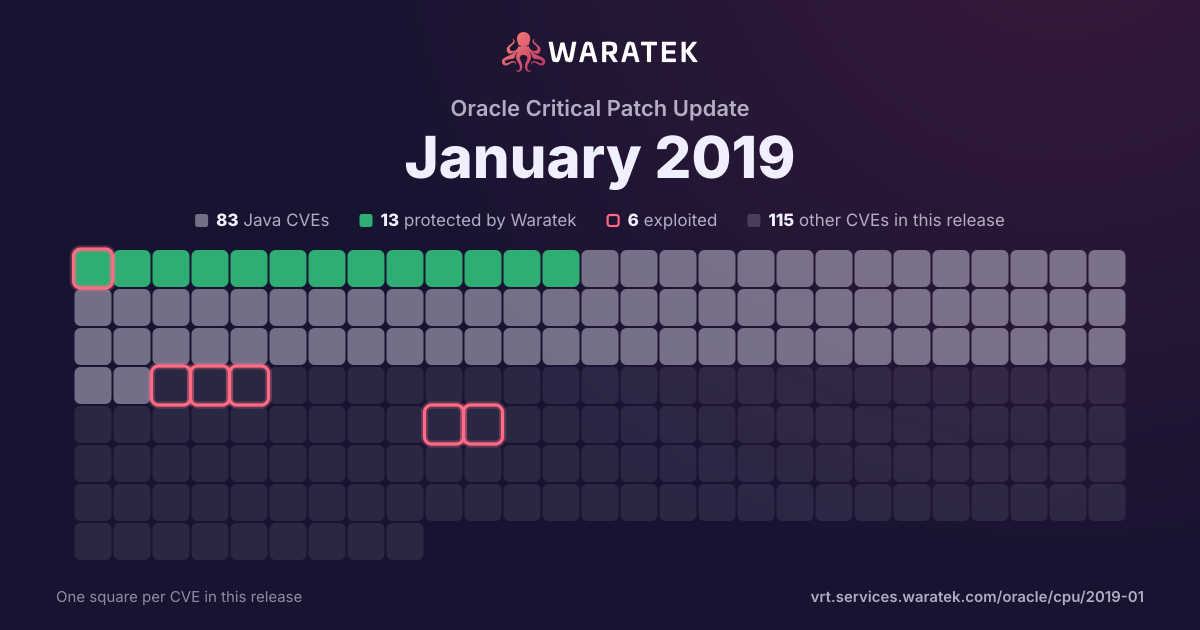
By status
13Protected by Waratek1Mitigation candidate69No exploit published34Outside Waratek scope81Not applicable
6Exploited, marked by the ring
No exploit published. For 67 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 83 matches · 13 protected · 1 exploited · 1 CISA KEV · 3 public PoC · 3 EPSS ≥ 0.5
Protected by Waratek
13
15.7%
Rule in development
0
0.0%
Mitigation candidate
1
1.2%
No exploit published
69
83.1%
blocked by ARMR today
13
15.7%
partly blocked
0
0.0%
not blocked
70
84.3%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
1.2%
Working exploit published
2
2.4%
Proof of concept only
0
0.0%
Forecast only
1
1.2%
No public exploit
79
95.2%
split by
peak 67 / year
20162
Protected by Waratek2
Critical1
High1
blocked by ARMR today2
No public exploit2
20174
Protected by Waratek3
No exploit published1
Critical3
Medium1
blocked by ARMR today3
not blocked1
Working exploit published1
No public exploit3
20189
Protected by Waratek5
No exploit published4
Critical4
High5
blocked by ARMR today5
not blocked4
Exploited1
Forecast only1
No public exploit7
201967
Protected by Waratek3
Mitigation candidate1
No exploit published63
Critical3
High16
Medium46
Low2
blocked by ARMR today3
not blocked64
Working exploit published1
No public exploit66
20200
20210
20220
20230
20241
No exploit published1
High1
not blocked1
No public exploit1
201620172018201920202021202220232024
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-2483 | High | 2024-12-24 | No exploit published | No public exploit | Vulnerability in the Oracle iStore product of Oracle E-Business Suite (component: Shopping Cart). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle iStore. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle iStore, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle iStore accessible data as well as unauthorized update, insert or delete access to some of Oracle iStore accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2018-12023 | High | 2019-03-21 | Protected by Waratek | No public exploit | An issue was discovered in FasterXML jackson-databind prior to 2.7.9.4, 2.8.11.2, and 2.9.6. When Default Typing is enabled (either globally or for a specific property), the service has the Oracle JDBC jar in the classpath, and an attacker can provide an LDAP service to access, it is possible to make the service execute a malicious payload. |
| CVE-2019-2550 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Direct Banking component of Oracle Financial Services Applications (subcomponent: Logoff Page). The supported version that is affected is 12.0.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle FLEXCUBE Direct Banking. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Direct Banking accessible data. CVSS 3.0 Base Score 4.3 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:U/C:N/I:L/A:N). |
| CVE-2019-2549 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Direct Banking component of Oracle Financial Services Applications (subcomponent: Logoff Page). The supported version that is affected is 12.0.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle FLEXCUBE Direct Banking. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle FLEXCUBE Direct Banking, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Direct Banking accessible data as well as unauthorized read access to a subset of Oracle FLEXCUBE Direct Banking accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2019-2546 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Applications Manager component of Oracle E-Business Suite (subcomponent: SQL Extensions). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Applications Manager. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Applications Manager accessible data. CVSS 3.0 Base Score 8.1 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:U/C:N/I:H/A:H). |
| CVE-2019-2540 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Java Advanced Management Console component of Oracle Java SE (subcomponent: Server). The supported version that is affected is Java Advanced Management Console: 2.12. Easily exploitable vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java Advanced Management Console. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Java Advanced Management Console, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Java Advanced Management Console accessible data as well as unauthorized read access to a subset of Java Advanced Management Console accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2019-2538 | High | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Managed File Transfer component of Oracle Fusion Middleware (subcomponent: MFT Runtime Server). Supported versions that are affected are 19.1.0.0.0 and 12.2.1.3.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Managed File Transfer. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Managed File Transfer accessible data as well as unauthorized read access to a subset of Oracle Managed File Transfer accessible data. CVSS 3.0 Base Score 7.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:H/A:N). |
| CVE-2019-2519 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise SCM eProcurement component of Oracle PeopleSoft Products (subcomponent: Manage Requisition Status). The supported version that is affected is 9.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise SCM eProcurement. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise SCM eProcurement, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise SCM eProcurement accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise SCM eProcurement accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2019-2512 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Primavera P6 Enterprise Project Portfolio Management component of Oracle Construction and Engineering Suite (subcomponent: Web Access). Supported versions that are affected are 8.4, 15.1, 15.2, 16.1, 16.2, 17.7-17.12 and 18.8. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Primavera P6 Enterprise Project Portfolio Management. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Primavera P6 Enterprise Project Portfolio Management, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Primavera P6 Enterprise Project Portfolio Management accessible data as well as unauthorized read access to a subset of Primavera P6 Enterprise Project Portfolio Management accessible data. CVSS 3.0 Base Score 4.7 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2019-2499 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: PIA Search Functionality). Supported versions that are affected are 8.55, 8.56 and 8.57. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PeopleTools, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PeopleTools accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2019-2498 | High | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Partner Management component of Oracle E-Business Suite (subcomponent: Partner Dash board). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Partner Management. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Partner Management, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Partner Management accessible data as well as unauthorized update, insert or delete access to some of Oracle Partner Management accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2019-2497 | High | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle CRM Technical Foundation component of Oracle E-Business Suite (subcomponent: Messages). Supported versions that are affected are 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle CRM Technical Foundation. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle CRM Technical Foundation, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle CRM Technical Foundation accessible data as well as unauthorized update, insert or delete access to some of Oracle CRM Technical Foundation accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2019-2496 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle CRM Technical Foundation component of Oracle E-Business Suite (subcomponent: Messages). Supported versions that are affected are 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle CRM Technical Foundation. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle CRM Technical Foundation, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle CRM Technical Foundation accessible data. CVSS 3.0 Base Score 4.7 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:N/I:L/A:N). |
| CVE-2019-2493 | Low | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise CS Campus Community component of Oracle PeopleSoft Products (subcomponent: Frameworks). Supported versions that are affected are 9.0 and 9.2. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise CS Campus Community. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise CS Campus Community accessible data. CVSS 3.0 Base Score 3.1 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:R/S:U/C:N/I:L/A:N). |
| CVE-2019-2492 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Email Center component of Oracle E-Business Suite (subcomponent: Message Display). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Email Center. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Email Center, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Email Center accessible data. CVSS 3.0 Base Score 4.7 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:N/I:L/A:N). |
| CVE-2019-2491 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Email Center component of Oracle E-Business Suite (subcomponent: Message Display). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Email Center. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Email Center, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Email Center accessible data. CVSS 3.0 Base Score 4.7 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:N/I:L/A:N). |
| CVE-2019-2490 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Panel Processor). Supported versions that are affected are 8.55, 8.56 and 8.57. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PeopleTools, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 4.7 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:N/I:L/A:N). |
| CVE-2019-2489 | Critical | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle One-to-One Fulfillment component of Oracle E-Business Suite (subcomponent: OCM Query). Supported versions that are affected are 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle One-to-One Fulfillment. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle One-to-One Fulfillment accessible data as well as unauthorized access to critical data or complete access to all Oracle One-to-One Fulfillment accessible data. CVSS 3.0 Base Score 9.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2019-2488 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle CRM Technical Foundation component of Oracle E-Business Suite (subcomponent: Session Management). Supported versions that are affected are 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle CRM Technical Foundation. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle CRM Technical Foundation accessible data. CVSS 3.0 Base Score 5.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2019-2487 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Transportation Management component of Oracle Supply Chain Products Suite (subcomponent: UI Infrastructure). Supported versions that are affected are 6.3.7, 6.4.1, 6.4.2 and 6.4.3. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Transportation Management. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Transportation Management accessible data. CVSS 3.0 Base Score 6.5 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:H/A:N). |
| CVE-2019-2485 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Mobile Field Service component of Oracle E-Business Suite (subcomponent: Administration). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Mobile Field Service. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Mobile Field Service, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Mobile Field Service accessible data. CVSS 3.0 Base Score 4.7 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:N/I:L/A:N). |
| CVE-2019-2471 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Portal). Supported versions that are affected are 8.55, 8.56 and 8.57. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PeopleTools, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PeopleTools accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2019-2470 | High | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Partner Management component of Oracle E-Business Suite (subcomponent: Partner Detail). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Partner Management. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Partner Management, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Partner Management accessible data as well as unauthorized update, insert or delete access to some of Oracle Partner Management accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2019-2453 | Critical | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Performance Management component of Oracle E-Business Suite (subcomponent: Performance Management Plan). Supported versions that are affected are 12.1.1, 12.1.2 and 12.1.3. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Performance Management. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Performance Management accessible data as well as unauthorized access to critical data or complete access to all Oracle Performance Management accessible data. CVSS 3.0 Base Score 9.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2019-2452 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: WLS Core Components). Supported versions that are affected are 10.3.6.0, 12.1.3.0 and 12.2.1.3. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle WebLogic Server. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle WebLogic Server accessible data as well as unauthorized read access to a subset of Oracle WebLogic Server accessible data and unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle WebLogic Server. CVSS 3.0 Base Score 6.7 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:L/I:H/A:H). |
| CVE-2019-2447 | High | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Partner Management component of Oracle E-Business Suite (subcomponent: Partner Detail). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Partner Management. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Partner Management, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Partner Management accessible data as well as unauthorized update, insert or delete access to some of Oracle Partner Management accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2019-2445 | High | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Content Manager component of Oracle E-Business Suite (subcomponent: Cover Letter). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Content Manager. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Content Manager, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Content Manager accessible data as well as unauthorized update, insert or delete access to some of Oracle Content Manager accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2019-2443 | High | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: XML Publisher). Supported versions that are affected are 8.55, 8.56 and 8.57. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks of this vulnerability can result in takeover of PeopleSoft Enterprise PeopleTools. CVSS 3.0 Base Score 7.2 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2019-2442 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Fluid Core). Supported versions that are affected are 8.55, 8.56 and 8.57. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PeopleTools, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PeopleTools accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2019-2441 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: Application Container - JavaEE). The supported version that is affected is 12.2.1.3. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebLogic Server. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle WebLogic Server accessible data. CVSS 3.0 Base Score 5.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2019-2440 | High | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Marketing component of Oracle E-Business Suite (subcomponent: User Interface). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Marketing. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Marketing, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Marketing accessible data as well as unauthorized update, insert or delete access to some of Oracle Marketing accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2019-2439 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Portal). Supported versions that are affected are 8.55, 8.56 and 8.57. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PeopleTools, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PeopleTools accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2019-2438 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Web Cache component of Oracle Fusion Middleware (subcomponent: ESI/Partial Page Caching). The supported version that is affected is 11.1.1.9.0. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Web Cache. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Web Cache, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Web Cache accessible data as well as unauthorized update, insert or delete access to some of Oracle Web Cache accessible data. CVSS 3.0 Base Score 6.9 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2019-2433 | High | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: XML Publisher). Supported versions that are affected are 8.55, 8.56 and 8.57. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks of this vulnerability can result in takeover of PeopleSoft Enterprise PeopleTools. CVSS 3.0 Base Score 7.2 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2019-2432 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Argus Safety component of Oracle Health Sciences Applications (subcomponent: Login). Supported versions that are affected are 8.1 and 8.2. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Argus Safety. While the vulnerability is in Oracle Argus Safety, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Argus Safety accessible data as well as unauthorized read access to a subset of Oracle Argus Safety accessible data. CVSS 3.0 Base Score 4.9 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:L/UI:N/S:C/C:L/I:L/A:N). |
| CVE-2019-2431 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Argus Safety component of Oracle Health Sciences Applications (subcomponent: Console). Supported versions that are affected are 8.1 and 8.2. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Argus Safety. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Argus Safety, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Argus Safety accessible data. CVSS 3.0 Base Score 6.1 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:R/S:C/C:N/I:H/A:N). |
| CVE-2019-2430 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Argus Safety component of Oracle Health Sciences Applications (subcomponent: Console). Supported versions that are affected are 8.1 and 8.2. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Argus Safety. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Argus Safety accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2019-2427 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Portal component of Oracle Fusion Middleware (subcomponent: WebCenter Spaces Application). Supported versions that are affected are 11.1.1.9.0 and 12.2.1.3.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebCenter Portal. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle WebCenter Portal accessible data. CVSS 3.0 Base Score 5.3 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2019-2426 | Low | 2019-01-16 | Protected by Waratek | No public exploit | Vulnerability in the Java SE component of Oracle Java SE (subcomponent: Networking). Supported versions that are affected are Java SE: 7u201, 8u192 and 11.0.1; Java SE Embedded: 8u191. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Java SE accessible data. Note: This vulnerability applies to Java deployments, typically in clients running sandboxed Java Web Start applications or sandboxed Java applets (in Java SE 8), that load and run untrusted code (e.g., code that comes from the internet) and rely on the Java sandbox for security. This vulnerability can also be exploited by using APIs in the specified Component, e.g., through a web service which supplies data to the APIs. CVSS 3.0 Base Score 3.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2019-2425 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality Reporting and Analytics component of Oracle Food and Beverage Applications. The supported version that is affected is 9.1.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Hospitality Reporting and Analytics. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Hospitality Reporting and Analytics accessible data as well as unauthorized read access to a subset of Oracle Hospitality Reporting and Analytics accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2019-2423 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: PIA Search). Supported versions that are affected are 8.55, 8.56 and 8.57. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PeopleTools, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PeopleTools accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2019-2421 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise HCM eProfile Manager Desktop component of Oracle PeopleSoft Products (subcomponent: Guided Self Service). The supported version that is affected is 9.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise HCM eProfile Manager Desktop. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise HCM eProfile Manager Desktop, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise HCM eProfile Manager Desktop accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise HCM eProfile Manager Desktop accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2019-2419 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise CC Common Application Objects component of Oracle PeopleSoft Products (subcomponent: Form and Approval Builder). The supported version that is affected is 9.2. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise CC Common Application Objects. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise CC Common Application Objects, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise CC Common Application Objects accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise CC Common Application Objects accessible data. Note: This Enterprise Common Component is used by all PeopleSoft Application products. Please refer to the <a target="_blank" href="https://support.oracle.com/rs?type=doc&id=2487756.1">MOS Note Doc ID 2493366.1 for patch information. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2019-2418 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: WLS Core Components). Supported versions that are affected are 10.3.6.0, 12.1.3.0 and 12.2.1.3. Difficult to exploit vulnerability allows unauthenticated attacker with network access via T3 to compromise Oracle WebLogic Server. While the vulnerability is in Oracle WebLogic Server, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle WebLogic Server accessible data as well as unauthorized read access to a subset of Oracle WebLogic Server accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle WebLogic Server. CVSS 3.0 Base Score 6.5 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:C/C:L/I:L/A:L). |
| CVE-2019-2417 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Performance Monitor). Supported versions that are affected are 8.55, 8.56 and 8.57. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PeopleTools accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2019-2416 | High | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Application Server). Supported versions that are affected are 8.55, 8.56 and 8.57. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks of this vulnerability can result in takeover of PeopleSoft Enterprise PeopleTools. CVSS 3.0 Base Score 8.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2019-2415 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Hyperion BI+ component of Oracle Hyperion (subcomponent: Foundation UI & Servlets). The supported version that is affected is 11.1.2.4. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Hyperion BI+. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Hyperion BI+ accessible data as well as unauthorized read access to a subset of Hyperion BI+ accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Hyperion BI+. CVSS 3.0 Base Score 4.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:U/C:L/I:L/A:L). |
| CVE-2019-2413 | Medium | 2019-01-16 | Mitigation candidate | Working exploit published | Vulnerability in the Oracle Reports Developer component of Oracle Fusion Middleware (subcomponent: Valid Session). The supported version that is affected is 12.2.1.3. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Reports Developer. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Reports Developer, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Reports Developer accessible data as well as unauthorized read access to a subset of Oracle Reports Developer accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2019-2411 | High | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality Cruise Shipboard Property Management System component of Oracle Hospitality Applications (subcomponent: SPMS Suite). The supported version that is affected is 8.0.8. Easily exploitable vulnerability allows low privileged attacker with network access via TCP to compromise Oracle Hospitality Cruise Shipboard Property Management System. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Hospitality Cruise Shipboard Property Management System, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Hospitality Cruise Shipboard Property Management System as well as unauthorized update, insert or delete access to some of Oracle Hospitality Cruise Shipboard Property Management System accessible data. CVSS 3.0 Base Score 7.6 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:N/I:L/A:H). |
| CVE-2019-2410 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality Cruise Shipboard Property Management System component of Oracle Hospitality Applications (subcomponent: DGS RES Online, FMS Sender, FMS Receiver, OHC WPF Security). The supported version that is affected is 8.0.8. Easily exploitable vulnerability allows unauthenticated attacker with logon to the infrastructure where Oracle Hospitality Cruise Shipboard Property Management System executes to compromise Oracle Hospitality Cruise Shipboard Property Management System. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Hospitality Cruise Shipboard Property Management System accessible data as well as unauthorized read access to a subset of Oracle Hospitality Cruise Shipboard Property Management System accessible data. CVSS 3.0 Base Score 5.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2019-2409 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality Cruise Shipboard Property Management System component of Oracle Hospitality Applications (subcomponent: SPMS Suite). The supported version that is affected is 8.0.8. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Hospitality Cruise Shipboard Property Management System executes to compromise Oracle Hospitality Cruise Shipboard Property Management System. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Hospitality Cruise Shipboard Property Management System, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Hospitality Cruise Shipboard Property Management System as well as unauthorized update, insert or delete access to some of Oracle Hospitality Cruise Shipboard Property Management System accessible data and unauthorized read access to a subset of Oracle Hospitality Cruise Shipboard Property Management System accessible data. CVSS 3.0 Base Score 7.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:H). |
| CVE-2019-2408 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Feeds). Supported versions that are affected are 8.55, 8.56 and 8.57. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 4.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:N/A:N). |
| CVE-2019-2407 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality Reporting and Analytics component of Oracle Food and Beverage Applications. The supported version that is affected is 9.1.0. Easily exploitable vulnerability allows low privileged attacker having Report privilege with logon to the infrastructure where Oracle Hospitality Reporting and Analytics executes to compromise Oracle Hospitality Reporting and Analytics. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Hospitality Reporting and Analytics accessible data as well as unauthorized update, insert or delete access to some of Oracle Hospitality Reporting and Analytics accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:L/A:N). |
| CVE-2019-2405 | High | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Security). Supported versions that are affected are 8.55, 8.56 and 8.57. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks of this vulnerability can result in takeover of PeopleSoft Enterprise PeopleTools. CVSS 3.0 Base Score 7.5 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2019-2404 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Portal). Supported versions that are affected are 8.55, 8.56 and 8.57. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks of this vulnerability can result in unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 5.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2019-2401 | High | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality Reporting and Analytics component of Oracle Food and Beverage Applications. The supported version that is affected is 9.1.0. Easily exploitable vulnerability allows low privileged attacker having Admin privilege with network access via HTTP to compromise Oracle Hospitality Reporting and Analytics. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Hospitality Reporting and Analytics accessible data as well as unauthorized access to critical data or complete access to all Oracle Hospitality Reporting and Analytics accessible data. CVSS 3.0 Base Score 8.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2019-2400 | High | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle iStore component of Oracle E-Business Suite (subcomponent: User Registration). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle iStore. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle iStore, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle iStore accessible data as well as unauthorized update, insert or delete access to some of Oracle iStore accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2019-2399 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Diameter Signaling Router (DSR) component of Oracle Communications Applications (subcomponent: Security). The supported version that is affected is prior to 8.3. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Communications Diameter Signaling Router (DSR). Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Communications Diameter Signaling Router (DSR) accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Communications Diameter Signaling Router (DSR). CVSS 3.0 Base Score 6.5 (Confidentiality and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:L). |
| CVE-2019-2398 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: WLS - Deployment). Supported versions that are affected are 10.3.6.0, 12.1.3.0 and 12.2.1.3. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle WebLogic Server. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle WebLogic Server accessible data. CVSS 3.0 Base Score 4.3 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2019-2397 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality Reporting and Analytics component of Oracle Food and Beverage Applications. The supported version that is affected is 9.1.0. Easily exploitable vulnerability allows low privileged attacker having Report privilege with logon to the infrastructure where Oracle Hospitality Reporting and Analytics executes to compromise Oracle Hospitality Reporting and Analytics. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Hospitality Reporting and Analytics accessible data as well as unauthorized read access to a subset of Oracle Hospitality Reporting and Analytics accessible data. CVSS 3.0 Base Score 4.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2019-2396 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle CRM Technical Foundation component of Oracle E-Business Suite (subcomponent: Messages). Supported versions that are affected are 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle CRM Technical Foundation. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle CRM Technical Foundation, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle CRM Technical Foundation accessible data. CVSS 3.0 Base Score 4.7 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:N/I:L/A:N). |
| CVE-2019-2395 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: WLS - Web Services). The supported version that is affected is 10.3.6.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle WebLogic Server. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle WebLogic Server accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle WebLogic Server. CVSS 3.0 Base Score 5.4 (Confidentiality and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:L). |
| CVE-2018-3311 | High | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Retail Xstore Payment component of Oracle Retail Applications (subcomponent: Security). The supported version that is affected is 3.3. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Retail Xstore Payment. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Retail Xstore Payment accessible data as well as unauthorized update, insert or delete access to some of Oracle Retail Xstore Payment accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Retail Xstore Payment. CVSS 3.0 Base Score 8.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:L/A:L). |
| CVE-2018-3305 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Application Testing Suite component of Oracle Enterprise Manager Products Suite (subcomponent: Load Testing for Web Apps). Supported versions that are affected are 12.5.0.3, 13.1.0.1, 13.2.0.1 and 13.3.0.1. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Application Testing Suite. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Application Testing Suite accessible data as well as unauthorized read access to a subset of Oracle Application Testing Suite accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Application Testing Suite. CVSS 3.0 Base Score 6.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:L). |
| CVE-2018-3304 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Application Testing Suite component of Oracle Enterprise Manager Products Suite (subcomponent: Load Testing for Web Apps). Supported versions that are affected are 12.5.0.3, 13.1.0.1, 13.2.0.1 and 13.3.0.1. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Application Testing Suite. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Application Testing Suite accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Application Testing Suite. CVSS 3.0 Base Score 6.5 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:L/A:L). |
| CVE-2018-3303 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Enterprise Manager Base Platform component of Oracle Enterprise Manager Products Suite (subcomponent: EM Console). Supported versions that are affected are 13.2 and 13.3. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Enterprise Manager Base Platform. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Enterprise Manager Base Platform accessible data as well as unauthorized read access to a subset of Enterprise Manager Base Platform accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2018-3125 | Medium | 2019-01-16 | No exploit published | No public exploit | Vulnerability in the Oracle Retail Merchandising System component of Oracle Retail Applications (subcomponent: Security (SQL Logger)). The supported version that is affected is 14.1. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Retail Merchandising System. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Retail Merchandising System accessible data as well as unauthorized read access to a subset of Oracle Retail Merchandising System accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2018-14718 | Critical | 2019-01-02 | Protected by Waratek | No public exploit | FasterXML jackson-databind 2.x before 2.9.7 might allow remote attackers to execute arbitrary code by leveraging failure to block the slf4j-ext class from polymorphic deserialization. |
| CVE-2018-11775 | High | 2018-09-10 | No exploit published | No public exploit | TLS hostname verification when using the Apache ActiveMQ Client before 5.15.6 was missing which could make the client vulnerable to a MITM attack between a Java application using the ActiveMQ client and the ActiveMQ server. This is now enabled by default. |
| CVE-2018-11776 | High | 2018-08-22 | Protected by Waratek | Exploited | Apache Struts versions 2.3 to 2.3.34 and 2.5 to 2.5.16 suffer from possible Remote Code Execution when alwaysSelectFullNamespace is true (either by user or a plugin like Convention Plugin) and then: results are used with no namespace and in same time, its upper package have no or wildcard namespace and similar to results, same possibility when using url tag which doesn't have value and action set and in same time, its upper package have no or wildcard namespace. |
| CVE-2018-1000632 | High | 2018-08-20 | Protected by Waratek | No public exploit | dom4j version prior to version 2.1.1 contains a CWE-91: XML Injection vulnerability in Class: Element. Methods: addElement, addAttribute that can result in an attacker tampering with XML documents through XML injection. This attack appear to be exploitable via an attacker specifying attributes or elements in the XML document. This vulnerability appears to have been fixed in 2.1.1 or later. |
| CVE-2017-7658 | Critical | 2018-06-26 | No exploit published | No public exploit | In Eclipse Jetty Server, versions 9.2.x and older, 9.3.x (all non HTTP/1.x configurations), and 9.4.x (all HTTP/1.x configurations), when presented with two content-lengths headers, Jetty ignored the second. When presented with a content-length and a chunked encoding header, the content-length was ignored (as per RFC 2616). If an intermediary decided on the shorter length, but still passed on the longer body, then body content could be interpreted by Jetty as a pipelined request. If the intermediary was imposing authorization, the fake pipelined request would bypass that authorization. |
| CVE-2018-1000180 | High | 2018-06-05 | No exploit published | No public exploit | Bouncy Castle BC 1.54 - 1.59, BC-FJA 1.0.0, BC-FJA 1.0.1 and earlier have a flaw in the Low-level interface to RSA key pair generator, specifically RSA Key Pairs generated in low-level API with added certainty may have less M-R tests than expected. This appears to be fixed in versions BC 1.60 beta 4 and later, BC-FJA 1.0.2 and later. |
| CVE-2018-8013 | Critical | 2018-05-24 | Protected by Waratek | No public exploit | In Apache Batik 1.x before 1.10, when deserializing subclass of `AbstractDocument`, the class takes a string from the inputStream as the class name which then use it to call the no-arg constructor of the class. Fix was to check the class type before calling newInstance in deserialization. |
| CVE-2018-1258 | High | 2018-05-11 | No exploit published | No public exploit | Spring Framework version 5.0.5 when used in combination with any versions of Spring Security contains an authorization bypass when using method security. An unauthorized malicious user can gain unauthorized access to methods that should be restricted. |
| CVE-2018-1275 | Critical | 2018-04-11 | Protected by Waratek | Forecast only | Spring Framework, versions 5.0 prior to 5.0.5 and versions 4.3 prior to 4.3.16 and older unsupported versions, allow applications to expose STOMP over WebSocket endpoints with a simple, in-memory STOMP broker through the spring-messaging module. A malicious user (or attacker) can craft a message to the broker that can lead to a remote code execution attack. This CVE addresses the partial fix for CVE-2018-1270 in the 4.3.x branch of the Spring Framework. |
| CVE-2017-15095 | Critical | 2018-02-06 | Protected by Waratek | No public exploit | A deserialization flaw was discovered in the jackson-databind in versions before 2.8.10 and 2.9.1, which could allow an unauthenticated user to perform code execution by sending the maliciously crafted input to the readValue method of the ObjectMapper. This issue extends the previous flaw CVE-2017-7525 by blacklisting more classes that could be used maliciously. |
| CVE-2017-14735 | Medium | 2017-09-25 | Protected by Waratek | No public exploit | OWASP AntiSamy before 1.5.7 allows XSS via HTML5 entities, as demonstrated by use of : to construct a javascript: URL. |
| CVE-2016-4000 | Critical | 2017-07-06 | Protected by Waratek | No public exploit | Jython before 2.7.1rc1 allows attackers to execute arbitrary code via a crafted serialized PyFunction object. |
| CVE-2017-5645 | Critical | 2017-04-17 | Protected by Waratek | Working exploit published | In Apache Log4j 2.x before 2.8.2, when using the TCP socket server or UDP socket server to receive serialized log events from another application, a specially crafted binary payload can be sent that, when deserialized, can execute arbitrary code. |
| CVE-2015-8965 | Critical | 2017-04-06 | No exploit published | No public exploit | Rogue Wave JViews before 8.8 patch 21 and 8.9 before patch 1 allows remote attackers to execute arbitrary Java code that exists in the classpath, such as test code or administration code. The issue exists because the ilog.views.faces.IlvFacesController servlet in jviews-framework-all.jar does not require explicit configuration of servlets that can be called. |
| CVE-2016-1000031 | Critical | 2016-10-25 | Protected by Waratek | No public exploit | Apache Commons FileUpload before 1.3.3 DiskFileItem File Manipulation Remote Code Execution |
| CVE-2016-1181 | High | 2016-07-04 | Protected by Waratek | No public exploit | ActionServlet.java in Apache Struts 1 1.x through 1.3.10 mishandles multithreaded access to an ActionForm instance, which allows remote attackers to execute arbitrary code or cause a denial of service (unexpected memory access) via a multipart request, a related issue to CVE-2015-0899. |