
Oracle Critical Patch Update October 2018
Released October 2018 · Oracle's advisory ↗ · ← Critical Patch Update, July 2018 · Critical Patch Update, January 2019 →
226 CVEs in this release, one square each
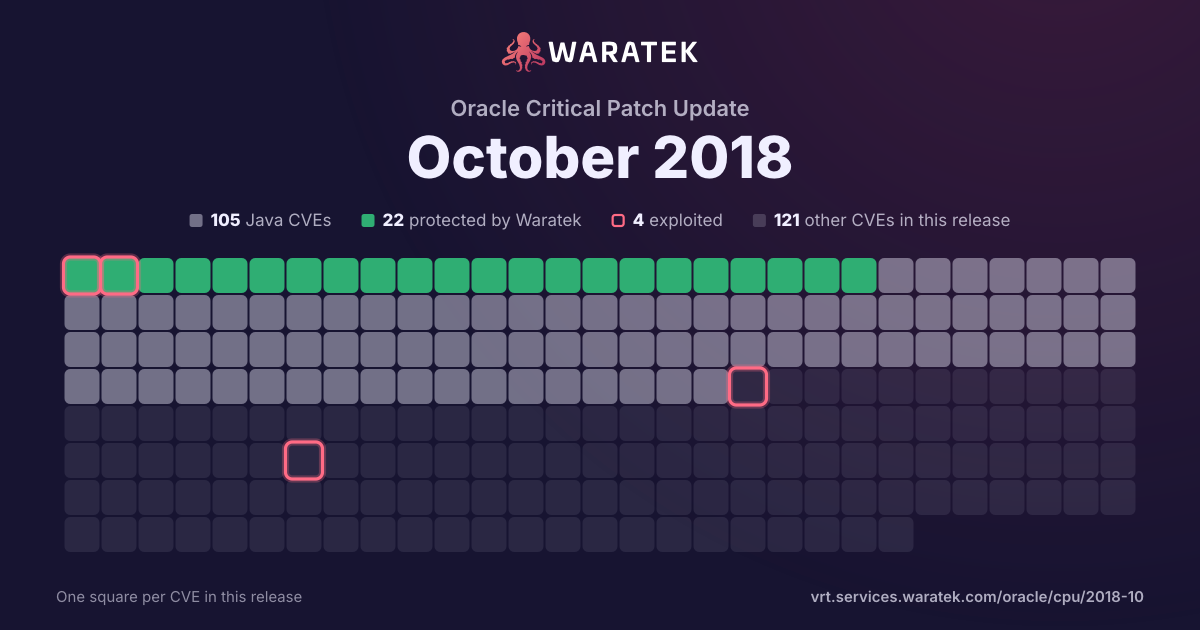
By status
22Protected by Waratek2Mitigation candidate81No exploit published46Outside Waratek scope75Not applicable
4Exploited, marked by the ring
No exploit published. For 81 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 6 matches · 2 in Waratek scope · 2 protected · 1 exploited · 0 CISA KEV · 2 public PoC · 2 EPSS ≥ 0.5
6matches
2in Waratek scope33.3%
2protected33.3%
1exploited16.7%
0CISA KEV0.0%
2public PoC33.3%
2EPSS ≥ 0.533.3%
Protected by Waratek
2
33.3%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
2
33.3%
Not applicable
2
33.3%
Withdrawn CVE
0
0.0%
blocked by ARMR today
2
33.3%
partly blocked
0
0.0%
not blocked
4
66.7%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
16.7%
Working exploit published
1
16.7%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
4
66.7%
split by
peak 2 / quarter
Q3 141
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Q4 140
Q1 151
Outside Waratek scope1
High1
not blocked1
Working exploit published1
Q2 150
Q3 150
Q4 150
Q1 160
Q2 161
Not applicable1
High1
not blocked1
No public exploit1
Q3 162
Protected by Waratek1
Outside Waratek scope1
High2
blocked by ARMR today1
not blocked1
No public exploit2
Q4 160
Q1 170
Q2 170
Q3 171
Not applicable1
High1
not blocked1
Exploited1
Q3 14Q1 15Q3 15Q1 16Q3 16Q1 17Q3 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2017-9798 | High | 2017-09-18 | Not applicable | Exploited | Apache httpd allows remote attackers to read secret data from process memory if the Limit directive can be set in a user's .htaccess file, or if httpd.conf has certain misconfigurations, aka Optionsbleed. This affects the Apache HTTP Server through 2.2.34 and 2.4.x through 2.4.27. The attacker sends an unauthenticated OPTIONS HTTP request when attempting to read secret data. This is a use-after-free issue and thus secret data is not always sent, and the specific data depends on many factors including configuration. Exploitation with .htaccess can be blocked with a patch to the ap_limit_section function in server/core.c. |
| CVE-2016-0635 | High | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Enterprise Manager Ops Center component in Oracle Enterprise Manager Grid Control 12.1.4, 12.2.2, and 12.3.2; the Oracle Health Sciences Information Manager component in Oracle Health Sciences Applications 1.2.8.3, 2.0.2.3, and 3.0.1.0; the Oracle Healthcare Master Person Index component in Oracle Health Sciences Applications 2.0.12, 3.0.0, and 4.0.1; the Oracle Documaker component in Oracle Insurance Applications before 12.5; the Oracle Insurance Calculation Engine component in Oracle Insurance Applications 9.7.1, 10.1.2, and 10.2.2; the Oracle Insurance Policy Administration J2EE and Oracle Insurance Rules Palette components in Oracle Insurance Applications 9.6.1, 9.7.1, 10.0.1, 10.1.2, 10.2.0, and 10.2.2; the Oracle Retail Integration Bus component in Oracle Retail Applications 15.0; the Oracle Retail Order Broker component in Oracle Retail Applications 5.1, 5.2, and 15.0; the Primavera Contract Management component in Oracle Primavera Products Suite 14.2; the Primavera P6 Enterprise Project Portfolio Management component in Oracle Primavera Products Suite 8.2, 8.3, 8.4, 15.1, 15.2, and 16.1; the Oracle Financial Services Analytical Applications Infrastructure component in Oracle Financial Services Applications 8.0.0, 8.0.1, 8.0.2, and 8.0.3; the Oracle Commerce Guided Search / Oracle Commerce Experience Manager component in Oracle Commerce 3.1.1, 3.1.2, 11.0, 11.1, and 11.2; the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5; the Oracle Communications BRM - Elastic Charging Engine 11.2.0.0.0 and 11.3.0.0.0; the Oracle Enterprise Repository Enterprise Repository 12.1.3.0.0; the Oracle Financial Services Behavior Detection Platform 8.0.1 and 8.0.2; the Oracle Hyperion Essbase 12.2.1.1; the Oracle Tuxedo System and Applications Monitor (TSAM) 11.1.1.2.0, 11.1.1.2.1, 11.1.1.2.1, 12.1.1.1.0, 12.1.3.0.0, and 12.2.2.0.0; the Oracle Communications WebRTC Session Controller component of Oracle Communications Applications (subcomponent: Security (Spring)) 7.0, 7.1 and 7.2; the Oracle Endeca Information Discovery Integrator 3.2; the Converged Commerce component of Oracle Retail Applications 16.0.1; the Oracle Identity Manager 11.1.2.3.0; Oracle Enterprise Manager for MySQL Database 12.1.0.4; Oracle Retail Invoice Matching 12.0, 13.0, 13.1, 13.2, 14.0, and 14.1; Oracle Communications Performance Intelligence Center (PIC) Software Prior to 10.2.1 and the Oracle Knowledge component of Oracle Siebel CRM (subcomponent: AnswerFlow (Spring Framework)) version 8.5.1.0 - 8.5.1.7 and 8.6.0 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-1182 | High | 2016-07-04 | Protected by Waratek | No public exploit | ActionServlet.java in Apache Struts 1 1.x through 1.3.10 does not properly restrict the Validator configuration, which allows remote attackers to conduct cross-site scripting (XSS) attacks or cause a denial of service via crafted input, a related issue to CVE-2015-0899. |
| CVE-2016-5244 | High | 2016-06-27 | Not applicable | No public exploit | The rds_inc_info_copy function in net/rds/recv.c in the Linux kernel through 4.6.3 does not initialize a certain structure member, which allows remote attackers to obtain sensitive information from kernel stack memory by reading an RDS message. |
| CVE-2015-0235 | High | 2015-01-28 | Outside Waratek scope | Working exploit published | Heap-based buffer overflow in the __nss_hostname_digits_dots function in glibc 2.2, and other 2.x versions before 2.18, allows context-dependent attackers to execute arbitrary code via vectors related to the (1) gethostbyname or (2) gethostbyname2 function, aka "GHOST." |
| CVE-2014-3490 | High | 2014-08-19 | Protected by Waratek | No public exploit | RESTEasy 2.3.1 before 2.3.8.SP2 and 3.x before 3.0.9, as used in Red Hat JBoss Enterprise Application Platform (EAP) 6.3.0, does not disable external entities when the resteasy.document.expand.entity.references parameter is set to false, which allows remote attackers to read arbitrary files and have other unspecified impact via unspecified vectors, related to an XML External Entity (XXE) issue. NOTE: this vulnerability exists because of an incomplete fix for CVE-2012-0818. |