
Oracle Critical Patch Update October 2018
Released October 2018 · Oracle's advisory ↗ · ← Critical Patch Update, July 2018 · Critical Patch Update, January 2019 →
226 CVEs in this release, one square each
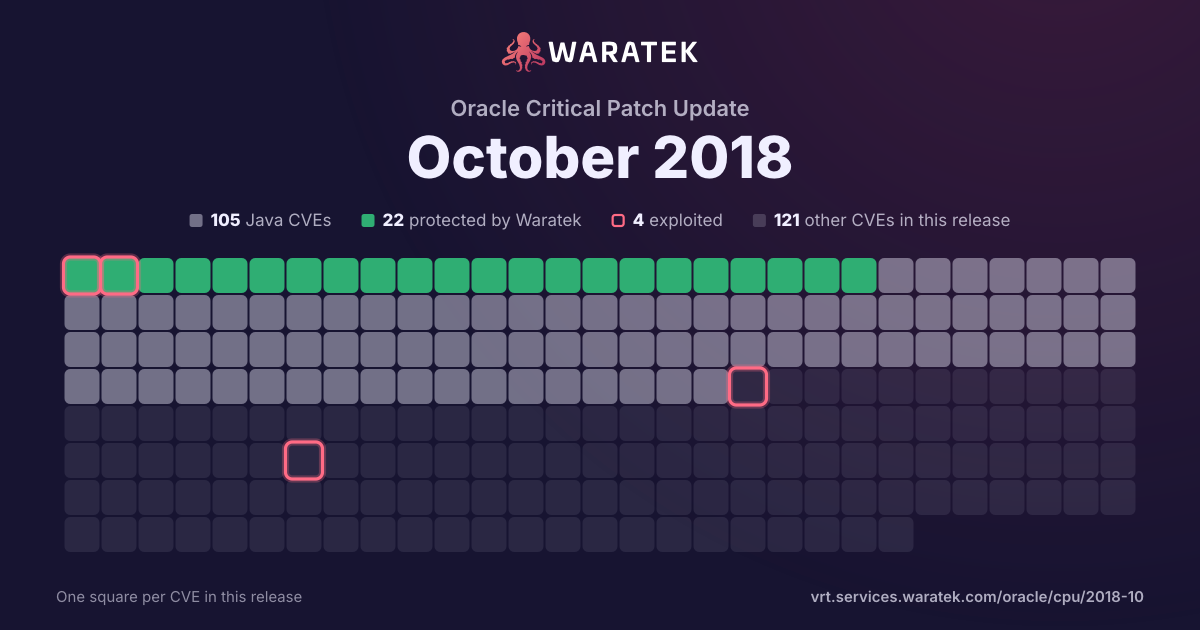
By status
22Protected by Waratek2Mitigation candidate81No exploit published46Outside Waratek scope75Not applicable
4Exploited, marked by the ring
No exploit published. For 81 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 10 matches · 5 in Waratek scope · 5 protected · 1 exploited · 0 CISA KEV · 2 public PoC · 2 EPSS ≥ 0.5
10matches
5in Waratek scope50.0%
5protected50.0%
1exploited10.0%
0CISA KEV0.0%
2public PoC20.0%
2EPSS ≥ 0.520.0%
Protected by Waratek
5
50.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
1
10.0%
Not applicable
4
40.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
5
50.0%
partly blocked
0
0.0%
not blocked
5
50.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
10.0%
Working exploit published
1
10.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
8
80.0%
split by
peak 3 / quarter
Q2 161
Not applicable1
Critical1
not blocked1
No public exploit1
Q3 161
Not applicable1
Critical1
not blocked1
No public exploit1
Q4 163
Protected by Waratek2
Not applicable1
Critical3
blocked by ARMR today2
not blocked1
No public exploit3
Q1 170
Q2 172
Protected by Waratek1
Outside Waratek scope1
Critical2
blocked by ARMR today1
not blocked1
Working exploit published1
No public exploit1
Q3 171
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Q4 172
Protected by Waratek1
Not applicable1
Critical2
blocked by ARMR today1
not blocked1
Exploited1
No public exploit1
Q2 16Q3 16Q4 16Q1 17Q2 17Q3 17Q4 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2017-5533 | Critical | 2017-11-15 | Not applicable | No public exploit | A vulnerability in the server content cache of TIBCO JasperReports Server, TIBCO JasperReports Server Community Edition, TIBCO JasperReports Server for ActiveMatrix BPM, TIBCO Jaspersoft for AWS with Multi-Tenancy, and TIBCO Jaspersoft Reporting and Analytics for AWS contains a vulnerability which fails to prevent remote access to all the contents of the web application, including key configuration files. Affected releases are TIBCO JasperReports Server 6.4.0, TIBCO JasperReports Server Community Edition 6.4.0, TIBCO JasperReports Server for ActiveMatrix BPM 6.4.0, TIBCO Jaspersoft for AWS with Multi-Tenancy 6.4.0, TIBCO Jaspersoft Reporting and Analytics for AWS 6.4.0. |
| CVE-2015-7501 | Critical | 2017-11-09 | Protected by Waratek | Exploited | Red Hat JBoss A-MQ 6.x; BPM Suite (BPMS) 6.x; BRMS 6.x and 5.x; Data Grid (JDG) 6.x; Data Virtualization (JDV) 6.x and 5.x; Enterprise Application Platform 6.x, 5.x, and 4.3.x; Fuse 6.x; Fuse Service Works (FSW) 6.x; Operations Network (JBoss ON) 3.x; Portal 6.x; SOA Platform (SOA-P) 5.x; Web Server (JWS) 3.x; Red Hat OpenShift/xPAAS 3.x; and Red Hat Subscription Asset Manager 1.3 allow remote attackers to execute arbitrary commands via a crafted serialized Java object, related to the Apache Commons Collections (ACC) library. |
| CVE-2016-4000 | Critical | 2017-07-06 | Protected by Waratek | No public exploit | Jython before 2.7.1rc1 allows attackers to execute arbitrary code via a crafted serialized PyFunction object. |
| CVE-2016-9843 | Critical | 2017-05-23 | Outside Waratek scope | No public exploit | The crc32_big function in crc32.c in zlib 1.2.8 might allow context-dependent attackers to have unspecified impact via vectors involving big-endian CRC calculation. |
| CVE-2017-5645 | Critical | 2017-04-17 | Protected by Waratek | Working exploit published | In Apache Log4j 2.x before 2.8.2, when using the TCP socket server or UDP socket server to receive serialized log events from another application, a specially crafted binary payload can be sent that, when deserialized, can execute arbitrary code. |
| CVE-2016-1000031 | Critical | 2016-10-25 | Protected by Waratek | No public exploit | Apache Commons FileUpload before 1.3.3 DiskFileItem File Manipulation Remote Code Execution |
| CVE-2016-7167 | Critical | 2016-10-07 | Not applicable | No public exploit | Multiple integer overflows in the (1) curl_escape, (2) curl_easy_escape, (3) curl_unescape, and (4) curl_easy_unescape functions in libcurl before 7.50.3 allow attackers to have unspecified impact via a string of length 0xffffffff, which triggers a heap-based buffer overflow. |
| CVE-2016-5019 | Critical | 2016-10-03 | Protected by Waratek | No public exploit | CoreResponseStateManager in Apache MyFaces Trinidad 1.0.0 through 1.0.13, 1.2.x before 1.2.15, 2.0.x before 2.0.2, and 2.1.x before 2.1.2 might allow attackers to conduct deserialization attacks via a crafted serialized view state string. |
| CVE-2016-5080 | Critical | 2016-07-19 | Not applicable | No public exploit | Integer overflow in the rtxMemHeapAlloc function in asn1rt_a.lib in Objective Systems ASN1C for C/C++ before 7.0.2 allows context-dependent attackers to execute arbitrary code or cause a denial of service (heap-based buffer overflow), on a system running an application compiled by ASN1C, via crafted ASN.1 data. |
| CVE-2016-0729 | Critical | 2016-04-07 | Not applicable | No public exploit | Multiple buffer overflows in (1) internal/XMLReader.cpp, (2) util/XMLURL.cpp, and (3) util/XMLUri.cpp in the XML Parser library in Apache Xerces-C before 3.1.3 allow remote attackers to cause a denial of service (segmentation fault or memory corruption) or possibly execute arbitrary code via a crafted document. |