
Oracle Critical Patch Update July 2017
Released July 2017 · Oracle's advisory ↗ · ← Critical Patch Update, April 2017 · Critical Patch Update, October 2017 →
272 CVEs in this release, one square each
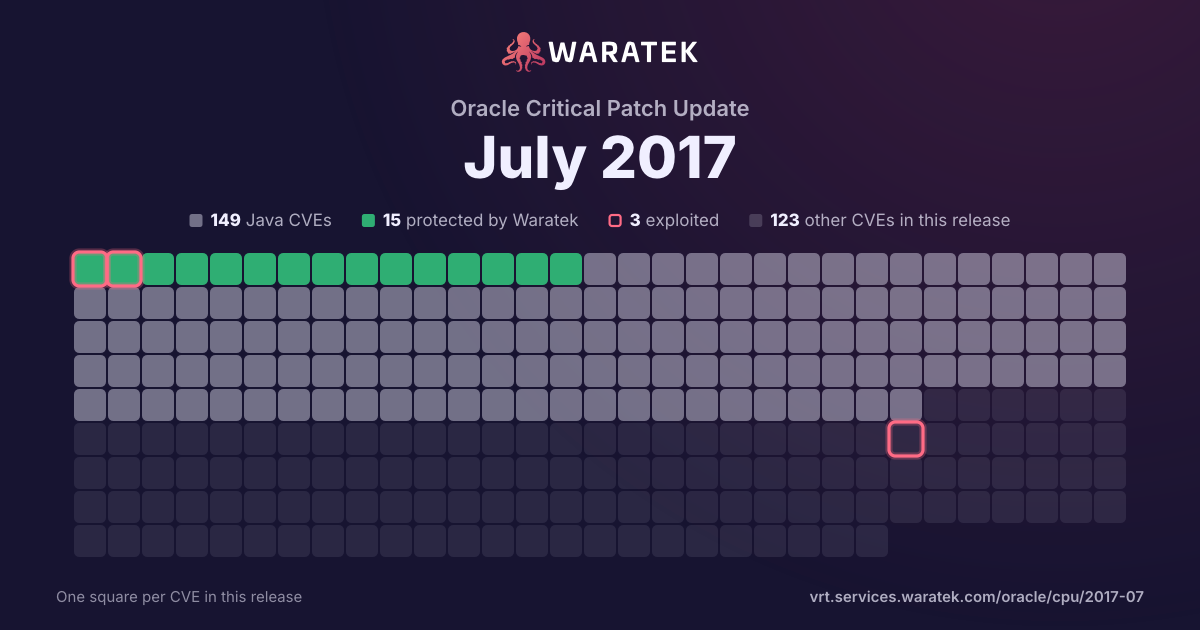
By status
15Protected by Waratek3Mitigation candidate131No exploit published30Outside Waratek scope93Not applicable
3Exploited, marked by the ring
No exploit published. For 126 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 7 matches · 5 in Waratek scope · 3 protected · 2 exploited · 2 CISA KEV · 3 public PoC · 2 EPSS ≥ 0.5
7matches
5in Waratek scope71.4%
3protected42.9%
2exploited28.6%
2CISA KEV28.6%
3public PoC42.9%
2EPSS ≥ 0.528.6%
Protected by Waratek
3
42.9%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
2
28.6%
Outside Waratek scope
1
14.3%
Not applicable
1
14.3%
Withdrawn CVE
0
0.0%
blocked by ARMR today
3
42.9%
partly blocked
0
0.0%
not blocked
4
57.1%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
2
28.6%
Working exploit published
0
0.0%
Proof of concept only
1
14.3%
Forecast only
0
0.0%
No public exploit
4
57.1%
split by
peak 2 / quarter
Q3 151
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
Q4 150
Q1 161
Protected by Waratek1
Critical1
blocked by ARMR today1
Proof of concept only1
Q2 160
Q3 160
Q4 162
Protected by Waratek1
No exploit published1
Critical2
blocked by ARMR today1
not blocked1
No public exploit2
Q1 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q2 172
No exploit published1
Not applicable1
Critical2
not blocked2
Exploited1
No public exploit1
Q3 15Q4 15Q1 16Q2 16Q3 16Q4 16Q1 17Q2 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2017-5689 | Critical | 2017-05-02 | Not applicable | Exploited | An unprivileged network attacker could gain system privileges to provisioned Intel manageability SKUs: Intel Active Management Technology (AMT) and Intel Standard Manageability (ISM). An unprivileged local attacker could provision manageability features gaining unprivileged network or local system privileges on Intel manageability SKUs: Intel Active Management Technology (AMT), Intel Standard Manageability (ISM), and Intel Small Business Technology (SBT). |
| CVE-2017-5651 | Critical | 2017-04-17 | No exploit published | No public exploit | In Apache Tomcat 9.0.0.M1 to 9.0.0.M18 and 8.5.0 to 8.5.12, the refactoring of the HTTP connectors introduced a regression in the send file processing. If the send file processing completed quickly, it was possible for the Processor to be added to the processor cache twice. This could result in the same Processor being used for multiple requests which in turn could lead to unexpected errors and/or response mix-up. |
| CVE-2017-5638 | Critical | 2017-03-11 | Protected by Waratek | Exploited | The Jakarta Multipart parser in Apache Struts 2 2.3.x before 2.3.32 and 2.5.x before 2.5.10.1 has incorrect exception handling and error-message generation during file-upload attempts, which allows remote attackers to execute arbitrary commands via a crafted Content-Type, Content-Disposition, or Content-Length HTTP header, as exploited in the wild in March 2017 with a Content-Type header containing a #cmd= string. |
| CVE-2016-5019 | Critical | 2016-10-03 | Protected by Waratek | No public exploit | CoreResponseStateManager in Apache MyFaces Trinidad 1.0.0 through 1.0.13, 1.2.x before 1.2.15, 2.0.x before 2.0.2, and 2.1.x before 2.1.2 might allow attackers to conduct deserialization attacks via a crafted serialized view state string. |
| CVE-2016-4436 | Critical | 2016-10-03 | No exploit published | No public exploit | Apache Struts 2 before 2.3.29 and 2.5.x before 2.5.1 allow attackers to have unspecified impact via vectors related to improper action name clean up. |
| CVE-2015-5254 | Critical | 2016-01-08 | Protected by Waratek | Proof of concept only | Apache ActiveMQ 5.x before 5.13.0 does not restrict the classes that can be serialized in the broker, which allows remote attackers to execute arbitrary code via a crafted serialized Java Message Service (JMS) ObjectMessage object. |
| CVE-2015-3253 | Critical | 2015-08-13 | Outside Waratek scope | No public exploit | The MethodClosure class in runtime/MethodClosure.java in Apache Groovy 1.7.0 through 2.4.3 allows remote attackers to execute arbitrary code or cause a denial of service via a crafted serialized object. |