
Oracle Critical Patch Update April 2017
Released April 2017 · Oracle's advisory ↗ · ← Critical Patch Update, January 2017 · Critical Patch Update, July 2017 →
227 CVEs in this release, one square each
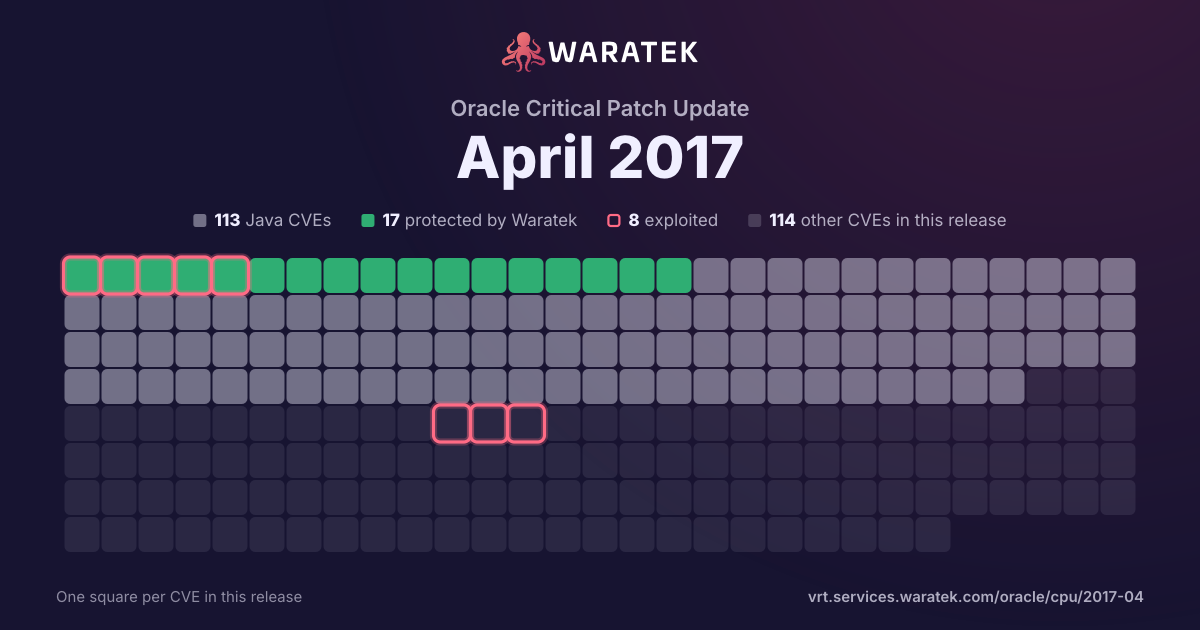
By status
17Protected by Waratek1Mitigation candidate95No exploit published13Outside Waratek scope101Not applicable
8Exploited, marked by the ring
No exploit published. For 93 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 5 matches · 1 in Waratek scope · 1 protected · 2 exploited · 1 CISA KEV · 2 public PoC · 2 EPSS ≥ 0.5
5matches
1in Waratek scope20.0%
1protected20.0%
2exploited40.0%
1CISA KEV20.0%
2public PoC40.0%
2EPSS ≥ 0.540.0%
Protected by Waratek
1
20.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
1
20.0%
Not applicable
3
60.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
20.0%
partly blocked
0
0.0%
not blocked
4
80.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
2
40.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
3
60.0%
split by
peak 2 / month
Jan 151
Not applicable1
Medium1
not blocked1
Exploited1
Feb 150
Mar 150
Apr 150
May 150
Jun 151
Not applicable1
Medium1
not blocked1
No public exploit1
Jul 150
Aug 150
Sep 150
Oct 150
Nov 152
Protected by Waratek1
Outside Waratek scope1
Critical1
Medium1
blocked by ARMR today1
not blocked1
Exploited1
No public exploit1
Dec 151
Not applicable1
High1
not blocked1
No public exploit1
Jan 15Feb 15Mar 15Apr 15May 15Jun 15Jul 15Aug 15Sep 15Oct 15Nov 15Dec 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-5252 | High | 2015-12-29 | Not applicable | No public exploit | vfs.c in smbd in Samba 3.x and 4.x before 4.1.22, 4.2.x before 4.2.7, and 4.3.x before 4.3.3, when share names with certain substring relationships exist, allows remote attackers to bypass intended file-access restrictions via a symlink that points outside of a share. |
| CVE-2015-4852 | Critical | 2015-11-18 | Protected by Waratek | Exploited | The WLS Security component in Oracle WebLogic Server 10.3.6.0, 12.1.2.0, 12.1.3.0, and 12.2.1.0 allows remote attackers to execute arbitrary commands via a crafted serialized Java object in T3 protocol traffic to TCP port 7001, related to oracle_common/modules/com.bea.core.apache.commons.collections.jar. NOTE: the scope of this CVE is limited to the WebLogic Server product. |
| CVE-2015-7940 | Medium | 2015-11-09 | Outside Waratek scope | No public exploit | The Bouncy Castle Java library before 1.51 does not validate a point is withing the elliptic curve, which makes it easier for remote attackers to obtain private keys via a series of crafted elliptic curve Diffie Hellman (ECDH) key exchanges, aka an "invalid curve attack." |
| CVE-2015-3237 | Medium | 2015-06-22 | Not applicable | No public exploit | The smb_request_state function in cURL and libcurl 7.40.0 through 7.42.1 allows remote SMB servers to obtain sensitive information from memory or cause a denial of service (out-of-bounds read and crash) via crafted length and offset values. |
| CVE-2015-0204 | Medium | 2015-01-09 | Not applicable | Exploited | The ssl3_get_key_exchange function in s3_clnt.c in OpenSSL before 0.9.8zd, 1.0.0 before 1.0.0p, and 1.0.1 before 1.0.1k allows remote SSL servers to conduct RSA-to-EXPORT_RSA downgrade attacks and facilitate brute-force decryption by offering a weak ephemeral RSA key in a noncompliant role, related to the "FREAK" issue. NOTE: the scope of this CVE is only client code based on OpenSSL, not EXPORT_RSA issues associated with servers or other TLS implementations. |