
Oracle Critical Patch Update April 2017
Released April 2017 · Oracle's advisory ↗ · ← Critical Patch Update, January 2017 · Critical Patch Update, July 2017 →
227 CVEs in this release, one square each
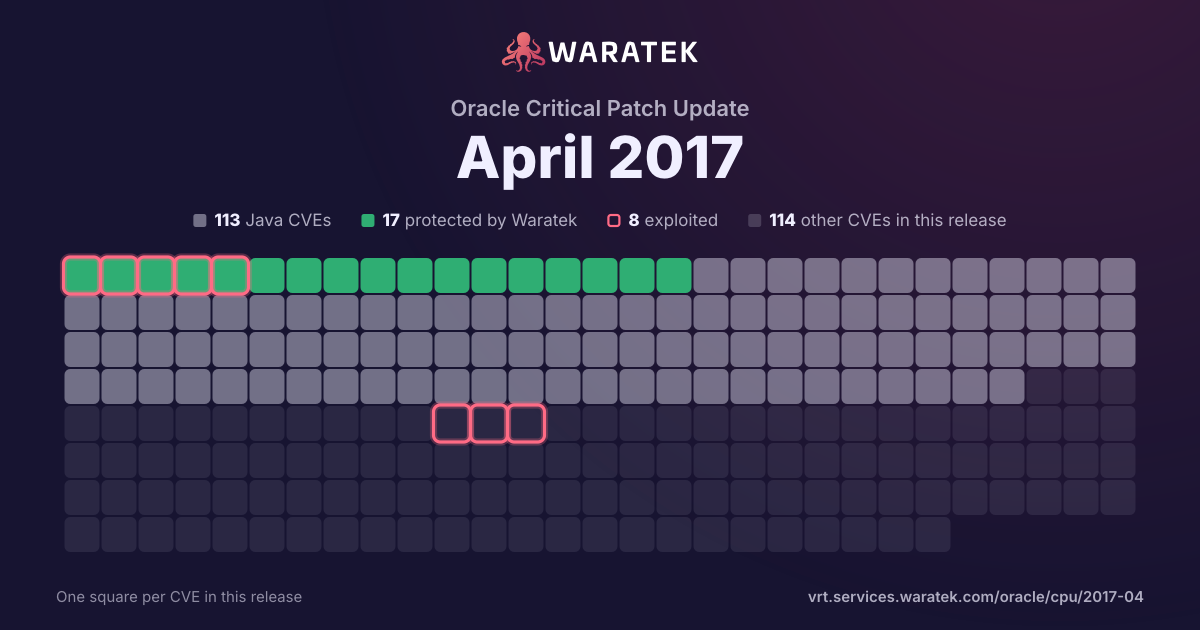
By status
17Protected by Waratek1Mitigation candidate95No exploit published13Outside Waratek scope101Not applicable
8Exploited, marked by the ring
No exploit published. For 93 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 13 matches · 2 in Waratek scope · 1 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
13matches
2in Waratek scope15.4%
1protected7.7%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
1
7.7%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
1
7.7%
Outside Waratek scope
2
15.4%
Not applicable
9
69.2%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
7.7%
partly blocked
0
0.0%
not blocked
12
92.3%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
13
100.0%
split by
peak 4 / quarter
Q2 121
Not applicable1
High1
not blocked1
No public exploit1
Q3 120
Q4 121
Not applicable1
Medium1
not blocked1
No public exploit1
Q1 130
Q2 131
Not applicable1
Medium1
not blocked1
No public exploit1
Q3 131
Not applicable1
High1
not blocked1
No public exploit1
Q4 130
Q1 140
Q2 140
Q3 141
No exploit published1
Medium1
not blocked1
No public exploit1
Q4 140
Q1 150
Q2 151
Not applicable1
Medium1
not blocked1
No public exploit1
Q3 150
Q4 152
Outside Waratek scope1
Not applicable1
High1
Medium1
not blocked2
No public exploit2
Q1 161
Outside Waratek scope1
High1
not blocked1
No public exploit1
Q2 164
Protected by Waratek1
Not applicable3
Critical1
High2
Medium1
blocked by ARMR today1
not blocked3
No public exploit4
Q2 12Q4 12Q2 13Q4 13Q2 14Q4 14Q2 15Q4 15Q2 16
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-3739 | Medium | 2016-05-20 | Not applicable | No public exploit | The (1) mbed_connect_step1 function in lib/vtls/mbedtls.c and (2) polarssl_connect_step1 function in lib/vtls/polarssl.c in cURL and libcurl before 7.49.0, when using SSLv3 or making a TLS connection to a URL that uses a numerical IP address, allow remote attackers to spoof servers via an arbitrary valid certificate. |
| CVE-2016-3674 | High | 2016-05-17 | Protected by Waratek | No public exploit | Multiple XML external entity (XXE) vulnerabilities in the (1) Dom4JDriver, (2) DomDriver, (3) JDomDriver, (4) JDom2Driver, (5) SjsxpDriver, (6) StandardStaxDriver, and (7) WstxDriver drivers in XStream before 1.4.9 allow remote attackers to read arbitrary files via a crafted XML document. |
| CVE-2016-2176 | High | 2016-05-05 | Not applicable | No public exploit | The X509_NAME_oneline function in crypto/x509/x509_obj.c in OpenSSL before 1.0.1t and 1.0.2 before 1.0.2h allows remote attackers to obtain sensitive information from process stack memory or cause a denial of service (buffer over-read) via crafted EBCDIC ASN.1 data. |
| CVE-2016-0729 | Critical | 2016-04-07 | Not applicable | No public exploit | Multiple buffer overflows in (1) internal/XMLReader.cpp, (2) util/XMLURL.cpp, and (3) util/XMLUri.cpp in the XML Parser library in Apache Xerces-C before 3.1.3 allow remote attackers to cause a denial of service (segmentation fault or memory corruption) or possibly execute arbitrary code via a crafted document. |
| CVE-2016-0714 | High | 2016-02-25 | Outside Waratek scope | No public exploit | The session-persistence implementation in Apache Tomcat 6.x before 6.0.45, 7.x before 7.0.68, 8.x before 8.0.31, and 9.x before 9.0.0.M2 mishandles session attributes, which allows remote authenticated users to bypass intended SecurityManager restrictions and execute arbitrary code in a privileged context via a web application that places a crafted object in a session. |
| CVE-2015-5252 | High | 2015-12-29 | Not applicable | No public exploit | vfs.c in smbd in Samba 3.x and 4.x before 4.1.22, 4.2.x before 4.2.7, and 4.3.x before 4.3.3, when share names with certain substring relationships exist, allows remote attackers to bypass intended file-access restrictions via a symlink that points outside of a share. |
| CVE-2015-7940 | Medium | 2015-11-09 | Outside Waratek scope | No public exploit | The Bouncy Castle Java library before 1.51 does not validate a point is withing the elliptic curve, which makes it easier for remote attackers to obtain private keys via a series of crafted elliptic curve Diffie Hellman (ECDH) key exchanges, aka an "invalid curve attack." |
| CVE-2015-3237 | Medium | 2015-06-22 | Not applicable | No public exploit | The smb_request_state function in cURL and libcurl 7.40.0 through 7.42.1 allows remote SMB servers to obtain sensitive information from memory or cause a denial of service (out-of-bounds read and crash) via crafted length and offset values. |
| CVE-2014-3596 | Medium | 2014-08-27 | No exploit published | No public exploit | The getCN function in Apache Axis 1.4 and earlier does not properly verify that the server hostname matches a domain name in the subject's Common Name (CN) or subjectAltName field of the X.509 certificate, which allows man-in-the-middle attackers to spoof SSL servers via a certificate with a subject that specifies a common name in a field that is not the CN field. NOTE: this issue exists because of an incomplete fix for CVE-2012-5784. |
| CVE-2013-5209 | High | 2013-08-29 | Not applicable | No public exploit | The sctp_send_initiate_ack function in sys/netinet/sctp_output.c in the SCTP implementation in the kernel in FreeBSD 8.3 through 9.2-PRERELEASE does not properly initialize the state-cookie data structure, which allows remote attackers to obtain sensitive information from kernel stack memory by reading packet data in INIT-ACK chunks. |
| CVE-2013-1982 | Medium | 2013-06-15 | Not applicable | No public exploit | Multiple integer overflows in X.org libXext 1.3.1 and earlier allow X servers to trigger allocation of insufficient memory and a buffer overflow via vectors related to the (1) XcupGetReservedColormapEntries, (2) XcupStoreColors, (3) XdbeGetVisualInfo, (4) XeviGetVisualInfo, (5) XShapeGetRectangles, and (6) XSyncListSystemCounters functions. |
| CVE-2012-5881 | Medium | 2012-11-16 | Not applicable | No public exploit | Cross-site scripting (XSS) vulnerability in the Flash component infrastructure in YUI 2.4.0 through 2.9.0 allows remote attackers to inject arbitrary web script or HTML via vectors related to charts.swf, a similar issue to CVE-2010-4207. |
| CVE-2012-0920 | High | 2012-06-05 | Not applicable | No public exploit | Use-after-free vulnerability in Dropbear SSH Server 0.52 through 2012.54, when command restriction and public key authentication are enabled, allows remote authenticated users to execute arbitrary code and bypass command restrictions via multiple crafted command requests, related to "channels concurrency." |