
Oracle Critical Patch Update April 2017
Released April 2017 · Oracle's advisory ↗ · ← Critical Patch Update, January 2017 · Critical Patch Update, July 2017 →
227 CVEs in this release, one square each
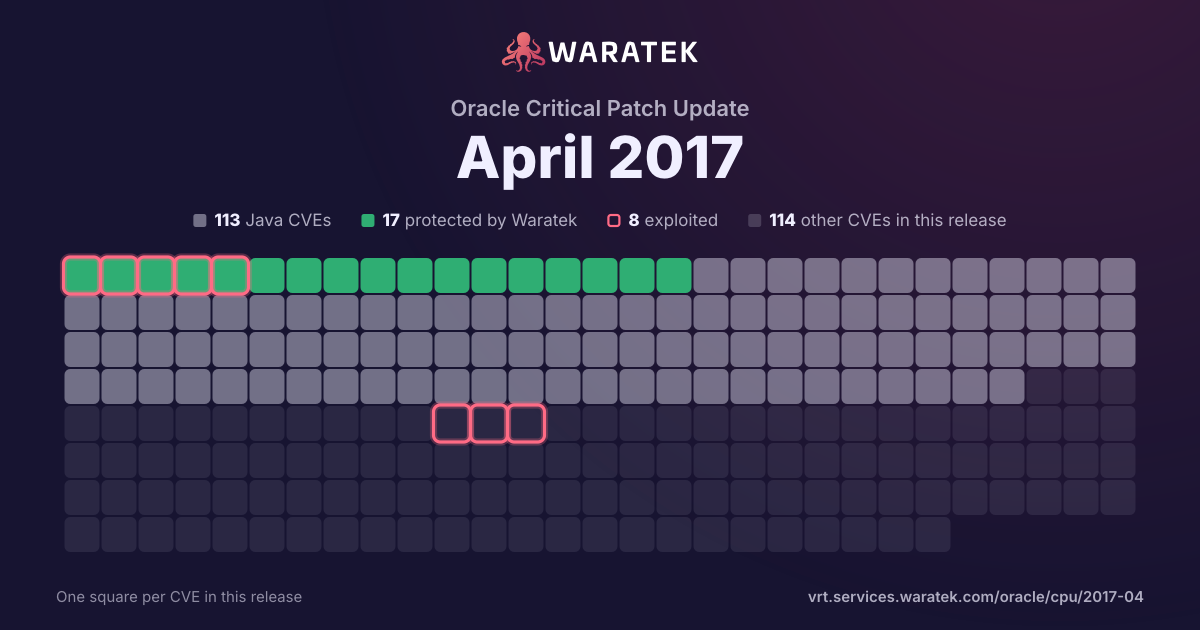
By status
17Protected by Waratek1Mitigation candidate95No exploit published13Outside Waratek scope101Not applicable
8Exploited, marked by the ring
No exploit published. For 93 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 227 matches · 113 in Waratek scope · 17 protected · 8 exploited · 3 CISA KEV · 21 public PoC · 13 EPSS ≥ 0.5
227matches
113in Waratek scope49.8%
17protected7.5%
8exploited3.5%
3CISA KEV1.3%
21public PoC9.3%
13EPSS ≥ 0.55.7%
Protected by Waratek
17
7.5%
Rule in development
0
0.0%
Mitigation candidate
1
0.4%
No exploit published
95
41.9%
Outside Waratek scope
13
5.7%
Not applicable
101
44.5%
Withdrawn CVE
0
0.0%
blocked by ARMR today
17
7.5%
partly blocked
0
0.0%
not blocked
210
92.5%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
8
3.5%
Working exploit published
13
5.7%
Proof of concept only
0
0.0%
Forecast only
4
1.8%
No public exploit
202
89.0%
split by
peak 197 / year
20091
Not applicable1
Critical1
not blocked1
Working exploit published1
20100
20110
20122
Not applicable2
High1
Medium1
not blocked2
No public exploit2
20133
Outside Waratek scope1
Not applicable2
High1
Medium2
not blocked3
Forecast only1
No public exploit2
20142
Protected by Waratek1
No exploit published1
High1
Medium1
blocked by ARMR today1
not blocked1
Exploited1
No public exploit1
20155
Protected by Waratek1
Outside Waratek scope1
Not applicable3
Critical1
High1
Medium3
blocked by ARMR today1
not blocked4
Exploited2
No public exploit3
201617
Protected by Waratek4
No exploit published2
Outside Waratek scope2
Not applicable9
Critical6
High9
Medium2
blocked by ARMR today4
not blocked13
Working exploit published1
Forecast only2
No public exploit14
2017197
Protected by Waratek11
Mitigation candidate1
No exploit published92
Outside Waratek scope9
Not applicable84
Critical9
High86
Medium84
Low18
blocked by ARMR today11
not blocked186
Exploited5
Working exploit published11
Forecast only1
No public exploit180
200920102011201220132014201520162017
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-7501 | Critical | 2017-11-09 | Protected by Waratek | Exploited | Red Hat JBoss A-MQ 6.x; BPM Suite (BPMS) 6.x; BRMS 6.x and 5.x; Data Grid (JDG) 6.x; Data Virtualization (JDV) 6.x and 5.x; Enterprise Application Platform 6.x, 5.x, and 4.3.x; Fuse 6.x; Fuse Service Works (FSW) 6.x; Operations Network (JBoss ON) 3.x; Portal 6.x; SOA Platform (SOA-P) 5.x; Web Server (JWS) 3.x; Red Hat OpenShift/xPAAS 3.x; and Red Hat Subscription Asset Manager 1.3 allow remote attackers to execute arbitrary commands via a crafted serialized Java object, related to the Apache Commons Collections (ACC) library. |
| CVE-2016-0762 | Medium | 2017-08-10 | Outside Waratek scope | No public exploit | The Realm implementations in Apache Tomcat versions 9.0.0.M1 to 9.0.0.M9, 8.5.0 to 8.5.4, 8.0.0.RC1 to 8.0.36, 7.0.0 to 7.0.70 and 6.0.0 to 6.0.45 did not process the supplied password if the supplied user name did not exist. This made a timing attack possible to determine valid user names. Note that the default configuration includes the LockOutRealm which makes exploitation of this vulnerability harder. |
| CVE-2016-8743 | High | 2017-07-27 | Outside Waratek scope | No public exploit | Apache HTTP Server, in all releases prior to 2.2.32 and 2.4.25, was liberal in the whitespace accepted from requests and sent in response lines and headers. Accepting these different behaviors represented a security concern when httpd participates in any chain of proxies or interacts with back-end application servers, either through mod_proxy or using conventional CGI mechanisms, and may result in request smuggling, response splitting and cache pollution. |
| CVE-2017-3732 | Medium | 2017-05-04 | Not applicable | No public exploit | There is a carry propagating bug in the x86_64 Montgomery squaring procedure in OpenSSL 1.0.2 before 1.0.2k and 1.1.0 before 1.1.0d. No EC algorithms are affected. Analysis suggests that attacks against RSA and DSA as a result of this defect would be very difficult to perform and are not believed likely. Attacks against DH are considered just feasible (although very difficult) because most of the work necessary to deduce information about a private key may be performed offline. The amount of resources required for such an attack would be very significant and likely only accessible to a limited number of attackers. An attacker would additionally need online access to an unpatched system using the target private key in a scenario with persistent DH parameters and a private key that is shared between multiple clients. For example this can occur by default in OpenSSL DHE based SSL/TLS ciphersuites. Note: This issue is very similar to CVE-2015-3193 but must be treated as a separate problem. |
| CVE-2017-3731 | High | 2017-05-04 | Not applicable | Forecast only | If an SSL/TLS server or client is running on a 32-bit host, and a specific cipher is being used, then a truncated packet can cause that server or client to perform an out-of-bounds read, usually resulting in a crash. For OpenSSL 1.1.0, the crash can be triggered when using CHACHA20/POLY1305; users should upgrade to 1.1.0d. For Openssl 1.0.2, the crash can be triggered when using RC4-MD5; users who have not disabled that algorithm should update to 1.0.2k. |
| CVE-2017-3626 | Low | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle GlassFish Server component of Oracle Fusion Middleware (subcomponent: Java Server Faces). The supported version that is affected is 3.1.2. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Oracle GlassFish Server. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle GlassFish Server accessible data. CVSS 3.0 Base Score 3.1 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:R/S:U/C:L/I:N/A:N). |
| CVE-2017-3625 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Content component of Oracle Fusion Middleware (subcomponent: Content Server). Supported versions that are affected are 11.1.1.7, 11.1.1.9, 12.2.1.0, 12.2.1.1 and 12.2.1.2. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebCenter Content. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle WebCenter Content, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle WebCenter Content accessible data as well as unauthorized update, insert or delete access to some of Oracle WebCenter Content accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-3623 | Critical | 2017-04-24 | Not applicable | Exploited | Vulnerability in the Solaris component of Oracle Sun Systems Products Suite (subcomponent: Kernel RPC). For supported versions that are affected see note. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Solaris. While the vulnerability is in Solaris, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Solaris. Note: CVE-2017-3623 is assigned for "Ebbisland". Solaris 10 systems which have had any Kernel patch installed after, or updated via patching tools since 2012-01-26 are not impacted. Also, any Solaris 10 system installed with Solaris 10 1/13 (Solaris 10 Update 11) are not vulnerable. Solaris 11 is not impacted by this issue. CVSS 3.0 Base Score 10.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2017-3622 | High | 2017-04-24 | Not applicable | Exploited | Vulnerability in the Solaris component of Oracle Sun Systems Products Suite (subcomponent: Common Desktop Environment (CDE)). The supported version that is affected is 10. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Solaris executes to compromise Solaris. Successful attacks of this vulnerability can result in takeover of Solaris. Note: CVE-2017-3622 is assigned for the "Extremeparr". CVSS 3.0 Base Score 7.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2017-3621 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Sun ZFS Storage Appliance Kit (AK) component of Oracle Sun Systems Products Suite (subcomponent: IPC Frameworks). The supported version that is affected is AK 2013. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Sun ZFS Storage Appliance Kit (AK). Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Sun ZFS Storage Appliance Kit (AK). CVSS 3.0 Base Score 7.5 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3620 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Automatic Service Request (ASR) component of Oracle Support Tools (subcomponent: ASR Manager). The supported version that is affected is Prior to 5.7. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Automatic Service Request (ASR) executes to compromise Automatic Service Request (ASR). Successful attacks of this vulnerability can result in takeover of Automatic Service Request (ASR). CVSS 3.0 Base Score 7.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2017-3619 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Automatic Service Request (ASR) component of Oracle Support Tools (subcomponent: ASR Manager). The supported version that is affected is Prior to 5.7. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Automatic Service Request (ASR) executes to compromise Automatic Service Request (ASR). Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Automatic Service Request (ASR) accessible data. CVSS 3.0 Base Score 5.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-3618 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Automatic Service Request (ASR) component of Oracle Support Tools (subcomponent: ASR Manager). The supported version that is affected is Prior to 5.7. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Automatic Service Request (ASR) executes to compromise Automatic Service Request (ASR). Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Automatic Service Request (ASR) accessible data as well as unauthorized access to critical data or complete access to all Automatic Service Request (ASR) accessible data. CVSS 3.0 Base Score 7.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-3617 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Data Store component of Oracle Berkeley DB. The supported version that is affected is Prior to 6.2.32. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Data Store executes to compromise Data Store. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Data Store. CVSS 3.0 Base Score 7.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2017-3616 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Data Store component of Oracle Berkeley DB. The supported version that is affected is Prior to 6.2.32. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Data Store executes to compromise Data Store. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Data Store. CVSS 3.0 Base Score 7.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2017-3615 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Data Store component of Oracle Berkeley DB. The supported version that is affected is Prior to 6.2.32. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Data Store executes to compromise Data Store. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Data Store. CVSS 3.0 Base Score 7.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2017-3614 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Data Store component of Oracle Berkeley DB. The supported version that is affected is Prior to 6.2.32. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Data Store executes to compromise Data Store. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Data Store. CVSS 3.0 Base Score 7.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2017-3613 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Data Store component of Oracle Berkeley DB. The supported version that is affected is Prior to 6.2.32. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Data Store executes to compromise Data Store. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Data Store. CVSS 3.0 Base Score 7.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2017-3612 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Data Store component of Oracle Berkeley DB. The supported version that is affected is Prior to 6.2.32. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Data Store executes to compromise Data Store. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Data Store. CVSS 3.0 Base Score 7.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2017-3611 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Data Store component of Oracle Berkeley DB. The supported version that is affected is Prior to 6.2.32. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Data Store executes to compromise Data Store. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Data Store. CVSS 3.0 Base Score 7.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2017-3610 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Data Store component of Oracle Berkeley DB. The supported version that is affected is Prior to 6.2.32. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Data Store executes to compromise Data Store. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Data Store. CVSS 3.0 Base Score 7.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2017-3609 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Data Store component of Oracle Berkeley DB. The supported version that is affected is Prior to 6.2.32. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Data Store executes to compromise Data Store. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Data Store. CVSS 3.0 Base Score 7.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2017-3608 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Data Store component of Oracle Berkeley DB. The supported version that is affected is Prior to 6.2.32. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Data Store executes to compromise Data Store. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Data Store. CVSS 3.0 Base Score 7.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2017-3607 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Data Store component of Oracle Berkeley DB. The supported version that is affected is Prior to 6.2.32. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Data Store executes to compromise Data Store. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Data Store. CVSS 3.0 Base Score 7.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2017-3606 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Data Store component of Oracle Berkeley DB. The supported version that is affected is Prior to 6.2.32. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Data Store executes to compromise Data Store. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Data Store. CVSS 3.0 Base Score 7.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2017-3605 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Data Store component of Oracle Berkeley DB. The supported version that is affected is Prior to 6.2.32. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Data Store executes to compromise Data Store. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Data Store. CVSS 3.0 Base Score 7.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2017-3604 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Data Store component of Oracle Berkeley DB. The supported version that is affected is Prior to 6.2.32. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Data Store executes to compromise Data Store. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Data Store. CVSS 3.0 Base Score 7.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2017-3603 | Low | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Sites component of Oracle Fusion Middleware (subcomponent: Advanced UI). Supported versions that are affected are 11.1.1.8.0, 12.2.1.0.0, 12.2.1.1.0 and 12.2.1.2.0. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle WebCenter Sites. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle WebCenter Sites accessible data. CVSS 3.0 Base Score 3.1 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-3602 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Sites component of Oracle Fusion Middleware (subcomponent: Advanced UI). Supported versions that are affected are 11.1.1.8.0, 12.2.1.0.0, 12.2.1.1.0 and 12.2.1.2.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle WebCenter Sites. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle WebCenter Sites accessible data as well as unauthorized access to critical data or complete access to all Oracle WebCenter Sites accessible data. CVSS 3.0 Base Score 8.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-3601 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle API Gateway component of Oracle Fusion Middleware (subcomponent: Oracle API Gateway). The supported version that is affected is 11.1.2.4.0. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle API Gateway. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle API Gateway accessible data as well as unauthorized access to critical data or complete access to all Oracle API Gateway accessible data. CVSS 3.0 Base Score 8.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:H/A:N). |
| CVE-2017-3600 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Client mysqldump). Supported versions that are affected are 5.5.54 and earlier, 5.6.35 and earlier and 5.7.17 and earlier. Difficult to exploit vulnerability allows high privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in takeover of MySQL Server. Note: CVE-2017-3600 is equivalent to CVE-2016-5483. CVSS 3.0 Base Score 6.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:H/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2017-3599 | High | 2017-04-24 | Not applicable | Working exploit published | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: Pluggable Auth). Supported versions that are affected are 5.6.35 and earlier and 5.7.17 and earlier. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.0 Base Score 7.5 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H). NOTE: the previous information is from the April 2017 CPU. Oracle has not commented on third-party claims that this issue is an integer overflow in sql/auth/sql_authentication.cc which allows remote attackers to cause a denial of service via a crafted authentication packet. |
| CVE-2017-3598 | Low | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Sites component of Oracle Fusion Middleware (subcomponent: Advanced UI). Supported versions that are affected are 11.1.1.8.0, 12.2.1.0.0, 12.2.1.1.0 and 12.2.1.2.0. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle WebCenter Sites. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle WebCenter Sites accessible data. CVSS 3.0 Base Score 3.1 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-3597 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Sites component of Oracle Fusion Middleware (subcomponent: Advanced UI). Supported versions that are affected are 11.1.1.8.0, 12.2.1.0.0, 12.2.1.1.0 and 12.2.1.2.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle WebCenter Sites. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle WebCenter Sites accessible data. CVSS 3.0 Base Score 5.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:U/C:H/I:N/A:N). |
| CVE-2017-3596 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Sites component of Oracle Fusion Middleware (subcomponent: Advanced UI). Supported versions that are affected are 11.1.1.8.0, 12.2.1.0.0, 12.2.1.1.0 and 12.2.1.2.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle WebCenter Sites. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle WebCenter Sites accessible data as well as unauthorized update, insert or delete access to some of Oracle WebCenter Sites accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle WebCenter Sites. CVSS 3.0 Base Score 7.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:L/A:L). |
| CVE-2017-3595 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Sites component of Oracle Fusion Middleware (subcomponent: Advanced UI). Supported versions that are affected are 11.1.1.8.0, 12.2.1.0.0, 12.2.1.1.0 and 12.2.1.2.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle WebCenter Sites. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle WebCenter Sites accessible data as well as unauthorized update, insert or delete access to some of Oracle WebCenter Sites accessible data. CVSS 3.0 Base Score 7.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:L/A:N). |
| CVE-2017-3594 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Sites component of Oracle Fusion Middleware (subcomponent: Advanced UI). Supported versions that are affected are 11.1.1.8.0, 12.2.1.0.0, 12.2.1.1.0 and 12.2.1.2.0. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle WebCenter Sites. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle WebCenter Sites accessible data as well as unauthorized update, insert or delete access to some of Oracle WebCenter Sites accessible data. CVSS 3.0 Base Score 5.9 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:L/UI:N/S:U/C:H/I:L/A:N). |
| CVE-2017-3593 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Sites component of Oracle Fusion Middleware (subcomponent: Advanced UI). Supported versions that are affected are 11.1.1.8.0, 12.2.1.0.0, 12.2.1.1.0 and 12.2.1.2.0. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebCenter Sites. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle WebCenter Sites accessible data as well as unauthorized update, insert or delete access to some of Oracle WebCenter Sites accessible data. CVSS 3.0 Base Score 7.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:L/A:N). |
| CVE-2017-3592 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Payables component of Oracle E-Business Suite (subcomponent: Self Service Manager). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily "exploitable" vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Payables. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Payables accessible data as well as unauthorized access to critical data or complete access to all Oracle Payables accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-3591 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Sites component of Oracle Fusion Middleware (subcomponent: Catalog Mover). Supported versions that are affected are 11.1.1.8.0, 12.2.1.0.0, 12.2.1.1.0 and 12.2.1.2.0. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebCenter Sites. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle WebCenter Sites accessible data as well as unauthorized read access to a subset of Oracle WebCenter Sites accessible data. CVSS 3.0 Base Score 7.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:H/A:N). |
| CVE-2017-3590 | Low | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Connectors component of Oracle MySQL (subcomponent: Connector/Python). Supported versions that are affected are 2.1.5 and earlier. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where MySQL Connectors executes to compromise MySQL Connectors. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of MySQL Connectors accessible data. CVSS 3.0 Base Score 3.3 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2017-3589 | Low | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Connectors component of Oracle MySQL (subcomponent: Connector/J). Supported versions that are affected are 5.1.41 and earlier. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where MySQL Connectors executes to compromise MySQL Connectors. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of MySQL Connectors accessible data. CVSS 3.0 Base Score 3.3 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2017-3587 | High | 2017-04-24 | Not applicable | Working exploit published | Vulnerability in the Oracle VM VirtualBox component of Oracle Virtualization (subcomponent: Shared Folder). Supported versions that are affected are Prior to 5.0.38 and Prior to 5.1.20. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Oracle VM VirtualBox executes to compromise Oracle VM VirtualBox. While the vulnerability is in Oracle VM VirtualBox, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle VM VirtualBox accessible data and unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle VM VirtualBox. CVSS 3.0 Base Score 8.4 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:C/C:N/I:H/A:H). |
| CVE-2017-3586 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the MySQL Connectors component of Oracle MySQL (subcomponent: Connector/J). Supported versions that are affected are 5.1.41 and earlier. Easily "exploitable" vulnerability allows low privileged attacker with network access via multiple protocols to compromise MySQL Connectors. While the vulnerability is in MySQL Connectors, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of MySQL Connectors accessible data as well as unauthorized read access to a subset of MySQL Connectors accessible data. CVSS 3.0 Base Score 6.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:L/I:L/A:N). |
| CVE-2017-3585 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Sun ZFS Storage Appliance Kit (AK) component of Oracle Sun Systems Products Suite (subcomponent: User Interface subsystem). The supported version that is affected is AK 2013. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Sun ZFS Storage Appliance Kit (AK). Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Sun ZFS Storage Appliance Kit (AK) accessible data. CVSS 3.0 Base Score 5.3 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2017-3584 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Sun ZFS Storage Appliance Kit (AK) component of Oracle Sun Systems Products Suite (subcomponent: RAS subsystems). The supported version that is affected is AK 2013. Difficult to exploit vulnerability allows low privileged attacker with logon to the infrastructure where Sun ZFS Storage Appliance Kit (AK) executes to compromise Sun ZFS Storage Appliance Kit (AK). While the vulnerability is in Sun ZFS Storage Appliance Kit (AK), attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Sun ZFS Storage Appliance Kit (AK). CVSS 3.0 Base Score 7.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:L/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2017-3583 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Primavera P6 Enterprise Project Portfolio Management component of Oracle Primavera Products Suite (subcomponent: Web Access). Supported versions that are affected are 8.3, 8.4, 15.1, 15.2, 16.1 and 16.2. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Primavera P6 Enterprise Project Portfolio Management. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Primavera P6 Enterprise Project Portfolio Management accessible data as well as unauthorized access to critical data or complete access to all Primavera P6 Enterprise Project Portfolio Management accessible data. CVSS 3.0 Base Score 8.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:H/A:N). |
| CVE-2017-3582 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Oracle SuperCluster Specific Software component of Oracle Sun Systems Products Suite (subcomponent: Backup/Restore Utility). Supported versions that are affected are 2.3.8 and 2.3.13. Easily "exploitable" vulnerability allows unauthenticated attacker with logon to the infrastructure where Oracle SuperCluster Specific Software executes to compromise Oracle SuperCluster Specific Software. Successful attacks of this vulnerability can result in takeover of Oracle SuperCluster Specific Software. CVSS 3.0 Base Score 8.4 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2017-3581 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Automatic Service Request (ASR) component of Oracle Support Tools (subcomponent: ASR Manager). The supported version that is affected is Prior to 5.7. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Automatic Service Request (ASR) executes to compromise Automatic Service Request (ASR). Successful attacks of this vulnerability can result in takeover of Automatic Service Request (ASR). CVSS 3.0 Base Score 7.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2017-3580 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Sun ZFS Storage Appliance Kit (AK) component of Oracle Sun Systems Products Suite (subcomponent: RAS subsystems). The supported version that is affected is AK 2013. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Sun ZFS Storage Appliance Kit (AK). Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Sun ZFS Storage Appliance Kit (AK), attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Sun ZFS Storage Appliance Kit (AK). CVSS 3.0 Base Score 8.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:R/S:C/C:H/I:H/A:H). |
| CVE-2017-3579 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Primavera P6 Enterprise Project Portfolio Management component of Oracle Primavera Products Suite (subcomponent: Web Access). Supported versions that are affected are 8.3, 8.4, 15.1, 15.2, 16.1 and 16.2. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Primavera P6 Enterprise Project Portfolio Management. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Primavera P6 Enterprise Project Portfolio Management, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Primavera P6 Enterprise Project Portfolio Management accessible data as well as unauthorized read access to a subset of Primavera P6 Enterprise Project Portfolio Management accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-3578 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Sun ZFS Storage Appliance Kit (AK) component of Oracle Sun Systems Products Suite (subcomponent: RAS subsystems). The supported version that is affected is AK 2013. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Sun ZFS Storage Appliance Kit (AK) executes to compromise Sun ZFS Storage Appliance Kit (AK). While the vulnerability is in Sun ZFS Storage Appliance Kit (AK), attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Sun ZFS Storage Appliance Kit (AK). CVSS 3.0 Base Score 8.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2017-3577 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise CS Campus Community component of Oracle PeopleSoft Products (subcomponent: Frameworks). The supported version that is affected is 9.2. Easily "exploitable" vulnerability allows high privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise CS Campus Community. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all PeopleSoft Enterprise CS Campus Community accessible data as well as unauthorized access to critical data or complete access to all PeopleSoft Enterprise CS Campus Community accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-3576 | High | 2017-04-24 | Not applicable | Working exploit published | Vulnerability in the Oracle VM VirtualBox component of Oracle Virtualization (subcomponent: Core). Supported versions that are affected are Prior to 5.0.38 and Prior to 5.1.20. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Oracle VM VirtualBox executes to compromise Oracle VM VirtualBox. While the vulnerability is in Oracle VM VirtualBox, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Oracle VM VirtualBox. CVSS 3.0 Base Score 8.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2017-3575 | High | 2017-04-24 | Not applicable | Working exploit published | Vulnerability in the Oracle VM VirtualBox component of Oracle Virtualization (subcomponent: Core). Supported versions that are affected are Prior to 5.0.38 and Prior to 5.1.20. Easily "exploitable" vulnerability allows high privileged attacker with logon to the infrastructure where Oracle VM VirtualBox executes to compromise Oracle VM VirtualBox. While the vulnerability is in Oracle VM VirtualBox, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle VM VirtualBox accessible data and unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle VM VirtualBox. CVSS 3.0 Base Score 7.9 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:H/UI:N/S:C/C:N/I:H/A:H). |
| CVE-2017-3574 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality OPERA 5 Property Services component of Oracle Hospitality Applications (subcomponent: OPERA License code configuration). Supported versions that are affected are 5.4.0.x, 5.4.1.x, 5.4.2.x, 5.4.3.x, 5.5.0.x and 5.5.1.x. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Hospitality OPERA 5 Property Services. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Hospitality OPERA 5 Property Services accessible data as well as unauthorized update, insert or delete access to some of Oracle Hospitality OPERA 5 Property Services accessible data. CVSS 3.0 Base Score 7.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:L/A:N). |
| CVE-2017-3573 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality OPERA 5 Property Services component of Oracle Hospitality Applications (subcomponent: OPERA Printing). Supported versions that are affected are 5.4.0.x, 5.4.1.x, 5.4.2.x, 5.4.3.x, 5.5.0.x and 5.5.1.x. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Hospitality OPERA 5 Property Services. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Hospitality OPERA 5 Property Services, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Hospitality OPERA 5 Property Services accessible data as well as unauthorized read access to a subset of Oracle Hospitality OPERA 5 Property Services accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-3572 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager component of Oracle Commerce (subcomponent: MDEX). Supported versions that are affected are 6.2.2, 6.3.0, 6.4.1.2, 6.5.0, 6.5.1 and 6.5.2. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Commerce Guided Search / Oracle Commerce Experience Manager. CVSS 3.0 Base Score 7.5 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3571 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise SCM eBill Payment component of Oracle PeopleSoft Products (subcomponent: Security). The supported version that is affected is 9.2. Easily "exploitable" vulnerability allows high privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise SCM eBill Payment. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all PeopleSoft Enterprise SCM eBill Payment accessible data as well as unauthorized access to critical data or complete access to all PeopleSoft Enterprise SCM eBill Payment accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-3570 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FSCM component of Oracle PeopleSoft Products (subcomponent: eSettlements). The supported version that is affected is 9.1. Easily "exploitable" vulnerability allows high privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise FSCM. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all PeopleSoft Enterprise FSCM accessible data as well as unauthorized access to critical data or complete access to all PeopleSoft Enterprise FSCM accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-3569 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality OPERA 5 Property Services component of Oracle Hospitality Applications (subcomponent: OPERA Business Events). Supported versions that are affected are 5.4.0.x, 5.4.1.x, 5.4.2.x, 5.4.3.x, 5.5.0.x and 5.5.1.x. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Hospitality OPERA 5 Property Services. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Hospitality OPERA 5 Property Services accessible data as well as unauthorized read access to a subset of Oracle Hospitality OPERA 5 Property Services accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-3568 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality OPERA 5 Property Services component of Oracle Hospitality Applications (subcomponent: OPERA Printing and Login). Supported versions that are affected are 5.4.0.x, 5.4.1.x, 5.4.2.x, 5.4.3.x, 5.5.0.x and 5.5.1.x. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Oracle Hospitality OPERA 5 Property Services executes to compromise Oracle Hospitality OPERA 5 Property Services. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Hospitality OPERA 5 Property Services accessible data as well as unauthorized access to critical data or complete access to all Oracle Hospitality OPERA 5 Property Services accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Hospitality OPERA 5 Property Services. CVSS 3.0 Base Score 6.5 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:L). |
| CVE-2017-3567 | Medium | 2017-04-24 | Outside Waratek scope | No public exploit | Vulnerability in the OJVM component of Oracle Database Server. Supported versions that are affected are 11.2.0.4 and 12.1.0.2. Difficult to exploit vulnerability allows low privileged attacker having Create Session, Create Procedure privilege with network access via multiple protocols to compromise OJVM. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of OJVM. CVSS 3.0 Base Score 5.3 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:L/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3565 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Solaris component of Oracle Sun Systems Products Suite (subcomponent: RBAC). The supported version that is affected is 11.3. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Solaris executes to compromise Solaris. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Solaris, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Solaris accessible data as well as unauthorized access to critical data or complete access to all Solaris accessible data. CVSS 3.0 Base Score 7.9 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:R/S:C/C:H/I:H/A:N). |
| CVE-2017-3564 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Solaris component of Oracle Sun Systems Products Suite (subcomponent: RBAC). The supported version that is affected is 11.3. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Solaris executes to compromise Solaris. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Solaris, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Solaris. CVSS 3.0 Base Score 8.2 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:R/S:C/C:H/I:H/A:H). |
| CVE-2017-3563 | High | 2017-04-24 | Not applicable | Working exploit published | Vulnerability in the Oracle VM VirtualBox component of Oracle Virtualization (subcomponent: Core). Supported versions that are affected are Prior to 5.0.38 and Prior to 5.1.20. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Oracle VM VirtualBox executes to compromise Oracle VM VirtualBox. While the vulnerability is in Oracle VM VirtualBox, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Oracle VM VirtualBox. CVSS 3.0 Base Score 8.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2017-3561 | High | 2017-04-24 | Not applicable | Working exploit published | Vulnerability in the Oracle VM VirtualBox component of Oracle Virtualization (subcomponent: Core). Supported versions that are affected are Prior to 5.0.38 and Prior to 5.1.20. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Oracle VM VirtualBox executes to compromise Oracle VM VirtualBox. While the vulnerability is in Oracle VM VirtualBox, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Oracle VM VirtualBox. CVSS 3.0 Base Score 8.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2017-3560 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality OPERA 5 Property Services component of Oracle Hospitality Applications (subcomponent: OXI Interface). Supported versions that are affected are 5.4.0.x, 5.4.1.x, 5.4.2.x, 5.4.3.x, 5.5.0.x and 5.5.1.x. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Hospitality OPERA 5 Property Services. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Hospitality OPERA 5 Property Services accessible data. CVSS 3.0 Base Score 4.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-3559 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Oracle VM VirtualBox component of Oracle Virtualization (subcomponent: Core). Supported versions that are affected are Prior to 5.0.38 and Prior to 5.1.20. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Oracle VM VirtualBox executes to compromise Oracle VM VirtualBox. While the vulnerability is in Oracle VM VirtualBox, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle VM VirtualBox as well as unauthorized update, insert or delete access to some of Oracle VM VirtualBox accessible data and unauthorized read access to a subset of Oracle VM VirtualBox accessible data. CVSS 3.0 Base Score 7.9 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:C/C:L/I:L/A:H). |
| CVE-2017-3558 | High | 2017-04-24 | Not applicable | Working exploit published | Vulnerability in the Oracle VM VirtualBox component of Oracle Virtualization (subcomponent: Core). Supported versions that are affected are Prior to 5.0.38 and Prior to 5.1.20. Easily "exploitable" vulnerability allows unauthenticated attacker with logon to the infrastructure where Oracle VM VirtualBox executes to compromise Oracle VM VirtualBox. While the vulnerability is in Oracle VM VirtualBox, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle VM VirtualBox as well as unauthorized update, insert or delete access to some of Oracle VM VirtualBox accessible data and unauthorized read access to a subset of Oracle VM VirtualBox accessible data. CVSS 3.0 Base Score 8.5 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:N/UI:N/S:C/C:L/I:L/A:H). |
| CVE-2017-3557 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle One-to-One Fulfillment component of Oracle E-Business Suite (subcomponent: Print Server). Supported versions that are affected are 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle One-to-One Fulfillment. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle One-to-One Fulfillment, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle One-to-One Fulfillment accessible data as well as unauthorized update, insert or delete access to some of Oracle One-to-One Fulfillment accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-3556 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Application Object Library component of Oracle E-Business Suite (subcomponent: File Management). Supported versions that are affected are 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Application Object Library. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Application Object Library accessible data. CVSS 3.0 Base Score 3.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-3555 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle iReceivables component of Oracle E-Business Suite (subcomponent: Self Registration). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle iReceivables. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle iReceivables. CVSS 3.0 Base Score 7.5 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-3554 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Sites component of Oracle Fusion Middleware (subcomponent: Catalog Mover). Supported versions that are affected are 11.1.1.8.0, 12.2.1.0.0, 12.2.1.1.0 and 12.2.1.2.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle WebCenter Sites. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle WebCenter Sites accessible data as well as unauthorized access to critical data or complete access to all Oracle WebCenter Sites accessible data. CVSS 3.0 Base Score 8.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-3553 | Critical | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Identity Manager component of Oracle Fusion Middleware (subcomponent: Rules Engine). The supported version that is affected is 11.1.2.3.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Identity Manager. While the vulnerability is in Oracle Identity Manager, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Oracle Identity Manager. CVSS 3.0 Base Score 9.9 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2017-3552 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality OPERA 5 Property Services component of Oracle Hospitality Applications (subcomponent: OPERA Room Image/Picture Setup). Supported versions that are affected are 5.4.0.x, 5.4.1.x, 5.4.2.x, 5.4.3.x, 5.5.0.x and 5.5.1.x. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Hospitality OPERA 5 Property Services. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Hospitality OPERA 5 Property Services accessible data. CVSS 3.0 Base Score 4.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-3551 | Medium | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Solaris component of Oracle Sun Systems Products Suite (subcomponent: Smartcard Libraries). The supported version that is affected is 11.3. Easily "exploitable" vulnerability allows low privileged attacker with logon to the infrastructure where Solaris executes to compromise Solaris. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Solaris as well as unauthorized update, insert or delete access to some of Solaris accessible data and unauthorized read access to a subset of Solaris accessible data. CVSS 3.0 Base Score 6.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:H). |
| CVE-2017-3550 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Customer Interaction History component of Oracle E-Business Suite (subcomponent: Admin Console). Supported versions that are affected are 12.1.1, 12.1.2 and 12.1.3. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Customer Interaction History. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Customer Interaction History, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Customer Interaction History accessible data as well as unauthorized update, insert or delete access to some of Oracle Customer Interaction History accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-3549 | Critical | 2017-04-24 | Protected by Waratek | Working exploit published | Vulnerability in the Oracle Scripting component of Oracle E-Business Suite (subcomponent: Scripting Administration). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Scripting. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Scripting accessible data as well as unauthorized access to critical data or complete access to all Oracle Scripting accessible data. CVSS 3.0 Base Score 9.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-3548 | Medium | 2017-04-24 | Protected by Waratek | Working exploit published | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Integration Broker). Supported versions that are affected are 8.54 and 8.55. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks of this vulnerability can result in unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of PeopleSoft Enterprise PeopleTools. CVSS 3.0 Base Score 6.5 (Confidentiality and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:L). |
| CVE-2017-3547 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: MultiChannel Framework). Supported versions that are affected are 8.54 and 8.55. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PeopleTools, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 7.4 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:N/I:H/A:N). |
| CVE-2017-3546 | Medium | 2017-04-24 | Protected by Waratek | Working exploit published | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: MultiChannel Framework). Supported versions that are affected are 8.54 and 8.55. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PeopleTools accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-3545 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Sites component of Oracle Fusion Middleware (subcomponent: Blob Server). Supported versions that are affected are 11.1.1.8.0, 12.2.1.0.0, 12.2.1.1.0 and 12.2.1.2.0. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebCenter Sites. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle WebCenter Sites accessible data as well as unauthorized read access to a subset of Oracle WebCenter Sites accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:H/A:N). |
| CVE-2017-3544 | Low | 2017-04-24 | Protected by Waratek | No public exploit | Vulnerability in the Java SE, Java SE Embedded, JRockit component of Oracle Java SE (subcomponent: Networking). Supported versions that are affected are Java SE: 6u141, 7u131 and 8u121; Java SE Embedded: 8u121; JRockit: R28.3.13. Difficult to exploit vulnerability allows unauthenticated attacker with network access via SMTP to compromise Java SE, Java SE Embedded, JRockit. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Java SE, Java SE Embedded, JRockit accessible data. Note: Applies to client and server deployment of Java. This vulnerability can be exploited through sandboxed Java Web Start applications and sandboxed Java applets. It can also be exploited by supplying data to APIs in the specified Component without using sandboxed Java Web Start applications or sandboxed Java applets, such as through a web service. CVSS 3.0 Base Score 3.7 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2017-3543 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Sites component of Oracle Fusion Middleware (subcomponent: Server). Supported versions that are affected are 11.1.1.8.0, 12.2.1.0.0, 12.2.1.1.0 and 12.2.1.2.0. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebCenter Sites. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle WebCenter Sites accessible data as well as unauthorized update, insert or delete access to some of Oracle WebCenter Sites accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle WebCenter Sites. CVSS 3.0 Base Score 8.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:L/A:L). |
| CVE-2017-3542 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Sites component of Oracle Fusion Middleware (subcomponent: Server). Supported versions that are affected are 11.1.1.8.0, 12.2.1.0.0, 12.2.1.1.0 and 12.2.1.2.0. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebCenter Sites. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle WebCenter Sites accessible data as well as unauthorized update, insert or delete access to some of Oracle WebCenter Sites accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle WebCenter Sites. CVSS 3.0 Base Score 8.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:L/A:L). |
| CVE-2017-3541 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Sites component of Oracle Fusion Middleware (subcomponent: Server). Supported versions that are affected are 11.1.1.8.0, 12.2.1.0.0, 12.2.1.1.0 and 12.2.1.2.0. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebCenter Sites. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle WebCenter Sites accessible data as well as unauthorized update, insert or delete access to some of Oracle WebCenter Sites accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:L/A:N). |
| CVE-2017-3540 | High | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Sites component of Oracle Fusion Middleware (subcomponent: Server). Supported versions that are affected are 11.1.1.8.0, 12.2.1.0.0, 12.2.1.1.0 and 12.2.1.2.0. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebCenter Sites. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle WebCenter Sites as well as unauthorized update, insert or delete access to some of Oracle WebCenter Sites accessible data and unauthorized read access to a subset of Oracle WebCenter Sites accessible data. CVSS 3.0 Base Score 8.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:H). |
| CVE-2017-3539 | Low | 2017-04-24 | Outside Waratek scope | No public exploit | Vulnerability in the Java SE, Java SE Embedded component of Oracle Java SE (subcomponent: Security). Supported versions that are affected are Java SE: 6u141, 7u131 and 8u121; Java SE Embedded: 8u121. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE, Java SE Embedded. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Java SE, Java SE Embedded accessible data. Note: This vulnerability applies to Java deployments, typically in clients running sandboxed Java Web Start applications or sandboxed Java applets, that load and run untrusted code (e.g., code that comes from the internet) and rely on the Java sandbox for security. This vulnerability does not apply to Java deployments, typically in servers, that load and run only trusted code (e.g., code installed by an administrator). CVSS 3.0 Base Score 3.1 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:R/S:U/C:N/I:L/A:N). |
| CVE-2017-3538 | High | 2017-04-24 | Not applicable | No public exploit | Vulnerability in the Oracle VM VirtualBox component of Oracle Virtualization (subcomponent: Shared Folder). Supported versions that are affected are Prior to 5.0.34 and Prior to 5.1.16. Difficult to exploit vulnerability allows low privileged attacker with logon to the infrastructure where Oracle VM VirtualBox executes to compromise Oracle VM VirtualBox. While the vulnerability is in Oracle VM VirtualBox, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle VM VirtualBox accessible data as well as unauthorized access to critical data or complete access to all Oracle VM VirtualBox accessible data. CVSS 3.0 Base Score 7.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:L/UI:N/S:C/C:H/I:H/A:N). |
| CVE-2017-3537 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Real-Time Scheduler component of Oracle Utilities Applications (subcomponent: Mobile Communications Platform). Supported versions that are affected are 2.2.0.3.13, 2.3.0.0 and 2.3.0.1. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Real-Time Scheduler. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Real-Time Scheduler, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Real-Time Scheduler accessible data as well as unauthorized read access to a subset of Oracle Real-Time Scheduler accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-3536 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Security). Supported versions that are affected are 8.54 and 8.55. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PeopleTools accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 4.6 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:U/C:L/I:L/A:N). |
| CVE-2017-3535 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Universal Banking component of Oracle Financial Services Applications (subcomponent: Infrastructure). Supported versions that are affected are 11.3.0, 11.4.0, 12.0.1, 12.0.2 and 12.0.3. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle FLEXCUBE Universal Banking. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle FLEXCUBE Universal Banking, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle FLEXCUBE Universal Banking accessible data. CVSS 3.0 Base Score 4.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:N/A:N). |
| CVE-2017-3534 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Universal Banking component of Oracle Financial Services Applications (subcomponent: Infrastructure). Supported versions that are affected are 12.0.1, 12.0.2, 12.0.3, 12.1.0, 12.2.0 and 12.3.0. Easily "exploitable" vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Universal Banking. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle FLEXCUBE Universal Banking accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-3533 | Low | 2017-04-24 | Protected by Waratek | No public exploit | Vulnerability in the Java SE, Java SE Embedded, JRockit component of Oracle Java SE (subcomponent: Networking). Supported versions that are affected are Java SE: 6u141, 7u131 and 8u121; Java SE Embedded: 8u121; JRockit: R28.3.13. Difficult to exploit vulnerability allows unauthenticated attacker with network access via FTP to compromise Java SE, Java SE Embedded, JRockit. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Java SE, Java SE Embedded, JRockit accessible data. Note: Applies to client and server deployment of Java. This vulnerability can be exploited through sandboxed Java Web Start applications and sandboxed Java applets. It can also be exploited by supplying data to APIs in the specified Component without using sandboxed Java Web Start applications or sandboxed Java applets, such as through a web service. CVSS 3.0 Base Score 3.7 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2017-3532 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Retail Warehouse Management System component of Oracle Retail Applications (subcomponent: Security). Supported versions that are affected are 13.2, 14.0 and 15.0. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Retail Warehouse Management System. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Retail Warehouse Management System, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Retail Warehouse Management System accessible data as well as unauthorized read access to a subset of Oracle Retail Warehouse Management System accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-3531 | High | 2017-04-24 | Protected by Waratek | No public exploit | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: Servlet Runtime). Supported versions that are affected are 12.1.3.0, 12.2.1.0, 12.2.1.1 and 12.2.1.2. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebLogic Server. While the vulnerability is in Oracle WebLogic Server, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle WebLogic Server accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle WebLogic Server. CVSS 3.0 Base Score 7.2 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:C/C:N/I:L/A:L). |
| CVE-2017-3530 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the Oracle Transportation Manager component of Oracle Supply Chain Products Suite (subcomponent: Security). Supported versions that are affected are 6.2, 6.3.0, 6.3.1, 6.3.2, 6.3.3, 6.3.4, 6.3.5, 6.3.6, 6.3.7, 6.4.0, 6.4.1 and 6.4.2. Easily "exploitable" vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Transportation Manager. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Transportation Manager accessible data as well as unauthorized access to critical data or complete access to all Oracle Transportation Manager accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:U/C:H/I:H/A:N). |
| CVE-2017-3528 | Medium | 2017-04-24 | Mitigation candidate | Working exploit published | Vulnerability in the Oracle Applications Framework component of Oracle E-Business Suite (subcomponent: Popup windows (lists of values, datepicker, etc.)). Supported versions that are affected are 12.1.3, 12.2.3, 12.2.4, 12.2.5 and 12.2.6. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Applications Framework. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Applications Framework, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Applications Framework accessible data. CVSS 3.0 Base Score 4.7 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:N/I:L/A:N). |
| CVE-2017-3527 | Medium | 2017-04-24 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Fluid Core). Supported versions that are affected are 8.54 and 8.55. Easily "exploitable" vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks of this vulnerability can result in unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 5.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N). |