
Oracle Critical Patch Update January 2017
Released January 2017 · Oracle's advisory ↗ · ← Critical Patch Update, October 2016 · Critical Patch Update, April 2017 →
163 CVEs in this release, one square each
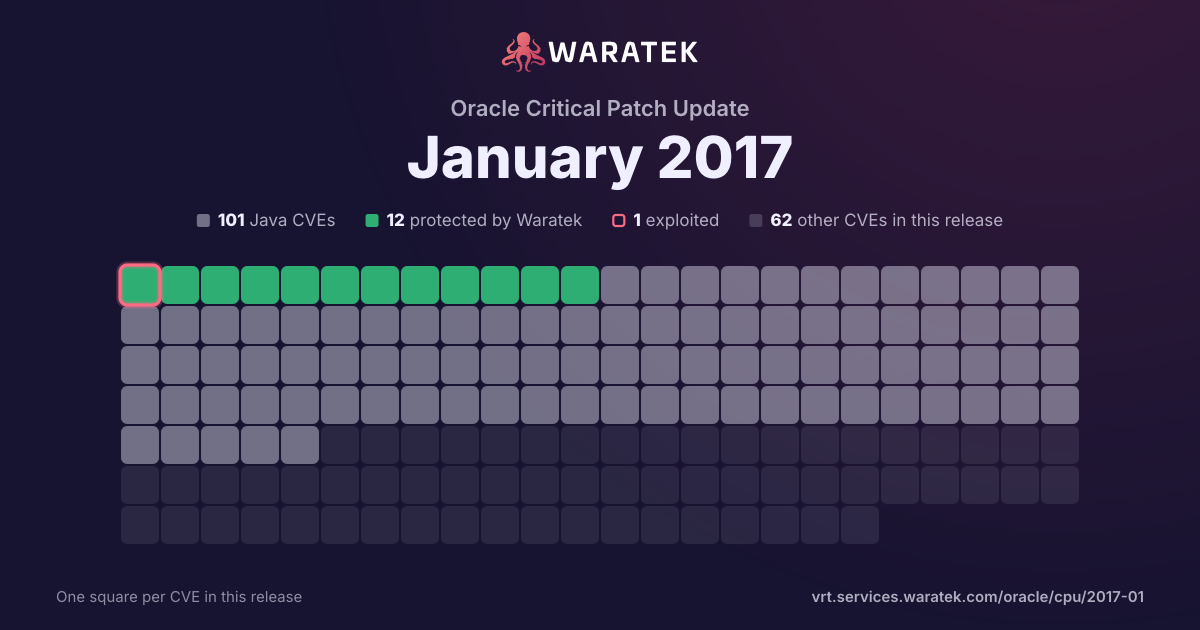
By status
12Protected by Waratek89No exploit published16Outside Waratek scope46Not applicable
1Exploited, marked by the ring
No exploit published. For 86 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 9 matches · 2 in Waratek scope · 1 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
9matches
2in Waratek scope22.2%
1protected11.1%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
1
11.1%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
1
11.1%
Outside Waratek scope
3
33.3%
Not applicable
4
44.4%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
11.1%
partly blocked
0
0.0%
not blocked
8
88.9%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
9
100.0%
split by
peak 2 / month
Mar 151
Protected by Waratek1
Medium1
blocked by ARMR today1
No public exploit1
Apr 150
May 150
Jun 152
Not applicable2
Medium2
not blocked2
No public exploit2
Jul 150
Aug 152
Outside Waratek scope1
Not applicable1
Critical1
Medium1
not blocked2
No public exploit2
Sep 150
Oct 150
Nov 151
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Dec 150
Jan 161
Not applicable1
Critical1
not blocked1
No public exploit1
Feb 161
Outside Waratek scope1
High1
not blocked1
No public exploit1
Mar 160
Apr 161
No exploit published1
Medium1
not blocked1
No public exploit1
Apr 15Jun 15Aug 15Oct 15Dec 15Feb 16Apr 16
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-0734 | Medium | 2016-04-07 | No exploit published | No public exploit | The web-based administration console in Apache ActiveMQ 5.x before 5.13.2 does not send an X-Frame-Options HTTP header, which makes it easier for remote attackers to conduct clickjacking attacks via a crafted web page that contains a (1) FRAME or (2) IFRAME element. |
| CVE-2016-0714 | High | 2016-02-25 | Outside Waratek scope | No public exploit | The session-persistence implementation in Apache Tomcat 6.x before 6.0.45, 7.x before 7.0.68, 8.x before 8.0.31, and 9.x before 9.0.0.M2 mishandles session attributes, which allows remote authenticated users to bypass intended SecurityManager restrictions and execute arbitrary code in a privileged context via a web application that places a crafted object in a session. |
| CVE-2016-1903 | Critical | 2016-01-19 | Not applicable | No public exploit | The gdImageRotateInterpolated function in ext/gd/libgd/gd_interpolation.c in PHP before 5.5.31, 5.6.x before 5.6.17, and 7.x before 7.0.2 allows remote attackers to obtain sensitive information or cause a denial of service (out-of-bounds read and application crash) via a large bgd_color argument to the imagerotate function. |
| CVE-2015-7940 | Medium | 2015-11-09 | Outside Waratek scope | No public exploit | The Bouncy Castle Java library before 1.51 does not validate a point is withing the elliptic curve, which makes it easier for remote attackers to obtain private keys via a series of crafted elliptic curve Diffie Hellman (ECDH) key exchanges, aka an "invalid curve attack." |
| CVE-2015-5505 | Medium | 2015-08-18 | Not applicable | No public exploit | The HTTP Strict Transport Security (HSTS) module 6.x-1.x before 6.x-1.1 and 7.x-1.x before 7.x-1.2 for Drupal does not properly implement the "include subdomains" directive, which causes the HSTS policy to not be applied to subdomains and allows man-in-the-middle attackers to have unspecified impact via unknown vectors. |
| CVE-2015-3253 | Critical | 2015-08-13 | Outside Waratek scope | No public exploit | The MethodClosure class in runtime/MethodClosure.java in Apache Groovy 1.7.0 through 2.4.3 allows remote attackers to execute arbitrary code or cause a denial of service via a crafted serialized object. |
| CVE-2015-3237 | Medium | 2015-06-22 | Not applicable | No public exploit | The smb_request_state function in cURL and libcurl 7.40.0 through 7.42.1 allows remote SMB servers to obtain sensitive information from memory or cause a denial of service (out-of-bounds read and crash) via crafted length and offset values. |
| CVE-2015-1791 | Medium | 2015-06-12 | Not applicable | No public exploit | Race condition in the ssl3_get_new_session_ticket function in ssl/s3_clnt.c in OpenSSL before 0.9.8zg, 1.0.0 before 1.0.0s, 1.0.1 before 1.0.1n, and 1.0.2 before 1.0.2b, when used for a multi-threaded client, allows remote attackers to cause a denial of service (double free and application crash) or possibly have unspecified other impact by providing a NewSessionTicket during an attempt to reuse a ticket that had been obtained earlier. |
| CVE-2015-0250 | Medium | 2015-03-24 | Protected by Waratek | No public exploit | XML external entity (XXE) vulnerability in the SVG to (1) PNG and (2) JPG conversion classes in Apache Batik 1.x before 1.8 allows remote attackers to read arbitrary files or cause a denial of service via a crafted SVG file. |