
Oracle Critical Patch Update July 2016
Released July 2016 · Oracle's advisory ↗ · ← Critical Patch Update, April 2016 · Critical Patch Update, October 2016 →
222 CVEs in this release, one square each
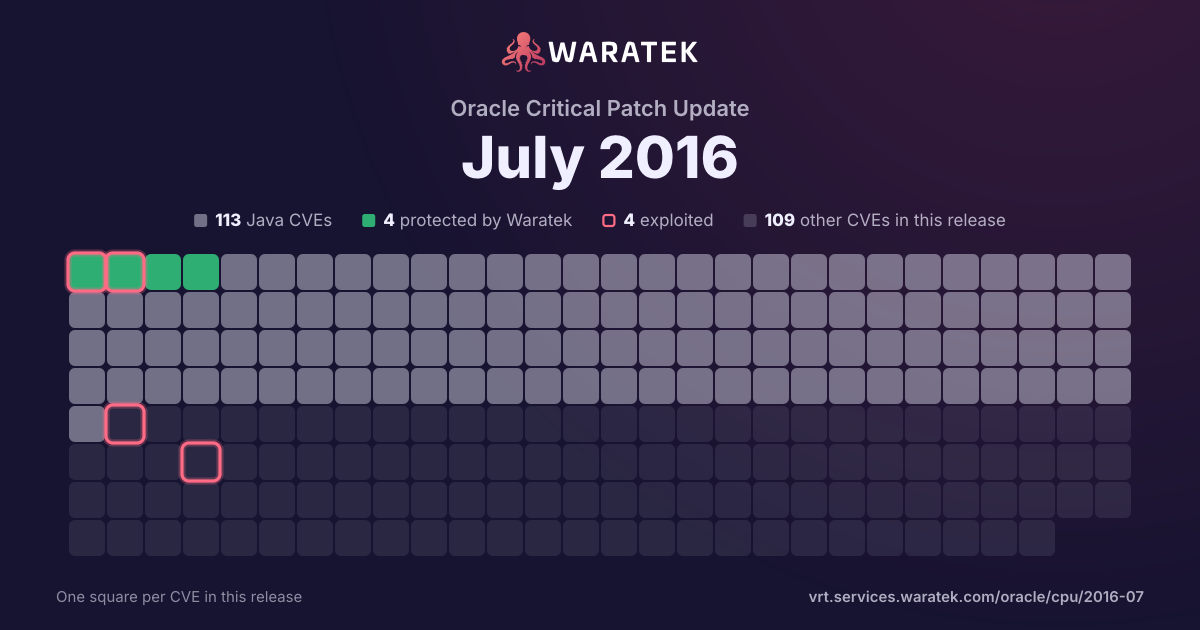
By status
4Protected by Waratek1Mitigation candidate108No exploit published30Outside Waratek scope79Not applicable
4Exploited, marked by the ring
No exploit published. For 108 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 69 matches · 29 in Waratek scope · 2 protected · 2 exploited · 1 CISA KEV · 3 public PoC · 3 EPSS ≥ 0.5
69matches
29in Waratek scope42.0%
2protected2.9%
2exploited2.9%
1CISA KEV1.4%
3public PoC4.3%
3EPSS ≥ 0.54.3%
Protected by Waratek
2
2.9%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
27
39.1%
Outside Waratek scope
7
10.1%
Not applicable
33
47.8%
Withdrawn CVE
0
0.0%
blocked by ARMR today
2
2.9%
partly blocked
0
0.0%
not blocked
67
97.1%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
2
2.9%
Working exploit published
1
1.4%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
66
95.7%
split by
peak 62 / quarter
Q2 141
Outside Waratek scope1
High1
not blocked1
Exploited1
Q3 140
Q4 140
Q1 151
Outside Waratek scope1
High1
not blocked1
Working exploit published1
Q2 150
Q3 151
Not applicable1
High1
not blocked1
No public exploit1
Q4 150
Q1 160
Q2 162
Protected by Waratek1
Not applicable1
High2
blocked by ARMR today1
not blocked1
Exploited1
No public exploit1
Q3 1662
Protected by Waratek1
No exploit published27
Outside Waratek scope5
Not applicable29
High62
blocked by ARMR today1
not blocked61
No public exploit62
Q4 160
Q1 171
Not applicable1
High1
not blocked1
No public exploit1
Q2 170
Q3 171
Not applicable1
High1
not blocked1
No public exploit1
Q3 14Q1 15Q3 15Q1 16Q3 16Q1 17Q3 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-5300 | High | 2017-07-21 | Not applicable | No public exploit | The panic_gate check in NTP before 4.2.8p5 is only re-enabled after the first change to the system clock that was greater than 128 milliseconds by default, which allows remote attackers to set NTP to an arbitrary time when started with the -g option, or to alter the time by up to 900 seconds otherwise by responding to an unspecified number of requests from trusted sources, and leveraging a resulting denial of service (abort and restart). |
| CVE-2016-1548 | High | 2017-01-06 | Not applicable | No public exploit | An attacker can spoof a packet from a legitimate ntpd server with an origin timestamp that matches the peer->dst timestamp recorded for that server. After making this switch, the client in NTP 4.2.8p4 and earlier and NTPSec aa48d001683e5b791a743ec9c575aaf7d867a2b0c will reject all future legitimate server responses. It is possible to force the victim client to move time after the mode has been changed. ntpq gives no indication that the mode has been switched. |
| CVE-2016-5476 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Integration Bus component in Oracle Retail Applications 13.0, 13.1, 13.2, 14.0, 14.1, and 15.0 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to Install. |
| CVE-2016-5475 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Service Backbone component in Oracle Retail Applications 14.0, 14.1, and 15.0 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to Install. |
| CVE-2016-5474 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Service Backbone component in Oracle Retail Applications 14.0, 14.1, and 15.0 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to RSB Kernel. |
| CVE-2016-5472 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.54 and 8.55 allows local users to affect confidentiality, integrity, and availability via vectors related to Install and Packaging. |
| CVE-2016-5465 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53, 8.54, and 8.55 allows remote attackers to affect confidentiality and integrity via vectors related to Panel Processor. |
| CVE-2016-5457 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the ILOM component in Oracle Sun Systems Products Suite 3.0, 3.1, and 3.2 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to LUMAIN. |
| CVE-2016-5451 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel UI Framework component in Oracle Siebel CRM 8.1.1, 8.2.2, IP2014, IP2015, and IP2016 allows remote authenticated users to affect confidentiality and integrity via vectors related to EAI, a different vulnerability than CVE-2016-5468. |
| CVE-2016-5449 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the ILOM component in Oracle Sun Systems Products Suite 3.0, 3.1, and 3.2 allows remote attackers to affect availability via vectors related to Console Redirection. |
| CVE-2016-5447 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the ILOM component in Oracle Sun Systems Products Suite 3.0, 3.1, and 3.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-5446 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the ILOM component in Oracle Sun Systems Products Suite 3.0, 3.1, and 3.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Infrastructure. |
| CVE-2016-5445 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the ILOM component in Oracle Sun Systems Products Suite 3.0, 3.1, and 3.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-3596 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-3574, CVE-2016-3575, CVE-2016-3576, CVE-2016-3577, CVE-2016-3578, CVE-2016-3579, CVE-2016-3580, CVE-2016-3581, CVE-2016-3582, CVE-2016-3583, CVE-2016-3590, CVE-2016-3591, CVE-2016-3592, CVE-2016-3593, CVE-2016-3594, and CVE-2016-3595. |
| CVE-2016-3595 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-3574, CVE-2016-3575, CVE-2016-3576, CVE-2016-3577, CVE-2016-3578, CVE-2016-3579, CVE-2016-3580, CVE-2016-3581, CVE-2016-3582, CVE-2016-3583, CVE-2016-3590, CVE-2016-3591, CVE-2016-3592, CVE-2016-3593, CVE-2016-3594, and CVE-2016-3596. |
| CVE-2016-3594 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-3574, CVE-2016-3575, CVE-2016-3576, CVE-2016-3577, CVE-2016-3578, CVE-2016-3579, CVE-2016-3580, CVE-2016-3581, CVE-2016-3582, CVE-2016-3583, CVE-2016-3590, CVE-2016-3591, CVE-2016-3592, CVE-2016-3593, CVE-2016-3595, and CVE-2016-3596. |
| CVE-2016-3593 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-3574, CVE-2016-3575, CVE-2016-3576, CVE-2016-3577, CVE-2016-3578, CVE-2016-3579, CVE-2016-3580, CVE-2016-3581, CVE-2016-3582, CVE-2016-3583, CVE-2016-3590, CVE-2016-3591, CVE-2016-3592, CVE-2016-3594, CVE-2016-3595, and CVE-2016-3596. |
| CVE-2016-3592 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-3574, CVE-2016-3575, CVE-2016-3576, CVE-2016-3577, CVE-2016-3578, CVE-2016-3579, CVE-2016-3580, CVE-2016-3581, CVE-2016-3582, CVE-2016-3583, CVE-2016-3590, CVE-2016-3591, CVE-2016-3593, CVE-2016-3594, CVE-2016-3595, and CVE-2016-3596. |
| CVE-2016-3591 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-3574, CVE-2016-3575, CVE-2016-3576, CVE-2016-3577, CVE-2016-3578, CVE-2016-3579, CVE-2016-3580, CVE-2016-3581, CVE-2016-3582, CVE-2016-3583, CVE-2016-3590, CVE-2016-3592, CVE-2016-3593, CVE-2016-3594, CVE-2016-3595, and CVE-2016-3596. |
| CVE-2016-3590 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-3574, CVE-2016-3575, CVE-2016-3576, CVE-2016-3577, CVE-2016-3578, CVE-2016-3579, CVE-2016-3580, CVE-2016-3581, CVE-2016-3582, CVE-2016-3583, CVE-2016-3591, CVE-2016-3592, CVE-2016-3593, CVE-2016-3594, CVE-2016-3595, and CVE-2016-3596. |
| CVE-2016-3585 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the ILOM component in Oracle Sun Systems Products Suite 3.0, 3.1, and 3.2 allows remote attackers to affect confidentiality and integrity via vectors related to Emulex. |
| CVE-2016-3584 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows local users to affect confidentiality, integrity, and availability via vectors related to Libadimalloc. |
| CVE-2016-3583 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-3574, CVE-2016-3575, CVE-2016-3576, CVE-2016-3577, CVE-2016-3578, CVE-2016-3579, CVE-2016-3580, CVE-2016-3581, CVE-2016-3582, CVE-2016-3590, CVE-2016-3591, CVE-2016-3592, CVE-2016-3593, CVE-2016-3594, CVE-2016-3595, and CVE-2016-3596. |
| CVE-2016-3582 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-3574, CVE-2016-3575, CVE-2016-3576, CVE-2016-3577, CVE-2016-3578, CVE-2016-3579, CVE-2016-3580, CVE-2016-3581, CVE-2016-3583, CVE-2016-3590, CVE-2016-3591, CVE-2016-3592, CVE-2016-3593, CVE-2016-3594, CVE-2016-3595, and CVE-2016-3596. |
| CVE-2016-3581 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-3574, CVE-2016-3575, CVE-2016-3576, CVE-2016-3577, CVE-2016-3578, CVE-2016-3579, CVE-2016-3580, CVE-2016-3582, CVE-2016-3583, CVE-2016-3590, CVE-2016-3591, CVE-2016-3592, CVE-2016-3593, CVE-2016-3594, CVE-2016-3595, and CVE-2016-3596. |
| CVE-2016-3580 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-3574, CVE-2016-3575, CVE-2016-3576, CVE-2016-3577, CVE-2016-3578, CVE-2016-3579, CVE-2016-3581, CVE-2016-3582, CVE-2016-3583, CVE-2016-3590, CVE-2016-3591, CVE-2016-3592, CVE-2016-3593, CVE-2016-3594, CVE-2016-3595, and CVE-2016-3596. |
| CVE-2016-3579 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-3574, CVE-2016-3575, CVE-2016-3576, CVE-2016-3577, CVE-2016-3578, CVE-2016-3580, CVE-2016-3581, CVE-2016-3582, CVE-2016-3583, CVE-2016-3590, CVE-2016-3591, CVE-2016-3592, CVE-2016-3593, CVE-2016-3594, CVE-2016-3595, and CVE-2016-3596. |
| CVE-2016-3578 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-3574, CVE-2016-3575, CVE-2016-3576, CVE-2016-3577, CVE-2016-3579, CVE-2016-3580, CVE-2016-3581, CVE-2016-3582, CVE-2016-3583, CVE-2016-3590, CVE-2016-3591, CVE-2016-3592, CVE-2016-3593, CVE-2016-3594, CVE-2016-3595, and CVE-2016-3596. |
| CVE-2016-3577 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-3574, CVE-2016-3575, CVE-2016-3576, CVE-2016-3578, CVE-2016-3579, CVE-2016-3580, CVE-2016-3581, CVE-2016-3582, CVE-2016-3583, CVE-2016-3590, CVE-2016-3591, CVE-2016-3592, CVE-2016-3593, CVE-2016-3594, CVE-2016-3595, and CVE-2016-3596. |
| CVE-2016-3576 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-3574, CVE-2016-3575, CVE-2016-3577, CVE-2016-3578, CVE-2016-3579, CVE-2016-3580, CVE-2016-3581, CVE-2016-3582, CVE-2016-3583, CVE-2016-3590, CVE-2016-3591, CVE-2016-3592, CVE-2016-3593, CVE-2016-3594, CVE-2016-3595, and CVE-2016-3596. |
| CVE-2016-3575 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-3574, CVE-2016-3576, CVE-2016-3577, CVE-2016-3578, CVE-2016-3579, CVE-2016-3580, CVE-2016-3581, CVE-2016-3582, CVE-2016-3583, CVE-2016-3590, CVE-2016-3591, CVE-2016-3592, CVE-2016-3593, CVE-2016-3594, CVE-2016-3595, and CVE-2016-3596. |
| CVE-2016-3574 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-3575, CVE-2016-3576, CVE-2016-3577, CVE-2016-3578, CVE-2016-3579, CVE-2016-3580, CVE-2016-3581, CVE-2016-3582, CVE-2016-3583, CVE-2016-3590, CVE-2016-3591, CVE-2016-3592, CVE-2016-3593, CVE-2016-3594, CVE-2016-3595, and CVE-2016-3596. |
| CVE-2016-3565 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Order Broker component in Oracle Retail Applications 5.1 and 5.2 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to System Administration. |
| CVE-2016-3564 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle TopLink component in Oracle Fusion Middleware 12.1.3.0, 12.2.1.0, and 12.2.1.1 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to JPA-RS. |
| CVE-2016-3561 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to SDK. |
| CVE-2016-3554 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to PC / BOM, MCAD, and Design. |
| CVE-2016-3552 | High | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 8u92 allows local users to affect confidentiality, integrity, and availability via vectors related to Install. |
| CVE-2016-3544 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Business Intelligence Enterprise Edition component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, and 11.2.1.0.0 allows remote authenticated users to affect confidentiality and integrity via vectors related to Analytics Web General. |
| CVE-2016-3539 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect integrity and availability via vectors related to File Folders / Attachment, a different vulnerability than CVE-2016-3538. |
| CVE-2016-3538 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect integrity and availability via vectors related to File Folders / Attachment, a different vulnerability than CVE-2016-3539. |
| CVE-2016-3536 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Marketing component in Oracle E-Business Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Deliverables. NOTE: the previous information is from the July 2016 CPU. Oracle has not commented on third-party claims that this issue involves multiple cross-site scripting (XSS) vulnerabilities, which allow remote attackers to inject arbitrary web script or HTML via unspecified vectors. |
| CVE-2016-3535 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle CRM Technical Foundation component in Oracle E-Business Suite 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Remote Launch. NOTE: the previous information is from the July 2016 CPU. Oracle has not commented on third-party claims that this issue is a cross-site scripting (XSS) vulnerability, which allows remote attackers to inject arbitrary web script or HTML via unspecified vectors. |
| CVE-2016-3532 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Advanced Inbound Telephony component in Oracle E-Business Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to SDK client integration. NOTE: the previous information is from the July 2016 CPU. Oracle has not commented on third-party claims that this issue involves multiple cross-site scripting (XSS) vulnerabilities, which allow remote attackers to inject arbitrary web script or HTML via unspecified vectors. |
| CVE-2016-3530 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect integrity and availability via vectors related to PGC / Import. |
| CVE-2016-3528 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Internet Expenses component in Oracle E-Business Suite 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect availability via vectors related to Expenses Admin Utilities. |
| CVE-2016-3526 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality via vectors related to SDK, a different vulnerability than CVE-2016-3529 and CVE-2016-3560. |
| CVE-2016-3522 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Web Applications Desktop Integrator component in Oracle E-Business Suite 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect confidentiality and integrity via vectors related to Application Service. |
| CVE-2016-3515 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Enterprise Communications Broker component in Oracle Communications Applications before PCz 2.0.0m4p1 allows remote attackers to affect confidentiality via unknown vectors. |
| CVE-2016-3512 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Customer Interaction History component in Oracle E-Business Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Function Security. |
| CVE-2016-3511 | High | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u101 and 8u92 allows local users to affect confidentiality, integrity, and availability via vectors related to Deployment. |
| CVE-2016-3506 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the JDBC component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2; the Oracle Retail Xstore Point of Service 5.5, 6.0, 6.5, 7.0, 7.1, 15.0, and 16.0; the Oracle Retail Warehouse Management System 14.04, 14.1.3, and 15.0.1; the Oracle Retail Workforce Management 1.60.7, and 1.64.0; the Oracle Retail Clearance Optimization Engine 13.4; the Oracle Retail Markdown Optimization 13.4 and 14.0; and Oracle Retail Merchandising System 16.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-3503 | High | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u115, 7u101, and 8u92 allows local users to affect confidentiality, integrity, and availability via vectors related to Install. |
| CVE-2016-3491 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle CRM Technical Foundation component in Oracle E-Business Suite 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Wireless Framework. NOTE: the previous information is from the July 2016 CPU. Oracle has not commented on third-party claims that this issue is a cross-site scripting (XSS) vulnerability, which allows remote attackers to inject arbitrary web script or HTML via unspecified vectors. |
| CVE-2016-3487 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Sites component in Oracle Fusion Middleware 11.1.1.8, and 12.2.1.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-3483 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53, 8.54, and 8.55 allows remote attackers to affect confidentiality and availability via vectors related to File Processing. |
| CVE-2016-3481 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the ILOM component in Oracle Sun Systems Products Suite 3.0, 3.1, and 3.2 allows remote authenticated users to affect availability via vectors related to Web. |
| CVE-2016-3479 | High | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Portable Clusterware component in Oracle Database Server 11.2.0.4 and 12.1.0.2 allows remote attackers to affect availability via unknown vectors. |
| CVE-2016-3477 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.49 and earlier, 5.6.30 and earlier, and 5.7.12 and earlier and MariaDB before 5.5.50, 10.0.x before 10.0.26, and 10.1.x before 10.1.15 allows local users to affect confidentiality, integrity, and availability via vectors related to Server: Parser. |
| CVE-2016-3471 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.45 and earlier and 5.6.26 and earlier allows local users to affect confidentiality, integrity, and availability via vectors related to Server: Option. |
| CVE-2016-3470 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Transportation Management component in Oracle Supply Chain Products Suite 6.4.1 allows remote authenticated users to affect confidentiality and integrity via vectors related to Install. |
| CVE-2016-3446 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Business Intelligence Enterprise Edition component in Oracle Fusion Middleware 11.1.1.7.0 and 11.1.1.9.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Analytics Web Administration. |
| CVE-2016-3440 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.11 and earlier allows remote authenticated users to affect availability via vectors related to Server: Optimizer. |
| CVE-2016-0635 | High | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Enterprise Manager Ops Center component in Oracle Enterprise Manager Grid Control 12.1.4, 12.2.2, and 12.3.2; the Oracle Health Sciences Information Manager component in Oracle Health Sciences Applications 1.2.8.3, 2.0.2.3, and 3.0.1.0; the Oracle Healthcare Master Person Index component in Oracle Health Sciences Applications 2.0.12, 3.0.0, and 4.0.1; the Oracle Documaker component in Oracle Insurance Applications before 12.5; the Oracle Insurance Calculation Engine component in Oracle Insurance Applications 9.7.1, 10.1.2, and 10.2.2; the Oracle Insurance Policy Administration J2EE and Oracle Insurance Rules Palette components in Oracle Insurance Applications 9.6.1, 9.7.1, 10.0.1, 10.1.2, 10.2.0, and 10.2.2; the Oracle Retail Integration Bus component in Oracle Retail Applications 15.0; the Oracle Retail Order Broker component in Oracle Retail Applications 5.1, 5.2, and 15.0; the Primavera Contract Management component in Oracle Primavera Products Suite 14.2; the Primavera P6 Enterprise Project Portfolio Management component in Oracle Primavera Products Suite 8.2, 8.3, 8.4, 15.1, 15.2, and 16.1; the Oracle Financial Services Analytical Applications Infrastructure component in Oracle Financial Services Applications 8.0.0, 8.0.1, 8.0.2, and 8.0.3; the Oracle Commerce Guided Search / Oracle Commerce Experience Manager component in Oracle Commerce 3.1.1, 3.1.2, 11.0, 11.1, and 11.2; the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5; the Oracle Communications BRM - Elastic Charging Engine 11.2.0.0.0 and 11.3.0.0.0; the Oracle Enterprise Repository Enterprise Repository 12.1.3.0.0; the Oracle Financial Services Behavior Detection Platform 8.0.1 and 8.0.2; the Oracle Hyperion Essbase 12.2.1.1; the Oracle Tuxedo System and Applications Monitor (TSAM) 11.1.1.2.0, 11.1.1.2.1, 11.1.1.2.1, 12.1.1.1.0, 12.1.3.0.0, and 12.2.2.0.0; the Oracle Communications WebRTC Session Controller component of Oracle Communications Applications (subcomponent: Security (Spring)) 7.0, 7.1 and 7.2; the Oracle Endeca Information Discovery Integrator 3.2; the Converged Commerce component of Oracle Retail Applications 16.0.1; the Oracle Identity Manager 11.1.2.3.0; Oracle Enterprise Manager for MySQL Database 12.1.0.4; Oracle Retail Invoice Matching 12.0, 13.0, 13.1, 13.2, 14.0, and 14.1; Oracle Communications Performance Intelligence Center (PIC) Software Prior to 10.2.1 and the Oracle Knowledge component of Oracle Siebel CRM (subcomponent: AnswerFlow (Spring Framework)) version 8.5.1.0 - 8.5.1.7 and 8.6.0 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-1181 | High | 2016-07-04 | Protected by Waratek | No public exploit | ActionServlet.java in Apache Struts 1 1.x through 1.3.10 mishandles multithreaded access to an ActionForm instance, which allows remote attackers to execute arbitrary code or cause a denial of service (unexpected memory access) via a multipart request, a related issue to CVE-2015-0899. |
| CVE-2016-2105 | High | 2016-05-05 | Not applicable | No public exploit | Integer overflow in the EVP_EncodeUpdate function in crypto/evp/encode.c in OpenSSL before 1.0.1t and 1.0.2 before 1.0.2h allows remote attackers to cause a denial of service (heap memory corruption) via a large amount of binary data. |
| CVE-2016-3081 | High | 2016-04-26 | Protected by Waratek | Exploited | Apache Struts 2.3.19 to 2.3.20.2, 2.3.21 to 2.3.24.1, and 2.3.25 to 2.3.28, when Dynamic Method Invocation is enabled, allow remote attackers to execute arbitrary code via method: prefix, related to chained expressions. |
| CVE-2015-5600 | High | 2015-08-03 | Not applicable | No public exploit | The kbdint_next_device function in auth2-chall.c in sshd in OpenSSH through 6.9 does not properly restrict the processing of keyboard-interactive devices within a single connection, which makes it easier for remote attackers to conduct brute-force attacks or cause a denial of service (CPU consumption) via a long and duplicative list in the ssh -oKbdInteractiveDevices option, as demonstrated by a modified client that provides a different password for each pam element on this list. |
| CVE-2015-0235 | High | 2015-01-28 | Outside Waratek scope | Working exploit published | Heap-based buffer overflow in the __nss_hostname_digits_dots function in glibc 2.2, and other 2.x versions before 2.18, allows context-dependent attackers to execute arbitrary code via vectors related to the (1) gethostbyname or (2) gethostbyname2 function, aka "GHOST." |
| CVE-2014-0224 | High | 2014-06-05 | Outside Waratek scope | Exploited | OpenSSL before 0.9.8za, 1.0.0 before 1.0.0m, and 1.0.1 before 1.0.1h does not properly restrict processing of ChangeCipherSpec messages, which allows man-in-the-middle attackers to trigger use of a zero-length master key in certain OpenSSL-to-OpenSSL communications, and consequently hijack sessions or obtain sensitive information, via a crafted TLS handshake, aka the "CCS Injection" vulnerability. |