
Oracle Critical Patch Update October 2015
Released October 2015 · Oracle's advisory ↗ · ← Critical Patch Update, July 2015 · Critical Patch Update, January 2016 →
140 CVEs in this release, one square each
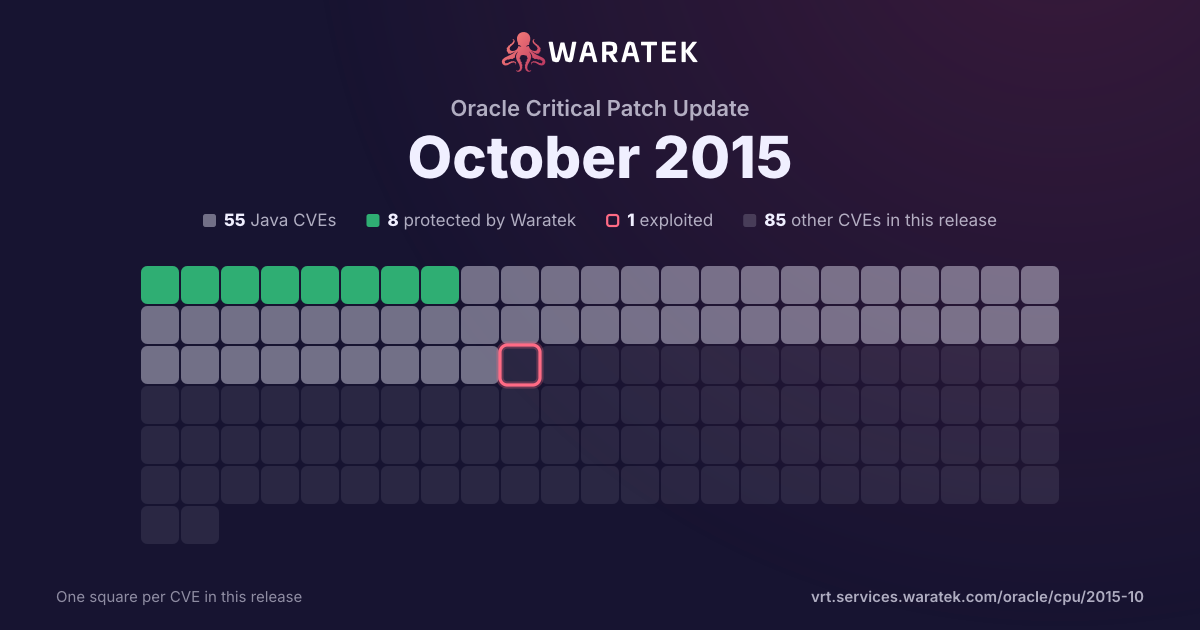
By status
8Protected by Waratek3Mitigation candidate44No exploit published34Outside Waratek scope51Not applicable
1Exploited, marked by the ring
No exploit published. For 44 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 140 matches · 55 in Waratek scope · 8 protected · 1 exploited · 1 CISA KEV · 8 public PoC · 5 EPSS ≥ 0.5
140matches
55in Waratek scope39.3%
8protected5.7%
1exploited0.7%
1CISA KEV0.7%
8public PoC5.7%
5EPSS ≥ 0.53.6%
Protected by Waratek
8
5.7%
Rule in development
0
0.0%
Mitigation candidate
3
2.1%
No exploit published
44
31.4%
Outside Waratek scope
34
24.3%
Not applicable
51
36.4%
Withdrawn CVE
0
0.0%
blocked by ARMR today
8
5.7%
partly blocked
0
0.0%
not blocked
132
94.3%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 136 / year
19991
Not applicable1
Medium1
not blocked1
No public exploit1
20000
20010
20020
20030
20040
20050
20060
20070
20080
20090
20101
Protected by Waratek1
Medium1
blocked by ARMR today1
Working exploit published1
20110
20120
20130
20142
Mitigation candidate1
Not applicable1
High2
not blocked2
Working exploit published1
No public exploit1
2015136
Protected by Waratek7
Mitigation candidate2
No exploit published44
Outside Waratek scope34
Not applicable49
High24
Medium81
Low31
blocked by ARMR today7
not blocked129
Exploited1
Working exploit published5
Proof of concept only1
No public exploit129
199920012003200520072009201120132015
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-4809 | Low | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows local users to affect availability via vectors related to Outside In PDF Export SDK, a different vulnerability than CVE-2015-4811. |
| CVE-2015-4807 | Low | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.45 and earlier and 5.6.26 and earlier, when running on Windows, allows remote authenticated users to affect availability via unknown vectors related to Server : Query Cache. |
| CVE-2015-4806 | Medium | 2015-10-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u101, 7u85, and 8u60, and Java SE Embedded 8u51, allows remote attackers to affect confidentiality and integrity via unknown vectors related to Libraries. |
| CVE-2015-4805 | High | 2015-10-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u101, 7u85, and 8u60, and Java SE Embedded 8u51, allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Serialization. |
| CVE-2015-4804 | Medium | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM Talent Acquisition Management component in Oracle PeopleSoft Products 9.2 allows remote authenticated users to affect confidentiality via unknown vectors related to Security. |
| CVE-2015-4803 | Medium | 2015-10-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u101, 7u85, and 8u60; Java SE Embedded 8u51; and JRockit R28.3.7 allows remote attackers to affect availability via vectors related to JAXP, a different vulnerability than CVE-2015-4893 and CVE-2015-4911. |
| CVE-2015-4802 | Medium | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.45 and earlier and 5.6.26 and earlier allows remote authenticated users to affect availability via unknown vectors related to Server : Partition, a different vulnerability than CVE-2015-4792. |
| CVE-2015-4801 | Low | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.2 allows local users to affect confidentiality via unknown vectors related to Solaris Kernel Zones. |
| CVE-2015-4800 | Medium | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.26 and earlier allows remote authenticated users to affect availability via unknown vectors related to Server : Optimizer. |
| CVE-2015-4799 | Medium | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Sites component in Oracle Fusion Middleware 7.6.2, 11.1.1.6.1, and 11.1.1.8.0 allows remote attackers to affect integrity via unknown vectors related to Security. |
| CVE-2015-4798 | High | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Technology Stack component in Oracle E-Business Suite 11.5.10.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to DB Listener, a different vulnerability than CVE-2015-4839. |
| CVE-2015-4797 | Low | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.3 allows remote authenticated users to affect integrity via unknown vectors related to Security. |
| CVE-2015-4796 | High | 2015-10-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java VM component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2, when running on Windows, allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2015-4888. |
| CVE-2015-4795 | High | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Utilities Work and Asset Management component in Oracle Industry Applications 1.9.1.1.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Add-On Applications. |
| CVE-2015-4794 | High | 2015-10-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java VM component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2015-4793 | Medium | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Communications Convergence component in Oracle Communications Applications 2.0 and 3.0.1 allows remote attackers to affect confidentiality via unknown vectors related to Mail Proxy. |
| CVE-2015-4792 | Low | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.45 and earlier and 5.6.26 and earlier allows remote authenticated users to affect availability via unknown vectors related to Server : Partition, a different vulnerability than CVE-2015-4802. |
| CVE-2015-4791 | Low | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.26 and earlier allows remote authenticated users to affect availability via unknown vectors related to Server : Security : Privileges. |
| CVE-2015-4766 | Low | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.25 and earlier allows local users to affect availability via unknown vectors related to Server : Security : Firewall. |
| CVE-2015-4762 | Medium | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications DBA component in Oracle E-Business Suite 12.2.3 and 12.2.4 allows remote authenticated users to affect confidentiality via unknown vectors related to Online patching. |
| CVE-2015-4734 | Medium | 2015-10-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u101, 7u85 and 8u60, and Java SE Embedded 8u51, allows remote attackers to affect confidentiality via vectors related to JGSS. |
| CVE-2015-4730 | Medium | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.20 and earlier allows remote authenticated users to affect availability via unknown vectors related to Types. |
| CVE-2015-2642 | Medium | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.2 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Gzip. |
| CVE-2015-2633 | Low | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Ops Center component in Oracle Enterprise Manager Grid Control 12.1.0.1 and 12.2.2 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Ops Center. |
| CVE-2015-2608 | High | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in (1) the Oracle Communications Diameter Signaling Router (DSR) component in Oracle Communications Applications 4.1.6 and earlier, 5.1.0 and earlier, 6.0.2 and earlier, and 7.1.0 and earlier; (2) the Oracle Communications Performance Intelligence Center Software component in Oracle Communications Applications 9.0.3 and earlier and 10.1.5 and earlier; (3) the Oracle Communications Policy Management component in Oracle Communications Applications 9.9.0 and earlier, 10.5.0 and earlier, 11.5.0 and earlier, and 12.1.0 and earlier; and (4) the Oracle Communications Tekelec HLR Router component in Oracle Communications Applications 4.0.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to PMAC. |
| CVE-2015-1829 | Medium | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle HTTP Server component in Oracle Fusion Middleware 10.1.3.5, 11.1.1.7, 11.1.1.9, 12.1.2.0, and 12.1.3.0 allows remote attackers to affect availability via unknown vectors related to Web Listener. |
| CVE-2014-3576 | High | 2015-08-14 | Protected by Waratek | No public exploit | The processControlCommand function in broker/TransportConnection.java in Apache ActiveMQ before 5.11.0 allows remote attackers to cause a denial of service (shutdown) via a shutdown command. |
| CVE-2015-1793 | Medium | 2015-07-09 | Outside Waratek scope | Working exploit published | The X509_verify_cert function in crypto/x509/x509_vfy.c in OpenSSL 1.0.1n, 1.0.1o, 1.0.2b, and 1.0.2c does not properly process X.509 Basic Constraints cA values during identification of alternative certificate chains, which allows remote attackers to spoof a Certification Authority role and trigger unintended certificate verifications via a valid leaf certificate. |
| CVE-2015-1791 | Medium | 2015-06-12 | Not applicable | No public exploit | Race condition in the ssl3_get_new_session_ticket function in ssl/s3_clnt.c in OpenSSL before 0.9.8zg, 1.0.0 before 1.0.0s, 1.0.1 before 1.0.1n, and 1.0.2 before 1.0.2b, when used for a multi-threaded client, allows remote attackers to cause a denial of service (double free and application crash) or possibly have unspecified other impact by providing a NewSessionTicket during an attempt to reuse a ticket that had been obtained earlier. |
| CVE-2015-4000 | Low | 2015-05-21 | Outside Waratek scope | Proof of concept only | The TLS protocol 1.2 and earlier, when a DHE_EXPORT ciphersuite is enabled on a server but not on a client, does not properly convey a DHE_EXPORT choice, which allows man-in-the-middle attackers to conduct cipher-downgrade attacks by rewriting a ClientHello with DHE replaced by DHE_EXPORT and then rewriting a ServerHello with DHE_EXPORT replaced by DHE, aka the "Logjam" issue. |
| CVE-2015-3144 | High | 2015-04-24 | Outside Waratek scope | No public exploit | The fix_hostname function in cURL and libcurl 7.37.0 through 7.41.0 does not properly calculate an index, which allows remote attackers to cause a denial of service (out-of-bounds read or write and crash) or possibly have other unspecified impact via a zero-length host name, as demonstrated by "http://:80" and ":80." |
| CVE-2015-0286 | Medium | 2015-03-19 | Not applicable | No public exploit | The ASN1_TYPE_cmp function in crypto/asn1/a_type.c in OpenSSL before 0.9.8zf, 1.0.0 before 1.0.0r, 1.0.1 before 1.0.1m, and 1.0.2 before 1.0.2a does not properly perform boolean-type comparisons, which allows remote attackers to cause a denial of service (invalid read operation and application crash) via a crafted X.509 certificate to an endpoint that uses the certificate-verification feature. |
| CVE-2015-0235 | High | 2015-01-28 | Outside Waratek scope | Working exploit published | Heap-based buffer overflow in the __nss_hostname_digits_dots function in glibc 2.2, and other 2.x versions before 2.18, allows context-dependent attackers to execute arbitrary code via vectors related to the (1) gethostbyname or (2) gethostbyname2 function, aka "GHOST." |
| CVE-2014-7940 | High | 2015-01-22 | Not applicable | No public exploit | The collator implementation in i18n/ucol.cpp in International Components for Unicode (ICU) 52 through SVN revision 293126, as used in Google Chrome before 40.0.2214.91, does not initialize memory for a data structure, which allows remote attackers to cause a denial of service or possibly have unspecified other impact via a crafted character sequence. |
| CVE-2014-0191 | Medium | 2015-01-21 | Not applicable | No public exploit | The xmlParserHandlePEReference function in parser.c in libxml2 before 2.9.2, as used in Web Listener in Oracle HTTP Server in Oracle Fusion Middleware 11.1.1.7.0, 12.1.2.0, and 12.1.3.0 and other products, loads external parameter entities regardless of whether entity substitution or validation is enabled, which allows remote attackers to cause a denial of service (resource consumption) via a crafted XML document. |
| CVE-2014-3571 | Medium | 2015-01-09 | Not applicable | No public exploit | OpenSSL before 0.9.8zd, 1.0.0 before 1.0.0p, and 1.0.1 before 1.0.1k allows remote attackers to cause a denial of service (NULL pointer dereference and application crash) via a crafted DTLS message that is processed with a different read operation for the handshake header than for the handshake body, related to the dtls1_get_record function in d1_pkt.c and the ssl3_read_n function in s3_pkt.c. |
| CVE-2014-1569 | High | 2014-12-15 | Not applicable | No public exploit | The definite_length_decoder function in lib/util/quickder.c in Mozilla Network Security Services (NSS) before 3.16.2.4 and 3.17.x before 3.17.3 does not ensure that the DER encoding of an ASN.1 length is properly formed, which allows remote attackers to conduct data-smuggling attacks by using a long byte sequence for an encoding, as demonstrated by the SEC_QuickDERDecodeItem function's improper handling of an arbitrary-length encoding of 0x00. |
| CVE-2014-0050 | High | 2014-04-01 | Mitigation candidate | Working exploit published | MultipartStream.java in Apache Commons FileUpload before 1.3.1, as used in Apache Tomcat, JBoss Web, and other products, allows remote attackers to cause a denial of service (infinite loop and CPU consumption) via a crafted Content-Type header that bypasses a loop's intended exit conditions. |
| CVE-2010-1622 | Medium | 2010-06-21 | Protected by Waratek | Working exploit published | SpringSource Spring Framework 2.5.x before 2.5.6.SEC02, 2.5.7 before 2.5.7.SR01, and 3.0.x before 3.0.3 allows remote attackers to execute arbitrary code via an HTTP request containing class.classLoader.URLs[0]=jar: followed by a URL of a crafted .jar file. |
| CVE-1999-0377 | Medium | 1999-02-22 | Not applicable | No public exploit | Process table attack in Unix systems allows a remote attacker to perform a denial of service by filling a machine's process tables through multiple connections to network services. |