
Oracle Critical Patch Update July 2015
Released July 2015 · Oracle's advisory ↗ · ← Critical Patch Update, April 2015 · Critical Patch Update, October 2015 →
171 CVEs in this release, one square each
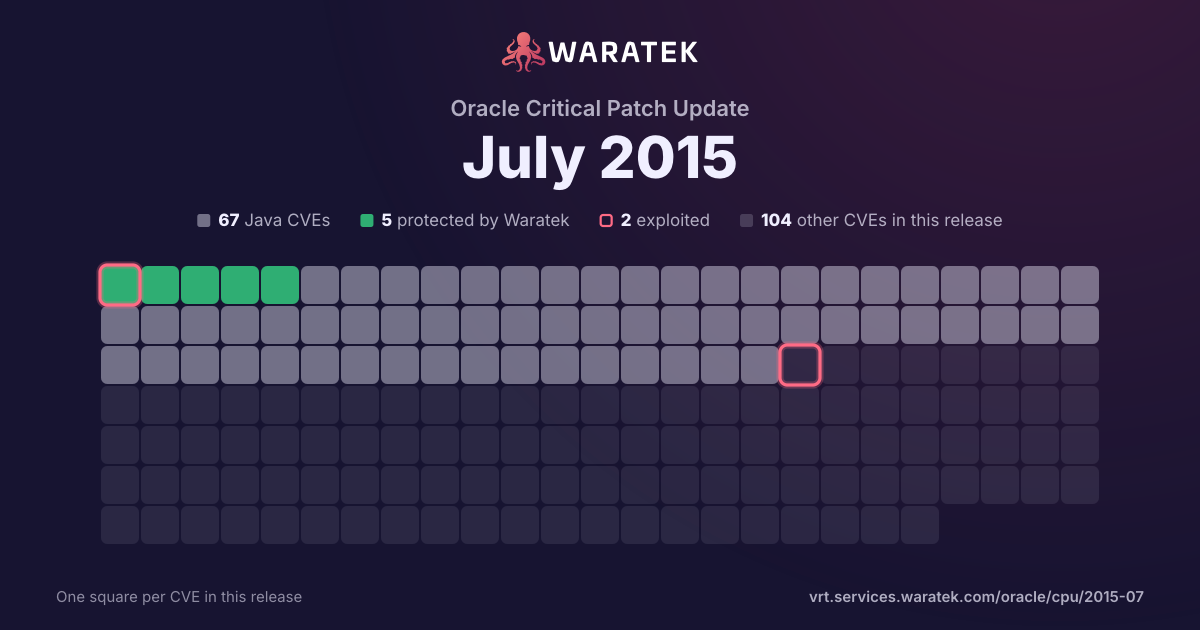
By status
5Protected by Waratek62No exploit published36Outside Waratek scope68Not applicable
2Exploited, marked by the ring
No exploit published. For 60 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 67 matches · 5 protected · 1 exploited · 1 CISA KEV · 2 public PoC · 1 EPSS ≥ 0.5
Protected by Waratek
5
7.5%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
62
92.5%
blocked by ARMR today
5
7.5%
partly blocked
0
0.0%
not blocked
62
92.5%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
1.5%
Working exploit published
0
0.0%
Proof of concept only
1
1.5%
Forecast only
0
0.0%
No public exploit
65
97.0%
split by
peak 64 / quarter
Q3 131
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q4 131
Protected by Waratek1
High1
blocked by ARMR today1
Proof of concept only1
Q1 140
Q2 140
Q3 140
Q4 140
Q1 150
Q2 151
No exploit published1
High1
not blocked1
No public exploit1
Q3 1564
Protected by Waratek3
No exploit published61
High10
Medium42
Low12
blocked by ARMR today3
not blocked61
No public exploit64
Q3 13Q4 13Q1 14Q2 14Q3 14Q4 14Q1 15Q2 15Q3 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-4773 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Common Security component in Oracle Hyperion 11.1.2.2, 11.1.2.3, and 11.1.2.4 allows remote authenticated users to affect availability via unknown vectors related to User Account Update. |
| CVE-2015-4768 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Transportation Management component in Oracle Supply Chain Products Suite 6.1, 6.2, 6.3.0, 6.3.1, 6.3.2, 6.3.3, 6.3.4, 6.3.5, 6.3.6, and 6.3.7 allows remote authenticated users to affect confidentiality via unknown vectors related to Diagnostics. |
| CVE-2015-4765 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Manager component in Oracle E-Business Suite 12.1.3, 12.2.3, and 12.2.4 allows remote authenticated users to affect integrity via vectors related to OAM Dashboard. |
| CVE-2015-4763 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Security. |
| CVE-2015-4759 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality based on Trillium, a different vulnerability than CVE-2015-0443, CVE-2015-0444, CVE-2015-0445, CVE-2015-0446, CVE-2015-2634, CVE-2015-2635, CVE-2015-2636, and CVE-2015-4758. |
| CVE-2015-4758 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality based on Trillium, a different vulnerability than CVE-2015-0443, CVE-2015-0444, CVE-2015-0445, CVE-2015-0446, CVE-2015-2634, CVE-2015-2635, CVE-2015-2636, and CVE-2015-4759. |
| CVE-2015-4751 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Access Manager component in Oracle Fusion Middleware 11.1.1.7 and 11.1.2.2 allows remote attackers to affect availability via unknown vectors related to Authentication Engine. |
| CVE-2015-4749 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45; JRockit R28.3.6; and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect availability via vectors related to JNDI. |
| CVE-2015-4748 | High | 2015-07-16 | Protected by Waratek | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45; JRockit R28.3.6; and Java SE Embedded 7u75 and Embedded 8u33 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Security. |
| CVE-2015-4747 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Event Processing component in Oracle Fusion Middleware 11.1.1.7 and 12.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to CEP system. |
| CVE-2015-4746 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile Product Lifecycle Management for Process component in Oracle Supply Chain Products Suite 6.0.0.7, 6.1.0.3, 6.1.1.5, and 6.2.0.0 allows remote authenticated users to affect confidentiality via unknown vectors related to Global Spec Management. |
| CVE-2015-4745 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Information Discovery Studio component in Oracle Fusion Middleware 2.2.2, 2.3, 2.4, 3.0, and 3.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Integrator, a different vulnerability than CVE-2015-2602, CVE-2015-2603, CVE-2015-2604, CVE-2015-2605, and CVE-2015-2606. |
| CVE-2015-4744 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle GlassFish Server component in Oracle Fusion Middleware 2.1.1, 3.0.1, and 3.1.2; and the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.1.0, 12.1.2.0, and 12.1.3.0 allows remote attackers to affect integrity via unknown vectors related to Java Server Faces. |
| CVE-2015-4743 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications DBA component in Oracle E-Business Suite 12.2.3 allows remote authenticated users to affect confidentiality via unknown vectors related to AD Utilities. |
| CVE-2015-4742 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle JDeveloper component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.2.4.0, 12.1.2.0.0, and 12.1.3.0.0 allows remote attackers to affect availability via vectors related to ADF Faces. |
| CVE-2015-4741 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 12.2.4 allows remote authenticated users to affect integrity via unknown vectors related to Dialog popup. |
| CVE-2015-4739 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 11.5.10.2 allows remote authenticated users to affect integrity via unknown vectors related to Help screens. |
| CVE-2015-4738 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM Candidate Gateway component in Oracle PeopleSoft Products 9.1 and 9.2 allows remote authenticated users to affect confidentiality via unknown vectors related to Security. |
| CVE-2015-4735 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager for Oracle Database component in Oracle Enterprise Manager Grid Control EM Base Platform 11.1.0.1, and EM DB Control 11.2.0.3 and 11.2.0.4, allows remote attackers to affect confidentiality via vectors related to RAC Management. |
| CVE-2015-4728 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Sourcing component in Oracle E-Business Suite 12.1.1, 12.1.2, 12.1.3, 12.2.3, and 12.2.4 allows remote authenticated users to affect confidentiality via unknown vectors related to Bid/Quote creation. |
| CVE-2015-2663 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Transportation Management component in Oracle Supply Chain Products Suite 6.1, 6.2, and 6.3.0 through 6.3.7 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Business Process Automation. |
| CVE-2015-2660 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 allows remote authenticated users to affect confidentiality and integrity via vectors related to Oracle Agile PLM Framework. |
| CVE-2015-2659 | Medium | 2015-07-16 | Protected by Waratek | No public exploit | Unspecified vulnerability in Oracle Java SE 8u45 and Java SE Embedded 8u33 allows remote attackers to affect availability via unknown vectors related to Security. |
| CVE-2015-2658 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Web Cache component in Oracle Fusion Middleware 11.1.1.7.0 allows remote attackers to affect confidentiality via vectors related to SSL/TLS Support. |
| CVE-2015-2657 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Transportation Management component in Oracle Supply Chain Products Suite 6.1, 6.2, and 6.3.0 through 6.3.7 allows remote authenticated users to affect confidentiality via unknown vectors related to Business Process Automation. |
| CVE-2015-2653 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager component in Oracle Commerce Platform 3.1.1, 3.1.2, 11.0, and 11.1 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Content Acquisition System. |
| CVE-2015-2652 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Marketing component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.1, 12.1.2, 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect integrity via unknown vectors related to Web Management. |
| CVE-2015-2650 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53 and 8.54 allows remote authenticated users to affect confidentiality via unknown vectors related to Multichannel Framework. |
| CVE-2015-2649 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel UI Framework component in Oracle Siebel CRM 8.1.1, 8.22, and 15.0 allows remote authenticated users to affect confidentiality via vectors related to UIF Open UI. |
| CVE-2015-2647 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager for Oracle Database component in Oracle Enterprise Manager Grid Control EM Base Platform 11.1.0.1; EM Plugin for DB 12.1.0.5, 12.1.0.6, 12.1.0.7; and EM DB Control 11.1.0.7, 11.2.0.3, and 11.2.0.4 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Content Management. |
| CVE-2015-2646 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager for Oracle Database component in Oracle Enterprise Manager Grid Control EM Base Platform: 11.1.0.1; EM Plugin for DB: 12.1.0.5, 12.1.0.6, 12.1.0.7; EM DB Control: 11.1.0.7, 11.2.0.3, and 11.2.0.4 allows remote attackers to affect integrity via unknown vectors related to Content Management. |
| CVE-2015-2645 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Web Applications Desktop Integrator component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote authenticated users to affect integrity via unknown vectors. |
| CVE-2015-2644 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM Framework component in Oracle Supply Chain Products Suite 9.3.3 allows remote attackers to affect confidentiality via unknown vectors related to Security. |
| CVE-2015-2636 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality based on Trillium, a different vulnerability than CVE-2015-0443, CVE-2015-0444, CVE-2015-0445, CVE-2015-0446, CVE-2015-2634, CVE-2015-2635, CVE-2015-4758, and CVE-2015-4759. |
| CVE-2015-2635 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality based on Trillium, a different vulnerability than CVE-2015-0443, CVE-2015-0444, CVE-2015-0445, CVE-2015-0446, CVE-2015-2634, CVE-2015-2636, CVE-2015-4758, and CVE-2015-4759. |
| CVE-2015-2634 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality based on Trillium, a different vulnerability than CVE-2015-0443, CVE-2015-0444, CVE-2015-0445, CVE-2015-0446, CVE-2015-2635, CVE-2015-2636, CVE-2015-4758, and CVE-2015-4759. |
| CVE-2015-2630 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Technology stack component in Oracle E-Business Suite 11.5.10.2, 12.0.6, and 12.1.3 allows remote attackers to affect integrity via unknown vectors related to Applet startup. |
| CVE-2015-2623 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle GlassFish Server component in Oracle Fusion Middleware 3.0.1 and 3.1.2, and the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.1.0, 12.1.2.0, and 12.1.3.0, allows remote attackers to affect integrity via unknown vectors related to Java Server Faces. |
| CVE-2015-2622 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.54 allows remote attackers to affect integrity via unknown vectors related to Fluid Core. |
| CVE-2015-2618 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote authenticated users to affect integrity via unknown vectors related to Input validation. |
| CVE-2015-2615 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 12.0.6, 12.1.3, and 12.2.3 allows remote attackers to affect confidentiality via unknown vectors related to Portal. |
| CVE-2015-2612 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Core - Server OM Svcs component in Oracle Siebel CRM 8.1.1, 8.2.2, and 15.0 allows remote attackers to affect confidentiality via vectors related to LDAP Security Adapter. |
| CVE-2015-2610 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect integrity via unknown vectors related to Popup windows. |
| CVE-2015-2607 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager component in Oracle Commerce Platform 3.0.2, 3.1.1, 3.1.2, 11.0, and 11.1 allows remote attackers to affect confidentiality via unknown vectors related to Content Acquisition System. |
| CVE-2015-2606 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Information Discovery Studio component in Oracle Fusion Middleware 2.2.2, 2.3, 2.4, 3.0, and 3.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Integrator, a different vulnerability than CVE-2015-2602, CVE-2015-2603, CVE-2015-2604, CVE-2015-2605, and CVE-2015-4745. |
| CVE-2015-2605 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Information Discovery Studio component in Oracle Fusion Middleware 2.2.2, 2.3, 2.4, 3.0, and 3.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Integrator, a different vulnerability than CVE-2015-2602, CVE-2015-2603, CVE-2015-2604, CVE-2015-2606, and CVE-2015-4745. |
| CVE-2015-2604 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Information Discovery Studio component in Oracle Fusion Middleware 2.2.2, 2.3, 2.4, 3.0, and 3.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Integrator, a different vulnerability than CVE-2015-2602, CVE-2015-2603, CVE-2015-2605, CVE-2015-2606, and CVE-2015-4745. |
| CVE-2015-2603 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Information Discovery Studio component in Oracle Fusion Middleware 2.2.2, 2.3, 2.4, 3.0, and 3.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Integrator, a different vulnerability than CVE-2015-2602, CVE-2015-2604, CVE-2015-2605, CVE-2015-2606, and CVE-2015-4745. |
| CVE-2015-2602 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Information Discovery Studio component in Oracle Fusion Middleware 2.2.2, 2.3, 2.4, 3.0, and 3.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Integrator, a different vulnerability than CVE-2015-2603, CVE-2015-2604, CVE-2015-2605, CVE-2015-2606, and CVE-2015-4745. |
| CVE-2015-2601 | Medium | 2015-07-16 | Protected by Waratek | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45, JRockit R28.3.6, and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect confidentiality via vectors related to JCE. |
| CVE-2015-2600 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Core - Server OM Svcs component in Oracle Siebel CRM 8.1.1, 8.2.2, and 15.0 allows remote authenticated users to affect confidentiality via unknown vectors related to Security. |
| CVE-2015-2598 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the mobile app in Oracle Business Intelligence Enterprise Edition in Oracle Fusion Middleware before 11.1.1.7.0 (11.6.39) allows remote authenticated users to affect integrity via unknown vectors related to Mobile - iPad. |
| CVE-2015-2593 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Access Manager component in Oracle Fusion Middleware 11.1.2.2 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Configuration Service. |
| CVE-2015-2592 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Enterprise Performance Management Architect component in Oracle Hyperion 11.1.2.2 and 11.1.2.3 allows remote authenticated users to affect integrity via unknown vectors related to Security, a different vulnerability than CVE-2015-2584. |
| CVE-2015-2591 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise Portal - Interaction Hub component in Oracle PeopleSoft Products 9.1.00 allows remote authenticated users to affect integrity via unknown vectors related to Enterprise Portal. |
| CVE-2015-2588 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53 and 8.54 allows remote attackers to affect integrity via vectors related to PIA Core Technology. |
| CVE-2015-2587 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel UI Framework component in Oracle Siebel CRM 8.1.1, 8.2.2, and 15.0 allows remote attackers to affect integrity via vectors related to SWSE Server Infrastructure. |
| CVE-2015-2584 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Enterprise Performance Management Architect component in Oracle Hyperion 11.1.2.2 and 11.1.2.3 allows remote authenticated users to affect integrity via unknown vectors related to Security, a different vulnerability than CVE-2015-2592. |
| CVE-2015-1926 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Portal component in Oracle Fusion Middleware 11.1.1.8.0 and 11.1.1.9.0, and the Oracle Applications Framework component in Oracle E-Business Suite 12.2.3 and 12.2.4, allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Portal. |
| CVE-2015-0467 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM Talent Acquisition Manager component in Oracle PeopleSoft Products 9.1 and 9.2 allows remote attackers to affect integrity via unknown vectors related to Security. |
| CVE-2015-0446 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality based on Trillium, a different vulnerability than CVE-2015-0443, CVE-2015-0444, CVE-2015-0445, CVE-2015-2634, CVE-2015-2635, CVE-2015-2636, CVE-2015-4758, and CVE-2015-4759. |
| CVE-2015-0445 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality based on Trillium, a different vulnerability than CVE-2015-0443, CVE-2015-0444, CVE-2015-0446, CVE-2015-2634, CVE-2015-2635, CVE-2015-2636, CVE-2015-4758, and CVE-2015-4759. |
| CVE-2015-0444 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality based on Trillium, a different vulnerability than CVE-2015-0443, CVE-2015-0445, CVE-2015-0446, CVE-2015-2634, CVE-2015-2635, CVE-2015-2636, CVE-2015-4758, and CVE-2015-4759. |
| CVE-2015-0443 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality based on Trillium, a different vulnerability than CVE-2015-0444, CVE-2015-0445, CVE-2015-0446, CVE-2015-2634, CVE-2015-2635, CVE-2015-2636, CVE-2015-4758, and CVE-2015-4759. |
| CVE-2014-0230 | High | 2015-06-07 | No exploit published | No public exploit | Apache Tomcat 6.x before 6.0.44, 7.x before 7.0.55, and 8.x before 8.0.9 does not properly handle cases where an HTTP response occurs before finishing the reading of an entire request body, which allows remote attackers to cause a denial of service (thread consumption) via a series of aborted upload attempts. |
| CVE-2013-2186 | High | 2013-10-28 | Protected by Waratek | Proof of concept only | The DiskFileItem class in Apache Commons FileUpload, as used in Red Hat JBoss BRMS 5.3.1; JBoss Portal 4.3 CP07, 5.2.2, and 6.0.0; and Red Hat JBoss Web Server 1.0.2 allows remote attackers to write to arbitrary files via a NULL byte in a file name in a serialized instance. |
| CVE-2013-2251 | Critical | 2013-07-20 | Protected by Waratek | Exploited | Apache Struts 2.0.0 through 2.3.15 allows remote attackers to execute arbitrary OGNL expressions via a parameter with a crafted (1) action:, (2) redirect:, or (3) redirectAction: prefix. |