
Oracle Critical Patch Update October 2015
Released October 2015 · Oracle's advisory ↗ · ← Critical Patch Update, July 2015 · Critical Patch Update, January 2016 →
140 CVEs in this release, one square each
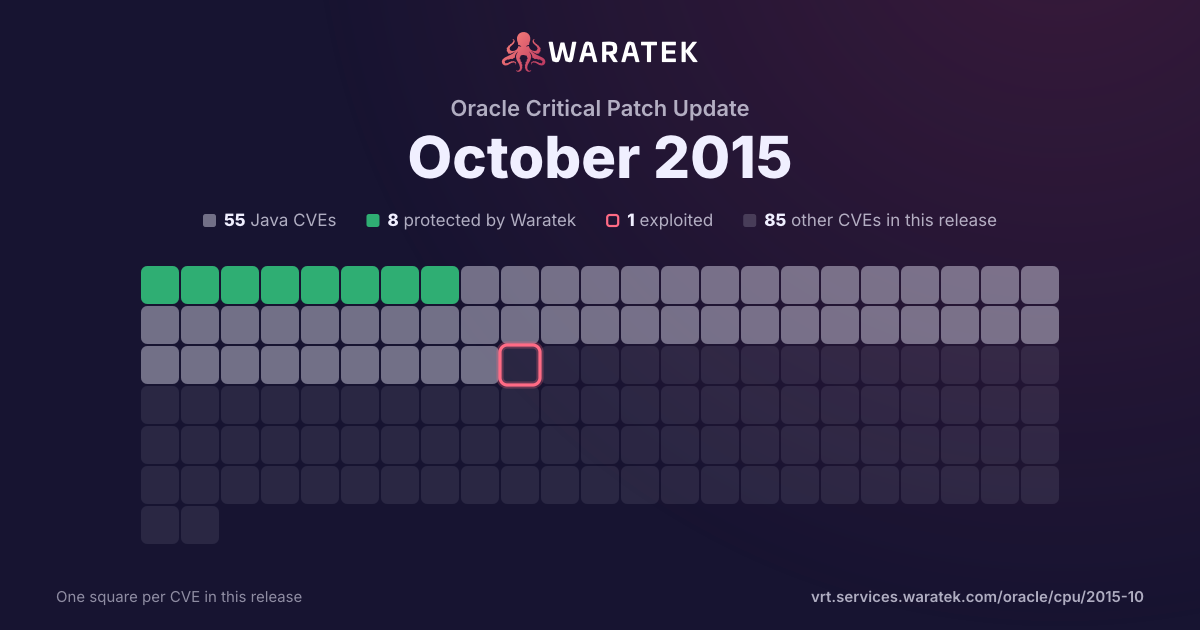
By status
8Protected by Waratek3Mitigation candidate44No exploit published34Outside Waratek scope51Not applicable
1Exploited, marked by the ring
No exploit published. For 44 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 12 matches · 4 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
Protected by Waratek
4
33.3%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
8
66.7%
blocked by ARMR today
4
33.3%
partly blocked
0
0.0%
not blocked
8
66.7%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
12
100.0%
split by
peak 12 / month
Oct 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-4898 | Medium | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote authenticated users to affect integrity via vectors related to Diagnostics and DMZ. |
| CVE-2015-4886 | Medium | 2015-10-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Oracle Report Manager component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Reports Security. NOTE: the previous information is from the October 2015 CPU. Oracle has not commented on third-party claims that this issue is an XML External Entity (XXE) vulnerability, which allows remote attackers to read arbitrary files, cause a denial of service, or conduct SMB Relay attacks via a crafted DTD in an XML request involving the OA_HTML/copxml servlet. |
| CVE-2015-4884 | Medium | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality via unknown vectors related to Single Signon. |
| CVE-2015-4865 | Low | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 12.1.3, 12.2.3, and 12.2.4 allows remote authenticated users to affect confidentiality via vectors related to Business Objects - BC4J. |
| CVE-2015-4854 | Medium | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect integrity via unknown vectors related to Single Signon. NOTE: the previous information is from the October 2015 CPU. Oracle has not commented on third-party claims that this issue is a cross-site scripting (XSS) vulnerability, which allows remote attackers to inject arbitrary web script or HTML via the Domain parameter in the CfgOCIReturn servlet. |
| CVE-2015-4851 | Medium | 2015-10-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Oracle iSupplier Portal component in Oracle E-Business Suite 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to XML input. NOTE: the previous information is from the October 2015 CPU. Oracle has not commented on third-party claims that this issue is an XML External Entity (XXE) vulnerability, which allows remote attackers to read arbitrary files, cause a denial of service, or conduct SMB Relay attacks via a crafted DTD in an XML request to OA_HTML/oramipp_lpr. |
| CVE-2015-4849 | Medium | 2015-10-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Oracle Payments component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Punch-in. NOTE: the previous information is from the October 2015 CPU. Oracle has not commented on third-party claims that this issue is an XML External Entity (XXE) vulnerability, which allows remote attackers to cause a denial of service or conduct SMB Relay attacks via a crafted DTD in an XML request to OA_HTML/IspPunchInServlet. |
| CVE-2015-4846 | Low | 2015-10-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Oracle Applications Manager component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote authenticated users to affect confidentiality and integrity via vectors related to SQL Extensions. NOTE: the previous information is from the October 2015 CPU. Oracle has not commented on third-party claims that this issue is a SQL injection vulnerability, which allows remote authenticated users to execute arbitrary SQL commands via a request involving the afamexts.sql SQL extension. |
| CVE-2015-4845 | Medium | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality via vectors related to Java APIs - AOL/J. NOTE: the previous information is from the October 2015 CPU. Oracle has not commented on third-party claims that this issue allows remote attackers to enumerate database users via a series of requests to Aoljtest.js. |
| CVE-2015-4839 | High | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Technology Stack component in Oracle E-Business Suite 11.5.10.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to DB Listener, a different vulnerability than CVE-2015-4798. |
| CVE-2015-4798 | High | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Technology Stack component in Oracle E-Business Suite 11.5.10.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to DB Listener, a different vulnerability than CVE-2015-4839. |
| CVE-2015-4762 | Medium | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications DBA component in Oracle E-Business Suite 12.2.3 and 12.2.4 allows remote authenticated users to affect confidentiality via unknown vectors related to Online patching. |