
Oracle Critical Patch Update July 2013
Released July 2013 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, June 2013 · Critical Patch Update, October 2013 →
89 CVEs in this release, one square each
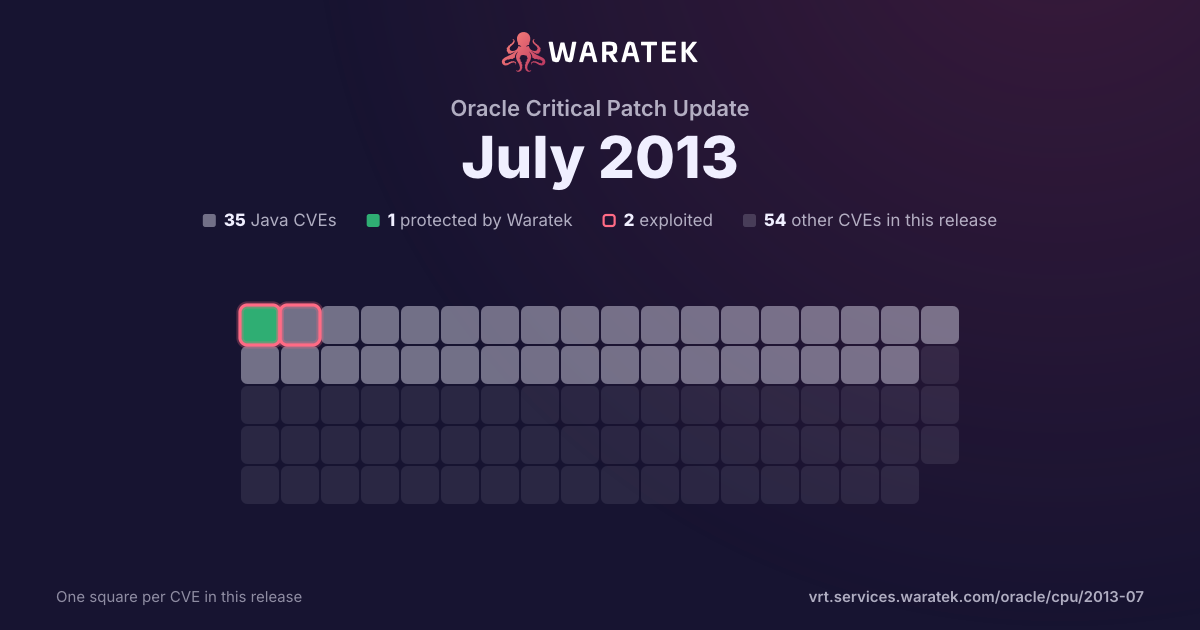
By status
1Protected by Waratek3Mitigation candidate31No exploit published8Outside Waratek scope46Not applicable
2Exploited, marked by the ring
No exploit published. For 31 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 10 matches · 0 protected · 1 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
1
10.0%
No exploit published
9
90.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
9
90.0%
not established
1
10.0%
unrecorded
0
0.0%
Exploited
1
10.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
9
90.0%
split by
peak 10 / month
Jul 13
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2013-3821 | Medium | 2013-07-17 | Mitigation candidate | Exploited | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.51, 8.52, and 8.53 allows remote attackers to affect confidentiality and availability via unknown vectors related to Integration Broker. |
| CVE-2013-3820 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.51, 8.52, and 8.53 allows remote attackers to affect availability via unknown vectors related to Business Interlink. |
| CVE-2013-3819 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.51, 8.52, and 8.53 allows remote attackers to affect confidentiality and availability via unknown vectors related to Mobile Applications. |
| CVE-2013-3818 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.51, 8.52, and 8.53 allows remote attackers to affect integrity via unknown vectors related to Portal, a different vulnerability than CVE-2013-2404. |
| CVE-2013-3800 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.51, 8.52, and 8.53 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Business Interlinks. |
| CVE-2013-3784 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HRMS component in Oracle PeopleSoft Products 9.1 allows remote authenticated users to affect confidentiality and integrity via unknown vectors Time and Labor. |
| CVE-2013-3780 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise Portal component in Oracle PeopleSoft Products 9.1 allows remote authenticated users to affect confidentiality via unknown vectors related to Saved Search. |
| CVE-2013-3768 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.51, 8.52, and 8.53 allows remote attackers to affect integrity via unknown vectors related to Rich Text Editor. |
| CVE-2013-3761 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products Portal 9.1 and PeopleTools 8.52 allows remote attackers to affect integrity via vectors related to PIA Core Technology. |
| CVE-2013-3759 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.52 and 8.53 allows remote attackers to affect integrity via vectors related to PIA Search Functionality. |