
Java SE CPU Jun 2013
Released June 2013 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, April 2013 · Critical Patch Update, July 2013 →
40 CVEs in this release, one square each
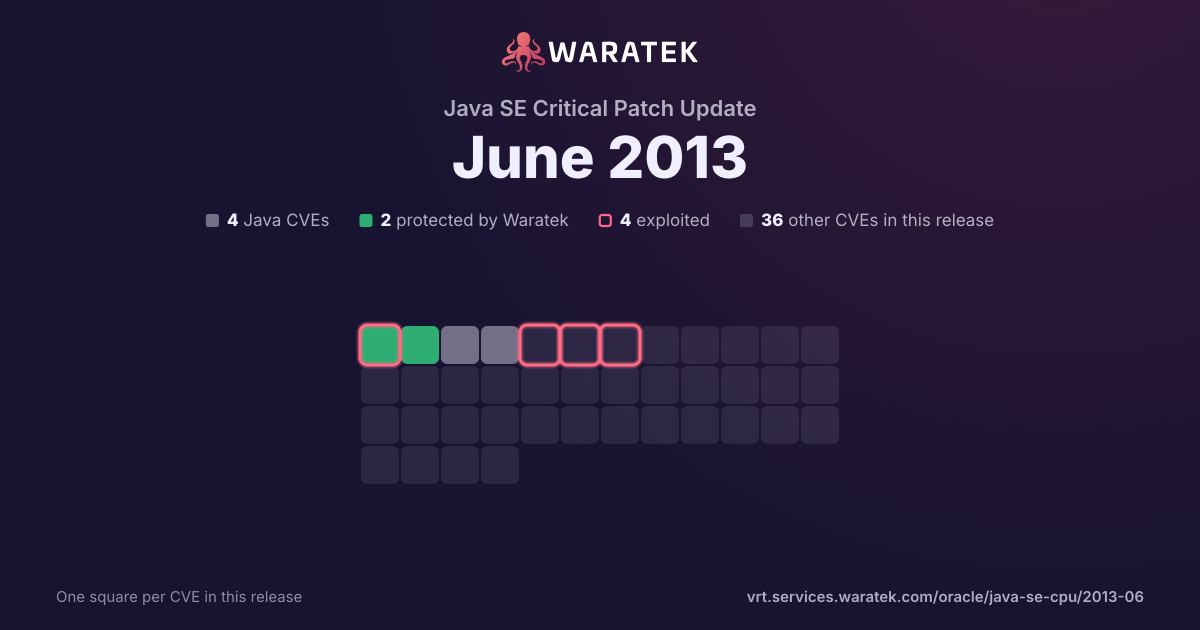
By status
No exploit published. For 1 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 4 matches · 2 protected · 1 exploited · 0 CISA KEV · 0 public PoC · 1 EPSS ≥ 0.5
Protected by Waratek
2
50.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
2
50.0%
blocked by ARMR today
2
50.0%
partly blocked
0
0.0%
not blocked
2
50.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
25.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
1
25.0%
No public exploit
2
50.0%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2013-2461 | High | 2013-06-18 | Protected by Waratek | Exploited | Unspecified vulnerability in the Java Runtime Environment (JRE) component in Oracle Java SE 7 Update 21 and earlier and 6 Update 45 and earlier; the Oracle JRockit component in Oracle Fusion Middleware R27.7.5 and earlier and R28.2.7 and earlier; and OpenJDK 7 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries. NOTE: the previous information is from the June and July 2013 CPU. Oracle has not commented on claims from another vendor that this issue allows remote attackers to bypass verification of XML signatures via vectors related to a "Missing check for [a] valid DOMCanonicalizationMethod canonicalization algorithm." |
| CVE-2013-2457 | Medium | 2013-06-18 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Java Runtime Environment (JRE) component in Oracle Java SE 7 Update 21 and earlier, 6 Update 45 and earlier, and 5.0 Update 45 and earlier, and OpenJDK 7, allows remote attackers to affect integrity via vectors related to JMX. NOTE: the previous information is from the June 2013 CPU. Oracle has not commented on claims from another vendor that this issue is due to an incorrect implementation of "certain class checks" that allows remote attackers to bypass intended class restrictions. |
| CVE-2013-2451 | Low | 2013-06-18 | No exploit published | No public exploit | Unspecified vulnerability in the Java Runtime Environment (JRE) component in Oracle Java SE 7 Update 21 and earlier and 6 Update 45 and earlier, and OpenJDK 7, allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Networking. NOTE: the previous information is from the June 2013 CPU. Oracle has not commented on claims from another vendor that this issue is related to improper enforcement of exclusive port binds when running on Windows, which allows attackers to bind to ports that are already in use. |
| CVE-2013-1571 | Medium | 2013-06-18 | No exploit published | Forecast only | Unspecified vulnerability in the Javadoc component in Oracle Java SE 7 Update 21 and earlier, 6 Update 45 and earlier, and 5.0 Update 45 and earlier; JavaFX 2.2.21 and earlier; and OpenJDK 7 allows remote attackers to affect integrity via unknown vectors related to Javadoc. NOTE: the previous information is from the June 2013 CPU. Oracle has not commented on claims from another vendor that this issue is related to frame injection in HTML that is generated by Javadoc. |