
Oracle Critical Patch Update July 2013
Released July 2013 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, June 2013 · Critical Patch Update, October 2013 →
89 CVEs in this release, one square each
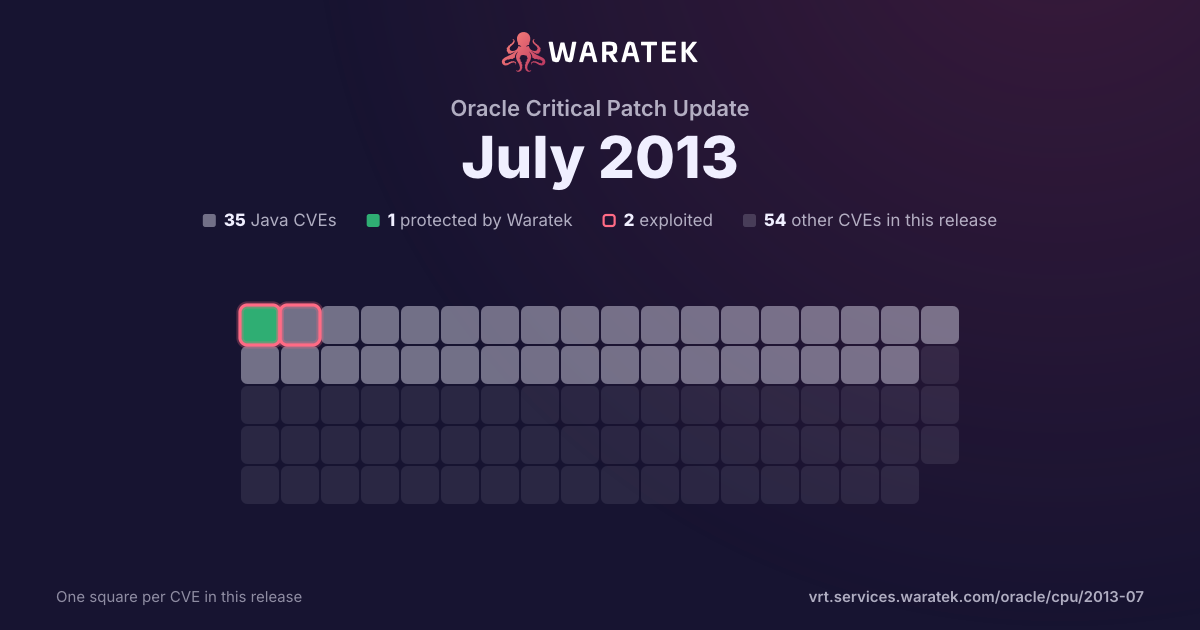
By status
1Protected by Waratek3Mitigation candidate31No exploit published8Outside Waratek scope46Not applicable
2Exploited, marked by the ring
No exploit published. For 31 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 35 matches · 1 protected · 2 exploited · 0 CISA KEV · 2 public PoC · 1 EPSS ≥ 0.5
Protected by Waratek
1
2.9%
Rule in development
0
0.0%
Mitigation candidate
3
8.6%
No exploit published
31
88.6%
blocked by ARMR today
1
2.9%
partly blocked
0
0.0%
not blocked
33
94.3%
not established
1
2.9%
unrecorded
0
0.0%
Exploited
2
5.7%
Working exploit published
2
5.7%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
31
88.6%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2013-3825 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile Product Collaboration component in Oracle Supply Chain Products Suite 9.3.1 allows remote authenticated users to affect confidentiality via unknown vectors related to Folders & Files Attachment. |
| CVE-2013-3824 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile Collaboration Framework component in Oracle Supply Chain Products Suite 9.3.1 allows remote authenticated users to affect integrity via unknown vectors related to Manufacturing/Mfg Parts. |
| CVE-2013-3823 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM Framework component in Oracle Supply Chain Products Suite 9.3.1 allows remote authenticated users to affect confidentiality via unknown vectors related to Security. |
| CVE-2013-3822 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM Framework component in Oracle Supply Chain Products Suite 9.3.1 allows remote attackers to affect integrity via unknown vectors related to Web Client (CS). |
| CVE-2013-3821 | Medium | 2013-07-17 | Mitigation candidate | Exploited | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.51, 8.52, and 8.53 allows remote attackers to affect confidentiality and availability via unknown vectors related to Integration Broker. |
| CVE-2013-3820 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.51, 8.52, and 8.53 allows remote attackers to affect availability via unknown vectors related to Business Interlink. |
| CVE-2013-3819 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.51, 8.52, and 8.53 allows remote attackers to affect confidentiality and availability via unknown vectors related to Mobile Applications. |
| CVE-2013-3818 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.51, 8.52, and 8.53 allows remote attackers to affect integrity via unknown vectors related to Portal, a different vulnerability than CVE-2013-2404. |
| CVE-2013-3816 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Policy Automation component in Oracle Industry Applications 10.2.0, 10.3.0, 10.3.1, 10.4.0, 10.4.1, and 10.4.2 allows remote authenticated users to affect confidentiality via unknown vectors related to Determinations Engine. |
| CVE-2013-3803 | Low | 2013-07-17 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Hyperion BI+ component in Oracle Hyperion 11.1.1.3, 11.1.1.4.107 and earlier, 11.1.2.1.129 and earlier, and 11.1.2.2.305 and earlier allows remote authenticated users to affect confidentiality via unknown vectors related to Intelligence Service. |
| CVE-2013-3800 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.51, 8.52, and 8.53 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Business Interlinks. |
| CVE-2013-3791 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in Enterprise Manager (EM) Base Platform 10.2.0.5 and EM DB Control 11.1.0.7 in Oracle Enterprise Manager Grid Control allows remote attackers to affect integrity via unknown vectors related to User Interface Framework. |
| CVE-2013-3788 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle iSupplier Portal component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect integrity via unknown vectors related to Supplier Management. |
| CVE-2013-3784 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HRMS component in Oracle PeopleSoft Products 9.1 allows remote authenticated users to affect confidentiality and integrity via unknown vectors Time and Labor. |
| CVE-2013-3781 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.3.7, 8.4.0, and 8.4.1 allows context-dependent attackers to affect availability via unknown vectors related to Outside In Filters, a different vulnerability than CVE-2013-3776. |
| CVE-2013-3780 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise Portal component in Oracle PeopleSoft Products 9.1 allows remote authenticated users to affect confidentiality via unknown vectors related to Saved Search. |
| CVE-2013-3778 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Technology Stack component in Oracle E-Business Suite 12.0.6 and 12.1.3 allows remote attackers to affect integrity via unknown vectors related to Help. |
| CVE-2013-3777 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 11.5.10.2, 12.0.6, and 12.1.3 allows remote attackers to affect integrity via unknown vectors related to Signon. |
| CVE-2013-3776 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.3.7, 8.4.0, and 8.4.1 allows context-dependent attackers to affect availability via unknown vectors related to Outside In Filters, a different vulnerability than CVE-2013-3781. |
| CVE-2013-3775 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle iLearning component in Oracle iLearning 5.2.1 and 6.0 allows remote attackers to affect integrity via unknown vectors related to Learner Pages. |
| CVE-2013-3772 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Content component in Oracle Fusion Middleware 10.1.3.5.1, 11.1.1.6.0, and 11.1.1.7.0 allows remote attackers to affect integrity via unknown vectors related to Web Forms. |
| CVE-2013-3770 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Content component in Oracle Fusion Middleware 10.1.3.5.1, 11.1.1.6.0, and 11.1.1.7.0 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Content Server. NOTE: the previous information is from the October 2013 CPU. Oracle has not commented on claims from a third party that the issue is related to "iDoc script injection" in the (1) cs and (2) urm components, which allows attackers to read "sensitive" files, as demonstrated by obtaining the "AES encryption key and encrypted credentials" of the weblogic user. |
| CVE-2013-3769 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Content component in Oracle Fusion Middleware 10.1.3.5.1, 11.1.1.6.0, and 11.1.1.7.0 allows remote attackers to affect integrity via unknown vectors related to Site Studio. |
| CVE-2013-3768 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.51, 8.52, and 8.53 allows remote attackers to affect integrity via unknown vectors related to Rich Text Editor. |
| CVE-2013-3767 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite Access Gate 1.2.1 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2013-3764 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Server component in Oracle Fusion Middleware 7.4.0 and 7.5.1.1 allows remote authenticated users to affect confidentiality and integrity via unknown vectors, a different vulnerability than CVE-2013-3763. |
| CVE-2013-3763 | Medium | 2013-07-17 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle Endeca Server component in Oracle Fusion Middleware 7.4.0 and 7.5.1.1 allows remote authenticated users to affect confidentiality and integrity via unknown vectors, a different vulnerability than CVE-2013-3764. |
| CVE-2013-3761 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products Portal 9.1 and PeopleTools 8.52 allows remote attackers to affect integrity via vectors related to PIA Core Technology. |
| CVE-2013-3759 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.52 and 8.53 allows remote attackers to affect integrity via vectors related to PIA Search Functionality. |
| CVE-2013-3758 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager (EM) Base Platform 10.2.0.5 and 11.1.0.1; EM DB Control 10.2.0.4, 10.2.0.5, 11.1.0.7, 11.2.0.2, and 11.2.0.3; and EM Plugin for DB 12.1.0.2 and 12.1.0.3 in Oracle Enterprise Manager Grid Control allows remote attackers to affect integrity via unknown vectors related to Schema Management. |
| CVE-2013-3756 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Landed Cost Management component in Oracle E-Business Suite 12.1.1, 12.1.2, and 12.1.3 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Shipment Workbench. |
| CVE-2013-3755 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Access Manager component in Oracle Fusion Middleware 11.1.1.5.0 allows remote attackers to affect integrity via vectors related to SSO Engine. |
| CVE-2013-3749 | Low | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 11.5.10.2, 12.0.6, and 12.1.3 allows remote authenticated users to affect confidentiality via unknown vectors related to Logging. NOTE: the previous information is from the July 2013 CPU. Oracle has not commented on claims from a third party that the issue is due to storage of credentials in the (1) FND_LOG_MESSAGES database table or (2) log files by "native login pages." |
| CVE-2013-3747 | Medium | 2013-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Technology Stack component in Oracle E-Business Suite 11.5.10.2, 12.0.6, and 12.1.3 allows remote authenticated users to affect confidentiality via unknown vectors related to Client System Analyzer. |
| CVE-2013-2461 | High | 2013-06-18 | Protected by Waratek | Exploited | Unspecified vulnerability in the Java Runtime Environment (JRE) component in Oracle Java SE 7 Update 21 and earlier and 6 Update 45 and earlier; the Oracle JRockit component in Oracle Fusion Middleware R27.7.5 and earlier and R28.2.7 and earlier; and OpenJDK 7 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries. NOTE: the previous information is from the June and July 2013 CPU. Oracle has not commented on claims from another vendor that this issue allows remote attackers to bypass verification of XML signatures via vectors related to a "Missing check for [a] valid DOMCanonicalizationMethod canonicalization algorithm." |