
Oracle Critical Security Patch Update August 2026
Released August 2026 · Oracle's advisory ↗ · ← Critical Patch Update, July 2026 · Security Patch Update, September 2026 →
1,021 CVEs in this release, one square each
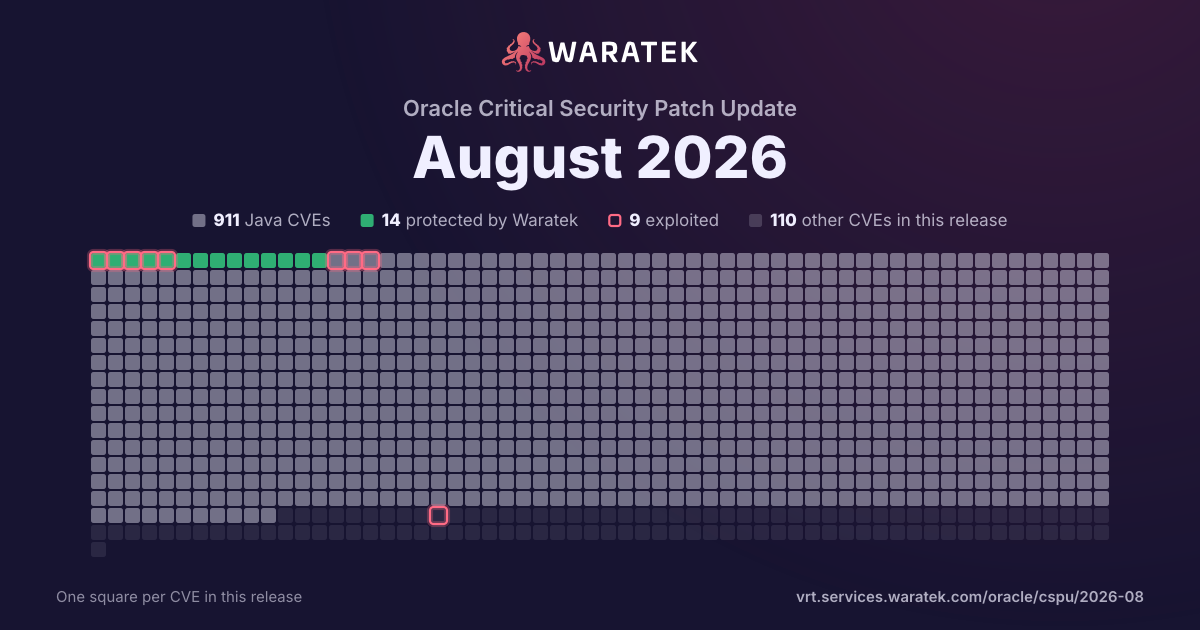
By status
14Protected by Waratek3Mitigation candidate894No exploit published9Outside Waratek scope101Not applicable
9Exploited, marked by the ring
No exploit published. For 848 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 5 matches · 3 exploited · 0 CISA KEV · 4 public PoC · 4 EPSS ≥ 0.5
Protected by Waratek
5
100.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
blocked by ARMR today
5
100.0%
partly blocked
0
0.0%
not blocked
0
0.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
3
60.0%
Working exploit published
0
0.0%
Proof of concept only
2
40.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 1 / month
Dec 211
Protected by Waratek1
High1
blocked by ARMR today1
Exploited1
Jan 221
Protected by Waratek1
Critical1
blocked by ARMR today1
Proof of concept only1
Feb 220
Mar 220
Apr 221
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
May 220
Jun 220
Jul 221
Protected by Waratek1
High1
blocked by ARMR today1
Proof of concept only1
Aug 220
Sep 220
Oct 220
Nov 220
Dec 220
Jan 230
Feb 230
Mar 231
Protected by Waratek1
High1
blocked by ARMR today1
Exploited1
Jan 22Mar 22May 22Jul 22Sep 22Nov 22Jan 23Mar 23
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2023-26464 | High | 2023-03-10 | Protected by Waratek | Exploited | ** UNSUPPORTED WHEN ASSIGNED ** When using the Chainsaw or SocketAppender components with Log4j 1.x on JRE less than 1.7, an attacker that manages to cause a logging entry involving a specially-crafted (ie, deeply nested) hashmap or hashtable (depending on which logging component is in use) to be processed could exhaust the available memory in the virtual machine and achieve Denial of Service when the object is deserialized. This issue affects Apache Log4j before 2. Affected users are recommended to update to Log4j 2.x. NOTE: This vulnerability only affects products that are no longer supported by the maintainer. |
| CVE-2022-34169 | High | 2022-07-19 | Protected by Waratek | Proof of concept only | The Apache Xalan Java XSLT library is vulnerable to an integer truncation issue when processing malicious XSLT stylesheets. This can be used to corrupt Java class files generated by the internal XSLTC compiler and execute arbitrary Java bytecode. Users are recommended to update to version 2.7.3 or later. Note: Java runtimes (such as OpenJDK) include repackaged copies of Xalan. |
| CVE-2021-31805 | Critical | 2022-04-12 | Protected by Waratek | Exploited | The fix issued for CVE-2020-17530 was incomplete. So from Apache Struts 2.0.0 to 2.5.29, still some of the tag’s attributes could perform a double evaluation if a developer applied forced OGNL evaluation by using the %{...} syntax. Using forced OGNL evaluation on untrusted user input can lead to a Remote Code Execution and security degradation. |
| CVE-2022-23305 | Critical | 2022-01-18 | Protected by Waratek | Proof of concept only | By design, the JDBCAppender in Log4j 1.2.x accepts an SQL statement as a configuration parameter where the values to be inserted are converters from PatternLayout. The message converter, %m, is likely to always be included. This allows attackers to manipulate the SQL by entering crafted strings into input fields or headers of an application that are logged allowing unintended SQL queries to be executed. Note this issue only affects Log4j 1.x when specifically configured to use the JDBCAppender, which is not the default. Beginning in version 2.0-beta8, the JDBCAppender was re-introduced with proper support for parameterized SQL queries and further customization over the columns written to in logs. Apache Log4j 1.2 reached end of life in August 2015. Users should upgrade to Log4j 2 as it addresses numerous other issues from the previous versions. |
| CVE-2021-4104 | High | 2021-12-14 | Protected by Waratek | Exploited | JMSAppender in Log4j 1.2 is vulnerable to deserialization of untrusted data when the attacker has write access to the Log4j configuration. The attacker can provide TopicBindingName and TopicConnectionFactoryBindingName configurations causing JMSAppender to perform JNDI requests that result in remote code execution in a similar fashion to CVE-2021-44228. Note this issue only affects Log4j 1.2 when specifically configured to use JMSAppender, which is not the default. Apache Log4j 1.2 reached end of life in August 2015. Users should upgrade to Log4j 2 as it addresses numerous other issues from the previous versions. |