
Oracle Critical Patch Update July 2026
Released July 2026 · Oracle's advisory ↗ · ← Security Patch Update, June 2026 · Security Patch Update, August 2026 →
1,433 CVEs in this release, one square each
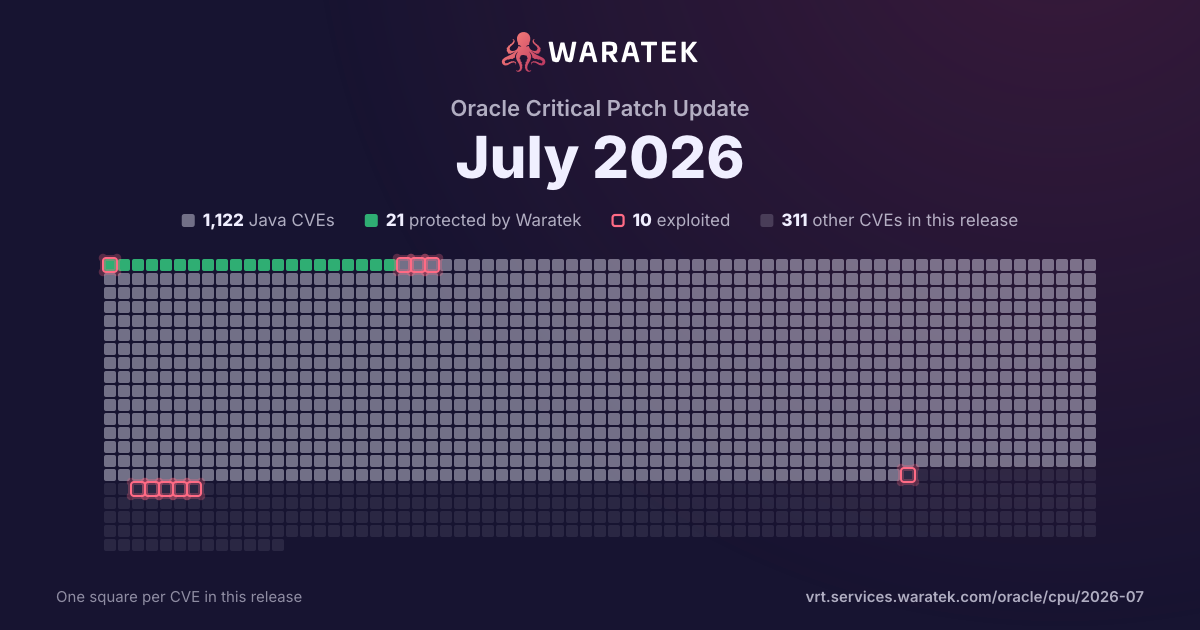
By status
21Protected by Waratek8Mitigation candidate1,093No exploit published16Outside Waratek scope295Not applicable
10Exploited, marked by the ring
No exploit published. For 971 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 50 matches · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
50matches
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
50
100.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
50
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
1
2.0%
Forecast only
0
0.0%
No public exploit
49
98.0%
split by
peak 43 / month
Jan 261
No exploit published1
Low1
not blocked1
No public exploit1
Feb 261
No exploit published1
Low1
not blocked1
No public exploit1
Mar 261
No exploit published1
Low1
not blocked1
No public exploit1
Apr 263
No exploit published3
Low3
not blocked3
No public exploit3
May 261
No exploit published1
Low1
not blocked1
Proof of concept only1
Jun 260
Jul 2643
No exploit published43
Low43
not blocked43
No public exploit43
Jan 26Feb 26Mar 26Apr 26May 26Jun 26Jul 26
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2026-62508 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Time and Labor product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Time and Labor. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Time and Labor. CVSS 3.1 Base Score 3.1 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2026-61303 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle EDI Gateway product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows high privileged attacker with logon to the infrastructure where Oracle EDI Gateway executes to compromise Oracle EDI Gateway. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle EDI Gateway accessible data. CVSS 3.1 Base Score 1.9 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:H/PR:H/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-61214 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle HRMS (UK) product of Oracle E-Business Suite (component: UK Payroll). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle HRMS (UK). Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle HRMS (UK) accessible data. CVSS 3.1 Base Score 2.2 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:H/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-61187 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Agile Engineering Data Management product of Oracle Supply Chain (component: Install). The supported version that is affected is 6.2.1. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Agile Engineering Data Management executes to compromise Oracle Agile Engineering Data Management. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Agile Engineering Data Management. CVSS 3.1 Base Score 2.8 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:R/S:U/C:N/I:N/A:L). |
| CVE-2026-61104 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise CS Student Records product of Oracle PeopleSoft (component: Research Tracking). The supported version that is affected is 9.2.38. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise CS Student Records. Successful attacks of this vulnerability can result in unauthorized read access to a subset of PeopleSoft Enterprise CS Student Records accessible data. CVSS 3.1 Base Score 3.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-61071 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FIN Engineering Argentina product of Oracle PeopleSoft (component: Engineering). The supported version that is affected is 9.1. Difficult to exploit vulnerability allows high privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise FIN Engineering Argentina. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise FIN Engineering Argentina accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise FIN Engineering Argentina accessible data. CVSS 3.1 Base Score 3.3 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:H/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2026-61048 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Inventory Optimization product of Oracle E-Business Suite (component: User Interface). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Inventory Optimization. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Inventory Optimization. CVSS 3.1 Base Score 3.1 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2026-61047 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Production Scheduling product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows high privileged attacker with logon to the infrastructure where Oracle Production Scheduling executes to compromise Oracle Production Scheduling. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Production Scheduling accessible data. CVSS 3.1 Base Score 1.9 (Integrity impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:H/PR:H/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2026-61036 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle HRMS (Norway) product of Oracle E-Business Suite (component: Norway Payroll). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle HRMS (Norway). Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle HRMS (Norway) accessible data as well as unauthorized read access to a subset of Oracle HRMS (Norway) accessible data. CVSS 3.1 Base Score 3.8 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2026-61028 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Inventory Management product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows high privileged attacker with logon to the infrastructure where Oracle Inventory Management executes to compromise Oracle Inventory Management. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Inventory Management. CVSS 3.1 Base Score 1.9 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:H/PR:H/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2026-61015 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Time and Labor product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Time and Labor. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Time and Labor accessible data. CVSS 3.1 Base Score 3.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-60950 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle HRMS (Ireland) product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle HRMS (Ireland). Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle HRMS (Ireland) accessible data. CVSS 3.1 Base Score 2.2 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:H/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-60939 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Project Contracts product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Project Contracts. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Project Contracts accessible data. CVSS 3.1 Base Score 3.1 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-60937 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Labor Distribution product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Labor Distribution. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Labor Distribution accessible data. CVSS 3.1 Base Score 3.1 (Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2026-60936 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Labor Distribution product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Labor Distribution. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Labor Distribution. CVSS 3.1 Base Score 3.1 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2026-60930 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Public Sector Financials product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Public Sector Financials. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Public Sector Financials accessible data. CVSS 3.1 Base Score 3.1 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-60929 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Public Sector Financials product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Public Sector Financials. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Public Sector Financials accessible data. CVSS 3.1 Base Score 3.1 (Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2026-60922 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle iSupplier Portal product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle iSupplier Portal. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle iSupplier Portal accessible data. CVSS 3.1 Base Score 3.1 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-60919 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle iSupplier Portal product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle iSupplier Portal. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle iSupplier Portal accessible data. CVSS 3.1 Base Score 3.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-60913 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Property Manager product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows high privileged attacker with logon to the infrastructure where Oracle Property Manager executes to compromise Oracle Property Manager. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Property Manager accessible data. CVSS 3.1 Base Score 1.9 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:H/PR:H/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-60896 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Work in Process product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Work in Process executes to compromise Oracle Work in Process. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Work in Process accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Work in Process. CVSS 3.1 Base Score 3.6 (Confidentiality and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:H/PR:L/UI:N/S:U/C:L/I:N/A:L). |
| CVE-2026-60891 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Work in Process product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows high privileged attacker with logon to the infrastructure where Oracle Work in Process executes to compromise Oracle Work in Process. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Work in Process accessible data. CVSS 3.1 Base Score 1.9 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:H/PR:H/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-60847 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Order Entry product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows high privileged attacker with logon to the infrastructure where Oracle Order Entry executes to compromise Oracle Order Entry. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Order Entry accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Order Entry. CVSS 3.1 Base Score 3.4 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:H/UI:N/S:U/C:N/I:L/A:L). |
| CVE-2026-60804 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle E-Business Intelligence product of Oracle E-Business Suite (component: Definition). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle E-Business Intelligence. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle E-Business Intelligence accessible data. CVSS 3.1 Base Score 2.0 (Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:H/UI:R/S:U/C:N/I:L/A:N). |
| CVE-2026-60628 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the JD Edwards EnterpriseOne Tools product of Oracle JD Edwards (component: Installation Security). The supported version that is affected is 9.2.26.3. Difficult to exploit vulnerability allows unauthenticated attacker with access to the physical communication segment attached to the hardware where the JD Edwards EnterpriseOne Tools executes to compromise JD Edwards EnterpriseOne Tools. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of JD Edwards EnterpriseOne Tools accessible data as well as unauthorized read access to a subset of JD Edwards EnterpriseOne Tools accessible data. CVSS 3.1 Base Score 3.7 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:A/AC:H/PR:N/UI:R/S:U/C:L/I:L/A:N). |
| CVE-2026-60596 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FIN eSettlements product of Oracle PeopleSoft (component: eSettlements). The supported version that is affected is 9.2. Easily exploitable vulnerability allows high privileged attacker with logon to the infrastructure where PeopleSoft Enterprise FIN eSettlements executes to compromise PeopleSoft Enterprise FIN eSettlements. Successful attacks of this vulnerability can result in unauthorized read access to a subset of PeopleSoft Enterprise FIN eSettlements accessible data. CVSS 3.1 Base Score 2.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:H/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-60357 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Siebel CRM Integration product of Oracle Siebel CRM (component: Siebel Server Sync for Exchange). Supported versions that are affected are 17.0-26.5. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Siebel CRM Integration. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Siebel CRM Integration accessible data. CVSS 3.1 Base Score 3.7 (Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2026-60354 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle JDeveloper product of Oracle Fusion Middleware (component: Data Visualization Tools). Supported versions that are affected are 12.2.1.4.0 and 14.1.2.0.0. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle JDeveloper. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle JDeveloper accessible data. CVSS 3.1 Base Score 3.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-60353 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle JDeveloper product of Oracle Fusion Middleware (component: ADF Faces). Supported versions that are affected are 12.2.1.4.0 and 14.1.2.0.0. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle JDeveloper. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle JDeveloper accessible data. CVSS 3.1 Base Score 3.1 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-60352 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle JDeveloper product of Oracle Fusion Middleware (component: ADF Faces). Supported versions that are affected are 12.2.1.4.0 and 14.1.2.0.0. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle JDeveloper. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle JDeveloper accessible data. CVSS 3.1 Base Score 3.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-60347 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the JD Edwards EnterpriseOne Tools product of Oracle JD Edwards (component: Enterprise Infrastructure Security). The supported version that is affected is 9.2.26.3. Difficult to exploit vulnerability allows low privileged attacker with logon to the infrastructure where JD Edwards EnterpriseOne Tools executes to compromise JD Edwards EnterpriseOne Tools. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of JD Edwards EnterpriseOne Tools accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of JD Edwards EnterpriseOne Tools. CVSS 3.1 Base Score 3.6 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:H/PR:L/UI:N/S:U/C:N/I:L/A:L). |
| CVE-2026-60346 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the JD Edwards EnterpriseOne Tools product of Oracle JD Edwards (component: Interoperability Security). The supported version that is affected is 9.2.26.3. Difficult to exploit vulnerability allows unauthenticated attacker with network access via JDENET to compromise JD Edwards EnterpriseOne Tools. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of JD Edwards EnterpriseOne Tools. CVSS 3.1 Base Score 3.7 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2026-60339 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Project Manufacturing product of Oracle E-Business Suite (component: PJM Command Center). The supported version that is affected is V16. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Project Manufacturing. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Project Manufacturing accessible data. CVSS 3.1 Base Score 3.1 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-60338 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Project Manufacturing product of Oracle E-Business Suite (component: PJM Command Center). The supported version that is affected is V16. Difficult to exploit vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Project Manufacturing executes to compromise Oracle Project Manufacturing. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Project Manufacturing accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Project Manufacturing. CVSS 3.1 Base Score 3.6 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:H/PR:L/UI:N/S:U/C:N/I:L/A:L). |
| CVE-2026-60318 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Data Integrator product of Oracle Fusion Middleware (component: Patchset Assistant). Supported versions that are affected are 12.2.1.4.0 and 14.1.2.0.0. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Data Integrator executes to compromise Oracle Data Integrator. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Data Integrator accessible data. CVSS 3.1 Base Score 3.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-60144 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Workflow product of Oracle E-Business Suite (component: Workflow Notification Mailer). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Workflow executes to compromise Oracle Workflow. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Workflow accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Workflow. CVSS 3.1 Base Score 3.6 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:H/PR:L/UI:N/S:U/C:N/I:L/A:L). |
| CVE-2026-47032 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Siebel CRM End User product of Oracle Siebel CRM (component: Redwood UI). Supported versions that are affected are 24.4-26.3. Difficult to exploit vulnerability allows high privileged attacker with network access via HTTP to compromise Siebel CRM End User. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Siebel CRM End User, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Siebel CRM End User. CVSS 3.1 Base Score 2.6 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:H/UI:R/S:C/C:N/I:N/A:L). |
| CVE-2026-47022 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the GoldenGate Stream Analytics product of Oracle GoldenGate (component: Security). The supported version that is affected is 26.1.0.0.0. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where GoldenGate Stream Analytics executes to compromise GoldenGate Stream Analytics. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of GoldenGate Stream Analytics. CVSS 3.1 Base Score 3.3 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2026-47016 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Siebel CRM Integration product of Oracle Siebel CRM (component: Event Publish and Subscribe). Supported versions that are affected are 17.0-26.4. Difficult to exploit vulnerability allows physical access to compromise Siebel CRM Integration. While the vulnerability is in Siebel CRM Integration, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized read access to a subset of Siebel CRM Integration accessible data. CVSS 3.1 Base Score 1.9 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:P/AC:H/PR:H/UI:N/S:C/C:L/I:N/A:N). |
| CVE-2026-47011 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Siebel CRM Deployment product of Oracle Siebel CRM (component: Application Interface). Supported versions that are affected are 17.0-26.4. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Siebel CRM Deployment. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Siebel CRM Deployment accessible data. CVSS 3.1 Base Score 2.6 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:R/S:U/C:L/I:N/A:N). |
| CVE-2026-47010 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition product of Oracle Java SE (component: ImageIO). Supported versions that are affected are Oracle Java SE: 8u491, 8u491-perf, 11.0.31, 17.0.19, 21.0.11, 25.0.3, 26.0.1; Oracle GraalVM for JDK: 17.0.19 and 21.0.11; Oracle GraalVM Enterprise Edition: 21.3.18. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition accessible data. Note: This vulnerability can be exploited by using APIs in the specified Component, e.g., through a web service which supplies data to the APIs. This vulnerability also applies to Java deployments, typically in clients running sandboxed Java Web Start applications or sandboxed Java applets, that load and run untrusted code (e.g., code that comes from the internet) and rely on the Java sandbox for security. CVSS 3.1 Base Score 3.7 (Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2026-47000 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Enterprise Manager Base Platform product of Oracle Enterprise Manager (component: Security Framework). The supported version that is affected is 24.1. Easily exploitable vulnerability allows low privileged attacker with network access via HTTPS to compromise Oracle Enterprise Manager Base Platform. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Enterprise Manager Base Platform accessible data. CVSS 3.1 Base Score 3.5 (Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:N/I:L/A:N). |
| CVE-2026-21953 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Retail Xstore Point of Service product of Oracle Retail Applications (component: Xstore Mobile). The supported version that is affected is 21.0.3. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Retail Xstore Point of Service executes to compromise Oracle Retail Xstore Point of Service. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Retail Xstore Point of Service accessible data. CVSS 3.1 Base Score 3.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-42578 | Low | 2026-05-13 | No exploit published | Proof of concept only | Netty is an asynchronous, event-driven network application framework. Prior to 4.2.13.Final and 4.1.133.Final, Netty's HttpProxyHandler constructs HTTP CONNECT requests with header validation explicitly disabled. The newInitialMessage() method creates headers using DefaultHttpHeadersFactory.headersFactory().withValidation(false), then adds user-provided outboundHeaders without any CRLF validation. This allows an attacker who can influence the outbound headers to inject arbitrary HTTP headers into the CONNECT request sent to the proxy server. This vulnerability is fixed in 4.2.13.Final and 4.1.133.Final. |
| CVE-2026-34268 | Low | 2026-04-21 | No exploit published | No public exploit | Vulnerability in the Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition product of Oracle Java SE (component: Security). Supported versions that are affected are Oracle Java SE: 8u481, 8u481-b50, 8u481-perf, 11.0.30, 17.0.18, 21.0.10, 25.0.2, 26; Oracle GraalVM for JDK: 17.0.18 and 21.0.10; Oracle GraalVM Enterprise Edition: 21.3.17. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition executes to compromise Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition accessible data. Note: This vulnerability can be exploited by using APIs in the specified Component, e.g., through a web service which supplies data to the APIs. This vulnerability also applies to Java deployments, typically in clients running sandboxed Java Web Start applications or sandboxed Java applets, that load and run untrusted code (e.g., code that comes from the internet) and rely on the Java sandbox for security. CVSS 3.1 Base Score 2.9 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:H/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-22018 | Low | 2026-04-21 | No exploit published | No public exploit | Vulnerability in the Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition product of Oracle Java SE (component: Libraries). Supported versions that are affected are Oracle Java SE: 8u481, 8u481-b50, 8u481-perf, 11.0.30, 17.0.18, 21.0.10, 25.0.2, 26; Oracle GraalVM for JDK: 17.0.18 and 21.0.10; Oracle GraalVM Enterprise Edition: 21.3.17. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition. Note: This vulnerability can be exploited by using APIs in the specified Component, e.g., through a web service which supplies data to the APIs. This vulnerability also applies to Java deployments, typically in clients running sandboxed Java Web Start applications or sandboxed Java applets, that load and run untrusted code (e.g., code that comes from the internet) and rely on the Java sandbox for security. CVSS 3.1 Base Score 3.7 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2026-22007 | Low | 2026-04-21 | No exploit published | No public exploit | Vulnerability in the Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition product of Oracle Java SE (component: Security). Supported versions that are affected are Oracle Java SE: 8u481, 8u481-b50, 8u481-perf, 11.0.30, 17.0.18, 21.0.10, 25.0.2, 26; Oracle GraalVM for JDK: 17.0.18 and 21.0.10; Oracle GraalVM Enterprise Edition: 21.3.17. Difficult to exploit vulnerability allows unauthenticated attacker with logon to the infrastructure where Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition executes to compromise Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition accessible data. Note: This vulnerability can be exploited by using APIs in the specified Component, e.g., through a web service which supplies data to the APIs. This vulnerability also applies to Java deployments, typically in clients running sandboxed Java Web Start applications or sandboxed Java applets, that load and run untrusted code (e.g., code that comes from the internet) and rely on the Java sandbox for security. CVSS 3.1 Base Score 2.9 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:H/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-22735 | Low | 2026-03-20 | No exploit published | No public exploit | Spring MVC and WebFlux applications are vulnerable to stream corruption when using Server-Sent Events (SSE). This issue affects Spring Foundation: from 7.0.0 through 7.0.5, from 6.2.0 through 6.2.16, from 6.1.0 through 6.1.25, from 5.3.0 through 5.3.46. |
| CVE-2026-23901 | Low | 2026-02-10 | No exploit published | No public exploit | Observable Timing Discrepancy vulnerability in Apache Shiro. This issue affects Apache Shiro: from 1.*, 2.* before 2.0.7. Users are recommended to upgrade to version 2.0.7 or later, which fixes the issue. Prior to Shiro 2.0.7, code paths for non-existent vs. existing users are different enough, that a brute-force attack may be able to tell, by timing the requests only, determine if the request failed because of a non-existent user vs. wrong password. The most likely attack vector is a local attack only. Shiro security model https://shiro.apache.org/security-model.html#username_enumeration discusses this as well. Typically, brute force attack can be mitigated at the infrastructure level. |
| CVE-2026-1225 | Low | 2026-01-22 | No exploit published | No public exploit | ACE vulnerability in configuration file processing by QOS.CH logback-core up to and including version 1.5.24 in Java applications, allows an attacker to instantiate classes already present on the class path by compromising an existing logback configuration file. The instantiation of a potentially malicious Java class requires that said class is present on the user's class-path. In addition, the attacker must have write access to a configuration file. However, after successful instantiation, the instance is very likely to be discarded with no further ado. |