
Oracle Critical Patch Update July 2026
Released July 2026 · Oracle's advisory ↗ · ← Security Patch Update, June 2026 · Security Patch Update, August 2026 →
1,433 CVEs in this release, one square each
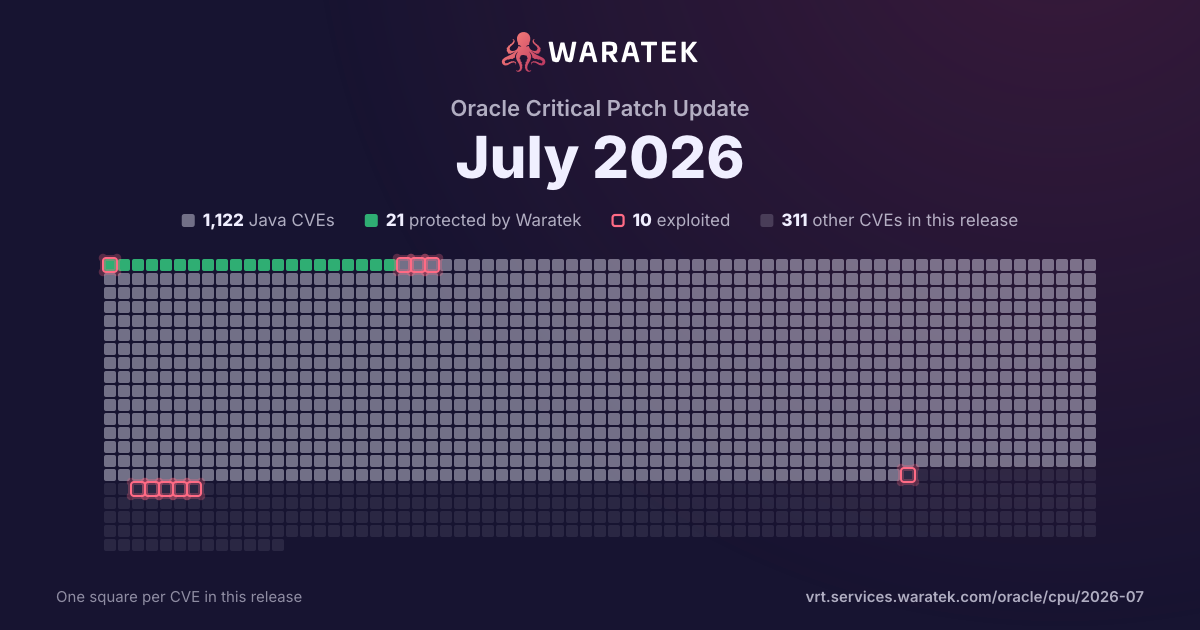
By status
21Protected by Waratek8Mitigation candidate1,093No exploit published16Outside Waratek scope295Not applicable
10Exploited, marked by the ring
No exploit published. For 971 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 1,093 matches · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
1,093matches
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
1,093
100.0%
Outside Waratek scope
0
0.0%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
1,093
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
24
2.2%
Forecast only
0
0.0%
No public exploit
1,069
97.8%
split by
peak 1,061 / year
20202
No exploit published2
Critical2
not blocked2
No public exploit2
20210
20221
No exploit published1
High1
not blocked1
No public exploit1
20235
No exploit published5
High4
Medium1
not blocked5
Proof of concept only4
No public exploit1
20245
No exploit published5
High2
Medium3
not blocked5
Proof of concept only1
No public exploit4
202519
No exploit published19
Critical1
High10
Medium8
not blocked19
Proof of concept only5
No public exploit14
20261,061
No exploit published1,061
Critical212
High532
Medium267
Low50
not blocked1,061
Proof of concept only14
No public exploit1,047
2020202120222023202420252026
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2026-61162 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager product of Oracle Commerce (component: Endeca Application Controller). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Commerce Guided Search / Oracle Commerce Experience Manager executes to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Commerce Guided Search / Oracle Commerce Experience Manager accessible data as well as unauthorized access to critical data or complete access to all Oracle Commerce Guided Search / Oracle Commerce Experience Manager accessible data. CVSS 3.1 Base Score 7.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2026-61161 | Critical | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager product of Oracle Commerce (component: Endeca Application Controller). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. Successful attacks of this vulnerability can result in takeover of Oracle Commerce Guided Search / Oracle Commerce Experience Manager. CVSS 3.1 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61160 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager product of Oracle Commerce (component: Experience Manager). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Commerce Guided Search / Oracle Commerce Experience Manager accessible data and unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Commerce Guided Search / Oracle Commerce Experience Manager. CVSS 3.1 Base Score 8.1 (Confidentiality and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:H). |
| CVE-2026-61159 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager product of Oracle Commerce (component: Experience Manager). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Commerce Guided Search / Oracle Commerce Experience Manager accessible data. CVSS 3.1 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-61158 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager product of Oracle Commerce (component: Experience Manager). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via RMI to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Commerce Guided Search / Oracle Commerce Experience Manager accessible data. CVSS 3.1 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-61157 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager product of Oracle Commerce (component: Experience Manager). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Commerce Guided Search / Oracle Commerce Experience Manager accessible data. CVSS 3.1 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-61156 | Critical | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search Platform Services product of Oracle Commerce (component: Forge). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTPS to compromise Oracle Commerce Guided Search Platform Services. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Commerce Guided Search Platform Services accessible data as well as unauthorized access to critical data or complete access to all Oracle Commerce Guided Search Platform Services accessible data. CVSS 3.1 Base Score 9.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2026-61155 | Critical | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search Platform Services product of Oracle Commerce (component: Forge). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Commerce Guided Search Platform Services. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Commerce Guided Search Platform Services accessible data and unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Commerce Guided Search Platform Services. CVSS 3.1 Base Score 9.1 (Confidentiality and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:H). |
| CVE-2026-61154 | Critical | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search Platform Services product of Oracle Commerce (component: Forge). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Commerce Guided Search Platform Services. Successful attacks of this vulnerability can result in takeover of Oracle Commerce Guided Search Platform Services. CVSS 3.1 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61153 | Critical | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager product of Oracle Commerce (component: Experience Manager). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Commerce Guided Search / Oracle Commerce Experience Manager accessible data as well as unauthorized access to critical data or complete access to all Oracle Commerce Guided Search / Oracle Commerce Experience Manager accessible data. CVSS 3.1 Base Score 9.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2026-61152 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager product of Oracle Commerce (component: Experience Manager). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Commerce Guided Search / Oracle Commerce Experience Manager accessible data as well as unauthorized read access to a subset of Oracle Commerce Guided Search / Oracle Commerce Experience Manager accessible data. CVSS 3.1 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2026-61151 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager product of Oracle Commerce (component: Experience Manager). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Commerce Guided Search / Oracle Commerce Experience Manager accessible data as well as unauthorized update, insert or delete access to some of Oracle Commerce Guided Search / Oracle Commerce Experience Manager accessible data. CVSS 3.1 Base Score 7.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:L/A:N). |
| CVE-2026-61150 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager product of Oracle Commerce (component: Experience Manager). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Commerce Guided Search / Oracle Commerce Experience Manager accessible data as well as unauthorized access to critical data or complete access to all Oracle Commerce Guided Search / Oracle Commerce Experience Manager accessible data. CVSS 3.1 Base Score 8.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2026-61149 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager product of Oracle Commerce (component: Experience Manager). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. Successful attacks of this vulnerability can result in takeover of Oracle Commerce Guided Search / Oracle Commerce Experience Manager. CVSS 3.1 Base Score 8.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61148 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager product of Oracle Commerce (component: Experience Manager). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. Successful attacks of this vulnerability can result in takeover of Oracle Commerce Guided Search / Oracle Commerce Experience Manager. CVSS 3.1 Base Score 8.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61147 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager product of Oracle Commerce (component: Content Acquisition System). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows unauthenticated attacker with logon to the infrastructure where Oracle Commerce Guided Search / Oracle Commerce Experience Manager executes to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Commerce Guided Search / Oracle Commerce Experience Manager. CVSS 3.1 Base Score 6.2 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2026-61146 | Critical | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager product of Oracle Commerce (component: Content Acquisition System). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. While the vulnerability is in Oracle Commerce Guided Search / Oracle Commerce Experience Manager, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in takeover of Oracle Commerce Guided Search / Oracle Commerce Experience Manager. CVSS 3.1 Base Score 9.9 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2026-61145 | Critical | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager product of Oracle Commerce (component: Content Acquisition System). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Commerce Guided Search / Oracle Commerce Experience Manager. Successful attacks of this vulnerability can result in takeover of Oracle Commerce Guided Search / Oracle Commerce Experience Manager. CVSS 3.1 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61143 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Convergent Charging Controller product of Oracle Communications (component: Prov IF). Supported versions that are affected are 15.0.0.0.0 and 15.2.0.0.0. Difficult to exploit vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Communications Convergent Charging Controller. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Oracle Communications Convergent Charging Controller. CVSS 3.1 Base Score 6.4 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:H/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2026-61142 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Payroll product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Payroll. While the vulnerability is in Oracle Payroll, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Payroll accessible data. CVSS 3.1 Base Score 7.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:N/A:N). |
| CVE-2026-61141 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Advanced Benefits product of Oracle E-Business Suite (component: Affordable Care Act). Supported versions that are affected are 12.2.7-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Advanced Benefits. Successful attacks of this vulnerability can result in takeover of Oracle Advanced Benefits. CVSS 3.1 Base Score 7.5 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61140 | Critical | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Sites product of Oracle Fusion Middleware (component: WebCenter Sites). The supported version that is affected is 14.1.2.0.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebCenter Sites. Successful attacks of this vulnerability can result in takeover of Oracle WebCenter Sites. CVSS 3.1 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61138 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Complex Maintenance, Repair and Overhaul product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Complex Maintenance, Repair and Overhaul. While the vulnerability is in Oracle Complex Maintenance, Repair and Overhaul, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Complex Maintenance, Repair and Overhaul accessible data as well as unauthorized update, insert or delete access to some of Oracle Complex Maintenance, Repair and Overhaul accessible data. CVSS 3.1 Base Score 7.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:C/C:H/I:L/A:N). |
| CVE-2026-61137 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Platform product of Oracle Commerce (component: Dynamo Application Framework). The supported version that is affected is 11.4.0. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Commerce Platform. Successful attacks of this vulnerability can result in takeover of Oracle Commerce Platform. CVSS 3.1 Base Score 8.1 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61136 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Platform product of Oracle Commerce (component: Dynamo Application Framework). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Commerce Platform. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Commerce Platform accessible data as well as unauthorized read access to a subset of Oracle Commerce Platform accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Commerce Platform. CVSS 3.1 Base Score 7.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:L). |
| CVE-2026-61135 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Platform product of Oracle Commerce (component: Dynamo Application Framework). The supported version that is affected is 11.4.0. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Commerce Platform. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Commerce Platform accessible data as well as unauthorized access to critical data or complete access to all Oracle Commerce Platform accessible data. CVSS 3.1 Base Score 7.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2026-61134 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Platform product of Oracle Commerce (component: Dynamo Application Framework). The supported version that is affected is 11.4.0. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Commerce Platform. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Commerce Platform accessible data as well as unauthorized access to critical data or complete access to all Oracle Commerce Platform accessible data. CVSS 3.1 Base Score 6.8 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2026-61133 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Platform product of Oracle Commerce (component: Dynamo Application Framework). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via LDAP to compromise Oracle Commerce Platform. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Commerce Platform accessible data. CVSS 3.1 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-61132 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Platform product of Oracle Commerce (component: Dynamo Application Framework). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Commerce Platform. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Commerce Platform, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Commerce Platform accessible data as well as unauthorized update, insert or delete access to some of Oracle Commerce Platform accessible data. CVSS 3.1 Base Score 7.6 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2026-61131 | Critical | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Platform product of Oracle Commerce (component: Dynamo Application Framework). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Commerce Platform. Successful attacks of this vulnerability can result in takeover of Oracle Commerce Platform. CVSS 3.1 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61130 | Critical | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Platform product of Oracle Commerce (component: Dynamo Application Framework). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Commerce Platform. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Commerce Platform accessible data and unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Commerce Platform. CVSS 3.1 Base Score 9.1 (Confidentiality and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:H). |
| CVE-2026-61129 | Critical | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Commerce Platform product of Oracle Commerce (component: ATG Portals). The supported version that is affected is 11.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Commerce Platform. Successful attacks of this vulnerability can result in takeover of Oracle Commerce Platform. CVSS 3.1 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61127 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Service Catalog and Design product of Oracle Communications (component: Solution Designer). Supported versions that are affected are 8.0.0.7.0-8.3.0.2.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Communications Service Catalog and Design. Successful attacks of this vulnerability can result in takeover of Oracle Communications Service Catalog and Design. CVSS 3.1 Base Score 8.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61126 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Billing and Revenue Management product of Oracle Communications (component: Platform). Supported versions that are affected are 15.0.0.0.0-15.0.1.0.0 and 15.1.0.0.0-15.2.0.0.0. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Communications Billing and Revenue Management executes to compromise Oracle Communications Billing and Revenue Management. Successful attacks of this vulnerability can result in takeover of Oracle Communications Billing and Revenue Management. CVSS 3.1 Base Score 7.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61125 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Configure to Order product of Oracle E-Business Suite (component: Supply to Order Workbench). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Configure to Order. While the vulnerability is in Oracle Configure to Order, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Configure to Order accessible data. CVSS 3.1 Base Score 7.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:N/A:N). |
| CVE-2026-61123 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle HRMS (US) product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle HRMS (US). Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle HRMS (US) accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle HRMS (US). CVSS 3.1 Base Score 4.2 (Confidentiality and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:L/I:N/A:L). |
| CVE-2026-61122 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle HRMS (UK) product of Oracle E-Business Suite (component: UK Payroll). Supported versions that are affected are 12.2.9-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle HRMS (UK). Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle HRMS (UK) accessible data as well as unauthorized access to critical data or complete access to all Oracle HRMS (UK) accessible data. CVSS 3.1 Base Score 8.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2026-61121 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle HRMS (UK) product of Oracle E-Business Suite (component: UK Payroll). Supported versions that are affected are 12.2.8-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle HRMS (UK). Successful attacks of this vulnerability can result in takeover of Oracle HRMS (UK). CVSS 3.1 Base Score 8.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61120 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle HRMS (US) product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with logon to the infrastructure where Oracle HRMS (US) executes to compromise Oracle HRMS (US). Successful attacks of this vulnerability can result in takeover of Oracle HRMS (US). CVSS 3.1 Base Score 7.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:H/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61119 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle HRMS (UK) product of Oracle E-Business Suite (component: UK Payroll). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle HRMS (UK). Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle HRMS (UK) accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle HRMS (UK). CVSS 3.1 Base Score 7.1 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:H/A:L). |
| CVE-2026-61117 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle HRMS (UK) product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.8-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle HRMS (UK). While the vulnerability is in Oracle HRMS (UK), attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle HRMS (UK) accessible data. CVSS 3.1 Base Score 6.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:C/C:H/I:N/A:N). |
| CVE-2026-61116 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Application Object Library product of Oracle E-Business Suite (component: Core). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Application Object Library. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Application Object Library accessible data. CVSS 3.1 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-61115 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Order Management product of Oracle E-Business Suite (component: Product Diagnostic Tools). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Order Management. Successful attacks of this vulnerability can result in takeover of Oracle Order Management. CVSS 3.1 Base Score 7.2 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61114 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Application Object Library product of Oracle E-Business Suite (component: DB Privileges). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Application Object Library. Successful attacks of this vulnerability can result in takeover of Oracle Application Object Library. CVSS 3.1 Base Score 7.5 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61113 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Application Object Library product of Oracle E-Business Suite (component: Core). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Application Object Library. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Application Object Library accessible data as well as unauthorized access to critical data or complete access to all Oracle Application Object Library accessible data. CVSS 3.1 Base Score 7.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2026-61112 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Order Management product of Oracle E-Business Suite (component: Product Diagnostic Tools). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Order Management. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Order Management accessible data. CVSS 3.1 Base Score 6.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-61111 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Application Object Library product of Oracle E-Business Suite (component: Core). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Application Object Library executes to compromise Oracle Application Object Library. While the vulnerability is in Oracle Application Object Library, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Application Object Library accessible data. CVSS 3.1 Base Score 6.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:C/C:H/I:N/A:N). |
| CVE-2026-61110 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Applications DBA product of Oracle E-Business Suite (component: ADPatch). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Applications DBA. Successful attacks of this vulnerability can result in takeover of Oracle Applications DBA. CVSS 3.1 Base Score 8.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61107 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Applications DBA product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Applications DBA. Successful attacks of this vulnerability can result in takeover of Oracle Applications DBA. CVSS 3.1 Base Score 7.2 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61105 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Banking Trade Finance product of Oracle Financial Services Applications (component: Infrastructure). Supported versions that are affected are 14.6.0-14.8.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Banking Trade Finance. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Banking Trade Finance accessible data as well as unauthorized access to critical data or complete access to all Oracle Banking Trade Finance accessible data. CVSS 3.1 Base Score 8.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2026-61104 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise CS Student Records product of Oracle PeopleSoft (component: Research Tracking). The supported version that is affected is 9.2.38. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise CS Student Records. Successful attacks of this vulnerability can result in unauthorized read access to a subset of PeopleSoft Enterprise CS Student Records accessible data. CVSS 3.1 Base Score 3.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2026-61103 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise CS Campus Community product of Oracle PeopleSoft (component: Security). The supported version that is affected is 9.2.38. Difficult to exploit vulnerability allows unauthenticated attacker with access to the physical communication segment attached to the hardware where the PeopleSoft Enterprise CS Campus Community executes to compromise PeopleSoft Enterprise CS Campus Community. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all PeopleSoft Enterprise CS Campus Community accessible data as well as unauthorized update, insert or delete access to some of PeopleSoft Enterprise CS Campus Community accessible data. CVSS 3.1 Base Score 5.9 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:A/AC:H/PR:N/UI:N/S:U/C:H/I:L/A:N). |
| CVE-2026-61102 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Banking Trade Finance product of Oracle Financial Services Applications (component: Infrastructure). Supported versions that are affected are 14.6.0-14.8.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Banking Trade Finance. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Banking Trade Finance accessible data as well as unauthorized access to critical data or complete access to all Oracle Banking Trade Finance accessible data. CVSS 3.1 Base Score 8.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2026-61101 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle MES for Process Manufacturing product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle MES for Process Manufacturing. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle MES for Process Manufacturing, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle MES for Process Manufacturing accessible data as well as unauthorized update, insert or delete access to some of Oracle MES for Process Manufacturing accessible data. CVSS 3.1 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2026-61100 | Critical | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Enterprise Capture product of Oracle Fusion Middleware (component: Client Bundle). Supported versions that are affected are 12.2.1.4.0 and 14.1.2.0.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebCenter Enterprise Capture. Successful attacks of this vulnerability can result in takeover of Oracle WebCenter Enterprise Capture. CVSS 3.1 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61099 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Enterprise Capture product of Oracle Fusion Middleware (component: Client Bundle). Supported versions that are affected are 12.2.1.4.0 and 14.1.2.0.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle WebCenter Enterprise Capture. Successful attacks of this vulnerability can result in takeover of Oracle WebCenter Enterprise Capture. CVSS 3.1 Base Score 8.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61098 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Enterprise Capture product of Oracle Fusion Middleware (component: Client Bundle). Supported versions that are affected are 12.2.1.4.0 and 14.1.2.0.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle WebCenter Enterprise Capture. Successful attacks of this vulnerability can result in takeover of Oracle WebCenter Enterprise Capture. CVSS 3.1 Base Score 8.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61097 | Critical | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Banking Trade Finance Process Management product of Oracle Financial Services Applications (component: Common). Supported versions that are affected are 14.6.0-14.8.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Banking Trade Finance Process Management. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Banking Trade Finance Process Management, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Banking Trade Finance Process Management accessible data as well as unauthorized access to critical data or complete access to all Oracle Banking Trade Finance Process Management accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Banking Trade Finance Process Management. CVSS 3.1 Base Score 9.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:H/A:L). |
| CVE-2026-61095 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Unified Inventory Management product of Oracle Communications (component: Security). Supported versions that are affected are 7.5.0, 7.5.1, 7.6.0, 7.7.0, 7.8.0 and 8.0.1. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Communications Unified Inventory Management. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Communications Unified Inventory Management accessible data as well as unauthorized update, insert or delete access to some of Oracle Communications Unified Inventory Management accessible data. CVSS 3.1 Base Score 7.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:L/A:N). |
| CVE-2026-61092 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Enterprise Capture product of Oracle Fusion Middleware (component: Client Bundle). Supported versions that are affected are 12.2.1.4.0 and 14.1.2.0.0. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebCenter Enterprise Capture. Successful attacks of this vulnerability can result in takeover of Oracle WebCenter Enterprise Capture. CVSS 3.1 Base Score 8.1 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61091 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Billing and Revenue Management product of Oracle Communications (component: BRM Server). Supported versions that are affected are 15.0.0.0.0, 15.0.1.0.0, 15.1.0.0.0 and 15.2.0.0.0. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Communications Billing and Revenue Management executes to compromise Oracle Communications Billing and Revenue Management. Successful attacks of this vulnerability can result in takeover of Oracle Communications Billing and Revenue Management. CVSS 3.1 Base Score 7.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61090 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Project Foundation product of Oracle E-Business Suite (component: Miscellaneous). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Project Foundation executes to compromise Oracle Project Foundation. Successful attacks of this vulnerability can result in takeover of Oracle Project Foundation. CVSS 3.1 Base Score 7.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61089 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise SCM Inventory product of Oracle PeopleSoft (component: Security). The supported version that is affected is 9.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise SCM Inventory. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all PeopleSoft Enterprise SCM Inventory accessible data as well as unauthorized update, insert or delete access to some of PeopleSoft Enterprise SCM Inventory accessible data. CVSS 3.1 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:L/A:N). |
| CVE-2026-61088 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise SCM Manufacturing product of Oracle PeopleSoft (component: Security). The supported version that is affected is 9.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise SCM Manufacturing. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all PeopleSoft Enterprise SCM Manufacturing accessible data. CVSS 3.1 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-61087 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FIN Payables product of Oracle PeopleSoft (component: Security). The supported version that is affected is 9.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise FIN Payables. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all PeopleSoft Enterprise FIN Payables accessible data. CVSS 3.1 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-61086 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise SCM Order Management product of Oracle PeopleSoft (component: Security). The supported version that is affected is 9.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTPS to compromise PeopleSoft Enterprise SCM Order Management. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all PeopleSoft Enterprise SCM Order Management accessible data. CVSS 3.1 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-61085 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise SCM Inventory product of Oracle PeopleSoft (component: Security). The supported version that is affected is 9.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTPS to compromise PeopleSoft Enterprise SCM Inventory. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all PeopleSoft Enterprise SCM Inventory accessible data. CVSS 3.1 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-61083 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Performance Management product of Oracle E-Business Suite (component: Appraisals). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Performance Management. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Performance Management accessible data as well as unauthorized read access to a subset of Oracle Performance Management accessible data. CVSS 3.1 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2026-61080 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Public Sector Human Resources product of Oracle E-Business Suite (component: Regression Testing). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Public Sector Human Resources. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Public Sector Human Resources accessible data as well as unauthorized read access to a subset of Oracle Public Sector Human Resources accessible data. CVSS 3.1 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2026-61078 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise CC Common Application Objects product of Oracle PeopleSoft (component: Common Application Objects). The supported version that is affected is 9.2. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise CC Common Application Objects. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise CC Common Application Objects, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all PeopleSoft Enterprise CC Common Application Objects accessible data as well as unauthorized access to critical data or complete access to all PeopleSoft Enterprise CC Common Application Objects accessible data. CVSS 3.1 Base Score 8.7 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:H/I:H/A:N). |
| CVE-2026-61077 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise SCM Mobile Inventory Management product of Oracle PeopleSoft (component: Security). The supported version that is affected is 9.2. Difficult to exploit vulnerability allows low privileged attacker with logon to the infrastructure where PeopleSoft Enterprise SCM Mobile Inventory Management executes to compromise PeopleSoft Enterprise SCM Mobile Inventory Management. While the vulnerability is in PeopleSoft Enterprise SCM Mobile Inventory Management, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all PeopleSoft Enterprise SCM Mobile Inventory Management accessible data as well as unauthorized access to critical data or complete access to all PeopleSoft Enterprise SCM Mobile Inventory Management accessible data. CVSS 3.1 Base Score 7.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:H/PR:L/UI:N/S:C/C:H/I:H/A:N). |
| CVE-2026-61076 | Critical | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise HCM Talent Acquisition Manager product of Oracle PeopleSoft (component: Job Opening). The supported version that is affected is 9.2. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise HCM Talent Acquisition Manager. While the vulnerability is in PeopleSoft Enterprise HCM Talent Acquisition Manager, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in takeover of PeopleSoft Enterprise HCM Talent Acquisition Manager. CVSS 3.1 Base Score 9.9 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2026-61075 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Self-Service Human Resources product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Self-Service Human Resources. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Self-Service Human Resources accessible data as well as unauthorized read access to a subset of Oracle Self-Service Human Resources accessible data. CVSS 3.1 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2026-61074 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FIN Common Objects Brazil product of Oracle PeopleSoft (component: eProcurement). The supported version that is affected is 9.1. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise FIN Common Objects Brazil. Successful attacks of this vulnerability can result in takeover of PeopleSoft Enterprise FIN Common Objects Brazil. CVSS 3.1 Base Score 8.1 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61073 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FIN Common Objects Brazil product of Oracle PeopleSoft (component: Purchasing). The supported version that is affected is 9.1. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise FIN Common Objects Brazil. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all PeopleSoft Enterprise FIN Common Objects Brazil accessible data. CVSS 3.1 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-61072 | Critical | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FIN Staffing Front Office Brazil product of Oracle PeopleSoft (component: Staffing). The supported version that is affected is 9.1. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise FIN Staffing Front Office Brazil. While the vulnerability is in PeopleSoft Enterprise FIN Staffing Front Office Brazil, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in takeover of PeopleSoft Enterprise FIN Staffing Front Office Brazil. CVSS 3.1 Base Score 9.9 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2026-61071 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FIN Engineering Argentina product of Oracle PeopleSoft (component: Engineering). The supported version that is affected is 9.1. Difficult to exploit vulnerability allows high privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise FIN Engineering Argentina. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise FIN Engineering Argentina accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise FIN Engineering Argentina accessible data. CVSS 3.1 Base Score 3.3 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:H/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2026-61070 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FIN Common Objects Argentina product of Oracle PeopleSoft (component: Cash Management). The supported version that is affected is 9.1. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise FIN Common Objects Argentina. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of PeopleSoft Enterprise FIN Common Objects Argentina. CVSS 3.1 Base Score 5.3 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2026-61069 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FIN General Ledger Argentina product of Oracle PeopleSoft (component: General Ledger). The supported version that is affected is 9.1. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise FIN General Ledger Argentina. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all PeopleSoft Enterprise FIN General Ledger Argentina accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of PeopleSoft Enterprise FIN General Ledger Argentina. CVSS 3.1 Base Score 5.9 (Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:N/I:H/A:L). |
| CVE-2026-61068 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FIN Billing Argentina product of Oracle PeopleSoft (component: Billing). The supported version that is affected is 9.1. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise FIN Billing Argentina. Successful attacks of this vulnerability can result in takeover of PeopleSoft Enterprise FIN Billing Argentina. CVSS 3.1 Base Score 7.2 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61067 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Access Manager product of Oracle Fusion Middleware (component: Authentication Engine). Supported versions that are affected are 12.2.1.4.0 and 14.1.2.1.0. Easily exploitable vulnerability allows low privileged attacker with access to the physical communication segment attached to the hardware where the Oracle Access Manager executes to compromise Oracle Access Manager. Successful attacks of this vulnerability can result in takeover of Oracle Access Manager. CVSS 3.1 Base Score 8.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:A/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61065 | Critical | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Access Manager product of Oracle Fusion Middleware (component: Authentication Engine). Supported versions that are affected are 12.2.1.4.0 and 14.1.2.1.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Access Manager. Successful attacks of this vulnerability can result in takeover of Oracle Access Manager. CVSS 3.1 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61064 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle iRecruitment product of Oracle E-Business Suite (component: Install / Upgrade Issues). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle iRecruitment. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle iRecruitment accessible data as well as unauthorized read access to a subset of Oracle iRecruitment accessible data. CVSS 3.1 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2026-61063 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise SCM Supplier Contract Management product of Oracle PeopleSoft (component: Security). The supported version that is affected is 9.2. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where PeopleSoft Enterprise SCM Supplier Contract Management executes to compromise PeopleSoft Enterprise SCM Supplier Contract Management. While the vulnerability is in PeopleSoft Enterprise SCM Supplier Contract Management, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in takeover of PeopleSoft Enterprise SCM Supplier Contract Management. CVSS 3.1 Base Score 8.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2026-61062 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FIN Cash Management product of Oracle PeopleSoft (component: Cash Management). The supported version that is affected is 9.2. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where PeopleSoft Enterprise FIN Cash Management executes to compromise PeopleSoft Enterprise FIN Cash Management. While the vulnerability is in PeopleSoft Enterprise FIN Cash Management, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in takeover of PeopleSoft Enterprise FIN Cash Management. CVSS 3.1 Base Score 8.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2026-61061 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle JDeveloper product of Oracle Fusion Middleware (component: Security Framework). Supported versions that are affected are 12.2.1.4.0 and 14.1.2.0.0. Difficult to exploit vulnerability allows low privileged attacker with logon to the infrastructure where Oracle JDeveloper executes to compromise Oracle JDeveloper. Successful attacks of this vulnerability can result in takeover of Oracle JDeveloper. CVSS 3.1 Base Score 7.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:H/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61060 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle E-Business Suite Secure Enterprise Search product of Oracle E-Business Suite (component: Search Integration Engine). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle E-Business Suite Secure Enterprise Search. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle E-Business Suite Secure Enterprise Search accessible data as well as unauthorized read access to a subset of Oracle E-Business Suite Secure Enterprise Search accessible data. CVSS 3.1 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2026-61059 | Critical | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise SCM Order Management product of Oracle PeopleSoft (component: Security). The supported version that is affected is 9.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise SCM Order Management. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all PeopleSoft Enterprise SCM Order Management accessible data as well as unauthorized access to critical data or complete access to all PeopleSoft Enterprise SCM Order Management accessible data. CVSS 3.1 Base Score 9.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2026-61057 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FIN eSettlements product of Oracle PeopleSoft (component: eSettlements). The supported version that is affected is 9.2. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise FIN eSettlements. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise FIN eSettlements accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise FIN eSettlements accessible data. CVSS 3.1 Base Score 4.8 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2026-61056 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FIN Grants product of Oracle PeopleSoft (component: Grants). The supported version that is affected is 9.2. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise FIN Grants. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise FIN Grants accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise FIN Grants accessible data. CVSS 3.1 Base Score 4.8 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2026-61055 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise SCM Order Management product of Oracle PeopleSoft (component: Security). The supported version that is affected is 9.2. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where PeopleSoft Enterprise SCM Order Management executes to compromise PeopleSoft Enterprise SCM Order Management. Successful attacks of this vulnerability can result in takeover of PeopleSoft Enterprise SCM Order Management. CVSS 3.1 Base Score 7.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61053 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Communications BRM - Elastic Charging Engine product of Oracle Communications (component: Diameter Gateway and SDK). Supported versions that are affected are 15.0.0.0.0, 15.0.1.0.0, 15.1.0.0.0 and 15.2.0.0.0. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Communications BRM - Elastic Charging Engine executes to compromise Oracle Communications BRM - Elastic Charging Engine. Successful attacks of this vulnerability can result in takeover of Oracle Communications BRM - Elastic Charging Engine. CVSS 3.1 Base Score 7.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2026-61051 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Concurrent Processing product of Oracle E-Business Suite (component: BI Publisher Integration). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Concurrent Processing. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Concurrent Processing accessible data as well as unauthorized read access to a subset of Oracle Concurrent Processing accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Concurrent Processing. CVSS 3.1 Base Score 6.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:L). |
| CVE-2026-61050 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Production Scheduling product of Oracle E-Business Suite (component: User Interface). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Production Scheduling. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Production Scheduling accessible data. CVSS 3.1 Base Score 5.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2026-61049 | High | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Production Scheduling product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows unauthenticated attacker with access to the physical communication segment attached to the hardware where the Oracle Production Scheduling executes to compromise Oracle Production Scheduling. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in takeover of Oracle Production Scheduling. CVSS 3.1 Base Score 7.1 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:A/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H). |
| CVE-2026-61048 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Inventory Optimization product of Oracle E-Business Suite (component: User Interface). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Inventory Optimization. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Inventory Optimization. CVSS 3.1 Base Score 3.1 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2026-61047 | Low | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Production Scheduling product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows high privileged attacker with logon to the infrastructure where Oracle Production Scheduling executes to compromise Oracle Production Scheduling. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Production Scheduling accessible data. CVSS 3.1 Base Score 1.9 (Integrity impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:H/PR:H/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2026-61046 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Production Scheduling product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Difficult to exploit vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Production Scheduling. While the vulnerability is in Oracle Production Scheduling, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Production Scheduling accessible data as well as unauthorized read access to a subset of Oracle Production Scheduling accessible data. CVSS 3.1 Base Score 6.6 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:H/UI:N/S:C/C:L/I:H/A:N). |
| CVE-2026-61044 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Production Scheduling product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Production Scheduling. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Production Scheduling accessible data as well as unauthorized read access to a subset of Oracle Production Scheduling accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Production Scheduling. CVSS 3.1 Base Score 4.7 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:L/I:L/A:L). |
| CVE-2026-61043 | Medium | 2026-07-21 | No exploit published | No public exploit | Vulnerability in the Oracle Production Scheduling product of Oracle E-Business Suite (component: Internal Operations). Supported versions that are affected are 12.2.3-12.2.15. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Production Scheduling executes to compromise Oracle Production Scheduling. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Production Scheduling, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Production Scheduling accessible data as well as unauthorized read access to a subset of Oracle Production Scheduling accessible data. CVSS 3.1 Base Score 6.7 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.1/AV:L/AC:L/PR:L/UI:R/S:C/C:L/I:H/A:N). |