
Oracle Critical Patch Update October 2025
Released October 2025 · Oracle's advisory ↗ · ← Critical Patch Update, July 2025 · Critical Patch Update, January 2026 →
234 CVEs in this release, one square each
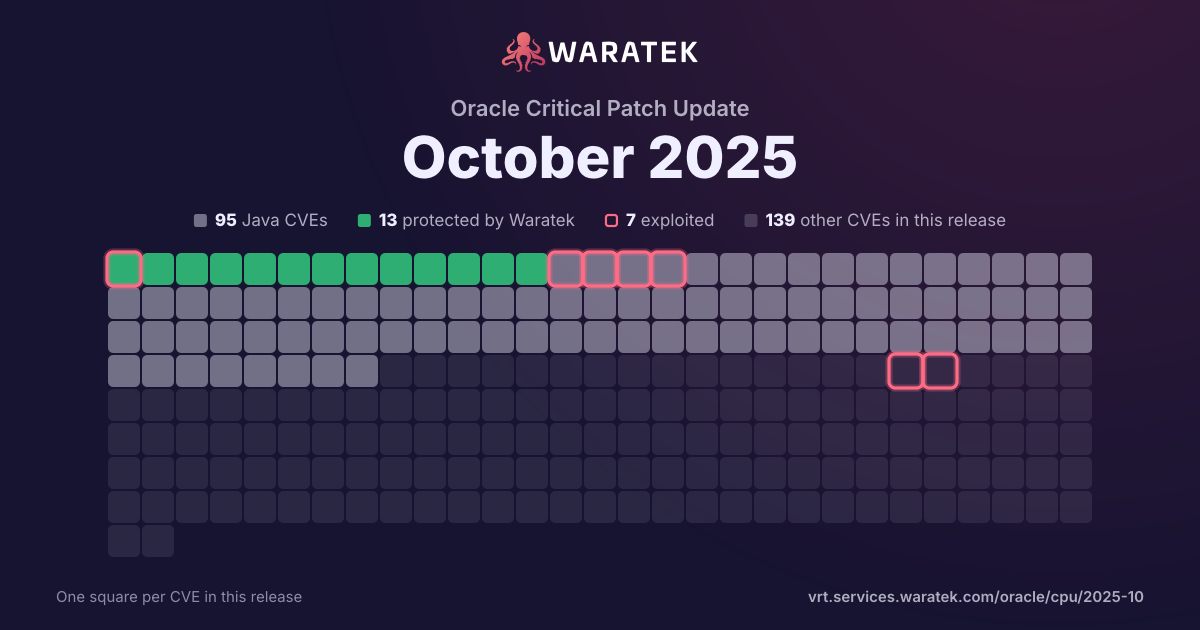
By status
13Protected by Waratek5Mitigation candidate77No exploit published15Outside Waratek scope124Not applicable
7Exploited, marked by the ring
No exploit published. For 36 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 12 matches · 1 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
12matches
1in Waratek scope8.3%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
1
8.3%
Outside Waratek scope
2
16.7%
Not applicable
9
75.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
12
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
2
16.7%
Forecast only
0
0.0%
No public exploit
10
83.3%
split by
peak 6 / month
Feb 251
Not applicable1
Low1
not blocked1
No public exploit1
Mar 250
Apr 250
May 251
No exploit published1
Low1
not blocked1
No public exploit1
Jun 251
Not applicable1
Low1
not blocked1
Proof of concept only1
Jul 253
Not applicable3
Low3
not blocked3
Proof of concept only1
No public exploit2
Aug 250
Sep 250
Oct 256
Outside Waratek scope2
Not applicable4
Low6
not blocked6
No public exploit6
Feb 25Mar 25Apr 25May 25Jun 25Jul 25Aug 25Sep 25Oct 25
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2025-62480 | Low | 2025-10-21 | Not applicable | No public exploit | Vulnerability in the Oracle ZFS Storage Appliance Kit product of Oracle Systems (component: Naming Subsystem). The supported version that is affected is 8.8. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle ZFS Storage Appliance Kit. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Oracle ZFS Storage Appliance Kit. CVSS 3.1 Base Score 2.7 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2025-62479 | Low | 2025-10-21 | Not applicable | No public exploit | Vulnerability in the Oracle ZFS Storage Appliance Kit product of Oracle Systems (component: Block Storage). The supported version that is affected is 8.8. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle ZFS Storage Appliance Kit. Successful attacks of this vulnerability can result in unauthorized ability to cause a partial denial of service (partial DOS) of Oracle ZFS Storage Appliance Kit. CVSS 3.1 Base Score 2.7 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:N/A:L). |
| CVE-2025-61755 | Low | 2025-10-21 | Outside Waratek scope | No public exploit | Vulnerability in the Oracle GraalVM for JDK product of Oracle Java SE (component: Compiler). Supported versions that are affected are Oracle GraalVM for JDK: 17.0.16 and 21.0.8. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Oracle GraalVM for JDK. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle GraalVM for JDK accessible data. CVSS 3.1 Base Score 3.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2025-61749 | Low | 2025-10-21 | Not applicable | No public exploit | Vulnerability in the Unified Audit component of Oracle Database Server. Supported versions that are affected are 23.4-23.9. Easily exploitable vulnerability allows high privileged attacker having DBA privilege with network access via Oracle Net to compromise Unified Audit. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Unified Audit accessible data. CVSS 3.1 Base Score 2.7 (Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2025-61748 | Low | 2025-10-21 | Outside Waratek scope | No public exploit | Vulnerability in the Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition product of Oracle Java SE (component: Libraries). Supported versions that are affected are Oracle Java SE: 21.0.8 and 25; Oracle GraalVM for JDK: 21.0.8; Oracle GraalVM Enterprise Edition: 21.3.15. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition accessible data. Note: This vulnerability can be exploited by using APIs in the specified Component, e.g., through a web service which supplies data to the APIs. This vulnerability also applies to Java deployments, typically in clients running sandboxed Java Web Start applications or sandboxed Java applets, that load and run untrusted code (e.g., code that comes from the internet) and rely on the Java sandbox for security. CVSS 3.1 Base Score 3.7 (Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2025-53051 | Low | 2025-10-21 | Not applicable | No public exploit | Vulnerability in the RDBMS Functional Index component of Oracle Database Server. Supported versions that are affected are 23.4-23.9. Easily exploitable vulnerability allows high privileged attacker having SYSDBA privilege with network access via Oracle Net to compromise RDBMS Functional Index. Successful attacks of this vulnerability can result in unauthorized read access to a subset of RDBMS Functional Index accessible data. CVSS 3.1 Base Score 2.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2025-4878 | Low | 2025-07-22 | Not applicable | No public exploit | A vulnerability was found in libssh, where an uninitialized variable exists under certain conditions in the privatekey_from_file() function. This flaw can be triggered if the file specified by the filename doesn't exist and may lead to possible signing failures or heap corruption. |
| CVE-2025-7339 | Low | 2025-07-17 | Not applicable | Proof of concept only | on-headers is a node.js middleware for listening to when a response writes headers. A bug in on-headers versions `<1.1.0` may result in response headers being inadvertently modified when an array is passed to `response.writeHead()`. Users should upgrade to version 1.1.0 to receive a patch. Uses are strongly encouraged to upgrade to `1.1.0`, but this issue can be worked around by passing an object to `response.writeHead()` rather than an array. |
| CVE-2025-53643 | Low | 2025-07-14 | Not applicable | No public exploit | AIOHTTP is an asynchronous HTTP client/server framework for asyncio and Python. Prior to version 3.12.14, the Python parser is vulnerable to a request smuggling vulnerability due to not parsing trailer sections of an HTTP request. If a pure Python version of aiohttp is installed (i.e. without the usual C extensions) or AIOHTTP_NO_EXTENSIONS is enabled, then an attacker may be able to execute a request smuggling attack to bypass certain firewalls or proxy protections. Version 3.12.14 contains a patch for this issue. |
| CVE-2025-5889 | Low | 2025-06-09 | Not applicable | Proof of concept only | A vulnerability was found in juliangruber brace-expansion up to 1.1.11/2.0.1/3.0.0/4.0.0. It has been rated as problematic. Affected by this issue is the function expand of the file index.js. The manipulation leads to inefficient regular expression complexity. The attack may be launched remotely. The complexity of an attack is rather high. The exploitation is known to be difficult. The exploit has been disclosed to the public and may be used. Upgrading to version 1.1.12, 2.0.2, 3.0.1 and 4.0.1 is able to address this issue. The name of the patch is a5b98a4f30d7813266b221435e1eaaf25a1b0ac5. It is recommended to upgrade the affected component. |
| CVE-2025-22233 | Low | 2025-05-16 | No exploit published | No public exploit | CVE-2024-38820 ensured Locale-independent, lowercase conversion for both the configured disallowedFields patterns and for request parameter names. However, there are still cases where it is possible to bypass the disallowedFields checks. Affected Spring Products and Versions Spring Framework: * 6.2.0 - 6.2.6 * 6.1.0 - 6.1.19 * 6.0.0 - 6.0.27 * 5.3.0 - 5.3.42 * Older, unsupported versions are also affected Mitigation Users of affected versions should upgrade to the corresponding fixed version. Affected version(s)Fix Version Availability 6.2.x 6.2.7 OSS6.1.x 6.1.20 OSS6.0.x 6.0.28 Commercial https://enterprise.spring.io/ 5.3.x 5.3.43 Commercial https://enterprise.spring.io/ No further mitigation steps are necessary. Generally, we recommend using a dedicated model object with properties only for data binding, or using constructor binding since constructor arguments explicitly declare what to bind together with turning off setter binding through the declarativeBinding flag. See the Model Design section in the reference documentation. For setting binding, prefer the use of allowedFields (an explicit list) over disallowedFields. Credit This issue was responsibly reported by the TERASOLUNA Framework Development Team from NTT DATA Group Corporation. |
| CVE-2025-1795 | Low | 2025-02-28 | Not applicable | No public exploit | During an address list folding when a separating comma ends up on a folded line and that line is to be unicode-encoded then the separator itself is also unicode-encoded. Expected behavior is that the separating comma remains a plan comma. This can result in the address header being misinterpreted by some mail servers. |