
Oracle Critical Patch Update October 2025
Released October 2025 · Oracle's advisory ↗ · ← Critical Patch Update, July 2025 · Critical Patch Update, January 2026 →
234 CVEs in this release, one square each
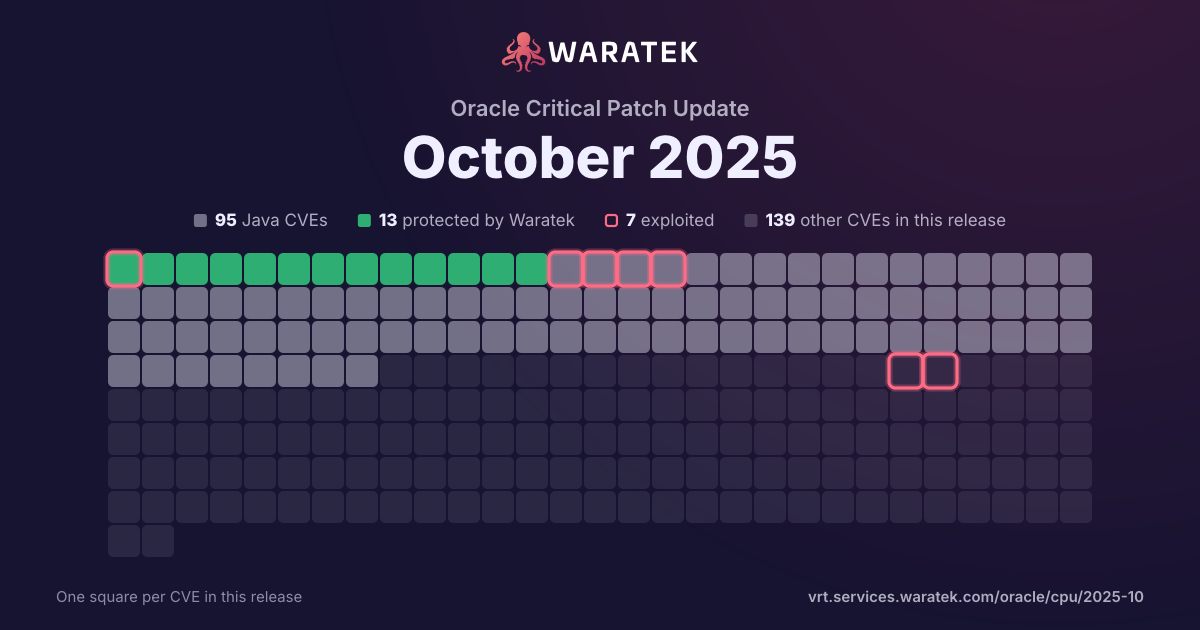
By status
13Protected by Waratek5Mitigation candidate77No exploit published15Outside Waratek scope124Not applicable
7Exploited, marked by the ring
No exploit published. For 36 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 219 matches · 80 in Waratek scope · 0 protected · 4 exploited · 2 CISA KEV · 10 public PoC · 5 EPSS ≥ 0.5
219matches
80in Waratek scope36.5%
0protected0.0%
4exploited1.8%
2CISA KEV0.9%
10public PoC4.6%
5EPSS ≥ 0.52.3%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
3
1.4%
No exploit published
77
35.2%
Outside Waratek scope
15
6.8%
Not applicable
124
56.6%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
219
100.0%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 72 / quarter
Q4 201
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Q1 211
No exploit published1
High1
not blocked1
No public exploit1
Q2 212
No exploit published1
Not applicable1
High1
Medium1
not blocked2
Proof of concept only1
Forecast only1
Q3 212
Outside Waratek scope2
Critical1
High1
not blocked2
Forecast only1
No public exploit1
Q4 210
Q1 221
No exploit published1
Medium1
not blocked1
No public exploit1
Q2 221
No exploit published1
Medium1
not blocked1
No public exploit1
Q3 220
Q4 220
Q1 230
Q2 236
No exploit published1
Not applicable5
High1
Medium5
not blocked6
Proof of concept only1
No public exploit5
Q3 230
Q4 233
No exploit published2
Not applicable1
Critical1
High1
Medium1
not blocked3
No public exploit3
Q1 242
Outside Waratek scope1
Not applicable1
Critical1
Medium1
not blocked2
Proof of concept only1
No public exploit1
Q2 245
Not applicable5
Critical1
High2
Medium2
not blocked5
Forecast only1
No public exploit4
Q3 246
No exploit published2
Not applicable4
High2
Medium4
not blocked6
Proof of concept only1
No public exploit5
Q4 248
No exploit published4
Outside Waratek scope2
Not applicable2
Critical2
High2
Medium4
not blocked8
No public exploit8
Q1 2514
No exploit published4
Not applicable10
High8
Medium5
Low1
not blocked14
Exploited1
Proof of concept only3
No public exploit10
Q2 2540
Mitigation candidate2
No exploit published11
Outside Waratek scope2
Not applicable25
Critical4
High20
Medium14
Low2
not blocked40
Exploited1
Working exploit published1
Proof of concept only11
No public exploit27
Q3 2555
Mitigation candidate1
No exploit published15
Outside Waratek scope2
Not applicable37
High27
Medium25
Low3
not blocked55
Exploited2
Working exploit published2
Proof of concept only7
No public exploit44
Q4 2572
No exploit published34
Outside Waratek scope5
Not applicable33
Critical1
High15
Medium50
Low6
not blocked72
No public exploit72
Q4 20Q2 21Q4 21Q2 22Q4 22Q2 23Q4 23Q2 24Q4 24Q2 25Q4 25
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2024-26462 | Medium | 2024-02-29 | Outside Waratek scope | Proof of concept only | Kerberos 5 (aka krb5) 1.21.2 contains a memory leak vulnerability in /krb5/src/kdc/ndr.c. |
| CVE-2024-23807 | Critical | 2024-02-29 | Not applicable | No public exploit | The Apache Xerces C++ XML parser on versions 3.0.0 before 3.2.5 contains a use-after-free error triggered during the scanning of external DTDs. Users are recommended to upgrade to version 3.2.5 which fixes the issue, or mitigate the issue by disabling DTD processing. This can be accomplished via the DOM using a standard parser feature, or via SAX using the XERCES_DISABLE_DTD environment variable. This issue has been disclosed before as CVE-2018-1311, but unfortunately that advisory incorrectly stated the issue would be fixed in version 3.2.3 or 3.2.4. |
| CVE-2023-34053 | High | 2023-11-28 | No exploit published | No public exploit | In Spring Framework versions 6.0.0 - 6.0.13, it is possible for a user to provide specially crafted HTTP requests that may cause a denial-of-service (DoS) condition. Specifically, an application is vulnerable when all of the following are true: * the application uses Spring MVC or Spring WebFlux * io.micrometer:micrometer-core is on the classpath * an ObservationRegistry is configured in the application to record observations Typically, Spring Boot applications need the org.springframework.boot:spring-boot-actuator dependency to meet all conditions. |
| CVE-2023-44483 | Medium | 2023-10-20 | No exploit published | No public exploit | All versions of Apache Santuario - XML Security for Java prior to 2.2.6, 2.3.4, and 3.0.3, when using the JSR 105 API, are vulnerable to an issue where a private key may be disclosed in log files when generating an XML Signature and logging with debug level is enabled. Users are recommended to upgrade to version 2.2.6, 2.3.4, or 3.0.3, which fixes this issue. |
| CVE-2023-45853 | Critical | 2023-10-14 | Not applicable | No public exploit | MiniZip in zlib through 1.3 has an integer overflow and resultant heap-based buffer overflow in zipOpenNewFileInZip4_64 via a long filename, comment, or extra field. NOTE: MiniZip is not a supported part of the zlib product. NOTE: pyminizip through 0.2.6 is also vulnerable because it bundles an affected zlib version, and exposes the applicable MiniZip code through its compress API. |
| CVE-2023-2976 | High | 2023-06-14 | No exploit published | No public exploit | Use of Java's default temporary directory for file creation in `FileBackedOutputStream` in Google Guava versions 1.0 to 31.1 on Unix systems and Android Ice Cream Sandwich allows other users and apps on the machine with access to the default Java temporary directory to be able to access the files created by the class. Even though the security vulnerability is fixed in version 32.0.0, we recommend using version 32.0.1 as version 32.0.0 breaks some functionality under Windows. |
| CVE-2023-26555 | Medium | 2023-04-11 | Not applicable | No public exploit | praecis_parse in ntpd/refclock_palisade.c in NTP 4.2.8p15 has an out-of-bounds write. Any attack method would be complex, e.g., with a manipulated GPS receiver. |
| CVE-2023-26554 | Medium | 2023-04-11 | Not applicable | Proof of concept only | mstolfp in libntp/mstolfp.c in NTP 4.2.8p15 has an out-of-bounds write when adding a '\0' character. An adversary may be able to attack a client ntpq process, but cannot attack ntpd. |
| CVE-2023-26553 | Medium | 2023-04-11 | Not applicable | No public exploit | mstolfp in libntp/mstolfp.c in NTP 4.2.8p15 has an out-of-bounds write when copying the trailing number. An adversary may be able to attack a client ntpq process, but cannot attack ntpd. |
| CVE-2023-26552 | Medium | 2023-04-11 | Not applicable | No public exploit | mstolfp in libntp/mstolfp.c in NTP 4.2.8p15 has an out-of-bounds write when adding a decimal point. An adversary may be able to attack a client ntpq process, but cannot attack ntpd. |
| CVE-2023-26551 | Medium | 2023-04-11 | Not applicable | No public exploit | mstolfp in libntp/mstolfp.c in NTP 4.2.8p15 has an out-of-bounds write in the cp<cpdec while loop. An adversary may be able to attack a client ntpq process, but cannot attack ntpd. |
| CVE-2022-22968 | Medium | 2022-04-14 | No exploit published | No public exploit | In Spring Framework versions 5.3.0 - 5.3.18, 5.2.0 - 5.2.20, and older unsupported versions, the patterns for disallowedFields on a DataBinder are case sensitive which means a field is not effectively protected unless it is listed with both upper and lower case for the first character of the field, including upper and lower case for the first character of all nested fields within the property path. |
| CVE-2022-24329 | Medium | 2022-02-25 | No exploit published | No public exploit | In JetBrains Kotlin before 1.6.0, it was not possible to lock dependencies for Multiplatform Gradle Projects. |
| CVE-2021-3712 | High | 2021-08-24 | Outside Waratek scope | No public exploit | ASN.1 strings are represented internally within OpenSSL as an ASN1_STRING structure which contains a buffer holding the string data and a field holding the buffer length. This contrasts with normal C strings which are repesented as a buffer for the string data which is terminated with a NUL (0) byte. Although not a strict requirement, ASN.1 strings that are parsed using OpenSSL's own "d2i" functions (and other similar parsing functions) as well as any string whose value has been set with the ASN1_STRING_set() function will additionally NUL terminate the byte array in the ASN1_STRING structure. However, it is possible for applications to directly construct valid ASN1_STRING structures which do not NUL terminate the byte array by directly setting the "data" and "length" fields in the ASN1_STRING array. This can also happen by using the ASN1_STRING_set0() function. Numerous OpenSSL functions that print ASN.1 data have been found to assume that the ASN1_STRING byte array will be NUL terminated, even though this is not guaranteed for strings that have been directly constructed. Where an application requests an ASN.1 structure to be printed, and where that ASN.1 structure contains ASN1_STRINGs that have been directly constructed by the application without NUL terminating the "data" field, then a read buffer overrun can occur. The same thing can also occur during name constraints processing of certificates (for example if a certificate has been directly constructed by the application instead of loading it via the OpenSSL parsing functions, and the certificate contains non NUL terminated ASN1_STRING structures). It can also occur in the X509_get1_email(), X509_REQ_get1_email() and X509_get1_ocsp() functions. If a malicious actor can cause an application to directly construct an ASN1_STRING and then process it through one of the affected OpenSSL functions then this issue could be hit. This might result in a crash (causing a Denial of Service attack). It could also result in the disclosure of private memory contents (such as private keys, or sensitive plaintext). Fixed in OpenSSL 1.1.1l (Affected 1.1.1-1.1.1k). Fixed in OpenSSL 1.0.2za (Affected 1.0.2-1.0.2y). |
| CVE-2021-3711 | Critical | 2021-08-24 | Outside Waratek scope | Forecast only | In order to decrypt SM2 encrypted data an application is expected to call the API function EVP_PKEY_decrypt(). Typically an application will call this function twice. The first time, on entry, the "out" parameter can be NULL and, on exit, the "outlen" parameter is populated with the buffer size required to hold the decrypted plaintext. The application can then allocate a sufficiently sized buffer and call EVP_PKEY_decrypt() again, but this time passing a non-NULL value for the "out" parameter. A bug in the implementation of the SM2 decryption code means that the calculation of the buffer size required to hold the plaintext returned by the first call to EVP_PKEY_decrypt() can be smaller than the actual size required by the second call. This can lead to a buffer overflow when EVP_PKEY_decrypt() is called by the application a second time with a buffer that is too small. A malicious attacker who is able present SM2 content for decryption to an application could cause attacker chosen data to overflow the buffer by up to a maximum of 62 bytes altering the contents of other data held after the buffer, possibly changing application behaviour or causing the application to crash. The location of the buffer is application dependent but is typically heap allocated. Fixed in OpenSSL 1.1.1l (Affected 1.1.1-1.1.1k). |
| CVE-2021-22897 | Medium | 2021-06-11 | Not applicable | Proof of concept only | curl 7.61.0 through 7.76.1 suffers from exposure of data element to wrong session due to a mistake in the code for CURLOPT_SSL_CIPHER_LIST when libcurl is built to use the Schannel TLS library. The selected cipher set was stored in a single "static" variable in the library, which has the surprising side-effect that if an application sets up multiple concurrent transfers, the last one that sets the ciphers will accidentally control the set used by all transfers. In a worst-case scenario, this weakens transport security significantly. |
| CVE-2021-28165 | High | 2021-04-01 | No exploit published | Forecast only | In Eclipse Jetty 7.2.2 to 9.4.38, 10.0.0.alpha0 to 10.0.1, and 11.0.0.alpha0 to 11.0.1, CPU usage can reach 100% upon receiving a large invalid TLS frame. |
| CVE-2020-11988 | High | 2021-02-24 | No exploit published | No public exploit | Apache XmlGraphics Commons 2.4 and earlier is vulnerable to server-side request forgery, caused by improper input validation by the XMPParser. By using a specially-crafted argument, an attacker could exploit this vulnerability to cause the underlying server to make arbitrary GET requests. Users should upgrade to 2.6 or later. |
| CVE-2020-13956 | Medium | 2020-12-02 | Outside Waratek scope | No public exploit | Apache HttpClient versions prior to version 4.5.13 and 5.0.3 can misinterpret malformed authority component in request URIs passed to the library as java.net.URI object and pick the wrong target host for request execution. |