
Oracle Critical Patch Update July 2025
Released July 2025 · Oracle's advisory ↗ · ← Critical Patch Update, April 2025 · Critical Patch Update, October 2025 →
196 CVEs in this release, one square each
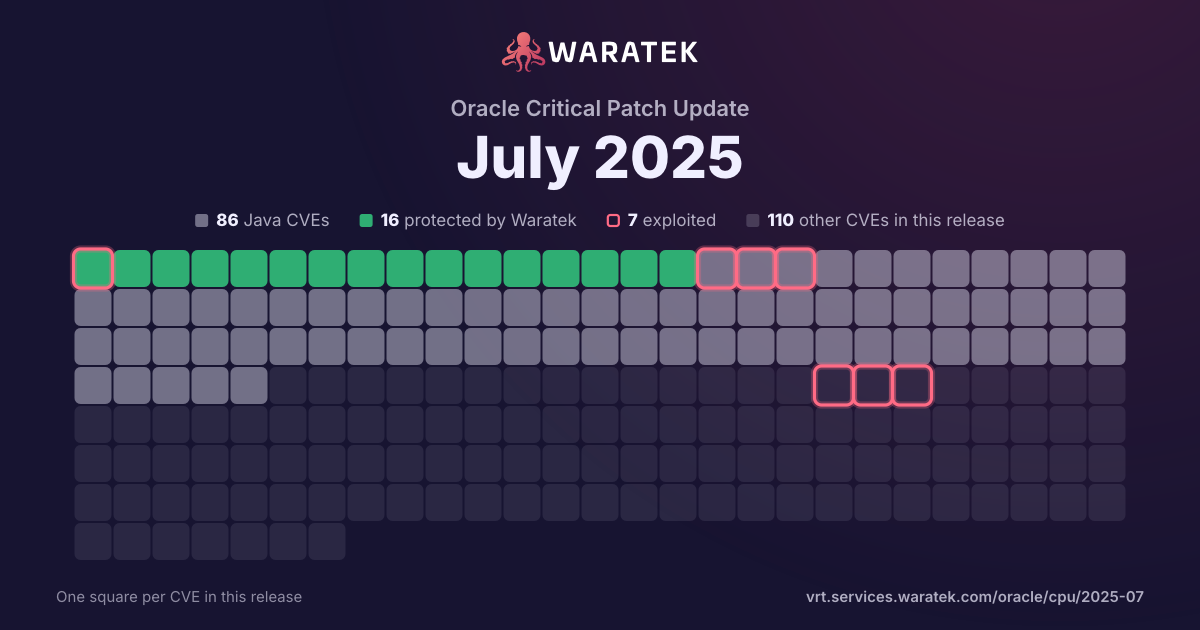
By status
16Protected by Waratek4Mitigation candidate66No exploit published14Outside Waratek scope96Not applicable
7Exploited, marked by the ring
No exploit published. For 31 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 4 matches · 3 in Waratek scope · 2 protected · 0 exploited · 0 CISA KEV · 3 EPSS ≥ 0.5
Protected by Waratek
2
50.0%
Rule in development
0
0.0%
Mitigation candidate
1
25.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
1
25.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
2
50.0%
partly blocked
0
0.0%
not blocked
2
50.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
4
100.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 1 / month
Jul 241
Not applicable1
High1
not blocked1
Working exploit published1
Aug 240
Sep 240
Oct 240
Nov 240
Dec 241
Protected by Waratek1
High1
blocked by ARMR today1
Working exploit published1
Jan 250
Feb 250
Mar 250
Apr 251
Protected by Waratek1
High1
blocked by ARMR today1
Working exploit published1
May 251
Mitigation candidate1
Medium1
not blocked1
Working exploit published1
Jul 24Aug 24Sep 24Oct 24Nov 24Dec 24Jan 25Feb 25Mar 25Apr 25May 25
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2025-27533 | Medium | 2025-05-07 | Mitigation candidate | Working exploit published | Memory Allocation with Excessive Size Value vulnerability in Apache ActiveMQ. During unmarshalling of OpenWire commands the size value of buffers was not properly validated which could lead to excessive memory allocation and be exploited to cause a denial of service (DoS) by depleting process memory, thereby affecting applications and services that rely on the availability of the ActiveMQ broker when not using mutual TLS connections. This issue affects Apache ActiveMQ: from 6.0.0 before 6.1.6, from 5.18.0 before 5.18.7, from 5.17.0 before 5.17.7, before 5.16.8. ActiveMQ 5.19.0 is not affected. Users are recommended to upgrade to version 6.1.6+, 5.19.0+, 5.18.7+, 5.17.7, or 5.16.8 or which fixes the issue. Existing users may implement mutual TLS to mitigate the risk on affected brokers. |
| CVE-2025-31650 | High | 2025-04-28 | Protected by Waratek | Working exploit published | Improper Input Validation vulnerability in Apache Tomcat. Incorrect error handling for some invalid HTTP priority headers resulted in incomplete clean-up of the failed request which created a memory leak. A large number of such requests could trigger an OutOfMemoryException resulting in a denial of service. This issue affects Apache Tomcat: from 9.0.76 through 9.0.102, from 10.1.10 through 10.1.39, from 11.0.0-M2 through 11.0.5. The following versions were EOL at the time the CVE was created but are known to be affected: 8.5.90 though 8.5.100. Users are recommended to upgrade to version 9.0.104, 10.1.40 or 11.0.6 which fix the issue. |
| CVE-2024-38819 | High | 2024-12-19 | Protected by Waratek | Working exploit published | Applications serving static resources through the functional web frameworks WebMvc.fn or WebFlux.fn are vulnerable to path traversal attacks. An attacker can craft malicious HTTP requests and obtain any file on the file system that is also accessible to the process in which the Spring application is running. |
| CVE-2024-38472 | High | 2024-07-01 | Not applicable | Working exploit published | SSRF in Apache HTTP Server on Windows allows to potentially leak NTLM hashes to a malicious server via SSRF and malicious requests or content Users are recommended to upgrade to version 2.4.60 which fixes this issue. Note: Existing configurations that access UNC paths will have to configure new directive "UNCList" to allow access during request processing. |