
Oracle Critical Patch Update April 2025
Released April 2025 · Oracle's advisory ↗ · ← Critical Patch Update, January 2025 · Critical Patch Update, July 2025 →
255 CVEs in this release, one square each
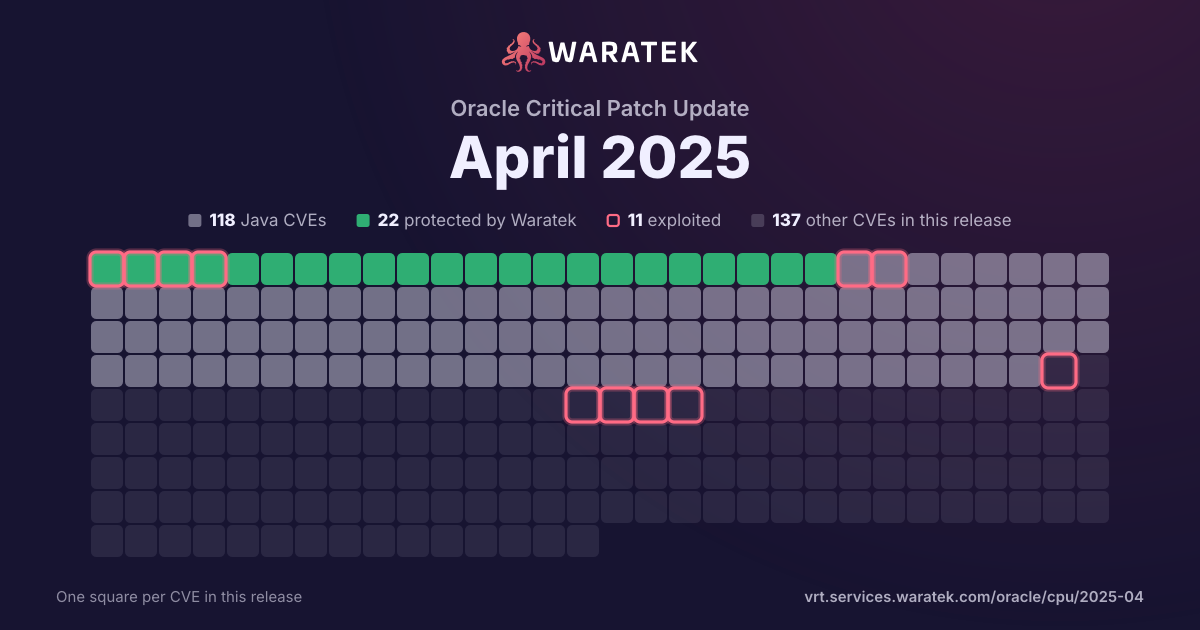
By status
22Protected by Waratek8Mitigation candidate88No exploit published16Outside Waratek scope121Not applicable
11Exploited, marked by the ring
No exploit published. For 33 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 8 matches · 4 protected · 2 exploited · 1 CISA KEV · 4 EPSS ≥ 0.5
Protected by Waratek
4
50.0%
Rule in development
0
0.0%
Mitigation candidate
4
50.0%
No exploit published
0
0.0%
blocked by ARMR today
4
50.0%
partly blocked
0
0.0%
not blocked
4
50.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
2
25.0%
Working exploit published
3
37.5%
Proof of concept only
3
37.5%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 2 / quarter
Q2 202
Protected by Waratek1
Mitigation candidate1
High2
blocked by ARMR today1
not blocked1
Working exploit published1
Proof of concept only1
Q3 201
Mitigation candidate1
High1
not blocked1
Working exploit published1
Q4 200
Q1 210
Q2 210
Q3 210
Q4 210
Q1 220
Q2 220
Q3 220
Q4 220
Q1 230
Q2 230
Q3 230
Q4 231
Mitigation candidate1
High1
not blocked1
Exploited1
Q1 241
Mitigation candidate1
High1
not blocked1
Proof of concept only1
Q2 240
Q3 242
Protected by Waratek2
High2
blocked by ARMR today2
Exploited1
Proof of concept only1
Q4 241
Protected by Waratek1
High1
blocked by ARMR today1
Working exploit published1
Q2 20Q4 20Q2 21Q4 21Q2 22Q4 22Q2 23Q4 23Q2 24Q4 24
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2024-38819 | High | 2024-12-19 | Protected by Waratek | Working exploit published | Applications serving static resources through the functional web frameworks WebMvc.fn or WebFlux.fn are vulnerable to path traversal attacks. An attacker can craft malicious HTTP requests and obtain any file on the file system that is also accessible to the process in which the Spring application is running. |
| CVE-2024-38816 | High | 2024-09-13 | Protected by Waratek | Exploited | Applications serving static resources through the functional web frameworks WebMvc.fn or WebFlux.fn are vulnerable to path traversal attacks. An attacker can craft malicious HTTP requests and obtain any file on the file system that is also accessible to the process in which the Spring application is running. Specifically, an application is vulnerable when both of the following are true: * the web application uses RouterFunctions to serve static resources * resource handling is explicitly configured with a FileSystemResource location However, malicious requests are blocked and rejected when any of the following is true: * the Spring Security HTTP Firewall https://docs.spring.io/spring-security/reference/servlet/exploits/firewall.html is in use * the application runs on Tomcat or Jetty |
| CVE-2024-43044 | High | 2024-08-07 | Protected by Waratek | Proof of concept only | Jenkins 2.470 and earlier, LTS 2.452.3 and earlier allows agent processes to read arbitrary files from the Jenkins controller file system by using the `ClassLoaderProxy#fetchJar` method in the Remoting library. |
| CVE-2024-24549 | High | 2024-03-13 | Mitigation candidate | Proof of concept only | Denial of Service due to improper input validation vulnerability for HTTP/2 requests in Apache Tomcat. When processing an HTTP/2 request, if the request exceeded any of the configured limits for headers, the associated HTTP/2 stream was not reset until after all of the headers had been processed.This issue affects Apache Tomcat: from 11.0.0-M1 through 11.0.0-M16, from 10.1.0-M1 through 10.1.18, from 9.0.0-M1 through 9.0.85, from 8.5.0 through 8.5.98. Other, older, EOL versions may also be affected. Users are recommended to upgrade to version 11.0.0-M17, 10.1.19, 9.0.86 or 8.5.99 which fix the issue. |
| CVE-2023-44487 | High | 2023-10-10 | Mitigation candidate | Exploited | The HTTP/2 protocol allows a denial of service (server resource consumption) because request cancellation can reset many streams quickly, as exploited in the wild in August through October 2023. |
| CVE-2020-13935 | High | 2020-07-14 | Mitigation candidate | Working exploit published | The payload length in a WebSocket frame was not correctly validated in Apache Tomcat 10.0.0-M1 to 10.0.0-M6, 9.0.0.M1 to 9.0.36, 8.5.0 to 8.5.56 and 7.0.27 to 7.0.104. Invalid payload lengths could trigger an infinite loop. Multiple requests with invalid payload lengths could lead to a denial of service. |
| CVE-2020-11996 | High | 2020-06-26 | Mitigation candidate | Proof of concept only | A specially crafted sequence of HTTP/2 requests sent to Apache Tomcat 10.0.0-M1 to 10.0.0-M5, 9.0.0.M1 to 9.0.35 and 8.5.0 to 8.5.55 could trigger high CPU usage for several seconds. If a sufficient number of such requests were made on concurrent HTTP/2 connections, the server could become unresponsive. |
| CVE-2020-9484 | High | 2020-05-20 | Protected by Waratek | Working exploit published | When using Apache Tomcat versions 10.0.0-M1 to 10.0.0-M4, 9.0.0.M1 to 9.0.34, 8.5.0 to 8.5.54 and 7.0.0 to 7.0.103 if a) an attacker is able to control the contents and name of a file on the server; and b) the server is configured to use the PersistenceManager with a FileStore; and c) the PersistenceManager is configured with sessionAttributeValueClassNameFilter="null" (the default unless a SecurityManager is used) or a sufficiently lax filter to allow the attacker provided object to be deserialized; and d) the attacker knows the relative file path from the storage location used by FileStore to the file the attacker has control over; then, using a specifically crafted request, the attacker will be able to trigger remote code execution via deserialization of the file under their control. Note that all of conditions a) to d) must be true for the attack to succeed. |