
Oracle Critical Patch Update July 2023
Released July 2023 · Oracle's advisory ↗ · ← Critical Patch Update, April 2023 · Critical Patch Update, October 2023 →
269 CVEs in this release, one square each
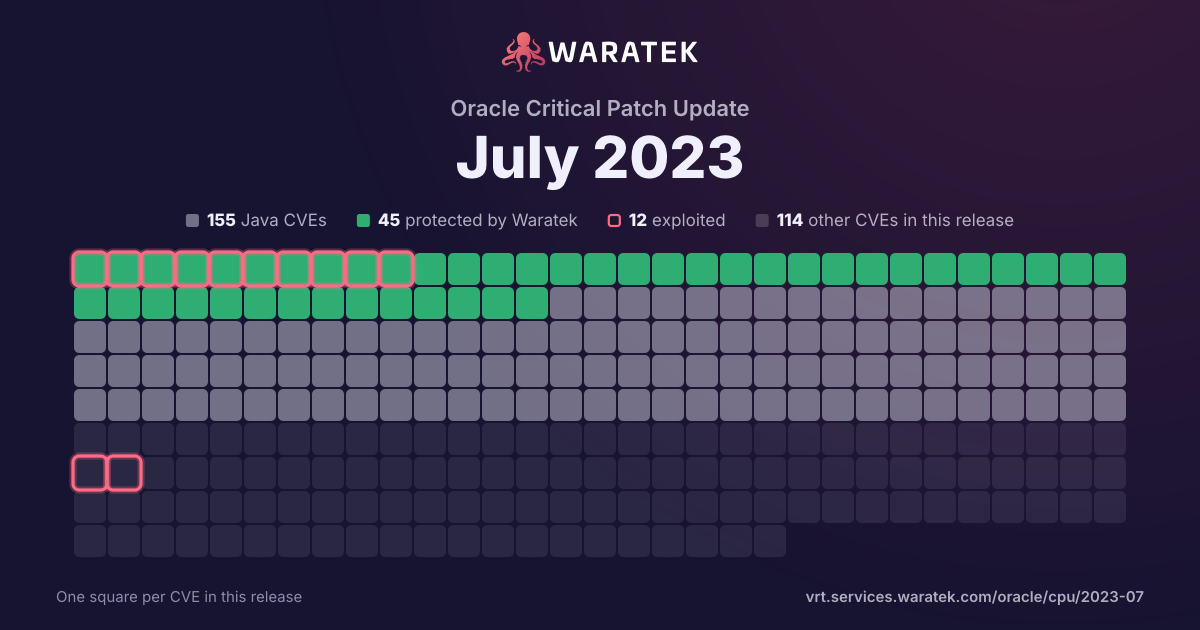
By status
45Protected by Waratek5Mitigation candidate105No exploit published31Outside Waratek scope83Not applicable
12Exploited, marked by the ring
No exploit published. For 37 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 25 matches · 11 in Waratek scope · 0 protected · 1 exploited · 0 CISA KEV · 5 public PoC · 1 EPSS ≥ 0.5
25matches
11in Waratek scope44.0%
0protected0.0%
1exploited4.0%
0CISA KEV0.0%
5public PoC20.0%
1EPSS ≥ 0.54.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
3
12.0%
No exploit published
8
32.0%
Outside Waratek scope
2
8.0%
Not applicable
12
48.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
25
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
4.0%
Working exploit published
0
0.0%
Proof of concept only
7
28.0%
Forecast only
0
0.0%
No public exploit
17
68.0%
split by
peak 8 / quarter
Q3 191
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
Q4 191
No exploit published1
Critical1
not blocked1
No public exploit1
Q1 201
No exploit published1
Critical1
not blocked1
No public exploit1
Q2 200
Q3 200
Q4 200
Q1 211
Not applicable1
Critical1
not blocked1
No public exploit1
Q2 210
Q3 210
Q4 210
Q1 220
Q2 222
Not applicable2
Critical2
not blocked2
Proof of concept only1
No public exploit1
Q3 228
Mitigation candidate1
No exploit published3
Outside Waratek scope1
Not applicable3
Critical8
not blocked8
Proof of concept only2
No public exploit6
Q4 223
Mitigation candidate2
Not applicable1
Critical3
not blocked3
Proof of concept only3
Q1 234
No exploit published1
Not applicable3
Critical4
not blocked4
Exploited1
Proof of concept only1
No public exploit2
Q2 232
No exploit published2
Critical2
not blocked2
No public exploit2
Q3 232
Not applicable2
Critical2
not blocked2
No public exploit2
Q3 19Q1 20Q3 20Q1 21Q3 21Q1 22Q3 22Q1 23Q3 23
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2023-21975 | Critical | 2023-07-18 | Not applicable | No public exploit | Vulnerability in the Application Express Customers Plugin product of Oracle Application Express (component: User Account). Supported versions that are affected are Application Express Customers Plugin: 18.2-22.2. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Application Express Customers Plugin. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Application Express Customers Plugin, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in takeover of Application Express Customers Plugin. CVSS 3.1 Base Score 9.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:H/I:H/A:H). |
| CVE-2023-21974 | Critical | 2023-07-18 | Not applicable | No public exploit | Vulnerability in the Application Express Team Calendar Plugin product of Oracle Application Express (component: User Account). Supported versions that are affected are Application Express Team Calendar Plugin: 18.2-22.1. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Application Express Team Calendar Plugin. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Application Express Team Calendar Plugin, attacks may significantly impact additional products (scope change). Successful attacks of this vulnerability can result in takeover of Application Express Team Calendar Plugin. CVSS 3.1 Base Score 9.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:H/I:H/A:H). |
| CVE-2023-20873 | Critical | 2023-04-20 | No exploit published | No public exploit | In Spring Boot versions 3.0.0 - 3.0.5, 2.7.0 - 2.7.10, and older unsupported versions, an application that is deployed to Cloud Foundry could be susceptible to a security bypass. Users of affected versions should apply the following mitigation: 3.0.x users should upgrade to 3.0.6+. 2.7.x users should upgrade to 2.7.11+. Users of older, unsupported versions should upgrade to 3.0.6+ or 2.7.11+. |
| CVE-2023-26119 | Critical | 2023-04-03 | No exploit published | No public exploit | Versions of the package net.sourceforge.htmlunit:htmlunit from 0 and before 3.0.0 are vulnerable to Remote Code Execution (RCE) via XSTL, when browsing the attacker’s webpage. |
| CVE-2023-27898 | Critical | 2023-03-10 | No exploit published | No public exploit | Jenkins 2.270 through 2.393 (both inclusive), LTS 2.277.1 through 2.375.3 (both inclusive) does not escape the Jenkins version a plugin depends on when rendering the error message stating its incompatibility with the current version of Jenkins, resulting in a stored cross-site scripting (XSS) vulnerability exploitable by attackers able to provide plugins to the configured update sites and have this message shown by Jenkins instances. |
| CVE-2023-25690 | Critical | 2023-03-07 | Not applicable | Exploited | Some mod_proxy configurations on Apache HTTP Server versions 2.4.0 through 2.4.55 allow a HTTP Request Smuggling attack. Configurations are affected when mod_proxy is enabled along with some form of RewriteRule or ProxyPassMatch in which a non-specific pattern matches some portion of the user-supplied request-target (URL) data and is then re-inserted into the proxied request-target using variable substitution. For example, something like: RewriteEngine on RewriteRule "^/here/(.*)" "http://example.com:8080/elsewhere?$1"; [P] ProxyPassReverse /here/ http://example.com:8080/ Request splitting/smuggling could result in bypass of access controls in the proxy server, proxying unintended URLs to existing origin servers, and cache poisoning. Users are recommended to update to at least version 2.4.56 of Apache HTTP Server. |
| CVE-2023-23914 | Critical | 2023-02-23 | Not applicable | Proof of concept only | A cleartext transmission of sensitive information vulnerability exists in curl <v7.88.0 that could cause HSTS functionality fail when multiple URLs are requested serially. Using its HSTS support, curl can be instructed to use HTTPS instead of usingan insecure clear-text HTTP step even when HTTP is provided in the URL. ThisHSTS mechanism would however surprisingly be ignored by subsequent transferswhen done on the same command line because the state would not be properlycarried on. |
| CVE-2022-36760 | Critical | 2023-01-17 | Not applicable | No public exploit | Inconsistent Interpretation of HTTP Requests ('HTTP Request Smuggling') vulnerability in mod_proxy_ajp of Apache HTTP Server allows an attacker to smuggle requests to the AJP server it forwards requests to. This issue affects Apache HTTP Server Apache HTTP Server 2.4 version 2.4.54 and prior versions. |
| CVE-2022-46364 | Critical | 2022-12-13 | Mitigation candidate | Proof of concept only | A SSRF vulnerability in parsing the href attribute of XOP:Include in MTOM requests in versions of Apache CXF before 3.5.5 and 3.4.10 allows an attacker to perform SSRF style attacks on webservices that take at least one parameter of any type. |
| CVE-2022-31692 | Critical | 2022-10-31 | Mitigation candidate | Proof of concept only | Spring Security, versions 5.7 prior to 5.7.5 and 5.6 prior to 5.6.9 could be susceptible to authorization rules bypass via forward or include dispatcher types. Specifically, an application is vulnerable when all of the following are true: The application expects that Spring Security applies security to forward and include dispatcher types. The application uses the AuthorizationFilter either manually or via the authorizeHttpRequests() method. The application configures the FilterChainProxy to apply to forward and/or include requests (e.g. spring.security.filter.dispatcher-types = request, error, async, forward, include). The application may forward or include the request to a higher privilege-secured endpoint.The application configures Spring Security to apply to every dispatcher type via authorizeHttpRequests().shouldFilterAllDispatcherTypes(true) |
| CVE-2022-37454 | Critical | 2022-10-21 | Not applicable | Proof of concept only | The Keccak XKCP SHA-3 reference implementation before fdc6fef has an integer overflow and resultant buffer overflow that allows attackers to execute arbitrary code or eliminate expected cryptographic properties. This occurs in the sponge function interface. |
| CVE-2022-37434 | Critical | 2022-08-05 | Outside Waratek scope | Proof of concept only | zlib through 1.2.12 has a heap-based buffer over-read or buffer overflow in inflate in inflate.c via a large gzip header extra field. NOTE: only applications that call inflateGetHeader are affected. Some common applications bundle the affected zlib source code but may be unable to call inflateGetHeader (e.g., see the nodejs/node reference). |
| CVE-2020-35169 | Critical | 2022-07-11 | No exploit published | No public exploit | Dell BSAFE Crypto-C Micro Edition, versions before 4.1.5, and Dell BSAFE Micro Edition Suite, versions before 4.5.2, contain an Improper Input Validation Vulnerability. |
| CVE-2020-35168 | Critical | 2022-07-11 | Not applicable | No public exploit | Dell BSAFE Crypto-C Micro Edition, versions before 4.1.5, and Dell BSAFE Micro Edition Suite, versions before 4.6, contain an Observable Timing Discrepancy Vulnerability. |
| CVE-2020-35167 | Critical | 2022-07-11 | Not applicable | No public exploit | Dell BSAFE Crypto-C Micro Edition, versions before 4.1.5, and Dell BSAFE Micro Edition Suite, versions before 4.6, contain an Observable Timing Discrepancy Vulnerability. |
| CVE-2020-35166 | Critical | 2022-07-11 | No exploit published | No public exploit | Dell BSAFE Crypto-C Micro Edition, versions before 4.1.5, and Dell BSAFE Micro Edition Suite, versions before 4.6, contain an Observable Timing Discrepancy Vulnerability. |
| CVE-2020-35163 | Critical | 2022-07-11 | Not applicable | No public exploit | Dell BSAFE Crypto-C Micro Edition, versions before 4.1.5, and Dell BSAFE Micro Edition Suite, versions before 4.6, contain a Use of Insufficiently Random Values Vulnerability. |
| CVE-2020-29508 | Critical | 2022-07-11 | No exploit published | No public exploit | Dell BSAFE Crypto-C Micro Edition, versions before 4.1.5, and Dell BSAFE Micro Edition Suite, versions before 4.6, contain an Improper Input Validation Vulnerability. |
| CVE-2022-33980 | Critical | 2022-07-06 | Mitigation candidate | Proof of concept only | Apache Commons Configuration performs variable interpolation, allowing properties to be dynamically evaluated and expanded. The standard format for interpolation is "${prefix:name}", where "prefix" is used to locate an instance of org.apache.commons.configuration2.interpol.Lookup that performs the interpolation. Starting with version 2.4 and continuing through 2.7, the set of default Lookup instances included interpolators that could result in arbitrary code execution or contact with remote servers. These lookups are: - "script" - execute expressions using the JVM script execution engine (javax.script) - "dns" - resolve dns records - "url" - load values from urls, including from remote servers Applications using the interpolation defaults in the affected versions may be vulnerable to remote code execution or unintentional contact with remote servers if untrusted configuration values are used. Users are recommended to upgrade to Apache Commons Configuration 2.8.0, which disables the problematic interpolators by default. |
| CVE-2022-29361 | Critical | 2022-05-25 | Not applicable | Proof of concept only | Improper parsing of HTTP requests in Pallets Werkzeug v2.1.0 and below allows attackers to perform HTTP Request Smuggling using a crafted HTTP request with multiple requests included inside the body. NOTE: the vendor's position is that this behavior can only occur in unsupported configurations involving development mode and an HTTP server from outside the Werkzeug project |
| CVE-2022-27404 | Critical | 2022-04-22 | Not applicable | No public exploit | FreeType commit 1e2eb65048f75c64b68708efed6ce904c31f3b2f was discovered to contain a heap buffer overflow via the function sfnt_init_face. |
| CVE-2021-24112 | Critical | 2021-02-25 | Not applicable | No public exploit | .NET Core Remote Code Execution Vulnerability |
| CVE-2020-1953 | Critical | 2020-03-13 | No exploit published | No public exploit | Apache Commons Configuration uses a third-party library to parse YAML files which by default allows the instantiation of classes if the YAML includes special statements. Apache Commons Configuration versions 2.2, 2.3, 2.4, 2.5, 2.6 did not change the default settings of this library. So if a YAML file was loaded from an untrusted source, it could therefore load and execute code out of the control of the host application. |
| CVE-2019-17531 | Critical | 2019-10-12 | No exploit published | No public exploit | A Polymorphic Typing issue was discovered in FasterXML jackson-databind 2.0.0 through 2.9.10. When Default Typing is enabled (either globally or for a specific property) for an externally exposed JSON endpoint and the service has the apache-log4j-extra (version 1.2.x) jar in the classpath, and an attacker can provide a JNDI service to access, it is possible to make the service execute a malicious payload. |
| CVE-2019-13990 | Critical | 2019-07-26 | Outside Waratek scope | No public exploit | initDocumentParser in xml/XMLSchedulingDataProcessor.java in Terracotta Quartz Scheduler through 2.3.0 allows XXE attacks via a job description. |