
Oracle Critical Patch Update October 2022
Released October 2022 · Oracle's advisory ↗ · ← Critical Patch Update, July 2022 · Critical Patch Update, January 2023 →
179 CVEs in this release, one square each
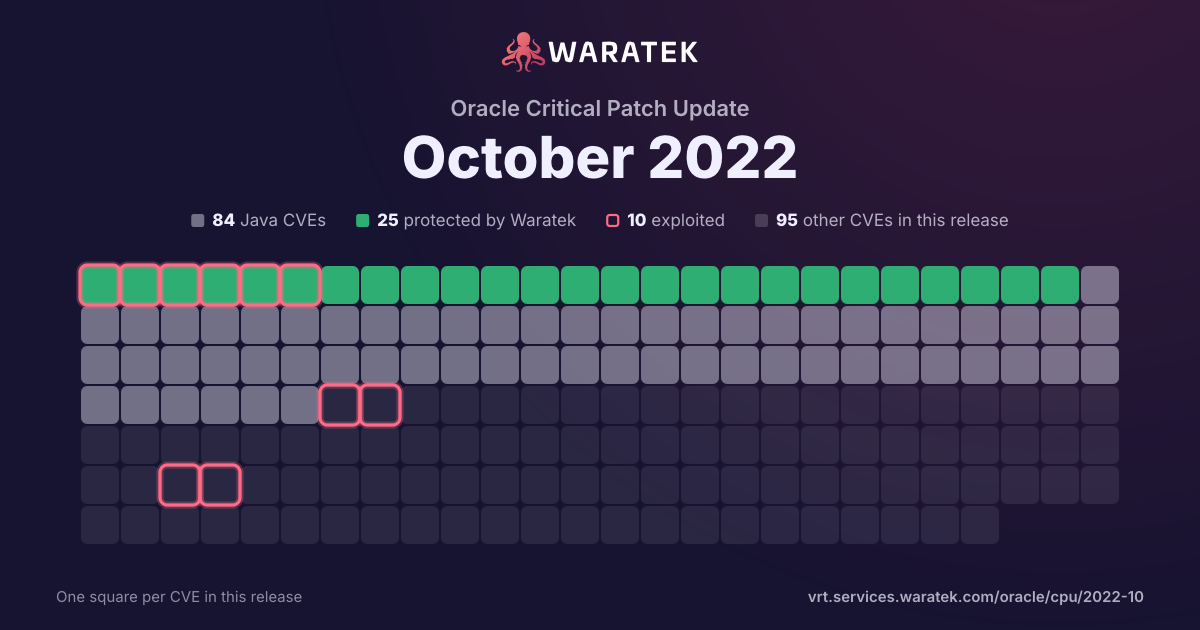
By status
25Protected by Waratek4Mitigation candidate55No exploit published48Outside Waratek scope47Not applicable
10Exploited, marked by the ring
No exploit published. For 33 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 8 matches · 3 protected · 0 exploited · 0 CISA KEV · 4 public PoC · 1 EPSS ≥ 0.5
Protected by Waratek
3
37.5%
Rule in development
0
0.0%
Mitigation candidate
3
37.5%
No exploit published
2
25.0%
blocked by ARMR today
3
37.5%
partly blocked
0
0.0%
not blocked
5
62.5%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
8
100.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 2 / month
Jan 221
Protected by Waratek1
Critical1
blocked by ARMR today1
Proof of concept only1
Feb 221
No exploit published1
High1
not blocked1
Proof of concept only1
Mar 220
Apr 221
Protected by Waratek1
Critical1
blocked by ARMR today1
Proof of concept only1
May 222
Mitigation candidate1
No exploit published1
Critical1
Medium1
not blocked2
Proof of concept only2
Jun 221
Mitigation candidate1
Critical1
not blocked1
Proof of concept only1
Jul 221
Mitigation candidate1
Critical1
not blocked1
Proof of concept only1
Aug 221
Protected by Waratek1
Medium1
blocked by ARMR today1
Proof of concept only1
Jan 22Feb 22Mar 22Apr 22May 22Jun 22Jul 22Aug 22
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2022-36033 | Medium | 2022-08-29 | Protected by Waratek | Proof of concept only | jsoup is a Java HTML parser, built for HTML editing, cleaning, scraping, and cross-site scripting (XSS) safety. jsoup may incorrectly sanitize HTML including `javascript:` URL expressions, which could allow XSS attacks when a reader subsequently clicks that link. If the non-default `SafeList.preserveRelativeLinks` option is enabled, HTML including `javascript:` URLs that have been crafted with control characters will not be sanitized. If the site that this HTML is published on does not set a Content Security Policy, an XSS attack is then possible. This issue is patched in jsoup 1.15.3. Users should upgrade to this version. Additionally, as the unsanitized input may have been persisted, old content should be cleaned again using the updated version. To remediate this issue without immediately upgrading: - disable `SafeList.preserveRelativeLinks`, which will rewrite input URLs as absolute URLs - ensure an appropriate [Content Security Policy](https://developer.mozilla.org/en-US/docs/Web/HTTP/CSP) is defined. (This should be used regardless of upgrading, as a defence-in-depth best practice.) |
| CVE-2022-33980 | Critical | 2022-07-06 | Mitigation candidate | Proof of concept only | Apache Commons Configuration performs variable interpolation, allowing properties to be dynamically evaluated and expanded. The standard format for interpolation is "${prefix:name}", where "prefix" is used to locate an instance of org.apache.commons.configuration2.interpol.Lookup that performs the interpolation. Starting with version 2.4 and continuing through 2.7, the set of default Lookup instances included interpolators that could result in arbitrary code execution or contact with remote servers. These lookups are: - "script" - execute expressions using the JVM script execution engine (javax.script) - "dns" - resolve dns records - "url" - load values from urls, including from remote servers Applications using the interpolation defaults in the affected versions may be vulnerable to remote code execution or unintentional contact with remote servers if untrusted configuration values are used. Users are recommended to upgrade to Apache Commons Configuration 2.8.0, which disables the problematic interpolators by default. |
| CVE-2022-32532 | Critical | 2022-06-29 | Mitigation candidate | Proof of concept only | Apache Shiro before 1.9.1, A RegexRequestMatcher can be misconfigured to be bypassed on some servlet containers. Applications using RegExPatternMatcher with `.` in the regular expression are possibly vulnerable to an authorization bypass. |
| CVE-2022-22978 | Critical | 2022-05-19 | Mitigation candidate | Proof of concept only | In spring security versions prior to 5.4.11+, 5.5.7+ , 5.6.4+ and older unsupported versions, RegexRequestMatcher can easily be misconfigured to be bypassed on some servlet containers. Applications using RegexRequestMatcher with `.` in the regular expression are possibly vulnerable to an authorization bypass. |
| CVE-2022-24823 | Medium | 2022-05-06 | No exploit published | Proof of concept only | Netty is an open-source, asynchronous event-driven network application framework. The package `io.netty:netty-codec-http` prior to version 4.1.77.Final contains an insufficient fix for CVE-2021-21290. When Netty's multipart decoders are used local information disclosure can occur via the local system temporary directory if temporary storing uploads on the disk is enabled. This only impacts applications running on Java version 6 and lower. Additionally, this vulnerability impacts code running on Unix-like systems, and very old versions of Mac OSX and Windows as they all share the system temporary directory between all users. Version 4.1.77.Final contains a patch for this vulnerability. As a workaround, specify one's own `java.io.tmpdir` when starting the JVM or use DefaultHttpDataFactory.setBaseDir(...) to set the directory to something that is only readable by the current user. |
| CVE-2022-23457 | Critical | 2022-04-25 | Protected by Waratek | Proof of concept only | ESAPI (The OWASP Enterprise Security API) is a free, open source, web application security control library. Prior to version 2.3.0.0, the default implementation of `Validator.getValidDirectoryPath(String, String, File, boolean)` may incorrectly treat the tested input string as a child of the specified parent directory. This potentially could allow control-flow bypass checks to be defeated if an attack can specify the entire string representing the 'input' path. This vulnerability is patched in release 2.3.0.0 of ESAPI. As a workaround, it is possible to write one's own implementation of the Validator interface. However, maintainers do not recommend this. |
| CVE-2021-43859 | High | 2022-02-01 | No exploit published | Proof of concept only | XStream is an open source java library to serialize objects to XML and back again. Versions prior to 1.4.19 may allow a remote attacker to allocate 100% CPU time on the target system depending on CPU type or parallel execution of such a payload resulting in a denial of service only by manipulating the processed input stream. XStream 1.4.19 monitors and accumulates the time it takes to add elements to collections and throws an exception if a set threshold is exceeded. Users are advised to upgrade as soon as possible. Users unable to upgrade may set the NO_REFERENCE mode to prevent recursion. See GHSA-rmr5-cpv2-vgjf for further details on a workaround if an upgrade is not possible. |
| CVE-2022-23305 | Critical | 2022-01-18 | Protected by Waratek | Proof of concept only | By design, the JDBCAppender in Log4j 1.2.x accepts an SQL statement as a configuration parameter where the values to be inserted are converters from PatternLayout. The message converter, %m, is likely to always be included. This allows attackers to manipulate the SQL by entering crafted strings into input fields or headers of an application that are logged allowing unintended SQL queries to be executed. Note this issue only affects Log4j 1.x when specifically configured to use the JDBCAppender, which is not the default. Beginning in version 2.0-beta8, the JDBCAppender was re-introduced with proper support for parameterized SQL queries and further customization over the columns written to in logs. Apache Log4j 1.2 reached end of life in August 2015. Users should upgrade to Log4j 2 as it addresses numerous other issues from the previous versions. |