
Oracle Critical Patch Update July 2022
Released July 2022 · Oracle's advisory ↗ · ← Critical Patch Update, April 2022 · Critical Patch Update, October 2022 →
188 CVEs in this release, one square each
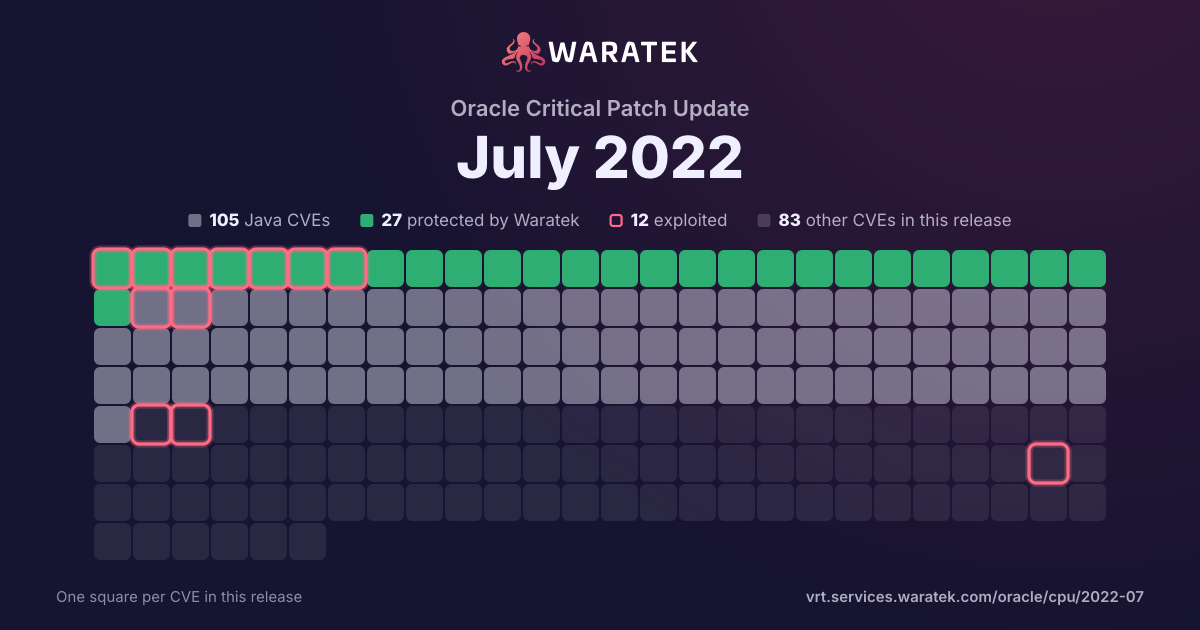
By status
27Protected by Waratek6Mitigation candidate72No exploit published49Outside Waratek scope34Not applicable
12Exploited, marked by the ring
No exploit published. For 47 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 4 matches · 3 in Waratek scope · 1 protected · 0 exploited · 0 CISA KEV · 3 EPSS ≥ 0.5
Protected by Waratek
1
25.0%
Rule in development
0
0.0%
Mitigation candidate
2
50.0%
No exploit published
0
0.0%
Outside Waratek scope
1
25.0%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
25.0%
partly blocked
0
0.0%
not blocked
3
75.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
4
100.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 1 / quarter
Q2 191
Outside Waratek scope1
High1
not blocked1
Working exploit published1
Q3 190
Q4 190
Q1 200
Q2 201
Protected by Waratek1
Medium1
blocked by ARMR today1
Working exploit published1
Q3 200
Q4 200
Q1 210
Q2 211
Mitigation candidate1
High1
not blocked1
Working exploit published1
Q3 210
Q4 210
Q1 220
Q2 221
Mitigation candidate1
High1
not blocked1
Working exploit published1
Q2 19Q4 19Q2 20Q4 20Q2 21Q4 21Q2 22
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2022-29885 | High | 2022-05-12 | Mitigation candidate | Working exploit published | The documentation of Apache Tomcat 10.1.0-M1 to 10.1.0-M14, 10.0.0-M1 to 10.0.20, 9.0.13 to 9.0.62 and 8.5.38 to 8.5.78 for the EncryptInterceptor incorrectly stated it enabled Tomcat clustering to run over an untrusted network. This was not correct. While the EncryptInterceptor does provide confidentiality and integrity protection, it does not protect against all risks associated with running over any untrusted network, particularly DoS risks. |
| CVE-2021-29505 | High | 2021-05-28 | Mitigation candidate | Working exploit published | XStream is software for serializing Java objects to XML and back again. A vulnerability in XStream versions prior to 1.4.17 may allow a remote attacker has sufficient rights to execute commands of the host only by manipulating the processed input stream. No user who followed the recommendation to setup XStream's security framework with a whitelist limited to the minimal required types is affected. The vulnerability is patched in version 1.4.17. |
| CVE-2020-7656 | Medium | 2020-05-19 | Protected by Waratek | Working exploit published | jquery prior to 1.9.0 allows Cross-site Scripting attacks via the load method. The load method fails to recognize and remove "<script>" HTML tags that contain a whitespace character, i.e: "</script >", which results in the enclosed script logic to be executed. |
| CVE-2019-0227 | High | 2019-05-01 | Outside Waratek scope | Working exploit published | A Server Side Request Forgery (SSRF) vulnerability affected the Apache Axis 1.4 distribution that was last released in 2006. Security and bug commits commits continue in the projects Axis 1.x Subversion repository, legacy users are encouraged to build from source. The successor to Axis 1.x is Axis2, the latest version is 1.7.9 and is not vulnerable to this issue. |