
Oracle Critical Patch Update April 2022
Released April 2022 · Oracle's advisory ↗ · ← Critical Patch Update, January 2022 · Critical Patch Update, July 2022 →
222 CVEs in this release, one square each
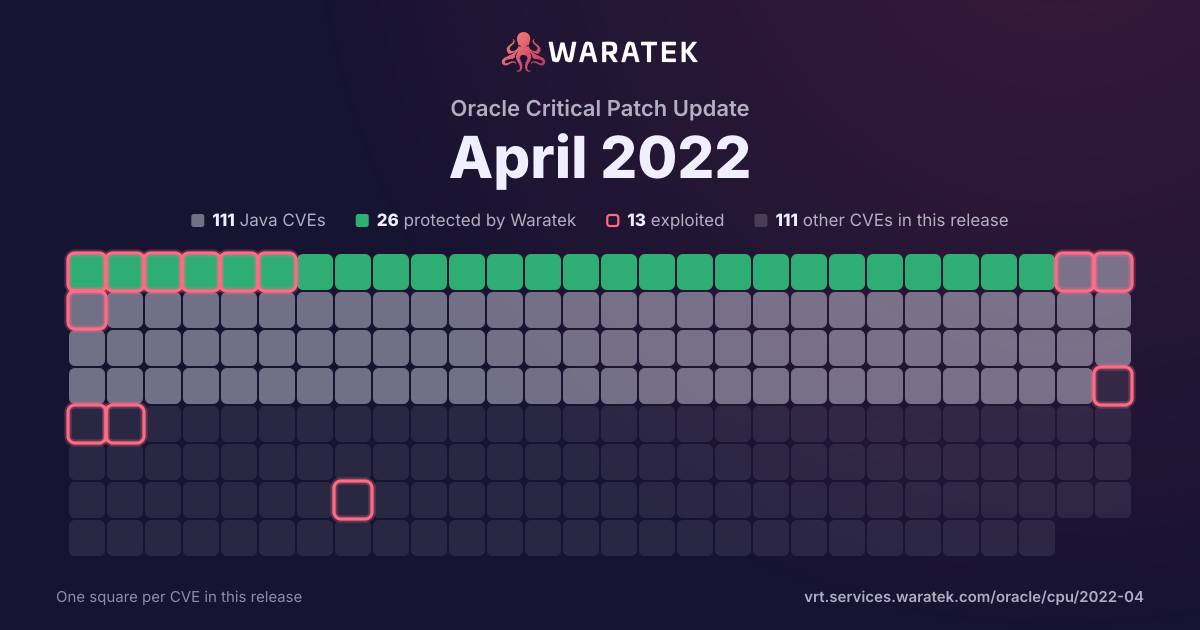
By status
26Protected by Waratek5Mitigation candidate80No exploit published64Outside Waratek scope47Not applicable
13Exploited, marked by the ring
No exploit published. For 40 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 6 matches · 3 in Waratek scope · 3 protected · 0 exploited · 0 CISA KEV · 5 EPSS ≥ 0.5
Protected by Waratek
3
50.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
2
33.3%
Not applicable
1
16.7%
Withdrawn CVE
0
0.0%
blocked by ARMR today
3
50.0%
partly blocked
0
0.0%
not blocked
3
50.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
6
100.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 2 / quarter
Q2 192
Protected by Waratek1
Outside Waratek scope1
High1
Medium1
blocked by ARMR today1
not blocked1
Working exploit published2
Q3 190
Q4 190
Q1 200
Q2 200
Q3 200
Q4 200
Q1 210
Q2 212
Protected by Waratek1
Not applicable1
High1
Medium1
blocked by ARMR today1
not blocked1
Working exploit published2
Q3 210
Q4 211
Outside Waratek scope1
Critical1
not blocked1
Working exploit published1
Q1 221
Protected by Waratek1
Critical1
blocked by ARMR today1
Working exploit published1
Q2 19Q3 19Q4 19Q1 20Q2 20Q3 20Q4 20Q1 21Q2 21Q3 21Q4 21Q1 22
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2021-42392 | Critical | 2022-01-10 | Protected by Waratek | Working exploit published | The org.h2.util.JdbcUtils.getConnection method of the H2 database takes as parameters the class name of the driver and URL of the database. An attacker may pass a JNDI driver name and a URL leading to a LDAP or RMI servers, causing remote code execution. This can be exploited through various attack vectors, most notably through the H2 Console which leads to unauthenticated remote code execution. |
| CVE-2021-44790 | Critical | 2021-12-20 | Outside Waratek scope | Working exploit published | A carefully crafted request body can cause a buffer overflow in the mod_lua multipart parser (r:parsebody() called from Lua scripts). The Apache httpd team is not aware of an exploit for the vulnerabilty though it might be possible to craft one. This issue affects Apache HTTP Server 2.4.51 and earlier. |
| CVE-2020-6950 | Medium | 2021-06-02 | Protected by Waratek | Working exploit published | Directory traversal in Eclipse Mojarra before 2.3.14 allows attackers to read arbitrary files via the loc parameter or con parameter. |
| CVE-2021-23017 | High | 2021-06-01 | Not applicable | Working exploit published | A security issue in nginx resolver was identified, which might allow an attacker who is able to forge UDP packets from the DNS server to cause 1-byte memory overwrite, resulting in worker process crash or potential other impact. |
| CVE-2019-3799 | Medium | 2019-05-06 | Protected by Waratek | Working exploit published | Spring Cloud Config, versions 2.1.x prior to 2.1.2, versions 2.0.x prior to 2.0.4, and versions 1.4.x prior to 1.4.6, and older unsupported versions allow applications to serve arbitrary configuration files through the spring-cloud-config-server module. A malicious user, or attacker, can send a request using a specially crafted URL that can lead a directory traversal attack. |
| CVE-2019-0227 | High | 2019-05-01 | Outside Waratek scope | Working exploit published | A Server Side Request Forgery (SSRF) vulnerability affected the Apache Axis 1.4 distribution that was last released in 2006. Security and bug commits commits continue in the projects Axis 1.x Subversion repository, legacy users are encouraged to build from source. The successor to Axis 1.x is Axis2, the latest version is 1.7.9 and is not vulnerable to this issue. |