
Oracle Critical Patch Update January 2022
Released January 2022 · Oracle's advisory ↗ · ← Critical Patch Update, October 2021 · Critical Patch Update, April 2022 →
266 CVEs in this release, one square each
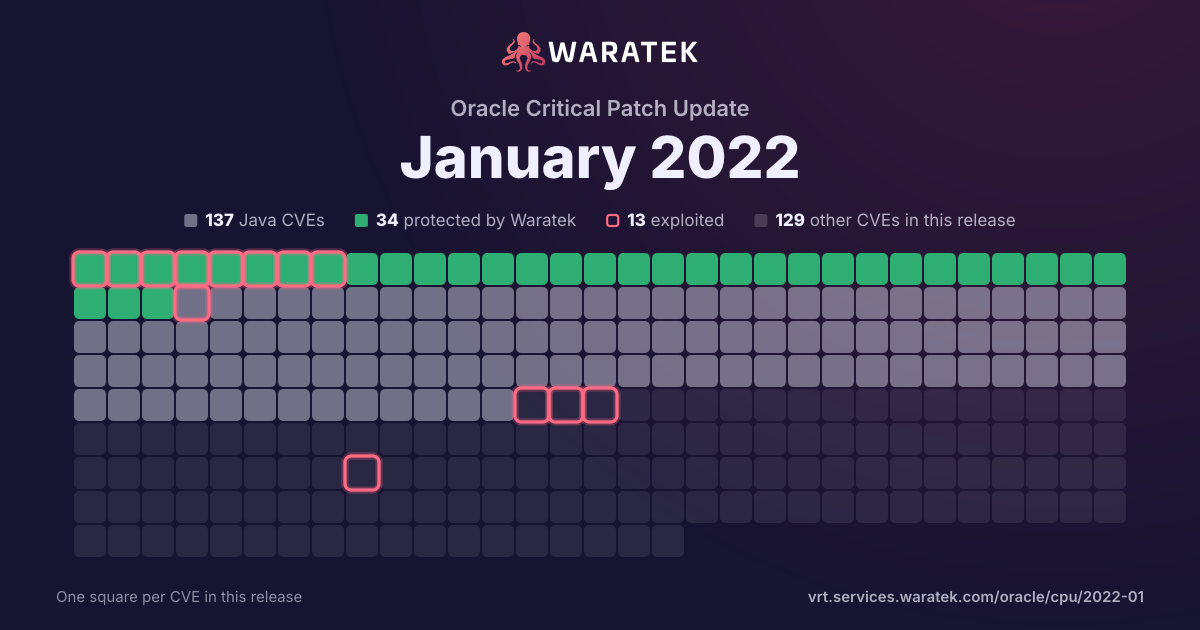
By status
34Protected by Waratek3Mitigation candidate100No exploit published57Outside Waratek scope72Not applicable
13Exploited, marked by the ring
No exploit published. For 71 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 103 matches · 0 protected · 1 exploited · 0 CISA KEV · 2 public PoC · 4 EPSS ≥ 0.5
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
3
2.9%
No exploit published
100
97.1%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
103
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
1.0%
Working exploit published
2
1.9%
Proof of concept only
0
0.0%
Forecast only
2
1.9%
No public exploit
98
95.1%
split by
peak 69 / quarter
Q1 181
No exploit published1
Medium1
not blocked1
No public exploit1
Q2 180
Q3 180
Q4 180
Q1 190
Q2 190
Q3 190
Q4 191
No exploit published1
Critical1
not blocked1
No public exploit1
Q1 200
Q2 200
Q3 203
Mitigation candidate1
No exploit published2
High2
Medium1
not blocked3
Working exploit published1
No public exploit2
Q4 204
No exploit published4
High3
Low1
not blocked4
No public exploit4
Q1 217
No exploit published7
Critical1
High4
Medium2
not blocked7
No public exploit7
Q2 216
Mitigation candidate1
No exploit published5
High4
Medium2
not blocked6
Working exploit published1
Forecast only1
No public exploit4
Q3 2112
Mitigation candidate1
No exploit published11
Critical1
High7
Medium4
not blocked12
Exploited1
Forecast only1
No public exploit10
Q4 210
Q1 2269
No exploit published69
Critical6
High12
Medium48
Low3
not blocked69
No public exploit69
Q1 18Q3 18Q1 19Q3 19Q1 20Q3 20Q1 21Q3 21Q1 22
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2020-13935 | High | 2020-07-14 | Mitigation candidate | Working exploit published | The payload length in a WebSocket frame was not correctly validated in Apache Tomcat 10.0.0-M1 to 10.0.0-M6, 9.0.0.M1 to 9.0.36, 8.5.0 to 8.5.56 and 7.0.27 to 7.0.104. Invalid payload lengths could trigger an infinite loop. Multiple requests with invalid payload lengths could lead to a denial of service. |
| CVE-2019-17495 | Critical | 2019-10-10 | No exploit published | No public exploit | A Cascading Style Sheets (CSS) injection vulnerability in Swagger UI before 3.23.11 allows attackers to use the Relative Path Overwrite (RPO) technique to perform CSS-based input field value exfiltration, such as exfiltration of a CSRF token value. In other words, this product intentionally allows the embedding of untrusted JSON data from remote servers, but it was not previously known that <style>@import within the JSON data was a functional attack method. |
| CVE-2018-1324 | Medium | 2018-03-16 | No exploit published | No public exploit | A specially crafted ZIP archive can be used to cause an infinite loop inside of Apache Commons Compress' extra field parser used by the ZipFile and ZipArchiveInputStream classes in versions 1.11 to 1.15. This can be used to mount a denial of service attack against services that use Compress' zip package. |