
Oracle Critical Patch Update July 2021
Released July 2021 · Oracle's advisory ↗ · ← Critical Patch Update, April 2021 · Critical Patch Update, October 2021 →
231 CVEs in this release, one square each
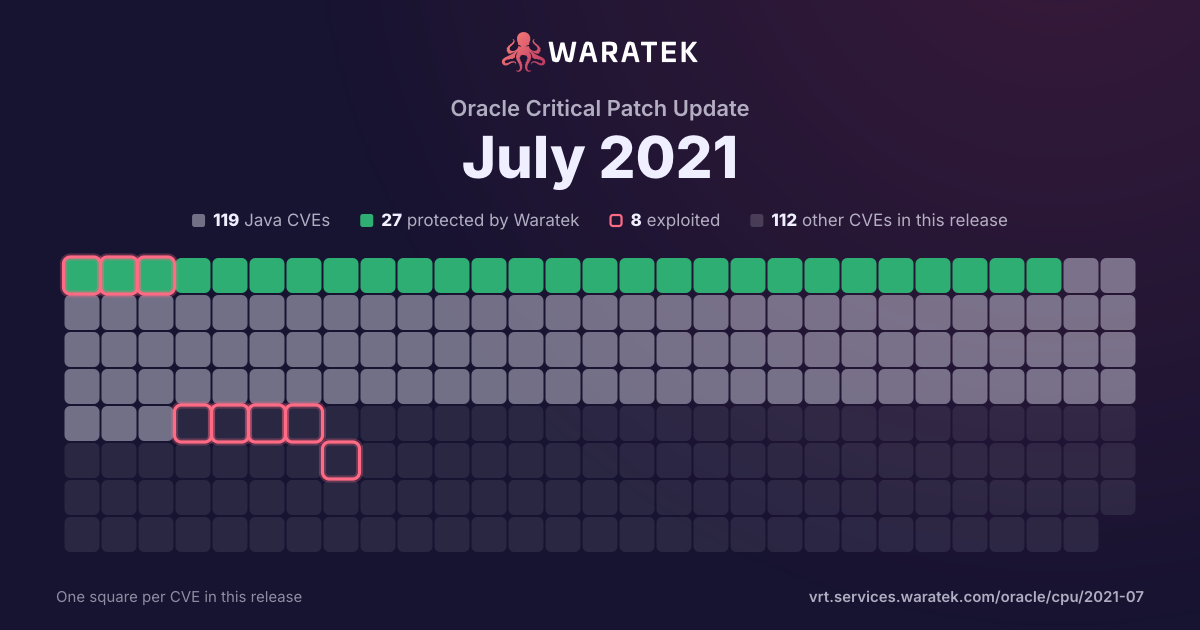
By status
27Protected by Waratek2Mitigation candidate90No exploit published33Outside Waratek scope79Not applicable
8Exploited, marked by the ring
No exploit published. For 70 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 118 matches · 26 protected · 3 exploited · 2 CISA KEV · 8 public PoC · 10 EPSS ≥ 0.5
Protected by Waratek
26
22.0%
Rule in development
0
0.0%
Mitigation candidate
2
1.7%
No exploit published
90
76.3%
blocked by ARMR today
26
22.0%
partly blocked
0
0.0%
not blocked
92
78.0%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 67 / quarter
Q2 171
No exploit published1
High1
not blocked1
No public exploit1
Q3 171
Protected by Waratek1
Medium1
blocked by ARMR today1
No public exploit1
Q4 171
No exploit published1
High1
not blocked1
No public exploit1
Q1 180
Q2 180
Q3 180
Q4 180
Q1 190
Q2 192
Protected by Waratek2
Critical2
blocked by ARMR today2
Exploited1
No public exploit1
Q3 192
Protected by Waratek1
No exploit published1
High2
blocked by ARMR today1
not blocked1
No public exploit2
Q4 192
Protected by Waratek1
No exploit published1
Medium2
blocked by ARMR today1
not blocked1
No public exploit2
Q1 204
Protected by Waratek2
No exploit published2
Critical2
High2
blocked by ARMR today2
not blocked2
Exploited1
No public exploit3
Q2 203
Protected by Waratek3
Critical1
High2
blocked by ARMR today3
Working exploit published1
No public exploit2
Q3 207
Protected by Waratek3
Mitigation candidate1
No exploit published3
Critical2
High3
Medium2
blocked by ARMR today3
not blocked4
Working exploit published1
No public exploit6
Q4 2013
Protected by Waratek5
No exploit published8
Critical1
High9
Medium2
Low1
blocked by ARMR today5
not blocked8
Exploited1
No public exploit12
Q1 2113
Protected by Waratek4
No exploit published9
Critical1
High5
Medium7
blocked by ARMR today4
not blocked9
Working exploit published1
No public exploit12
Q2 212
Protected by Waratek1
No exploit published1
Critical1
High1
blocked by ARMR today1
not blocked1
No public exploit2
Q3 2167
Protected by Waratek3
Mitigation candidate1
No exploit published63
Critical6
High31
Medium27
Low3
blocked by ARMR today3
not blocked64
Proof of concept only2
Forecast only2
No public exploit63
Q3 17Q1 18Q3 18Q1 19Q3 19Q1 20Q3 20Q1 21Q3 21
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2020-7017 | Medium | 2020-07-27 | No exploit published | No public exploit | In Kibana versions before 6.8.11 and 7.8.1 the region map visualization in contains a stored XSS flaw. An attacker who is able to edit or create a region map visualization could obtain sensitive information or perform destructive actions on behalf of Kibana users who view the region map visualization. |
| CVE-2020-13935 | High | 2020-07-14 | Mitigation candidate | Working exploit published | The payload length in a WebSocket frame was not correctly validated in Apache Tomcat 10.0.0-M1 to 10.0.0-M6, 9.0.0.M1 to 9.0.36, 8.5.0 to 8.5.56 and 7.0.27 to 7.0.104. Invalid payload lengths could trigger an infinite loop. Multiple requests with invalid payload lengths could lead to a denial of service. |
| CVE-2020-14195 | High | 2020-06-16 | Protected by Waratek | No public exploit | FasterXML jackson-databind 2.x before 2.9.10.5 mishandles the interaction between serialization gadgets and typing, related to org.jsecurity.realm.jndi.JndiRealmFactory (aka org.jsecurity). |
| CVE-2020-9484 | High | 2020-05-20 | Protected by Waratek | Working exploit published | When using Apache Tomcat versions 10.0.0-M1 to 10.0.0-M4, 9.0.0.M1 to 9.0.34, 8.5.0 to 8.5.54 and 7.0.0 to 7.0.103 if a) an attacker is able to control the contents and name of a file on the server; and b) the server is configured to use the PersistenceManager with a FileStore; and c) the PersistenceManager is configured with sessionAttributeValueClassNameFilter="null" (the default unless a SecurityManager is used) or a sufficiently lax filter to allow the attacker provided object to be deserialized; and d) the attacker knows the relative file path from the storage location used by FileStore to the file the attacker has control over; then, using a specifically crafted request, the attacker will be able to trigger remote code execution via deserialization of the file under their control. Note that all of conditions a) to d) must be true for the attack to succeed. |
| CVE-2020-10683 | Critical | 2020-05-01 | Protected by Waratek | No public exploit | dom4j before 2.0.3 and 2.1.x before 2.1.3 allows external DTDs and External Entities by default, which might enable XXE attacks. However, there is popular external documentation from OWASP showing how to enable the safe, non-default behavior in any application that uses dom4j. |
| CVE-2020-2604 | High | 2020-01-15 | Protected by Waratek | No public exploit | Vulnerability in the Java SE, Java SE Embedded product of Oracle Java SE (component: Serialization). Supported versions that are affected are Java SE: 7u241, 8u231, 11.0.5 and 13.0.1; Java SE Embedded: 8u231. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE, Java SE Embedded. Successful attacks of this vulnerability can result in takeover of Java SE, Java SE Embedded. Note: This vulnerability applies to Java deployments, typically in clients running sandboxed Java Web Start applications or sandboxed Java applets (in Java SE 8), that load and run untrusted code (e.g., code that comes from the internet) and rely on the Java sandbox for security. This vulnerability can also be exploited by using APIs in the specified Component, e.g., through a web service which supplies data to the APIs. CVSS v3.0 Base Score 8.1 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2020-2555 | Critical | 2020-01-15 | Protected by Waratek | Exploited | Vulnerability in the Oracle Coherence product of Oracle Fusion Middleware (component: Caching,CacheStore,Invocation). Supported versions that are affected are 3.7.1.0, 12.1.3.0.0, 12.2.1.3.0 and 12.2.1.4.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via T3 to compromise Oracle Coherence. Successful attacks of this vulnerability can result in takeover of Oracle Coherence. CVSS 3.0 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2019-12399 | High | 2020-01-14 | No exploit published | No public exploit | When Connect workers in Apache Kafka 2.0.0, 2.0.1, 2.1.0, 2.1.1, 2.2.0, 2.2.1, or 2.3.0 are configured with one or more config providers, and a connector is created/updated on that Connect cluster to use an externalized secret variable in a substring of a connector configuration property value, then any client can issue a request to the same Connect cluster to obtain the connector's task configuration and the response will contain the plaintext secret rather than the externalized secrets variables. |
| CVE-2019-0219 | Critical | 2020-01-14 | No exploit published | No public exploit | A website running in the InAppBrowser webview on Android could execute arbitrary JavaScript in the main application's webview using a specially crafted gap-iab: URI. |
| CVE-2019-12415 | Medium | 2019-10-23 | Protected by Waratek | No public exploit | In Apache POI up to 4.1.0, when using the tool XSSFExportToXml to convert user-provided Microsoft Excel documents, a specially crafted document can allow an attacker to read files from the local filesystem or from internal network resources via XML External Entity (XXE) Processing. |
| CVE-2019-2897 | Medium | 2019-10-16 | No exploit published | No public exploit | Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Fusion Middleware (component: Analytics Actions). Supported versions that are affected are 12.2.1.3.0 and 12.2.1.4.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Business Intelligence Enterprise Edition. While the vulnerability is in Oracle Business Intelligence Enterprise Edition, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Business Intelligence Enterprise Edition accessible data as well as unauthorized read access to a subset of Oracle Business Intelligence Enterprise Edition accessible data. CVSS 3.0 Base Score 6.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:L/I:L/A:N). |
| CVE-2019-12402 | High | 2019-08-30 | No exploit published | No public exploit | The file name encoding algorithm used internally in Apache Commons Compress 1.15 to 1.18 can get into an infinite loop when faced with specially crafted inputs. This can lead to a denial of service attack if an attacker can choose the file names inside of an archive created by Compress. |
| CVE-2019-10086 | High | 2019-08-20 | Protected by Waratek | No public exploit | In Apache Commons Beanutils 1.9.2, a special BeanIntrospector class was added which allows suppressing the ability for an attacker to access the classloader via the class property available on all Java objects. We, however were not using this by default characteristic of the PropertyUtilsBean. |
| CVE-2019-2729 | Critical | 2019-06-19 | Protected by Waratek | Exploited | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: Web Services). Supported versions that are affected are 10.3.6.0.0, 12.1.3.0.0 and 12.2.1.3.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebLogic Server. Successful attacks of this vulnerability can result in takeover of Oracle WebLogic Server. CVSS 3.0 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2019-0228 | Critical | 2019-04-17 | Protected by Waratek | No public exploit | Apache PDFBox 2.0.14 does not properly initialize the XML parser, which allows context-dependent attackers to conduct XML External Entity (XXE) attacks via a crafted XFDF. |
| CVE-2012-0881 | High | 2017-10-30 | No exploit published | No public exploit | Apache Xerces2 Java Parser before 2.12.0 allows remote attackers to cause a denial of service (CPU consumption) via a crafted message to an XML service, which triggers hash table collisions. |
| CVE-2017-14735 | Medium | 2017-09-25 | Protected by Waratek | No public exploit | OWASP AntiSamy before 1.5.7 allows XSS via HTML5 entities, as demonstrated by use of : to construct a javascript: URL. |
| CVE-2017-9735 | High | 2017-06-16 | No exploit published | No public exploit | Jetty through 9.4.x is prone to a timing channel in util/security/Password.java, which makes it easier for remote attackers to obtain access by observing elapsed times before rejection of incorrect passwords. |