
Oracle Critical Patch Update April 2021
Released April 2021 · Oracle's advisory ↗ · ← Critical Patch Update, January 2021 · Critical Patch Update, July 2021 →
258 CVEs in this release, one square each
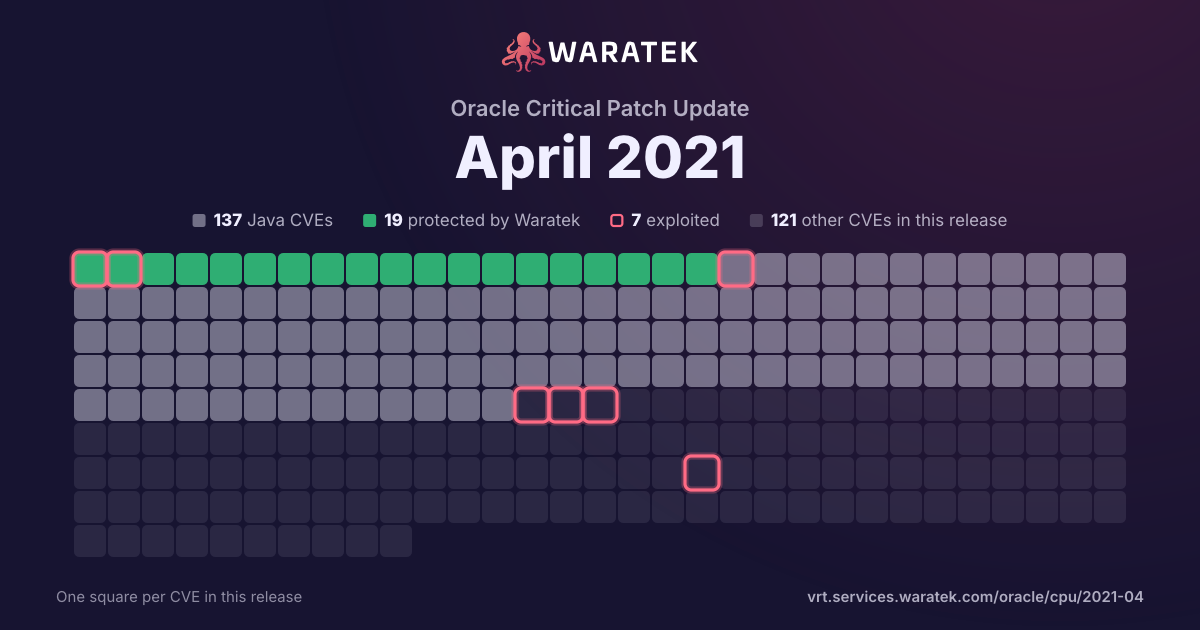
By status
19Protected by Waratek3Mitigation candidate115No exploit published67Outside Waratek scope54Not applicable
7Exploited, marked by the ring
No exploit published. For 97 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 2 matches · 1 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
1
50.0%
Outside Waratek scope
1
50.0%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
2
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
2
100.0%
No public exploit
0
0.0%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2020-27223 | Medium | 2021-02-26 | No exploit published | Forecast only | In Eclipse Jetty 9.4.6.v20170531 to 9.4.36.v20210114 (inclusive), 10.0.0, and 11.0.0 when Jetty handles a request containing multiple Accept headers with a large number of “quality” (i.e. q) parameters, the server may enter a denial of service (DoS) state due to high CPU usage processing those quality values, resulting in minutes of CPU time exhausted processing those quality values. |
| CVE-2020-1927 | Medium | 2020-04-02 | Outside Waratek scope | Forecast only | In Apache HTTP Server 2.4.0 to 2.4.41, redirects configured with mod_rewrite that were intended to be self-referential might be fooled by encoded newlines and redirect instead to an an unexpected URL within the request URL. |