
WaratekVRT Sign in

Oracle Critical Patch Update April 2021

Released April 2021 · Oracle's advisory ↗ · ← Critical Patch Update, January 2021 · Critical Patch Update, July 2021 →

258 CVEs in this release, one square each
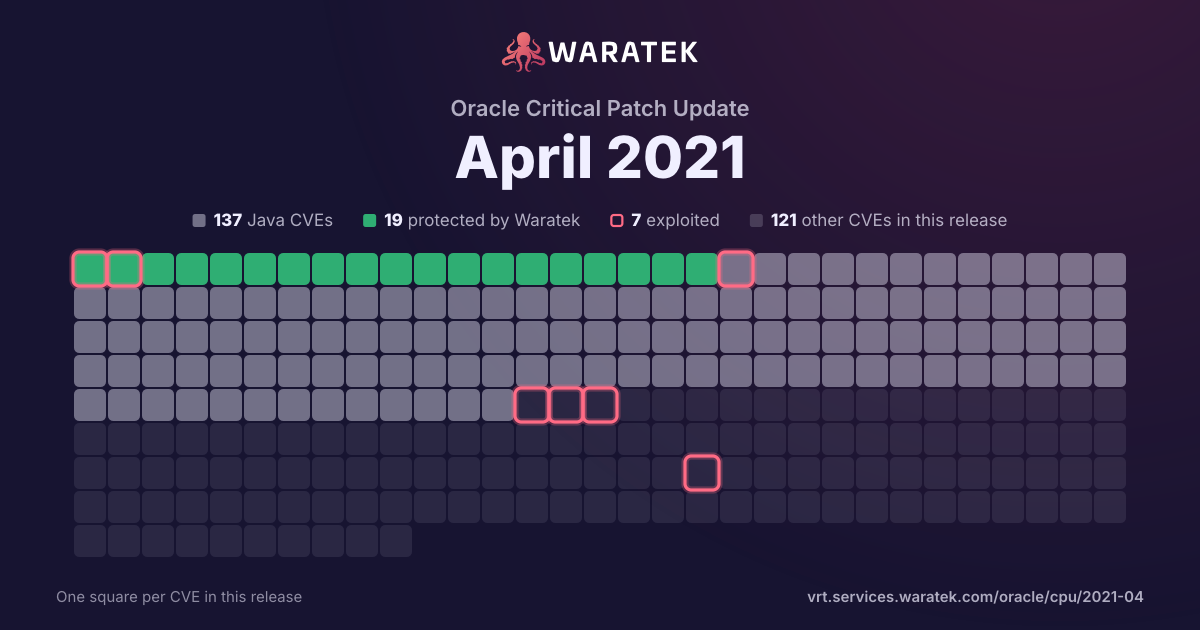
Protected by Waratek, exploitedProtected by Waratek, exploitedProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekMitigation candidate, exploitedMitigation candidateMitigation candidateNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedOutside Waratek scope, exploitedOutside Waratek scope, exploitedOutside Waratek scope, exploitedOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeNot applicable, exploitedNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicable
Share this chart Oracle Critical Patch Update April 2021, one square per CVE: 137 Java CVEs, 19 protected by Waratek, 7 exploited, 121 other CVEs in this release.

Download the image

By status

No exploit published. For 97 of them, Oracle's security advisory is the source of public detail.

Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.

Reset
More filters (1)
Columns
Including CVEs outside Waratek scope✕EPSS ≥ 0.5✕
Overview 7 matches · 2 in Waratek scope · 0 protected · 3 exploited · 1 CISA KEV · 5 public PoC
Protected by Waratek 0 0.0% Rule in development 0 0.0% Mitigation candidate 1 14.3% No exploit published 1 14.3% Outside Waratek scope 5 71.4% Not applicable 0 0.0% Withdrawn CVE 0 0.0%
Critical 0 0.0% High 0 0.0% Medium 7 100.0% Low 0 0.0% None 0 0.0% Unknown 0 0.0%
blocked by ARMR today 0 0.0% partly blocked 0 0.0% not blocked 7 100.0% not established 0 0.0% unrecorded 0 0.0%
split by peak 3 / quarter
Q2 19Q3 19Q4 19Q1 20Q2 20Q3 20Q4 20Q1 21
7 matches Sign in to download these CVEs as CSV or JSON, or to follow them in a feed.
CVE Severity Published▾ Status Exploitation Description
CVE-2021-3449 Medium 2021-03-25 Outside Waratek scope Proof of concept only An OpenSSL TLS server may crash if sent a maliciously crafted renegotiation ClientHello message from a client. If a TLSv1.2 renegotiation ClientHello omits the signature_algorithms extension (where it was present in the initial ClientHello), but includes a signature_algorithms_cert extension then a NULL pointer dereference will result, leading to a crash and a denial of service attack. A server is only vulnerable if it has TLSv1.2 and renegotiation enabled (which is the default configuration). OpenSSL TLS clients are not impacted by this issue. All OpenSSL 1.1.1 versions are affected by this issue. Users of these versions should upgrade to OpenSSL 1.1.1k. OpenSSL 1.0.2 is not impacted by this issue. Fixed in OpenSSL 1.1.1k (Affected 1.1.1-1.1.1j).
CVE-2020-27223 Medium 2021-02-26 No exploit published Forecast only In Eclipse Jetty 9.4.6.v20170531 to 9.4.36.v20210114 (inclusive), 10.0.0, and 11.0.0 when Jetty handles a request containing multiple Accept headers with a large number of “quality” (i.e. q) parameters, the server may enter a denial of service (DoS) state due to high CPU usage processing those quality values, resulting in minutes of CPU time exhausted processing those quality values.
CVE-2020-11023 Medium 2020-04-29 Outside Waratek scope Exploited In jQuery versions greater than or equal to 1.0.3 and before 3.5.0, passing HTML containing <option> elements from untrusted sources - even after sanitizing it - to one of jQuery's DOM manipulation methods (i.e. .html(), .append(), and others) may execute untrusted code. This problem is patched in jQuery 3.5.0.
CVE-2020-11022 Medium 2020-04-29 Outside Waratek scope Exploited In jQuery starting with 1.12.0 and before 3.5.0, passing HTML from untrusted sources - even after sanitizing it - to one of jQuery's DOM manipulation methods (i.e. .html(), .append(), and others) may execute untrusted code. This problem is patched in jQuery 3.5.0.
CVE-2020-1927 Medium 2020-04-02 Outside Waratek scope Forecast only In Apache HTTP Server 2.4.0 to 2.4.41, redirects configured with mod_rewrite that were intended to be self-referential might be fooled by encoded newlines and redirect instead to an an unexpected URL within the request URL.
CVE-2019-0221 Medium 2019-05-28 Mitigation candidate Working exploit published The SSI printenv command in Apache Tomcat 9.0.0.M1 to 9.0.0.17, 8.5.0 to 8.5.39 and 7.0.0 to 7.0.93 echoes user provided data without escaping and is, therefore, vulnerable to XSS. SSI is disabled by default. The printenv command is intended for debugging and is unlikely to be present in a production website.
CVE-2019-11358 Medium 2019-04-20 Outside Waratek scope Exploited jQuery before 3.4.0, as used in Drupal, Backdrop CMS, and other products, mishandles jQuery.extend(true, {}, ...) because of Object.prototype pollution. If an unsanitized source object contained an enumerable __proto__ property, it could extend the native Object.prototype.