
Oracle Critical Patch Update January 2021
Released January 2021 · Oracle's advisory ↗ · ← Critical Patch Update, October 2020 · Critical Patch Update, April 2021 →
202 CVEs in this release, one square each
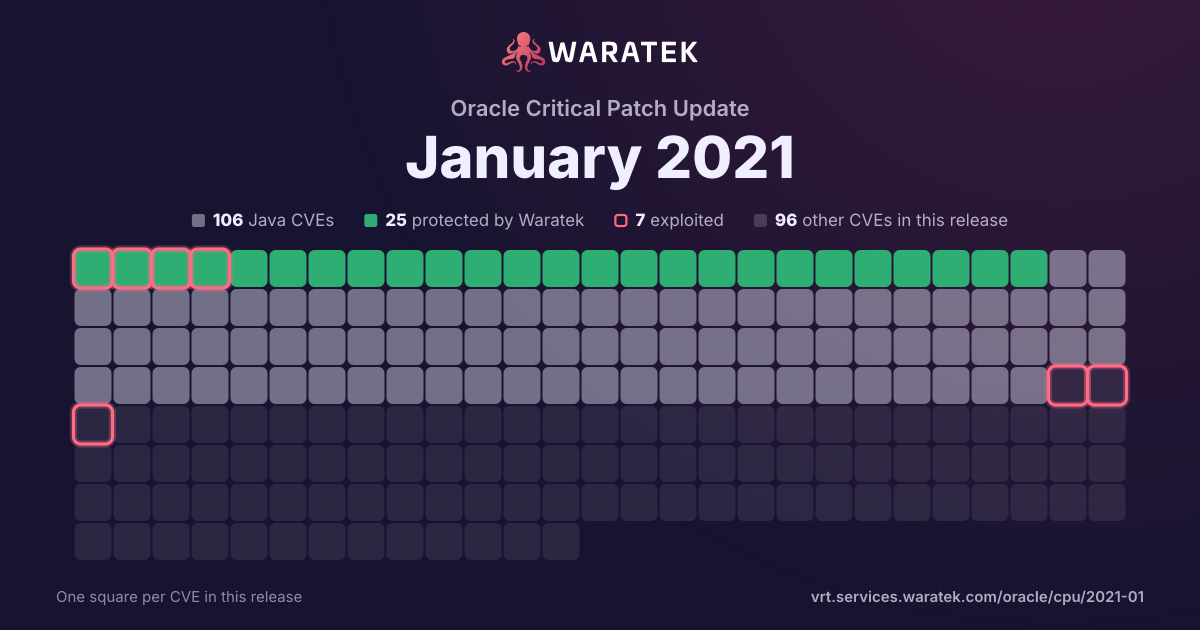
By status
25Protected by Waratek3Mitigation candidate78No exploit published59Outside Waratek scope37Not applicable
7Exploited, marked by the ring
No exploit published. For 66 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 17 matches · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
17matches
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
17
100.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
blocked by ARMR today
17
100.0%
partly blocked
0
0.0%
not blocked
0
0.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
17
100.0%
split by
peak 3 / quarter
Q4 161
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Q1 170
Q2 170
Q3 170
Q4 170
Q1 180
Q2 182
Protected by Waratek2
Medium2
blocked by ARMR today2
No public exploit2
Q3 180
Q4 180
Q1 191
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Q2 190
Q3 191
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Q4 193
Protected by Waratek3
High1
Medium2
blocked by ARMR today3
No public exploit3
Q1 200
Q2 203
Protected by Waratek3
Critical2
High1
blocked by ARMR today3
No public exploit3
Q3 203
Protected by Waratek3
Critical2
High1
blocked by ARMR today3
No public exploit3
Q4 203
Protected by Waratek3
High1
Medium2
blocked by ARMR today3
No public exploit3
Q4 16Q2 17Q4 17Q2 18Q4 18Q2 19Q4 19Q2 20Q4 20
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2020-17521 | Medium | 2020-12-07 | Protected by Waratek | No public exploit | Apache Groovy provides extension methods to aid with creating temporary directories. Prior to this fix, Groovy's implementation of those extension methods was using a now superseded Java JDK method call that is potentially not secure on some operating systems in some contexts. Users not using the extension methods mentioned in the advisory are not affected, but may wish to read the advisory for further details. Versions Affected: 2.0 to 2.4.20, 2.5.0 to 2.5.13, 3.0.0 to 3.0.6, and 4.0.0-alpha-1. Fixed in versions 2.4.21, 2.5.14, 3.0.7, 4.0.0-alpha-2. |
| CVE-2019-17566 | High | 2020-11-12 | Protected by Waratek | No public exploit | Apache Batik is vulnerable to server-side request forgery, caused by improper input validation by the "xlink:href" attributes. By using a specially-crafted argument, an attacker could exploit this vulnerability to cause the underlying server to make arbitrary GET requests. |
| CVE-2020-14803 | Medium | 2020-10-21 | Protected by Waratek | No public exploit | Vulnerability in the Java SE product of Oracle Java SE (component: Libraries). Supported versions that are affected are Java SE: 11.0.8 and 15. Easily exploitable vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Java SE accessible data. Note: This vulnerability applies to Java deployments, typically in clients running sandboxed Java Web Start applications or sandboxed Java applets, that load and run untrusted code (e.g., code that comes from the internet) and rely on the Java sandbox for security. This vulnerability does not apply to Java deployments, typically in servers, that load and run only trusted code (e.g., code installed by an administrator). CVSS 3.1 Base Score 5.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2020-24750 | High | 2020-09-17 | Protected by Waratek | No public exploit | FasterXML jackson-databind 2.x before 2.9.10.6 mishandles the interaction between serialization gadgets and typing, related to com.pastdev.httpcomponents.configuration.JndiConfiguration. |
| CVE-2020-11998 | Critical | 2020-09-10 | Protected by Waratek | No public exploit | A regression has been introduced in the commit preventing JMX re-bind. By passing an empty environment map to RMIConnectorServer, instead of the map that contains the authentication credentials, it leaves ActiveMQ open to the following attack: https://docs.oracle.com/javase/8/docs/technotes/guides/management/agent.html "A remote client could create a javax.management.loading.MLet MBean and use it to create new MBeans from arbitrary URLs, at least if there is no security manager. In other words, a rogue remote client could make your Java application execute arbitrary code." Mitigation: Upgrade to Apache ActiveMQ 5.15.13 |
| CVE-2020-25020 | Critical | 2020-08-29 | Protected by Waratek | No public exploit | MPXJ through 8.1.3 allows XXE attacks. This affects the GanttProjectReader and PhoenixReader components. |
| CVE-2020-14195 | High | 2020-06-16 | Protected by Waratek | No public exploit | FasterXML jackson-databind 2.x before 2.9.10.5 mishandles the interaction between serialization gadgets and typing, related to org.jsecurity.realm.jndi.JndiRealmFactory (aka org.jsecurity). |
| CVE-2020-11973 | Critical | 2020-05-14 | Protected by Waratek | No public exploit | Apache Camel Netty enables Java deserialization by default. Apache Camel 2.22.x, 2.23.x, 2.24.x, 2.25.0, 3.0.0 up to 3.1.0 are affected. 2.x users should upgrade to 2.25.1, 3.x users should upgrade to 3.2.0. |
| CVE-2020-10683 | Critical | 2020-05-01 | Protected by Waratek | No public exploit | dom4j before 2.0.3 and 2.1.x before 2.1.3 allows external DTDs and External Entities by default, which might enable XXE attacks. However, there is popular external documentation from OWASP showing how to enable the safe, non-default behavior in any application that uses dom4j. |
| CVE-2019-17563 | High | 2019-12-23 | Protected by Waratek | No public exploit | When using FORM authentication with Apache Tomcat 9.0.0.M1 to 9.0.29, 8.5.0 to 8.5.49 and 7.0.0 to 7.0.98 there was a narrow window where an attacker could perform a session fixation attack. The window was considered too narrow for an exploit to be practical but, erring on the side of caution, this issue has been treated as a security vulnerability. |
| CVE-2019-12415 | Medium | 2019-10-23 | Protected by Waratek | No public exploit | In Apache POI up to 4.1.0, when using the tool XSSFExportToXml to convert user-provided Microsoft Excel documents, a specially crafted document can allow an attacker to read files from the local filesystem or from internal network resources via XML External Entity (XXE) Processing. |
| CVE-2019-17091 | Medium | 2019-10-02 | Protected by Waratek | No public exploit | faces/context/PartialViewContextImpl.java in Eclipse Mojarra, as used in Mojarra for Eclipse EE4J before 2.3.10 and Mojarra JavaServer Faces before 2.2.20, allows Reflected XSS because a client window field is mishandled. |
| CVE-2019-10086 | High | 2019-08-20 | Protected by Waratek | No public exploit | In Apache Commons Beanutils 1.9.2, a special BeanIntrospector class was added which allows suppressing the ability for an attacker to access the classloader via the class property available on all Java objects. We, however were not using this by default characteristic of the PropertyUtilsBean. |
| CVE-2019-3773 | Critical | 2019-01-18 | Protected by Waratek | No public exploit | Spring Web Services, versions 2.4.3, 3.0.4, and older unsupported versions of all three projects, were susceptible to XML External Entity Injection (XXE) when receiving XML data from untrusted sources. |
| CVE-2018-10237 | Medium | 2018-04-26 | Protected by Waratek | No public exploit | Unbounded memory allocation in Google Guava 11.0 through 24.x before 24.1.1 allows remote attackers to conduct denial of service attacks against servers that depend on this library and deserialize attacker-provided data, because the AtomicDoubleArray class (when serialized with Java serialization) and the CompoundOrdering class (when serialized with GWT serialization) perform eager allocation without appropriate checks on what a client has sent and whether the data size is reasonable. |
| CVE-2018-2587 | Medium | 2018-04-19 | Protected by Waratek | No public exploit | Vulnerability in the Oracle Access Manager component of Oracle Fusion Middleware (subcomponent: Web Server Plugin). Supported versions that are affected are 10.1.4.3.0, 11.1.2.3.0 and 12.2.1.3.0. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Access Manager. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Access Manager accessible data as well as unauthorized read access to a subset of Oracle Access Manager accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:U/C:L/I:H/A:N). |
| CVE-2016-1000031 | Critical | 2016-10-25 | Protected by Waratek | No public exploit | Apache Commons FileUpload before 1.3.3 DiskFileItem File Manipulation Remote Code Execution |