
Oracle Critical Patch Update April 2020
Released April 2020 · Oracle's advisory ↗ · ← Critical Patch Update, January 2020 · Critical Patch Update, July 2020 →
300 CVEs in this release, one square each
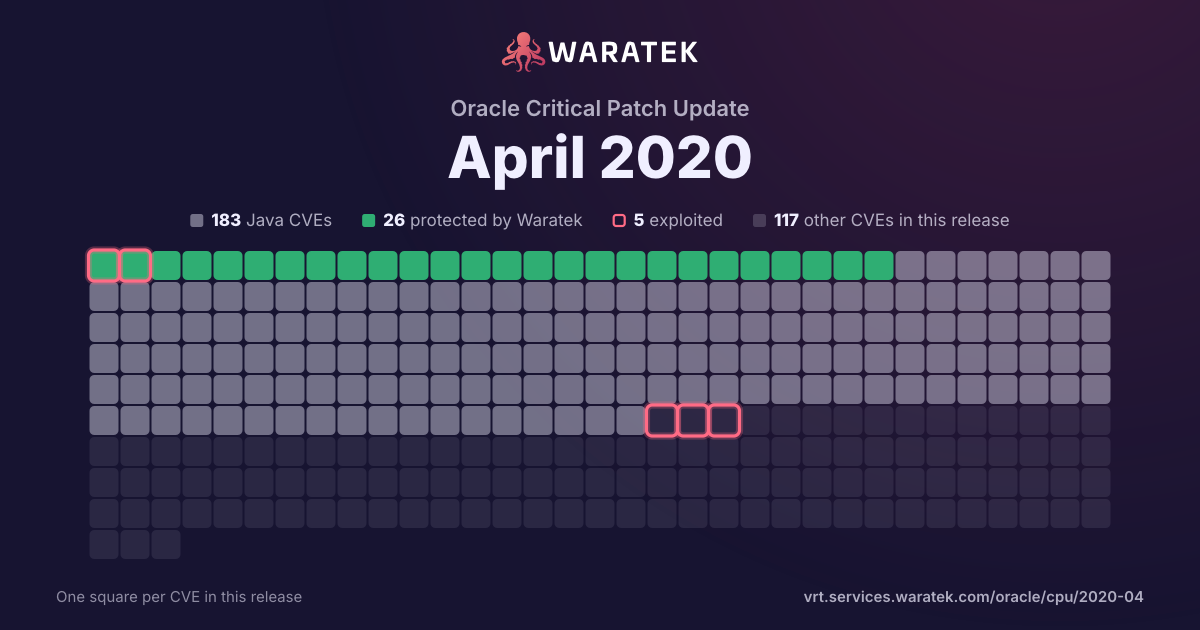
By status
28Protected by Waratek7Mitigation candidate166No exploit published6Outside Waratek scope92Not applicable1Withdrawn CVE
5Exploited, marked by the ring
No exploit published. For 145 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 4 matches · 2 in Waratek scope · 2 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
4matches
2in Waratek scope50.0%
2protected50.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC25.0%
1EPSS ≥ 0.525.0%
Protected by Waratek
2
50.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
2
50.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
2
50.0%
partly blocked
0
0.0%
not blocked
2
50.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
1
25.0%
Forecast only
0
0.0%
No public exploit
3
75.0%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-17563 | High | 2019-12-23 | Protected by Waratek | No public exploit | When using FORM authentication with Apache Tomcat 9.0.0.M1 to 9.0.29, 8.5.0 to 8.5.49 and 7.0.0 to 7.0.98 there was a narrow window where an attacker could perform a session fixation attack. The window was considered too narrow for an exploit to be practical but, erring on the side of caution, this issue has been treated as a security vulnerability. |
| CVE-2019-17571 | Critical | 2019-12-20 | Protected by Waratek | Proof of concept only | Included in Log4j 1.2 is a SocketServer class that is vulnerable to deserialization of untrusted data which can be exploited to remotely execute arbitrary code when combined with a deserialization gadget when listening to untrusted network traffic for log data. This affects Log4j versions up to 1.2 up to 1.2.17. |
| CVE-2019-14889 | High | 2019-12-10 | Not applicable | No public exploit | A flaw was found with the libssh API function ssh_scp_new() in versions before 0.9.3 and before 0.8.8. When the libssh SCP client connects to a server, the scp command, which includes a user-provided path, is executed on the server-side. In case the library is used in a way where users can influence the third parameter of the function, it would become possible for an attacker to inject arbitrary commands, leading to a compromise of the remote target. |
| CVE-2019-19646 | Critical | 2019-12-09 | Not applicable | No public exploit | pragma.c in SQLite through 3.30.1 mishandles NOT NULL in an integrity_check PRAGMA command in certain cases of generated columns. |