
Oracle Critical Patch Update April 2020
Released April 2020 · Oracle's advisory ↗ · ← Critical Patch Update, January 2020 · Critical Patch Update, July 2020 →
300 CVEs in this release, one square each
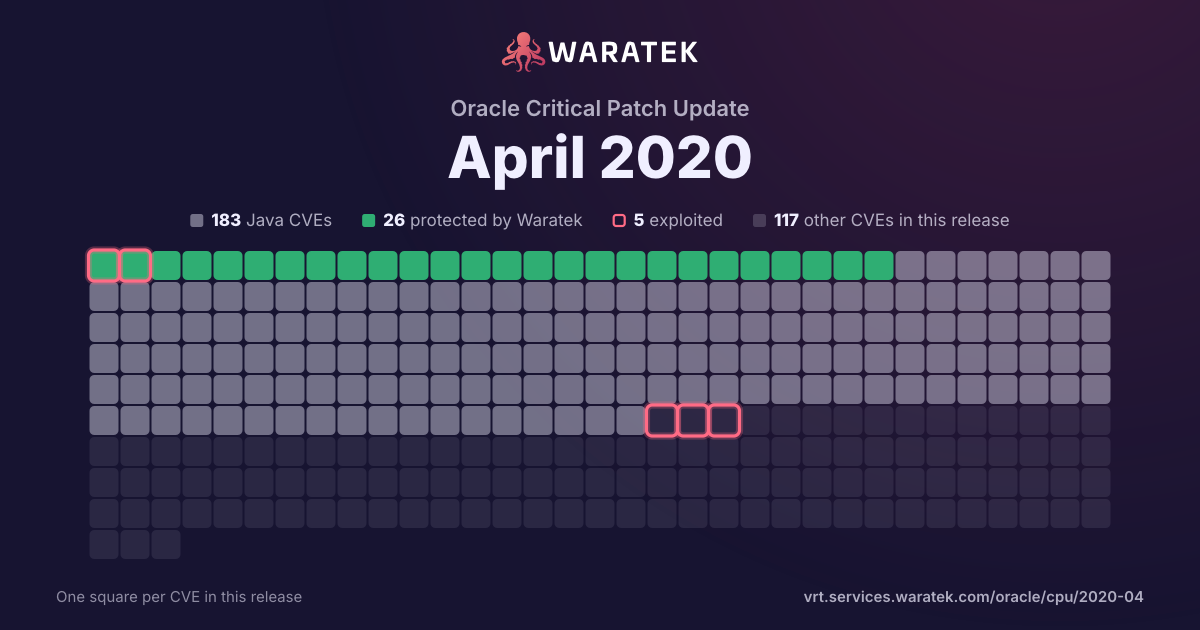
By status
26Protected by Waratek1Mitigation candidate156No exploit published60Outside Waratek scope56Not applicable1Withdrawn CVE
5Exploited, marked by the ring
No exploit published. For 141 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 108 matches · 53 in Waratek scope · 7 protected · 2 exploited · 0 CISA KEV · 2 public PoC · 2 EPSS ≥ 0.5
108matches
53in Waratek scope49.1%
7protected6.5%
2exploited1.9%
0CISA KEV0.0%
2public PoC1.9%
2EPSS ≥ 0.51.9%
Protected by Waratek
7
6.5%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
46
42.6%
Outside Waratek scope
38
35.2%
Not applicable
17
15.7%
Withdrawn CVE
0
0.0%
blocked by ARMR today
7
6.5%
partly blocked
0
0.0%
not blocked
101
93.5%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
2
1.9%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
1
0.9%
No public exploit
105
97.2%
split by
peak 92 / quarter
Q4 151
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Q1 160
Q2 160
Q3 160
Q4 160
Q1 171
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Q2 170
Q3 171
Protected by Waratek1
Medium1
blocked by ARMR today1
No public exploit1
Q4 170
Q1 182
Outside Waratek scope1
Not applicable1
Medium2
not blocked2
Exploited1
Forecast only1
Q2 181
Protected by Waratek1
Medium1
blocked by ARMR today1
No public exploit1
Q3 180
Q4 183
No exploit published2
Not applicable1
Medium3
not blocked3
No public exploit3
Q1 190
Q2 192
No exploit published1
Outside Waratek scope1
Medium2
not blocked2
Exploited1
No public exploit1
Q3 193
Not applicable3
Medium3
not blocked3
No public exploit3
Q4 192
Protected by Waratek2
Medium2
blocked by ARMR today2
No public exploit2
Q1 200
Q2 2092
Protected by Waratek3
No exploit published43
Outside Waratek scope34
Not applicable12
Medium92
blocked by ARMR today3
not blocked89
No public exploit92
Q4 15Q2 16Q4 16Q2 17Q4 17Q2 18Q4 18Q2 19Q4 19Q2 20
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2018-17197 | Medium | 2018-12-24 | No exploit published | No public exploit | A carefully crafted or corrupt sqlite file can cause an infinite loop in Apache Tika's SQLite3Parser in versions 1.8-1.19.1 of Apache Tika. |
| CVE-2018-11797 | Medium | 2018-10-05 | No exploit published | No public exploit | In Apache PDFBox 1.8.0 to 1.8.15 and 2.0.0RC1 to 2.0.11, a carefully crafted PDF file can trigger an extremely long running computation when parsing the page tree. |
| CVE-2018-10237 | Medium | 2018-04-26 | Protected by Waratek | No public exploit | Unbounded memory allocation in Google Guava 11.0 through 24.x before 24.1.1 allows remote attackers to conduct denial of service attacks against servers that depend on this library and deserialize attacker-provided data, because the AtomicDoubleArray class (when serialized with Java serialization) and the CompoundOrdering class (when serialized with GWT serialization) perform eager allocation without appropriate checks on what a client has sent and whether the data size is reasonable. |
| CVE-2015-9251 | Medium | 2018-01-18 | Outside Waratek scope | Exploited | jQuery before 3.0.0 is vulnerable to Cross-site Scripting (XSS) attacks when a cross-domain Ajax request is performed without the dataType option, causing text/javascript responses to be executed. |
| CVE-2018-5712 | Medium | 2018-01-16 | Not applicable | Forecast only | An issue was discovered in PHP before 5.6.33, 7.0.x before 7.0.27, 7.1.x before 7.1.13, and 7.2.x before 7.2.1. There is Reflected XSS on the PHAR 404 error page via the URI of a request for a .phar file. |
| CVE-2017-14735 | Medium | 2017-09-25 | Protected by Waratek | No public exploit | OWASP AntiSamy before 1.5.7 allows XSS via HTML5 entities, as demonstrated by use of : to construct a javascript: URL. |
| CVE-2016-7103 | Medium | 2017-03-15 | Outside Waratek scope | No public exploit | Cross-site scripting (XSS) vulnerability in jQuery UI before 1.12.0 might allow remote attackers to inject arbitrary web script or HTML via the closeText parameter of the dialog function. |
| CVE-2015-7940 | Medium | 2015-11-09 | Outside Waratek scope | No public exploit | The Bouncy Castle Java library before 1.51 does not validate a point is withing the elliptic curve, which makes it easier for remote attackers to obtain private keys via a series of crafted elliptic curve Diffie Hellman (ECDH) key exchanges, aka an "invalid curve attack." |