
Oracle Critical Patch Update January 2020
Released January 2020 · Oracle's advisory ↗ · ← Critical Patch Update, October 2019 · Critical Patch Update, April 2020 →
255 CVEs in this release, one square each
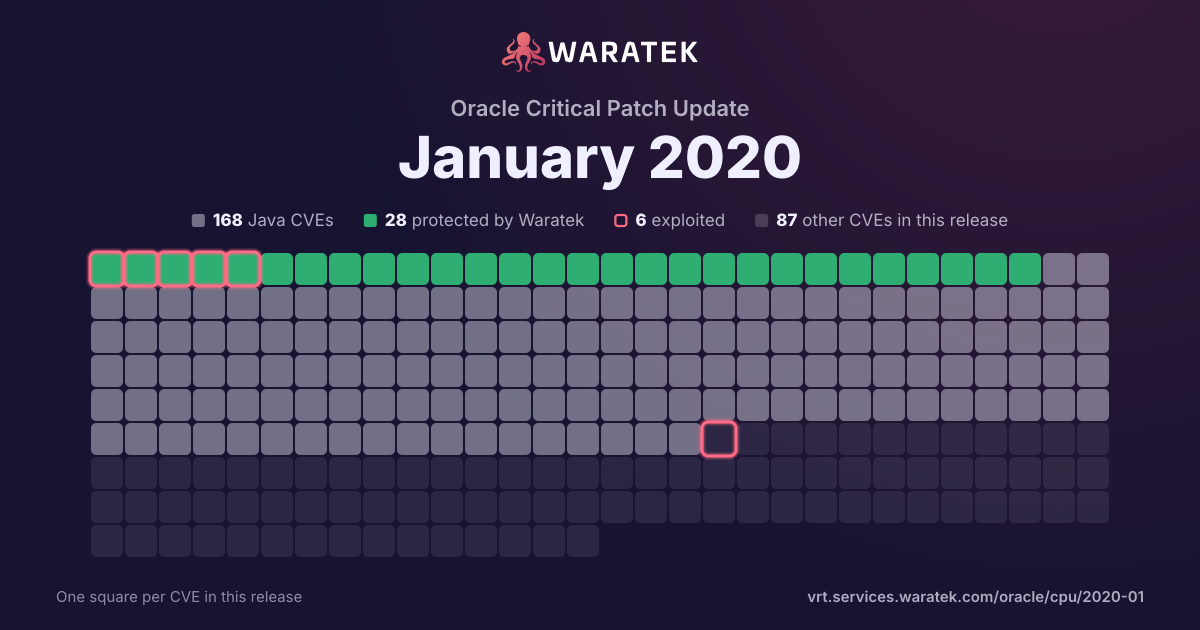
By status
28Protected by Waratek140No exploit published35Outside Waratek scope52Not applicable
6Exploited, marked by the ring
No exploit published. For 132 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 3 matches · 1 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
Protected by Waratek
1
33.3%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
2
66.7%
blocked by ARMR today
1
33.3%
partly blocked
0
0.0%
not blocked
2
66.7%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
3
100.0%
split by
peak 1 / quarter
Q3 16Q4 16Q1 17Q2 17Q3 17Q4 17Q1 18Q2 18
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2018-1258 | High | 2018-05-11 | No exploit published | No public exploit | Spring Framework version 5.0.5 when used in combination with any versions of Spring Security contains an authorization bypass when using method security. An unauthorized malicious user can gain unauthorized access to methods that should be restricted. |
| CVE-2017-12626 | High | 2018-01-29 | No exploit published | No public exploit | Apache POI in versions prior to release 3.17 are vulnerable to Denial of Service Attacks: 1) Infinite Loops while parsing crafted WMF, EMF, MSG and macros (POI bugs 61338 and 61294), and 2) Out of Memory Exceptions while parsing crafted DOC, PPT and XLS (POI bugs 52372 and 61295). |
| CVE-2016-1181 | High | 2016-07-04 | Protected by Waratek | No public exploit | ActionServlet.java in Apache Struts 1 1.x through 1.3.10 mishandles multithreaded access to an ActionForm instance, which allows remote attackers to execute arbitrary code or cause a denial of service (unexpected memory access) via a multipart request, a related issue to CVE-2015-0899. |