
Oracle Critical Patch Update October 2019
Released October 2019 · Oracle's advisory ↗ · ← Critical Patch Update, July 2019 · Critical Patch Update, January 2020 →
180 CVEs in this release, one square each
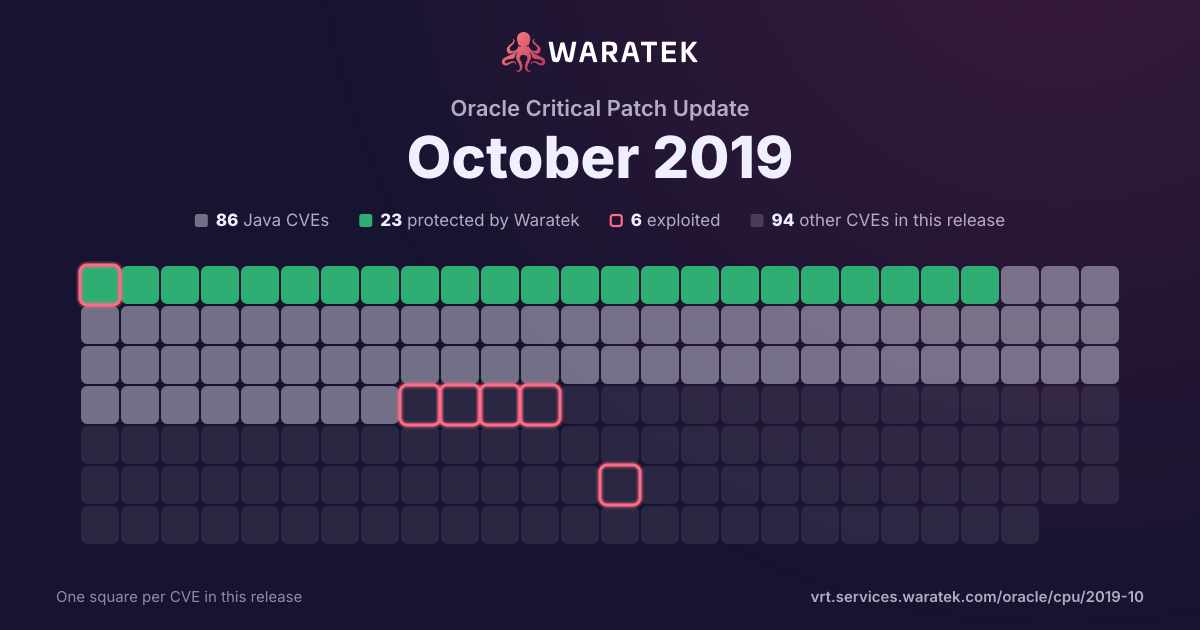
By status
24Protected by Waratek5Mitigation candidate65No exploit published17Outside Waratek scope69Not applicable
6Exploited, marked by the ring
No exploit published. For 56 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 10 matches · 0 protected · 2 exploited · 0 CISA KEV · 3 public PoC · 2 EPSS ≥ 0.5
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
3
30.0%
No exploit published
7
70.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
10
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
2
20.0%
Working exploit published
1
10.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
7
70.0%
split by
peak 4 / quarter
Q1 182
Mitigation candidate1
No exploit published1
High1
Medium1
not blocked2
Exploited1
No public exploit1
Q2 180
Q3 180
Q4 181
No exploit published1
High1
not blocked1
No public exploit1
Q1 190
Q2 193
Mitigation candidate2
No exploit published1
High1
Medium2
not blocked3
Exploited1
Working exploit published1
No public exploit1
Q3 190
Q4 194
No exploit published4
Critical1
Medium3
not blocked4
No public exploit4
Q1 18Q2 18Q3 18Q4 18Q1 19Q2 19Q3 19Q4 19
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-3019 | Medium | 2019-10-16 | No exploit published | No public exploit | Vulnerability in the Oracle Banking Digital Experience product of Oracle Financial Services Applications (component: Loan Calculator). Supported versions that are affected are 18.1, 18.2, 18.3 and 19.1. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Banking Digital Experience. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Banking Digital Experience, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Banking Digital Experience accessible data as well as unauthorized read access to a subset of Oracle Banking Digital Experience accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2019-2980 | Medium | 2019-10-16 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Direct Banking product of Oracle Financial Services Applications (component: eMail). Supported versions that are affected are 12.0.2 and 12.0.3. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Direct Banking. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle FLEXCUBE Direct Banking accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2019-2979 | Medium | 2019-10-16 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Direct Banking product of Oracle Financial Services Applications (component: Payments). Supported versions that are affected are 12.0.2 and 12.0.3. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Direct Banking. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle FLEXCUBE Direct Banking accessible data. CVSS 3.0 Base Score 5.7 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:U/C:N/I:H/A:N). |
| CVE-2019-2904 | Critical | 2019-10-16 | No exploit published | No public exploit | Vulnerability in the Oracle JDeveloper and ADF product of Oracle Fusion Middleware (component: ADF Faces). Supported versions that are affected are 11.1.1.9.0, 12.1.3.0.0 and 12.2.1.3.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle JDeveloper and ADF. Successful attacks of this vulnerability can result in takeover of Oracle JDeveloper and ADF. CVSS 3.0 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2019-0227 | High | 2019-05-01 | Mitigation candidate | Working exploit published | A Server Side Request Forgery (SSRF) vulnerability affected the Apache Axis 1.4 distribution that was last released in 2006. Security and bug commits commits continue in the projects Axis 1.x Subversion repository, legacy users are encouraged to build from source. The successor to Axis 1.x is Axis2, the latest version is 1.7.9 and is not vulnerable to this issue. |
| CVE-2019-10247 | Medium | 2019-04-22 | No exploit published | No public exploit | In Eclipse Jetty version 7.x, 8.x, 9.2.27 and older, 9.3.26 and older, and 9.4.16 and older, the server running on any OS and Jetty version combination will reveal the configured fully qualified directory base resource location on the output of the 404 error for not finding a Context that matches the requested path. The default server behavior on jetty-distribution and jetty-home will include at the end of the Handler tree a DefaultHandler, which is responsible for reporting this 404 error, it presents the various configured contexts as HTML for users to click through to. This produced HTML includes output that contains the configured fully qualified directory base resource location for each context. |
| CVE-2019-11358 | Medium | 2019-04-20 | Mitigation candidate | Exploited | jQuery before 3.4.0, as used in Drupal, Backdrop CMS, and other products, mishandles jQuery.extend(true, {}, ...) because of Object.prototype pollution. If an unsanitized source object contained an enumerable __proto__ property, it could extend the native Object.prototype. |
| CVE-2018-15756 | High | 2018-10-18 | No exploit published | No public exploit | Spring Framework, version 5.1, versions 5.0.x prior to 5.0.10, versions 4.3.x prior to 4.3.20, and older unsupported versions on the 4.2.x branch provide support for range requests when serving static resources through the ResourceHttpRequestHandler, or starting in 5.0 when an annotated controller returns an org.springframework.core.io.Resource. A malicious user (or attacker) can add a range header with a high number of ranges, or with wide ranges that overlap, or both, for a denial of service attack. This vulnerability affects applications that depend on either spring-webmvc or spring-webflux. Such applications must also have a registration for serving static resources (e.g. JS, CSS, images, and others), or have an annotated controller that returns an org.springframework.core.io.Resource. Spring Boot applications that depend on spring-boot-starter-web or spring-boot-starter-webflux are ready to serve static resources out of the box and are therefore vulnerable. |
| CVE-2017-12626 | High | 2018-01-29 | No exploit published | No public exploit | Apache POI in versions prior to release 3.17 are vulnerable to Denial of Service Attacks: 1) Infinite Loops while parsing crafted WMF, EMF, MSG and macros (POI bugs 61338 and 61294), and 2) Out of Memory Exceptions while parsing crafted DOC, PPT and XLS (POI bugs 52372 and 61295). |
| CVE-2015-9251 | Medium | 2018-01-18 | Mitigation candidate | Exploited | jQuery before 3.0.0 is vulnerable to Cross-site Scripting (XSS) attacks when a cross-domain Ajax request is performed without the dataType option, causing text/javascript responses to be executed. |