
Oracle Critical Patch Update April 2019
Released April 2019 · Oracle's advisory ↗ · ← Critical Patch Update, January 2019 · Critical Patch Update, July 2019 →
207 CVEs in this release, one square each
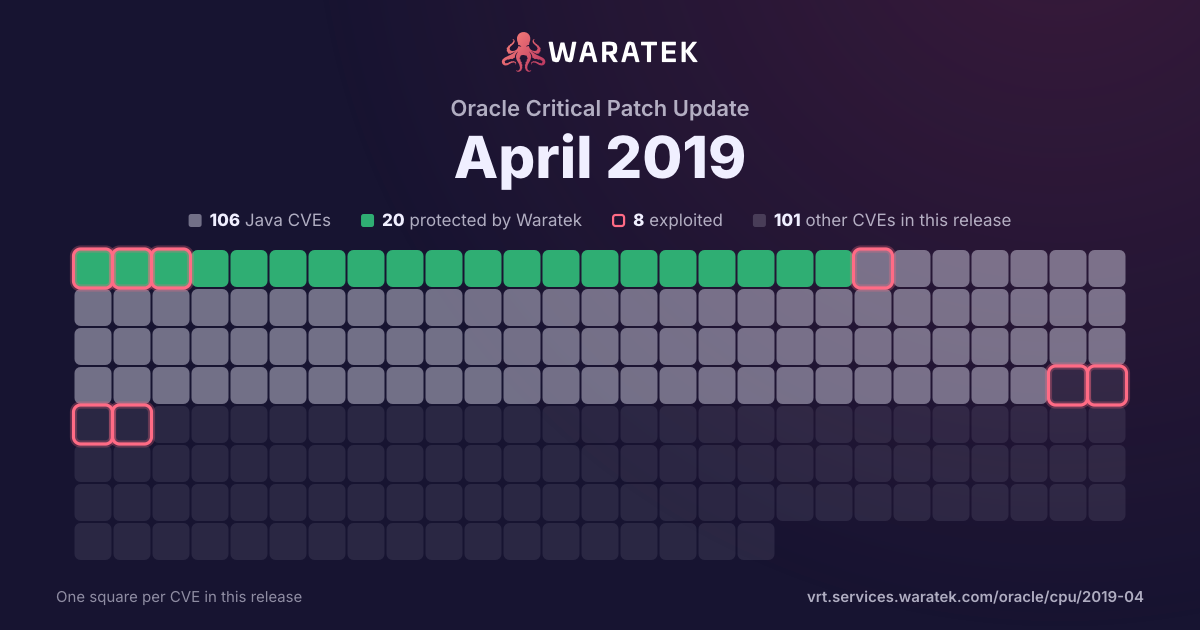
By status
20Protected by Waratek3Mitigation candidate83No exploit published58Outside Waratek scope43Not applicable
8Exploited, marked by the ring
No exploit published. For 80 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 6 matches · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
6matches
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
6
100.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
blocked by ARMR today
6
100.0%
partly blocked
0
0.0%
not blocked
0
0.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
6
100.0%
split by
peak 3 / month
Feb 181
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Mar 181
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Apr 180
May 181
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Jun 180
Jul 180
Aug 180
Sep 180
Oct 180
Nov 180
Dec 180
Jan 193
Protected by Waratek3
Critical3
blocked by ARMR today3
No public exploit3
Feb 18Mar 18Apr 18May 18Jun 18Jul 18Aug 18Sep 18Oct 18Nov 18Dec 18Jan 19
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-3772 | Critical | 2019-01-18 | Protected by Waratek | No public exploit | Spring Integration (spring-integration-xml and spring-integration-ws modules), versions 4.3.18, 5.0.10, 5.1.1, and older unsupported versions, were susceptible to XML External Entity Injection (XXE) when receiving XML data from untrusted sources. |
| CVE-2018-19362 | Critical | 2019-01-02 | Protected by Waratek | No public exploit | FasterXML jackson-databind 2.x before 2.9.8 might allow attackers to have unspecified impact by leveraging failure to block the jboss-common-core class from polymorphic deserialization. |
| CVE-2018-14718 | Critical | 2019-01-02 | Protected by Waratek | No public exploit | FasterXML jackson-databind 2.x before 2.9.7 might allow remote attackers to execute arbitrary code by leveraging failure to block the slf4j-ext class from polymorphic deserialization. |
| CVE-2018-8013 | Critical | 2018-05-24 | Protected by Waratek | No public exploit | In Apache Batik 1.x before 1.10, when deserializing subclass of `AbstractDocument`, the class takes a string from the inputStream as the class name which then use it to call the no-arg constructor of the class. Fix was to check the class type before calling newInstance in deserialization. |
| CVE-2018-8088 | Critical | 2018-03-20 | Protected by Waratek | No public exploit | org.slf4j.ext.EventData in the slf4j-ext module in QOS.CH SLF4J before 1.8.0-beta2 allows remote attackers to bypass intended access restrictions via crafted data. EventData in the slf4j-ext module in QOS.CH SLF4J, has been fixed in SLF4J versions 1.7.26 later and in the 2.0.x series. |
| CVE-2018-7489 | Critical | 2018-02-26 | Protected by Waratek | No public exploit | FasterXML jackson-databind before 2.7.9.3, 2.8.x before 2.8.11.1 and 2.9.x before 2.9.5 allows unauthenticated remote code execution because of an incomplete fix for the CVE-2017-7525 deserialization flaw. This is exploitable by sending maliciously crafted JSON input to the readValue method of the ObjectMapper, bypassing a blacklist that is ineffective if the c3p0 libraries are available in the classpath. |