
Oracle Critical Patch Update April 2019
Released April 2019 · Oracle's advisory ↗ · ← Critical Patch Update, January 2019 · Critical Patch Update, July 2019 →
207 CVEs in this release, one square each
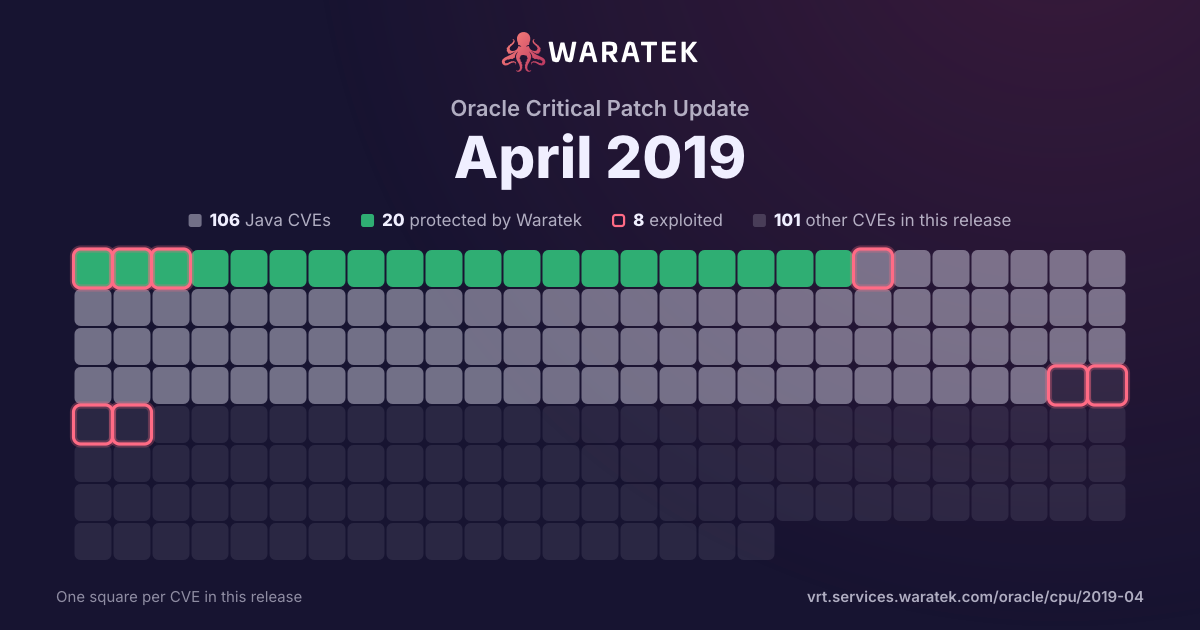
By status
21Protected by Waratek6Mitigation candidate89No exploit published8Outside Waratek scope83Not applicable
8Exploited, marked by the ring
No exploit published. For 81 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 9 matches · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
9matches
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
9
100.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
9
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
9
100.0%
split by
peak 6 / month
May 181
No exploit published1
High1
not blocked1
No public exploit1
Jun 181
No exploit published1
High1
not blocked1
No public exploit1
Jul 180
Aug 180
Sep 180
Oct 181
No exploit published1
High1
not blocked1
No public exploit1
Nov 180
Dec 180
Jan 190
Feb 190
Mar 190
Apr 196
No exploit published6
High5
Medium1
not blocked6
No public exploit6
May 18Jun 18Jul 18Aug 18Sep 18Oct 18Nov 18Dec 18Jan 19Feb 19Mar 19Apr 19
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-2558 | High | 2019-04-23 | No exploit published | No public exploit | Vulnerability in the Oracle Retail Point-of-Service component of Oracle Retail Applications (subcomponent: Infrastructure). Supported versions that are affected are 13.4, 14.0 and 14.1. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Retail Point-of-Service. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Retail Point-of-Service accessible data as well as unauthorized read access to a subset of Oracle Retail Point-of-Service accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Retail Point-of-Service. CVSS 3.0 Base Score 7.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:L). |
| CVE-2019-2424 | High | 2019-04-23 | No exploit published | No public exploit | Vulnerability in the Oracle Retail Convenience Store Back Office component of Oracle Retail Applications (subcomponent: Level 3 Maintenance Functions). The supported version that is affected is 3.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Retail Convenience Store Back Office. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Retail Convenience Store Back Office accessible data as well as unauthorized read access to a subset of Oracle Retail Convenience Store Back Office accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Retail Convenience Store Back Office. CVSS 3.0 Base Score 7.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:L). |
| CVE-2018-3314 | High | 2019-04-23 | No exploit published | No public exploit | Vulnerability in the MICROS Relate CRM Software component of Oracle Retail Applications (subcomponent: Customer). The supported version that is affected is 11.4. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise MICROS Relate CRM Software. While the vulnerability is in MICROS Relate CRM Software, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all MICROS Relate CRM Software accessible data as well as unauthorized access to critical data or complete access to all MICROS Relate CRM Software accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:L/UI:N/S:C/C:H/I:H/A:N). |
| CVE-2018-3312 | Medium | 2019-04-23 | No exploit published | No public exploit | Vulnerability in the Oracle Retail Customer Engagement component of Oracle Retail Applications (subcomponent: Segment). Supported versions that are affected are 16.0 and 17.0. Difficult to exploit vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Retail Customer Engagement. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Retail Customer Engagement accessible data as well as unauthorized read access to a subset of Oracle Retail Customer Engagement accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Retail Customer Engagement. CVSS 3.0 Base Score 5.5 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:H/UI:N/S:U/C:L/I:H/A:L). |
| CVE-2018-3120 | High | 2019-04-23 | No exploit published | No public exploit | Vulnerability in the MICROS Lucas component of Oracle Retail Applications (subcomponent: Security). Supported versions that are affected are 2.9.5.6 and 2.9.5.7. Difficult to exploit vulnerability allows low privileged attacker with network access via HTTP to compromise MICROS Lucas. Successful attacks of this vulnerability can result in takeover of MICROS Lucas. CVSS 3.0 Base Score 7.5 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:L/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2018-2880 | High | 2019-04-23 | No exploit published | No public exploit | Vulnerability in the MICROS Retail-J component of Oracle Retail Applications (subcomponent: Back Office). The supported version that is affected is 12.1.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise MICROS Retail-J. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all MICROS Retail-J accessible data. CVSS 3.0 Base Score 7.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2018-15756 | High | 2018-10-18 | No exploit published | No public exploit | Spring Framework, version 5.1, versions 5.0.x prior to 5.0.10, versions 4.3.x prior to 4.3.20, and older unsupported versions on the 4.2.x branch provide support for range requests when serving static resources through the ResourceHttpRequestHandler, or starting in 5.0 when an annotated controller returns an org.springframework.core.io.Resource. A malicious user (or attacker) can add a range header with a high number of ranges, or with wide ranges that overlap, or both, for a denial of service attack. This vulnerability affects applications that depend on either spring-webmvc or spring-webflux. Such applications must also have a registration for serving static resources (e.g. JS, CSS, images, and others), or have an annotated controller that returns an org.springframework.core.io.Resource. Spring Boot applications that depend on spring-boot-starter-web or spring-boot-starter-webflux are ready to serve static resources out of the box and are therefore vulnerable. |
| CVE-2018-1000180 | High | 2018-06-05 | No exploit published | No public exploit | Bouncy Castle BC 1.54 - 1.59, BC-FJA 1.0.0, BC-FJA 1.0.1 and earlier have a flaw in the Low-level interface to RSA key pair generator, specifically RSA Key Pairs generated in low-level API with added certainty may have less M-R tests than expected. This appears to be fixed in versions BC 1.60 beta 4 and later, BC-FJA 1.0.2 and later. |
| CVE-2018-1258 | High | 2018-05-11 | No exploit published | No public exploit | Spring Framework version 5.0.5 when used in combination with any versions of Spring Security contains an authorization bypass when using method security. An unauthorized malicious user can gain unauthorized access to methods that should be restricted. |